InfoSec-Prep:OSCP Walkthrough
id_rsa泄露打点,sudo提权
Posted Updated 
By
1 min read
InfoSec-Prep:OSCP Walkthrough
Recon
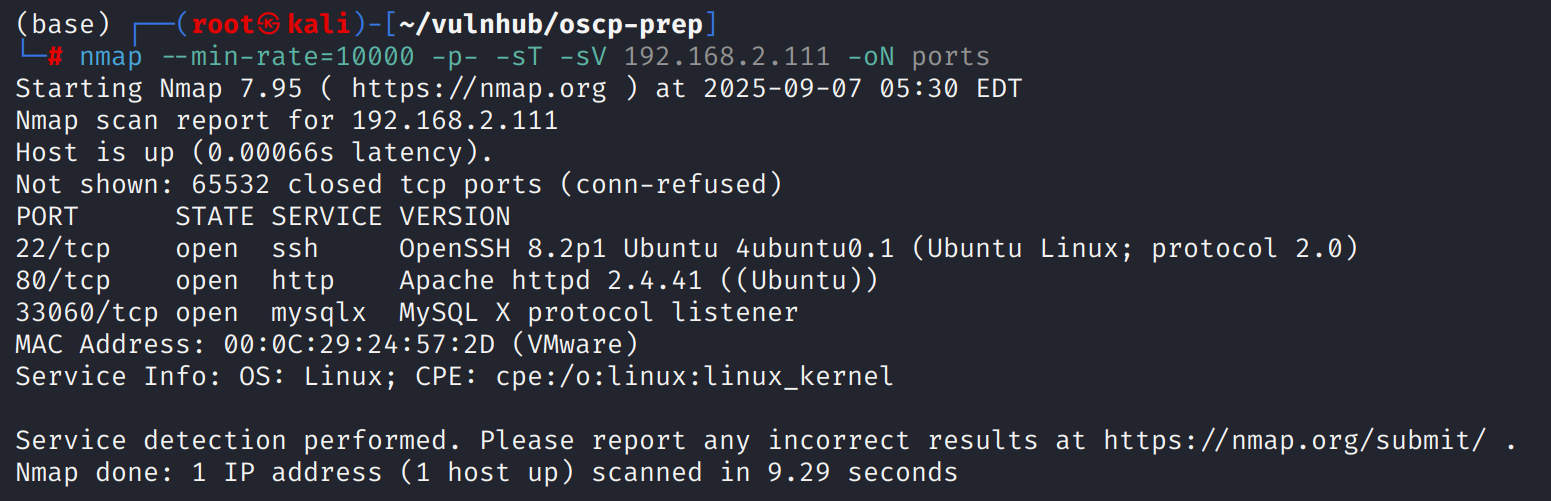
机器开放了标准端口的ssh、web和mysql x
Web
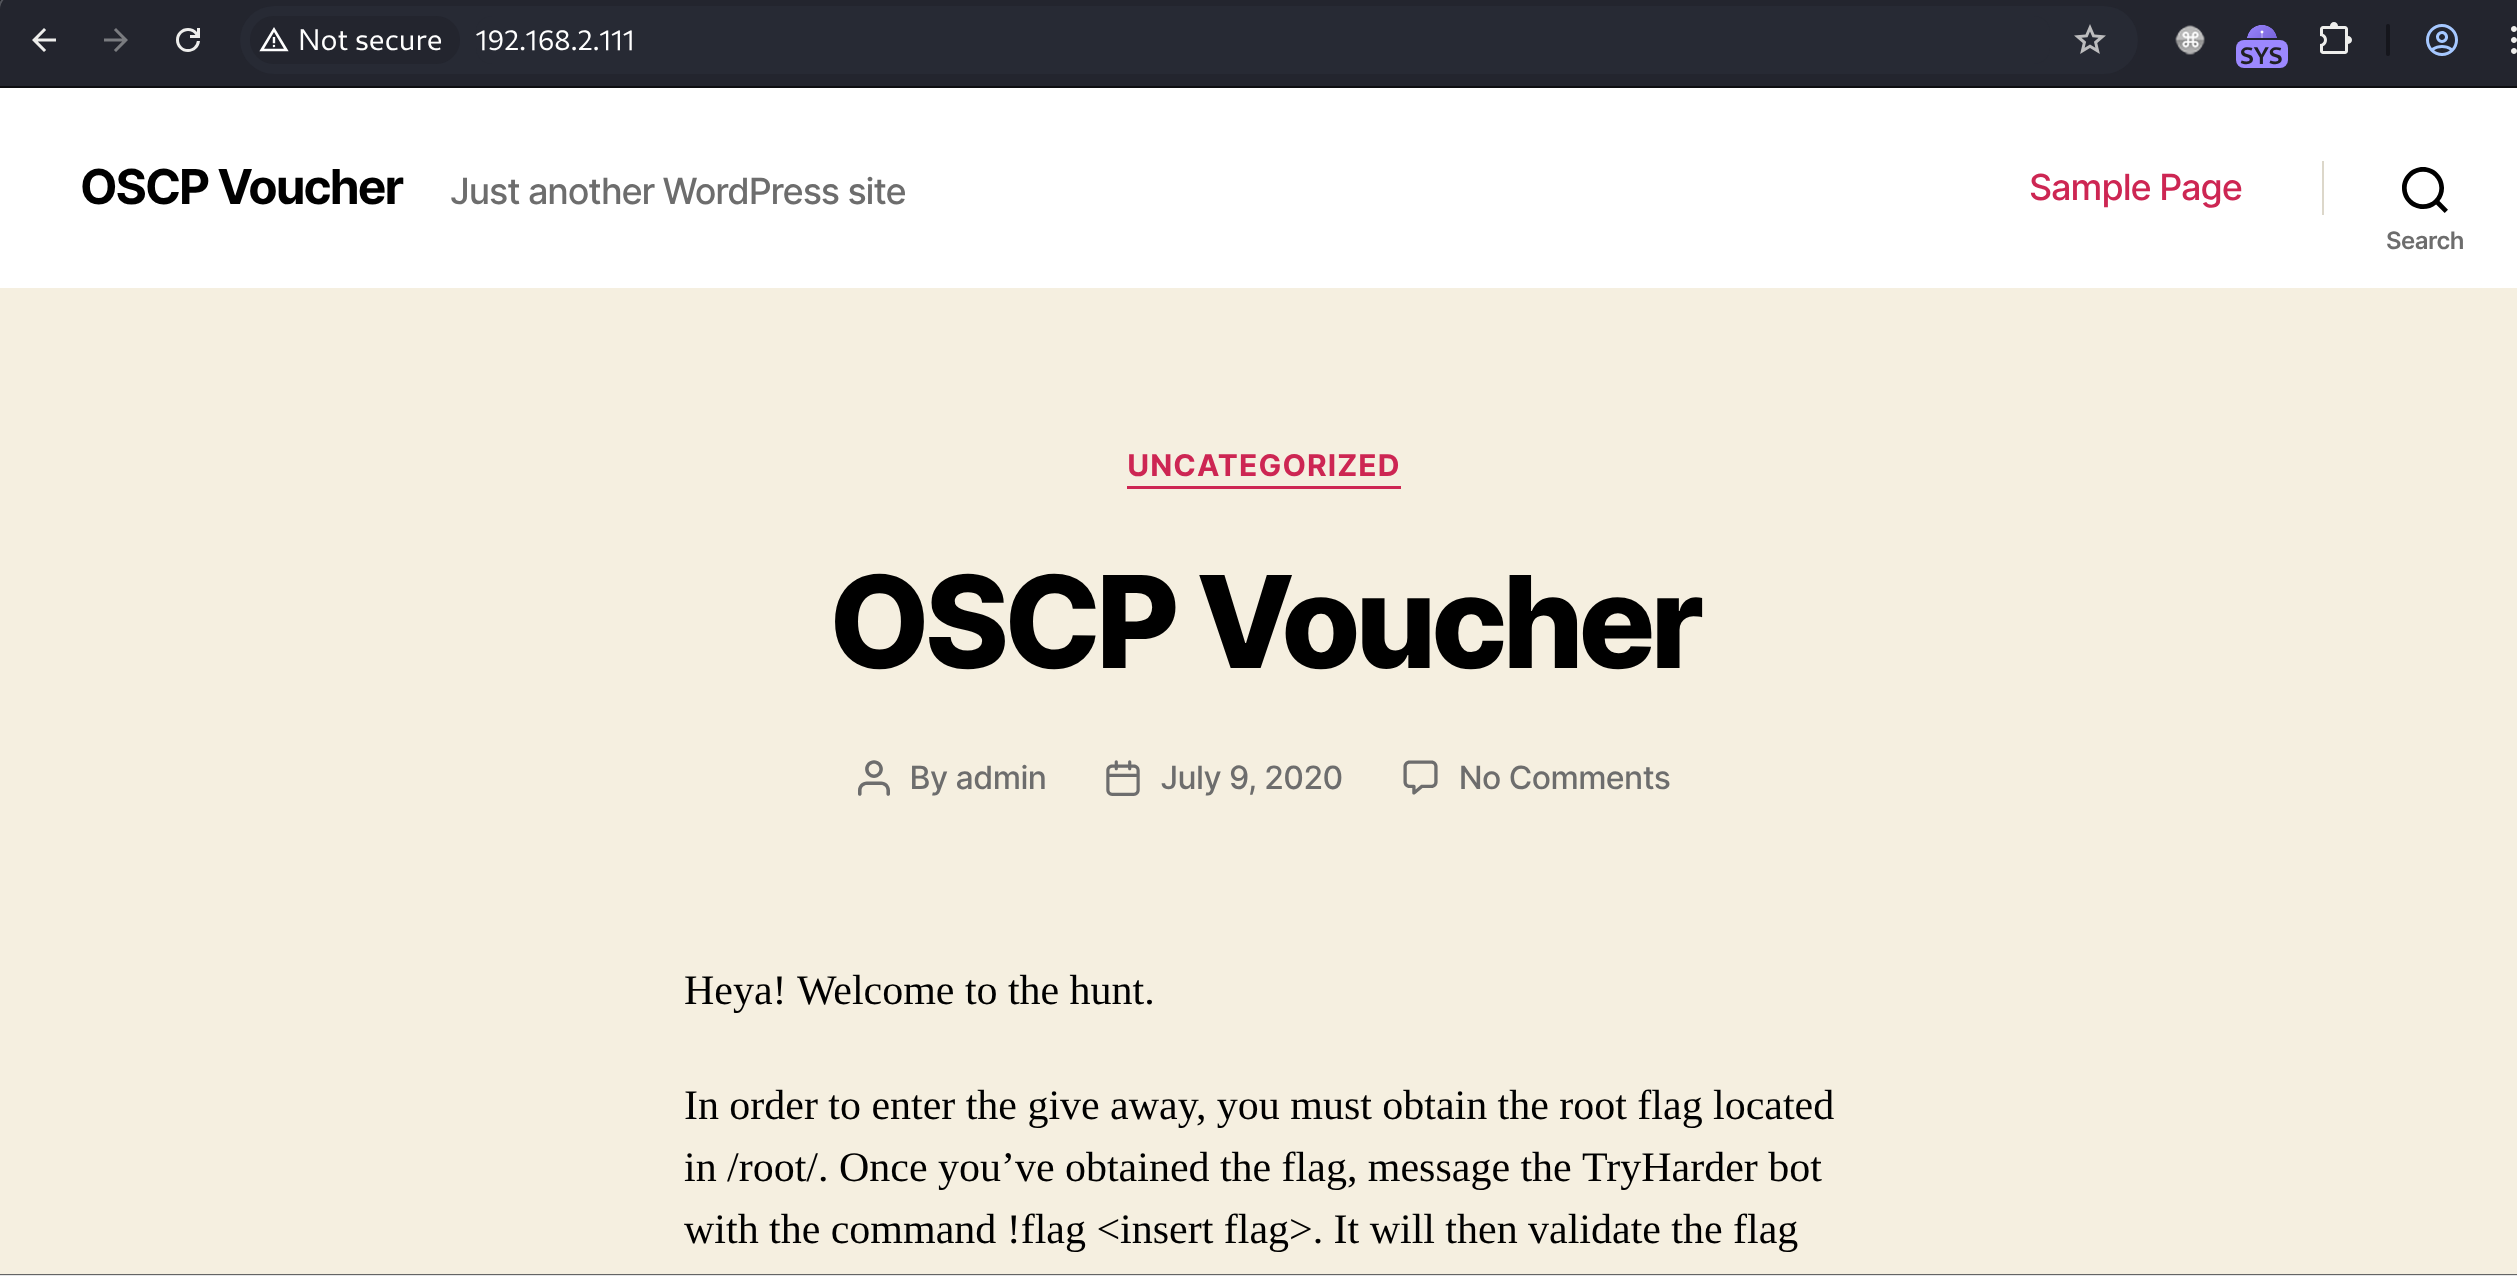
web是一个wordpress
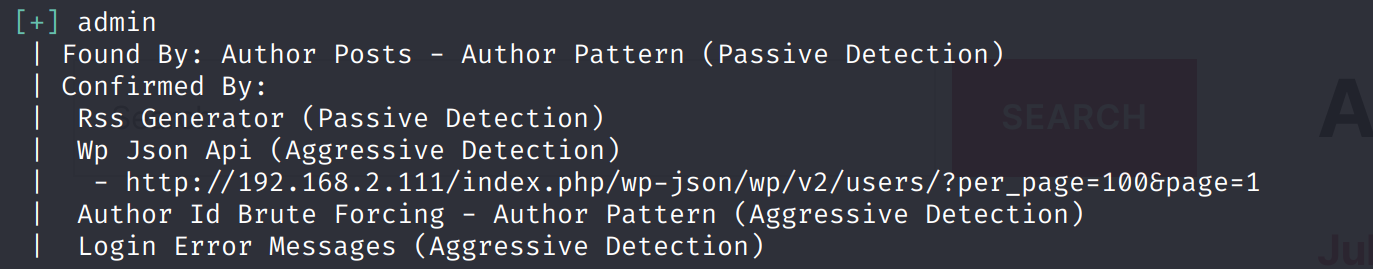
wpscan -e u用户枚举只得到admin
shell as oscp by id_rsa
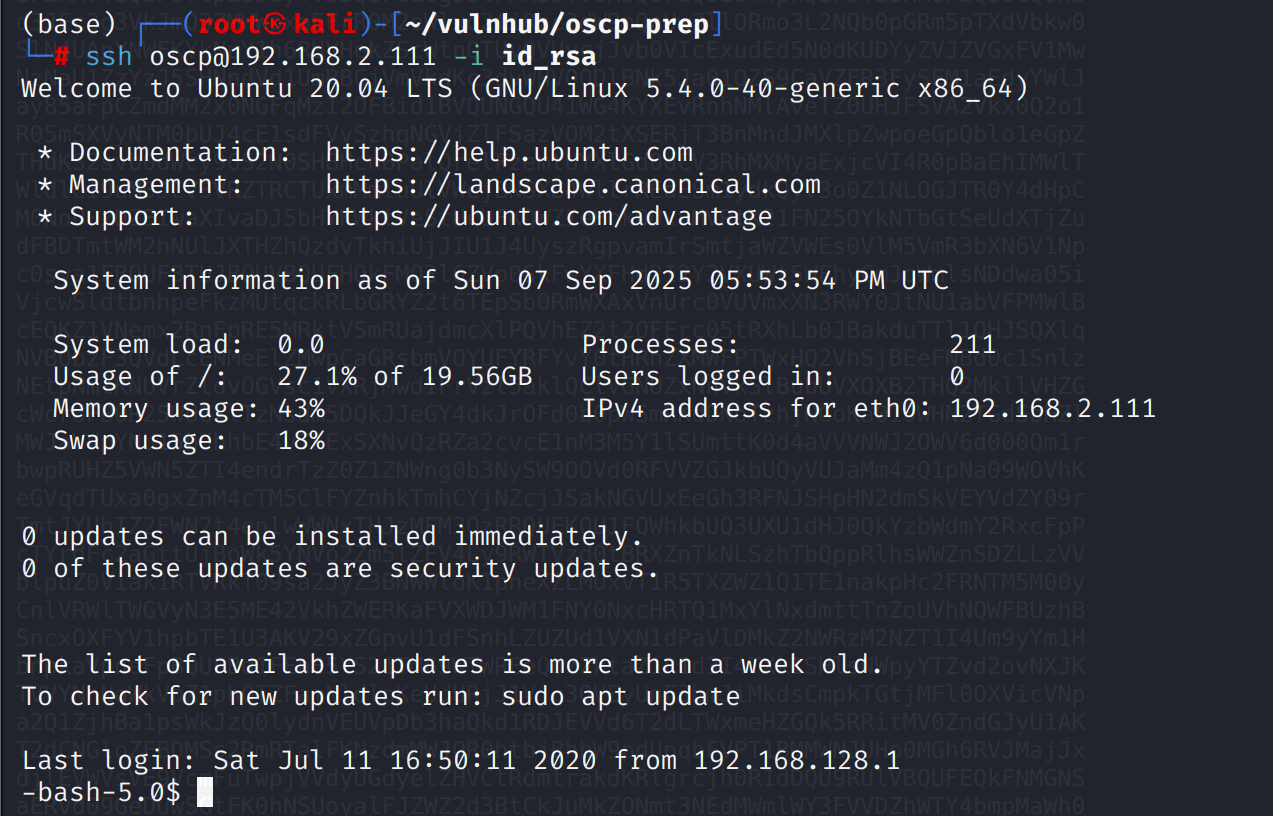
在robots.txt下发现/secret.txt,其中存放了base64内容,解码后发现是ssh私钥
通过对私钥主体解码得到用户名oscp
shell as root by suid
例行检查,发现bash具有suid,/bin/bash -p即可
This post is licensed under CC BY 4.0 by the author.